
API security
The interface is the product now, and the attack surface with it.
23 sketches
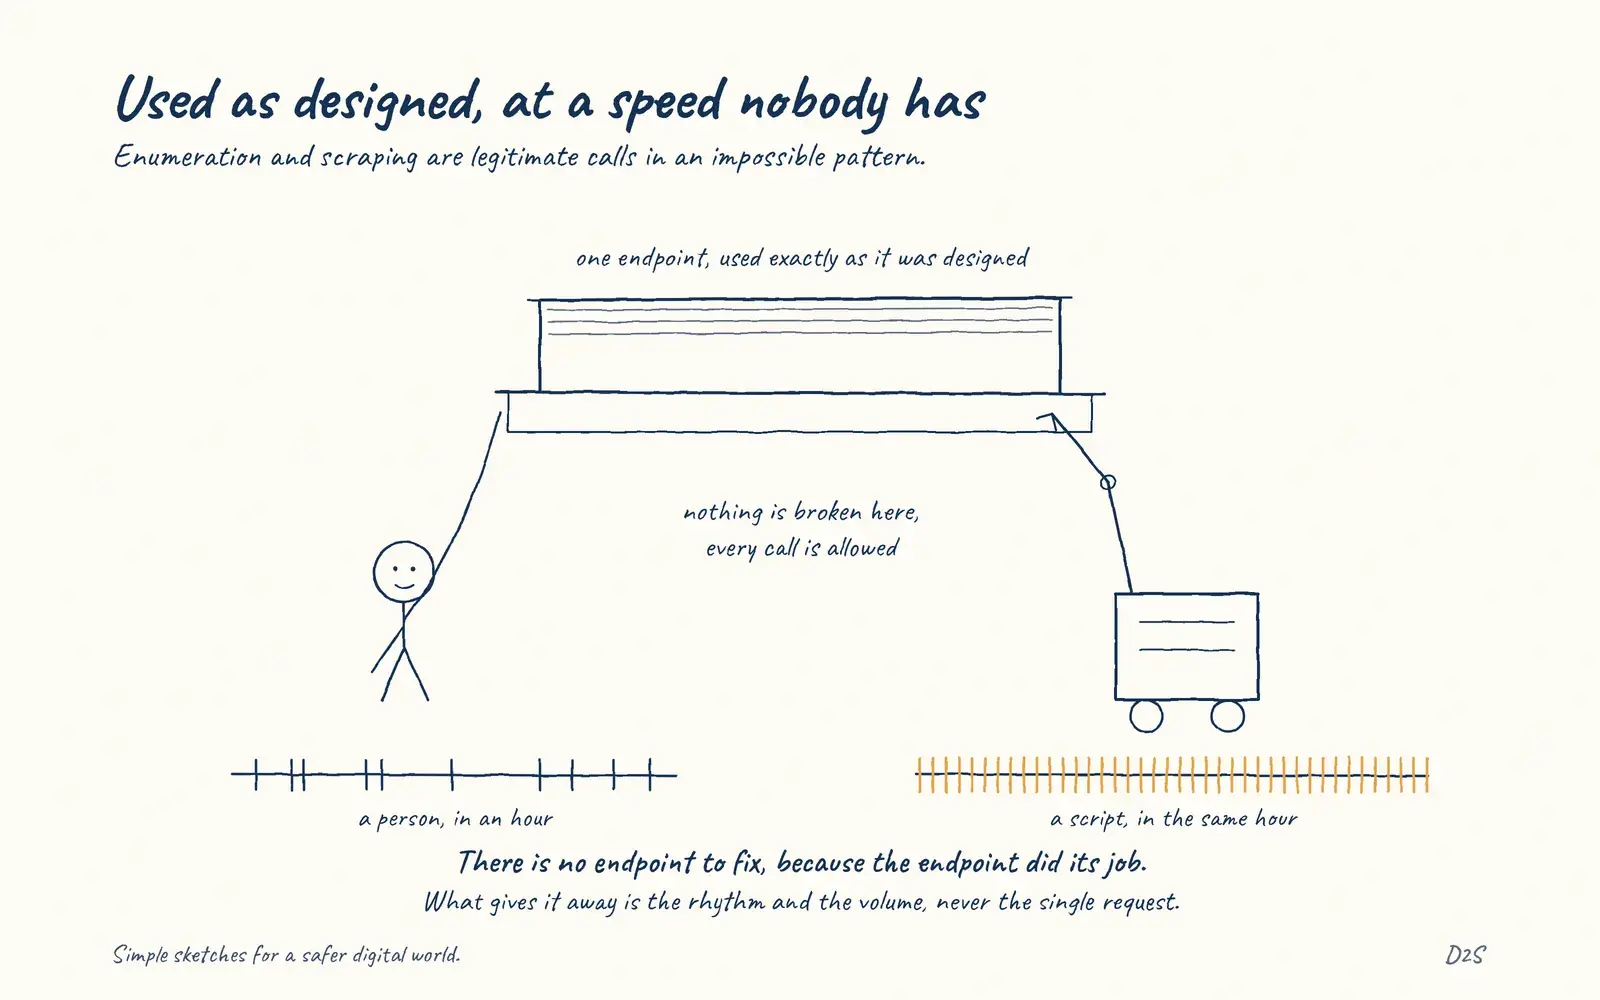 API abuseUsed as designed, at a speed nobody has
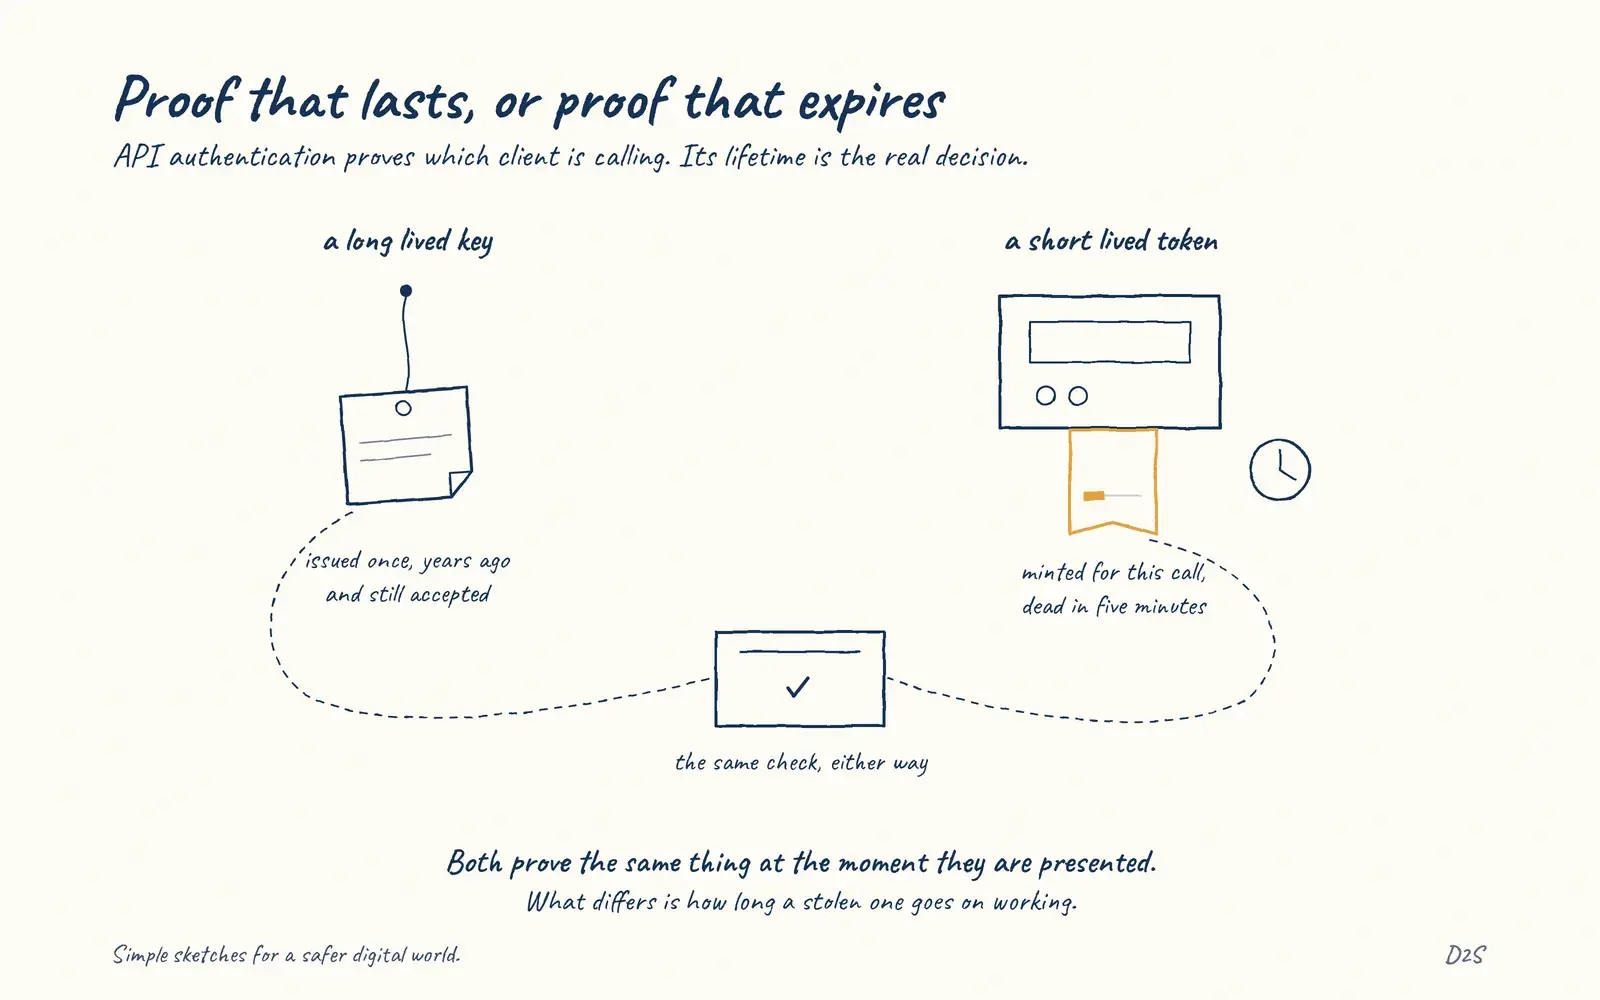 API authenticationProof that lasts, or proof that expires
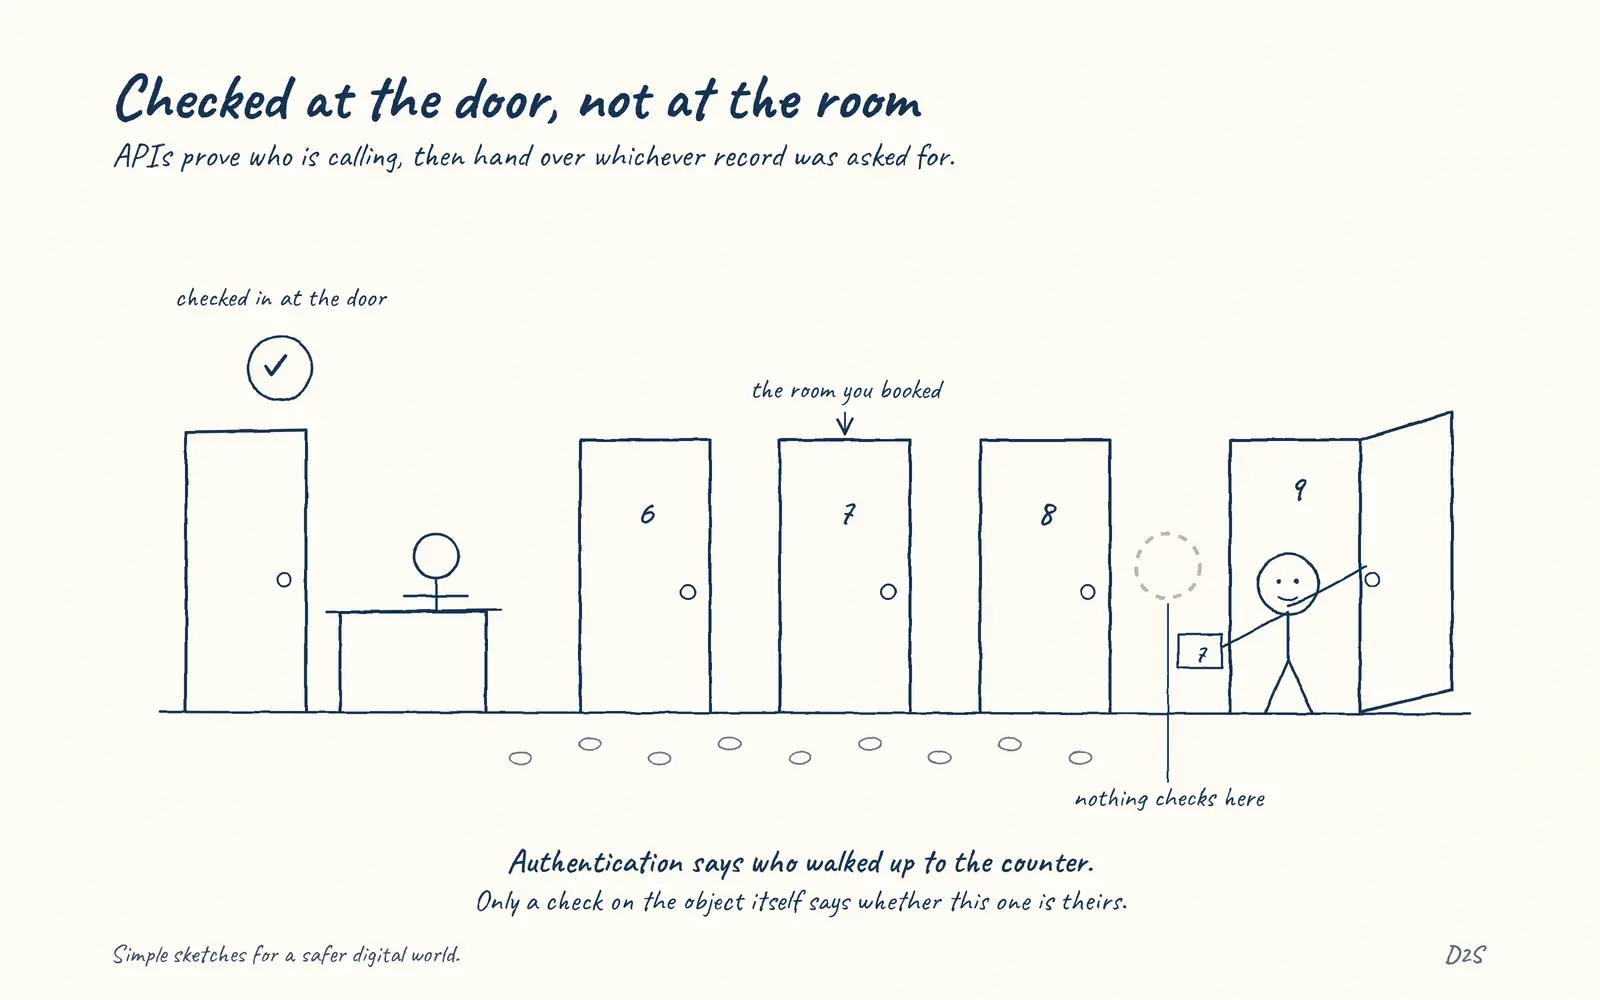 API authorisationChecked at the door, not at the room
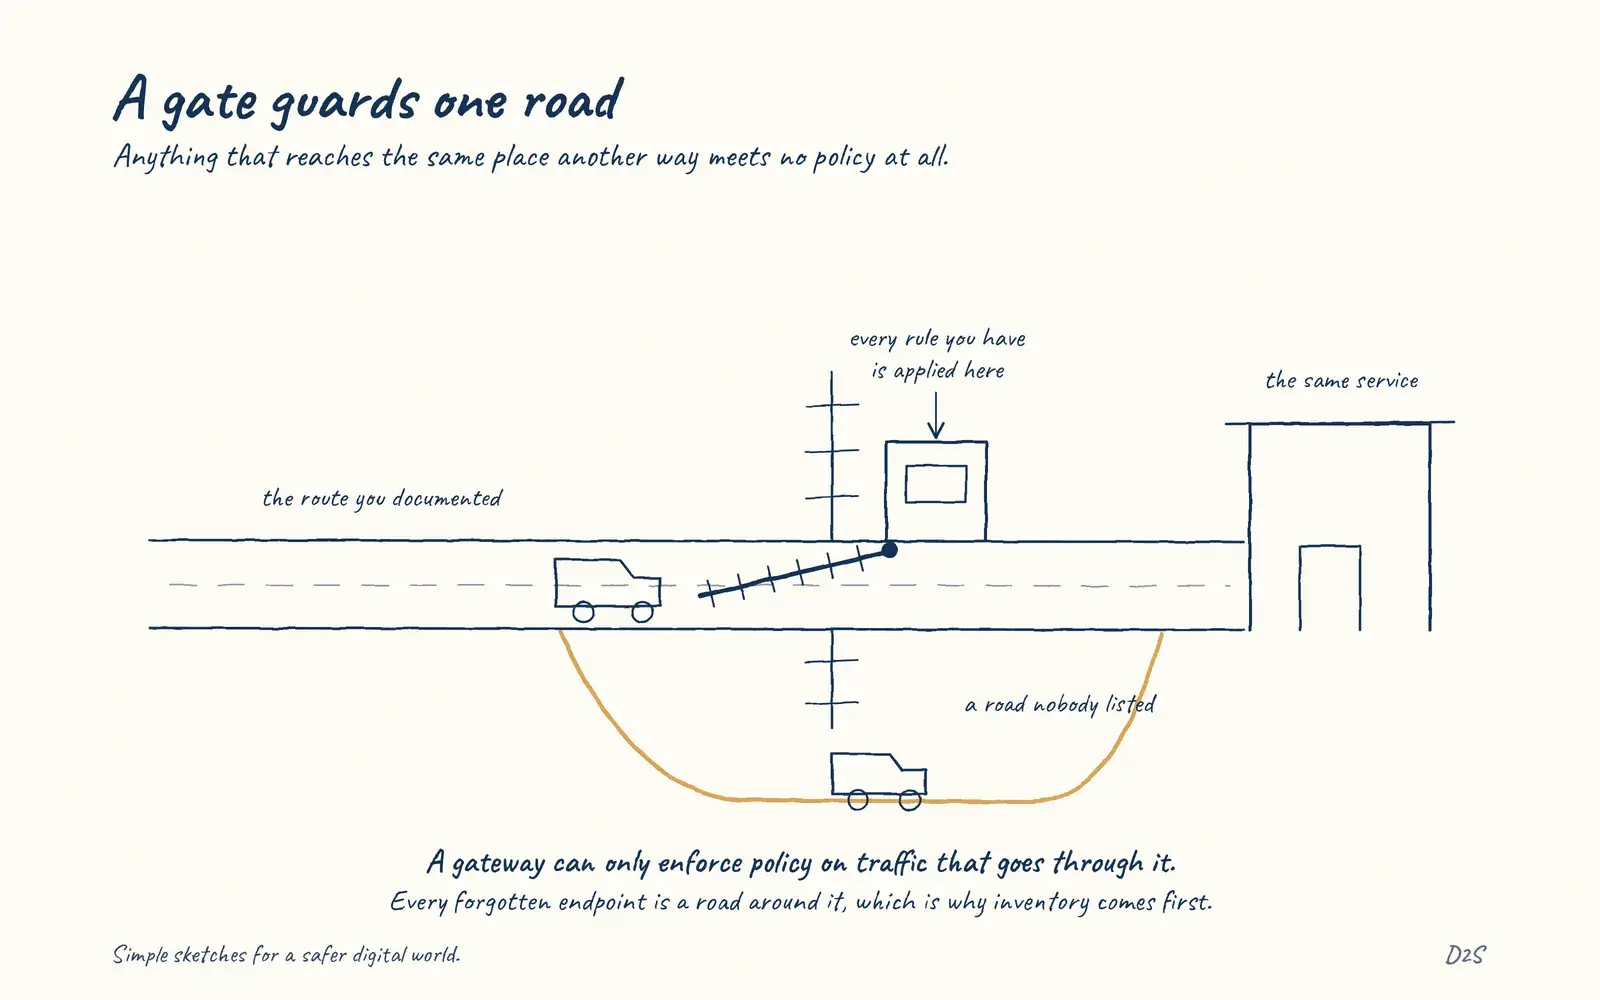 API gatewaysA gate guards one road
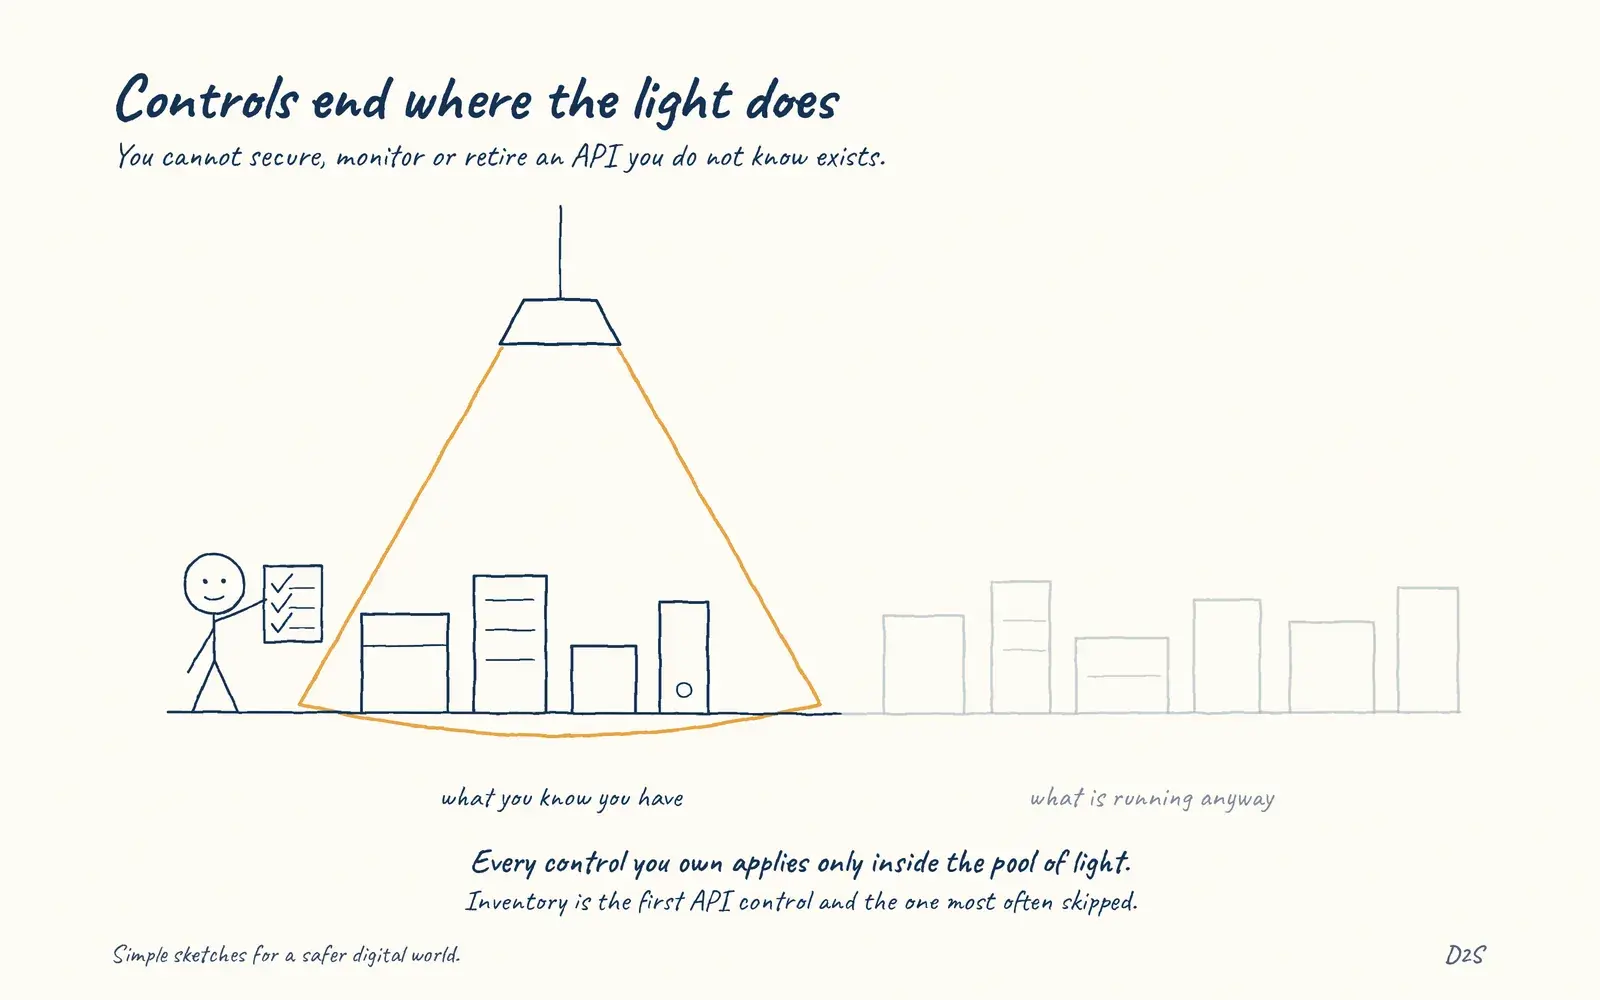 API inventoryControls end where the light does
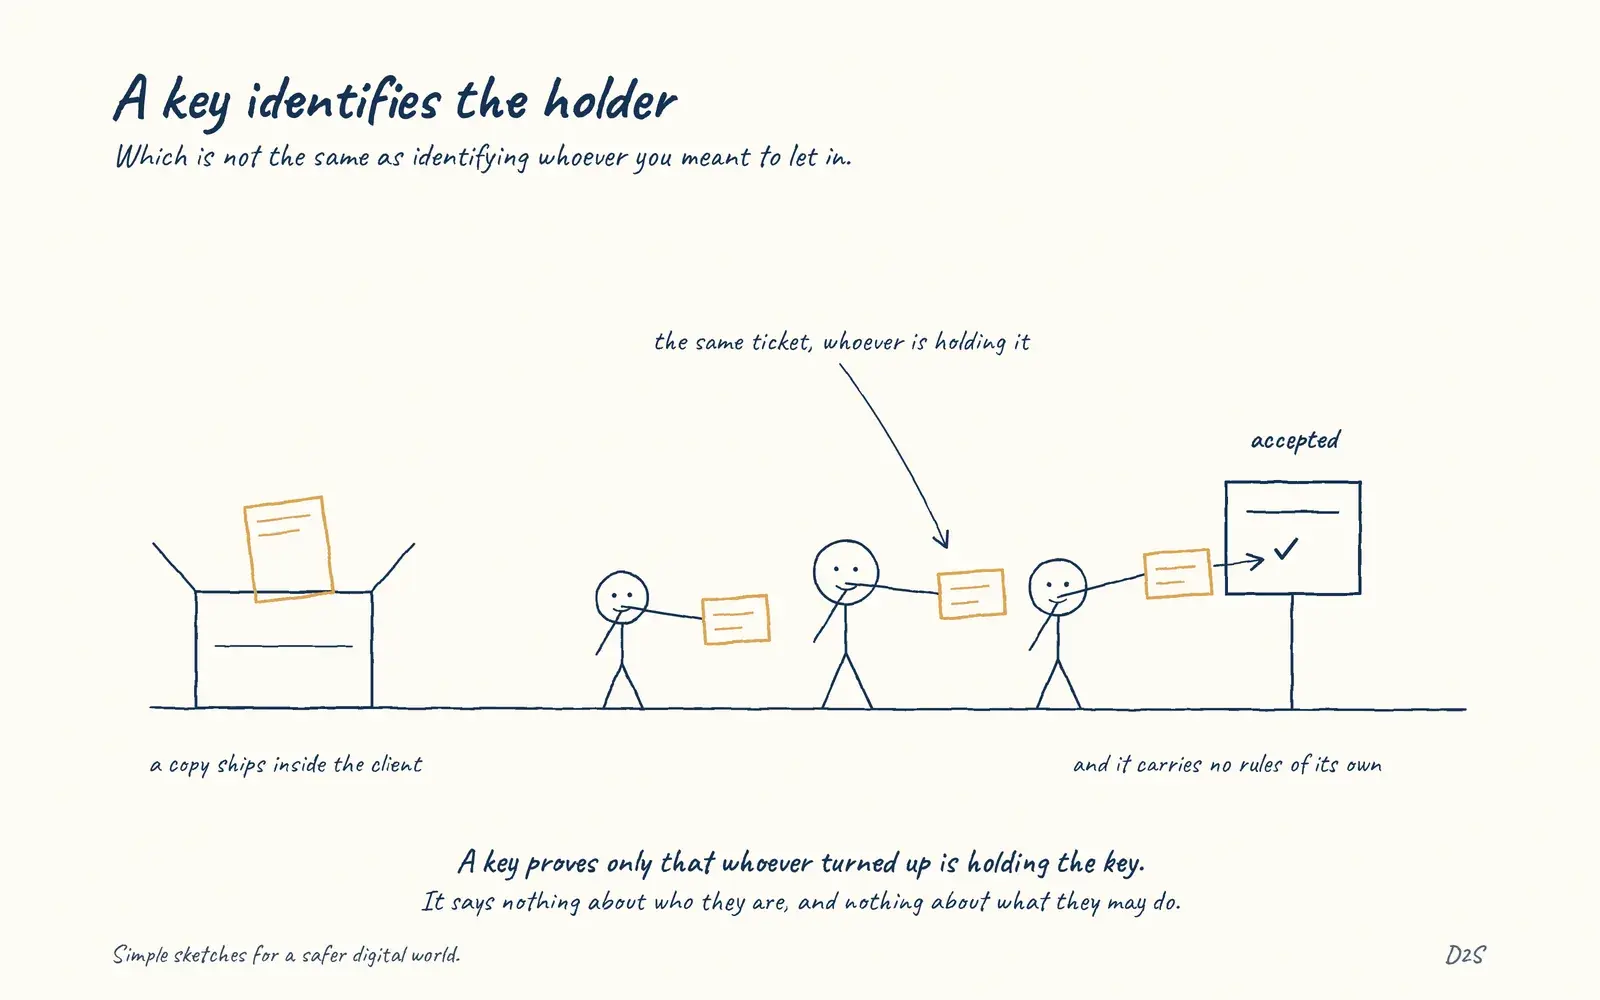 API keysA key identifies the holder
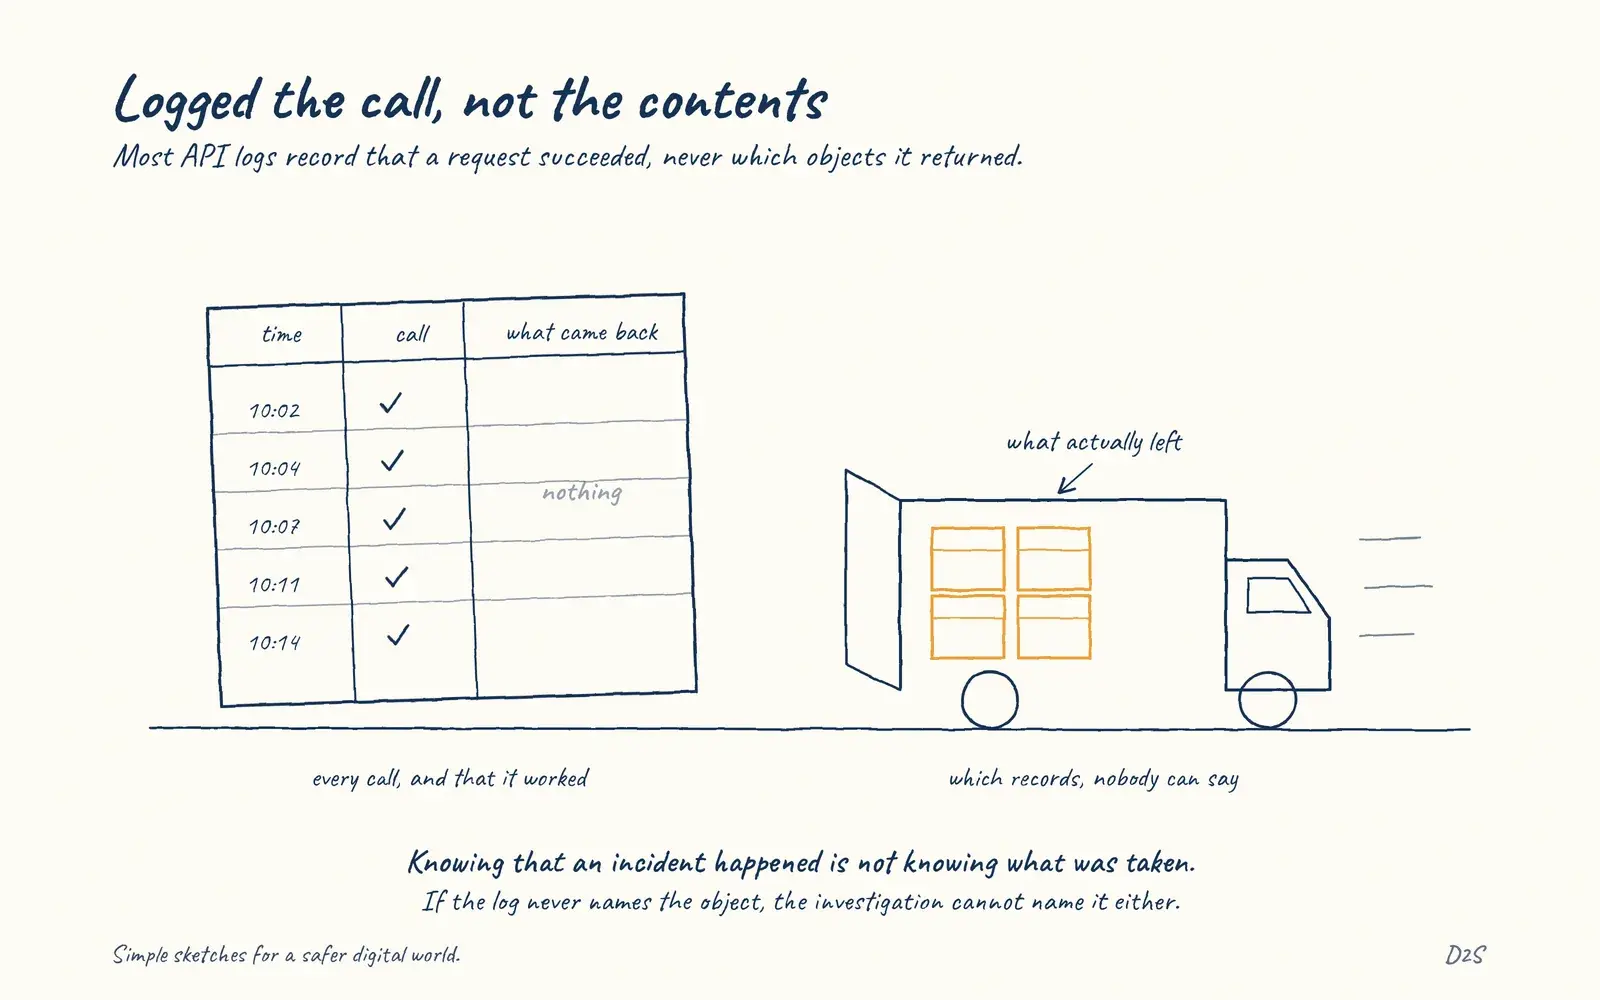 API observabilityLogged the call, not the contents
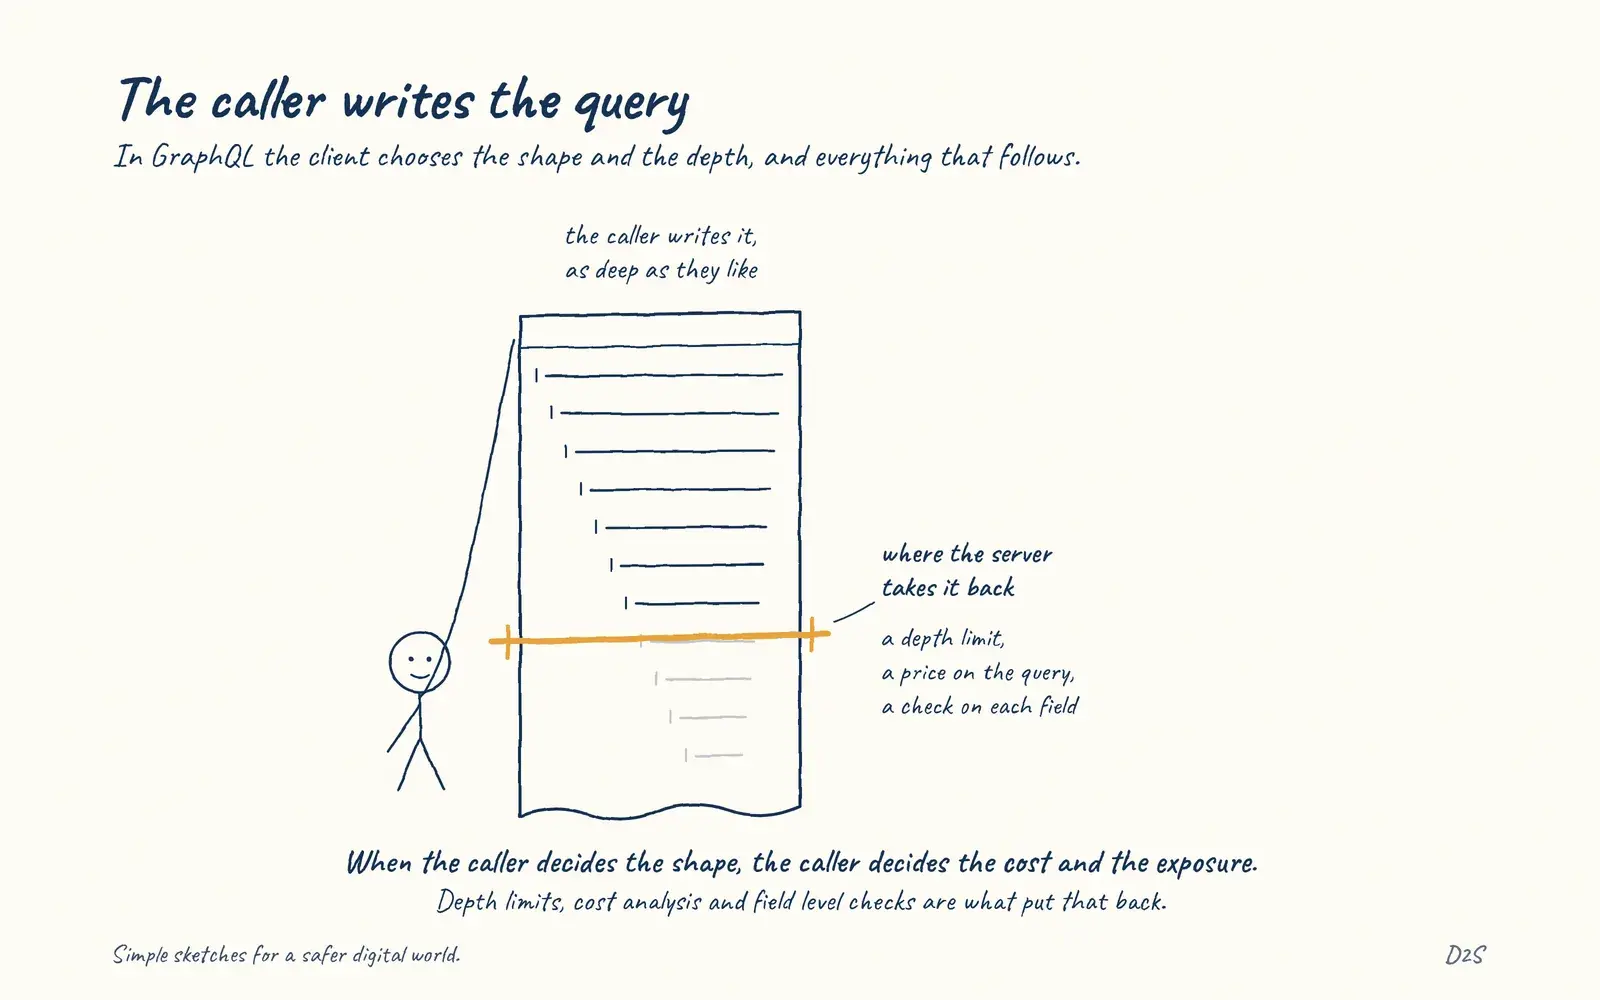 GraphQL securityThe caller writes the query
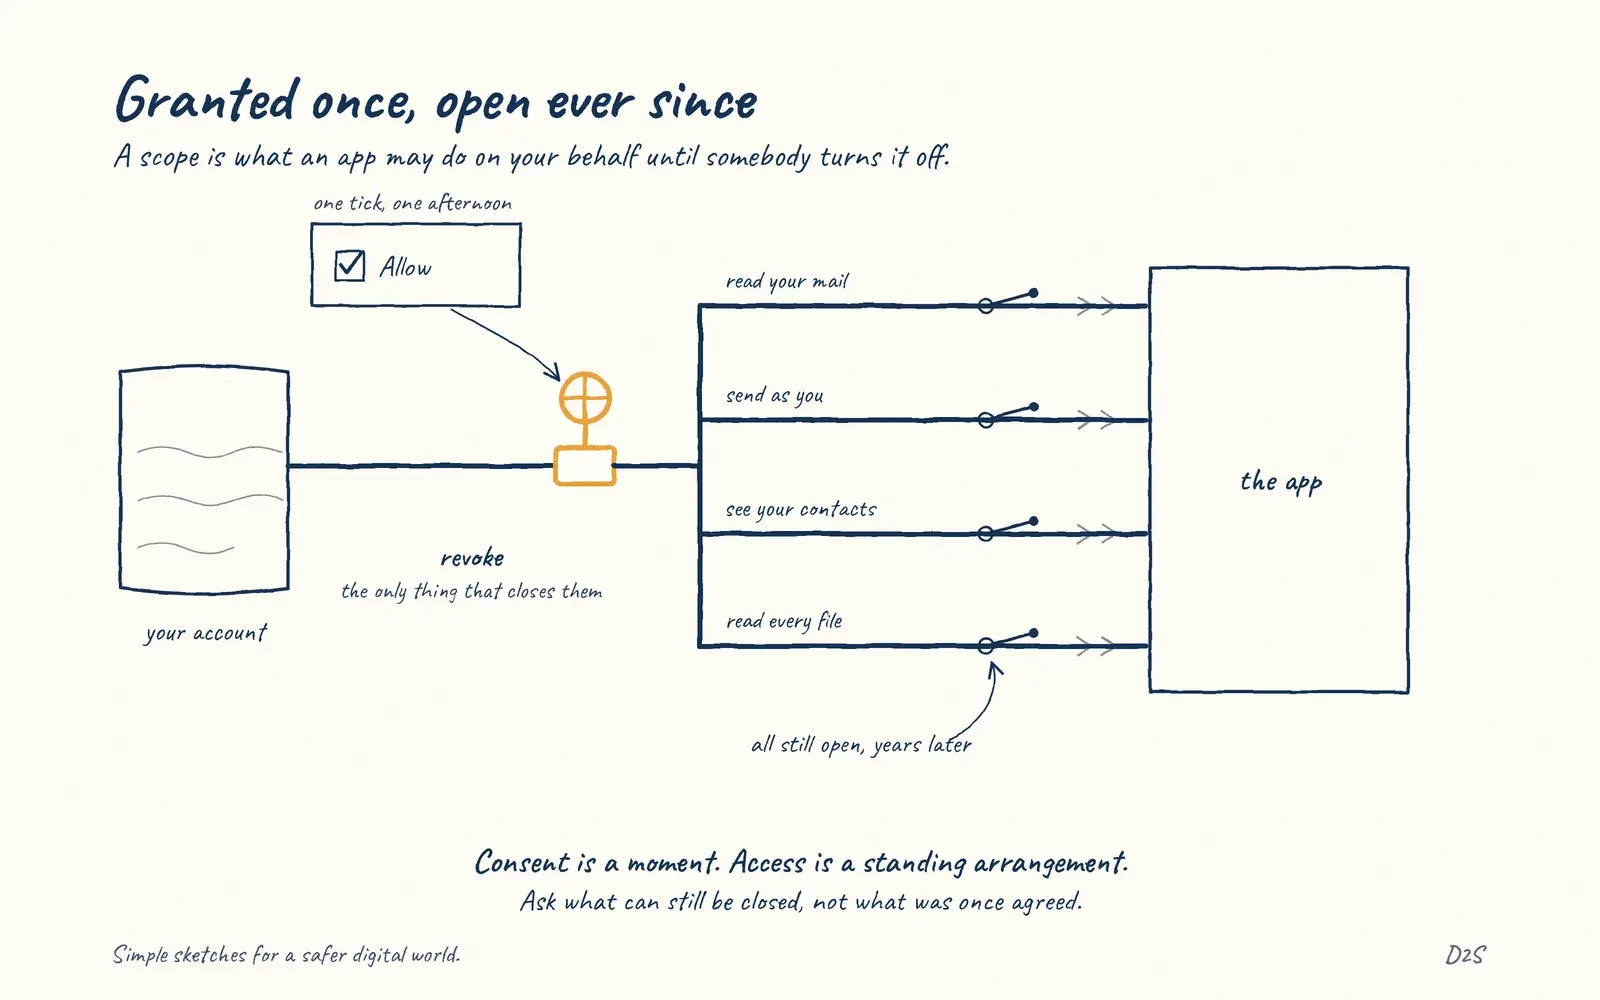 OAuth scopesGranted once, open ever since
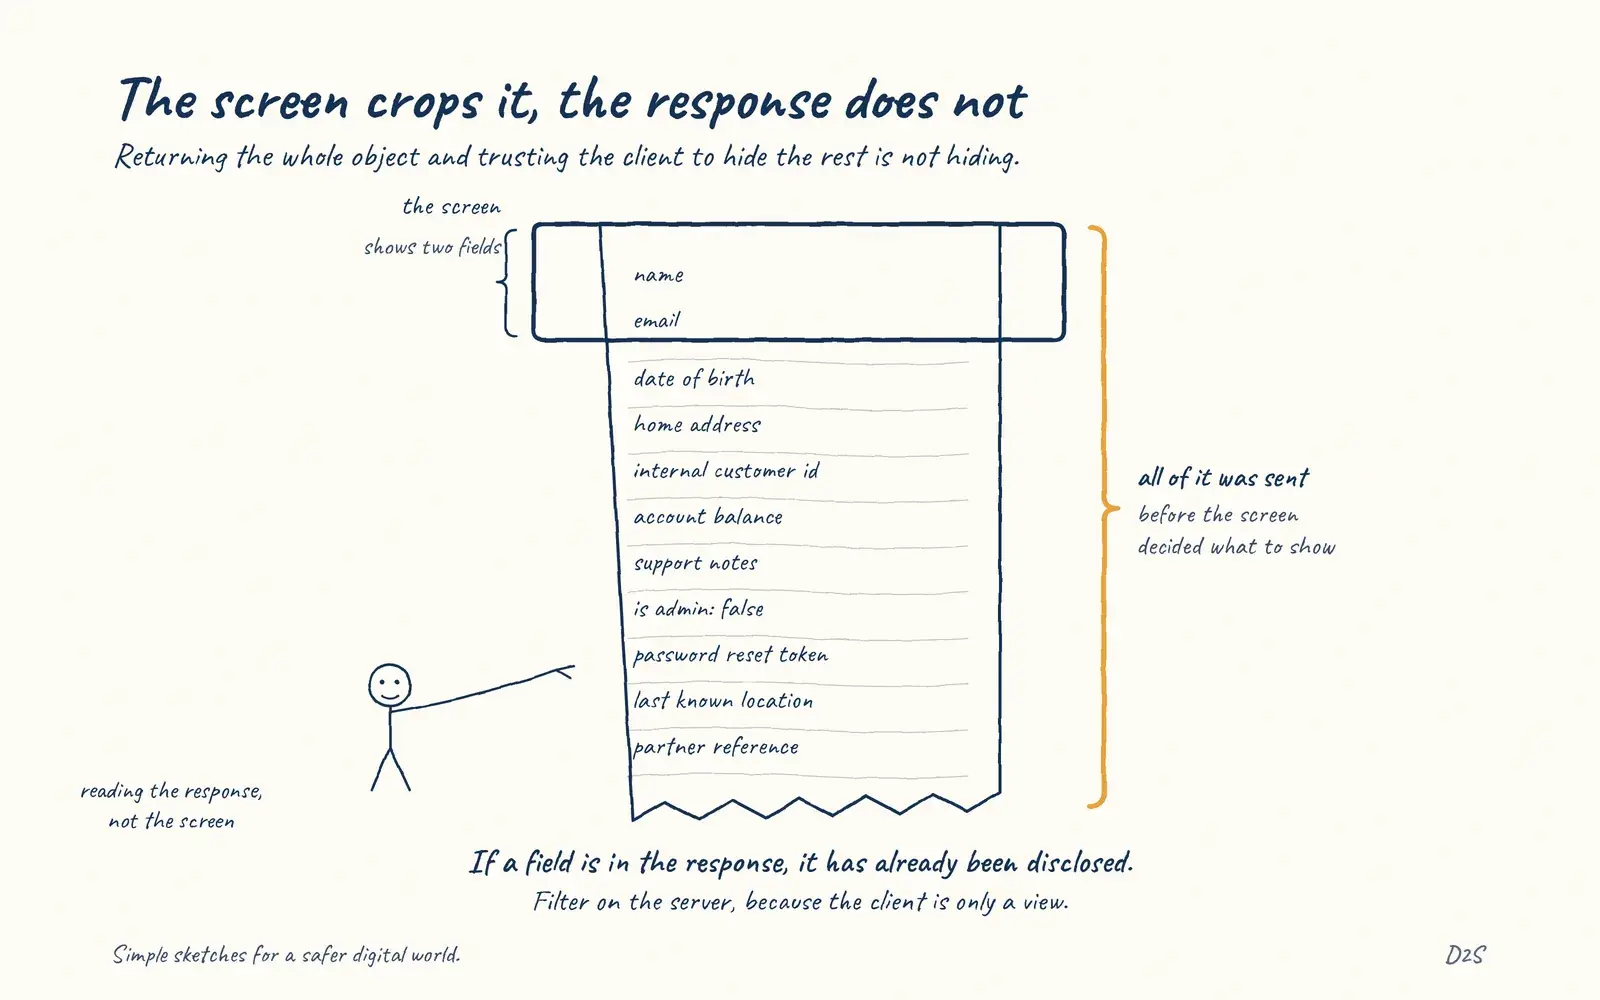 Excessive data exposureThe screen crops it, the response does not
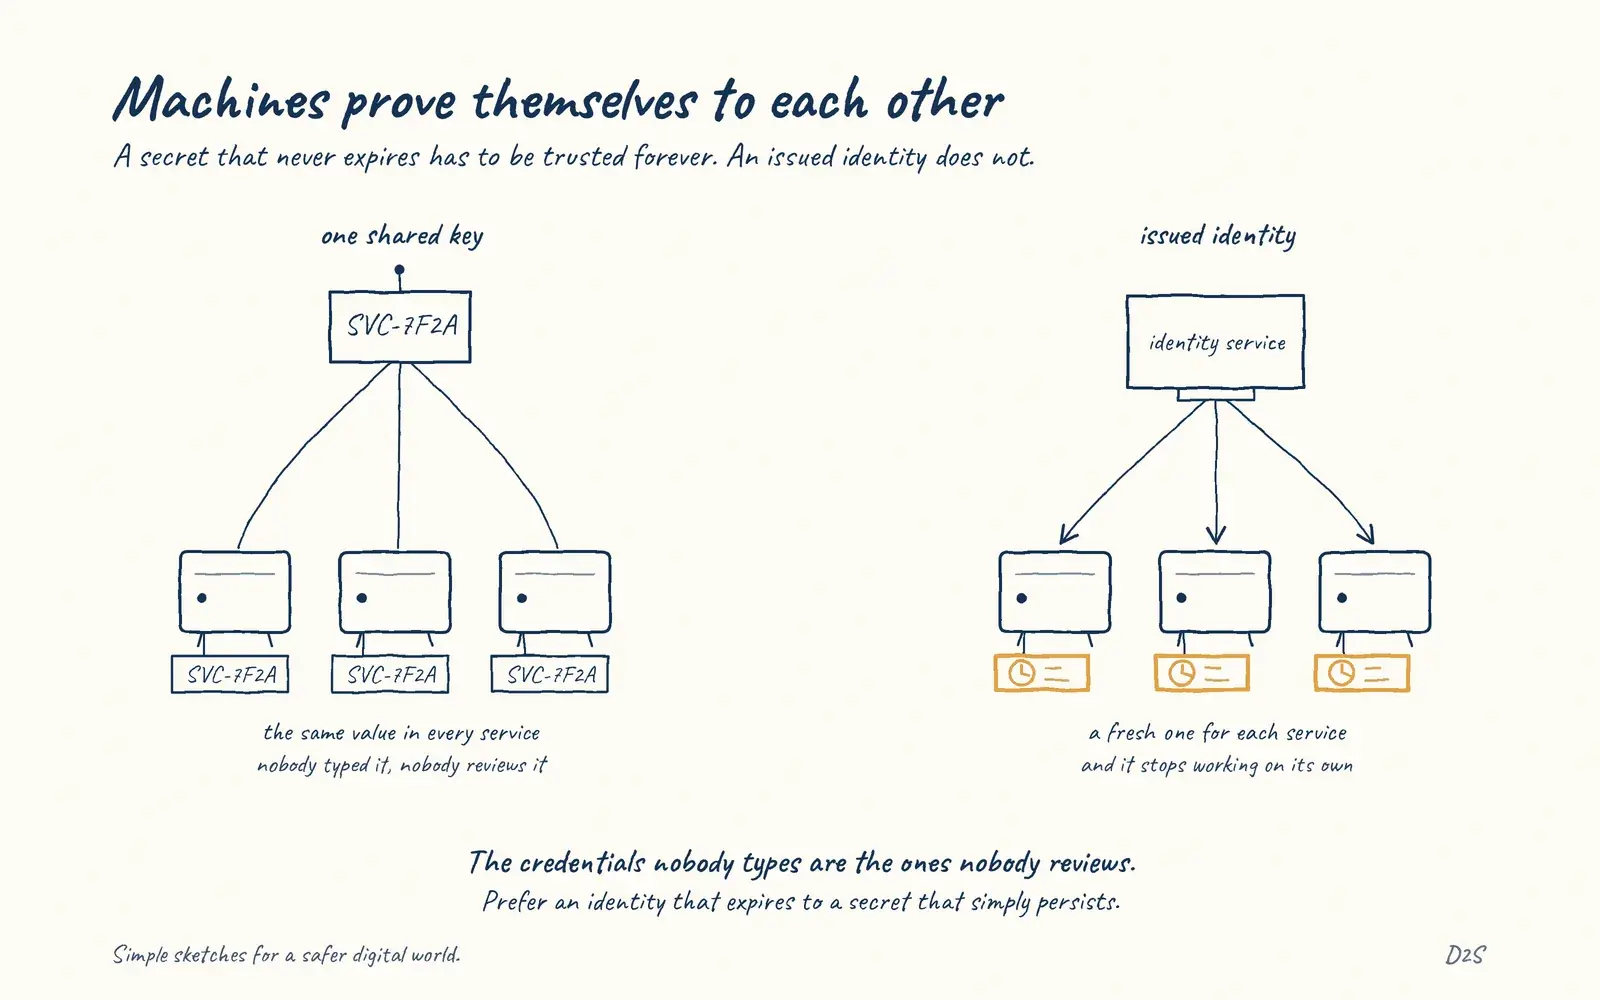 Machine-to-machine trustMachines prove themselves to each other
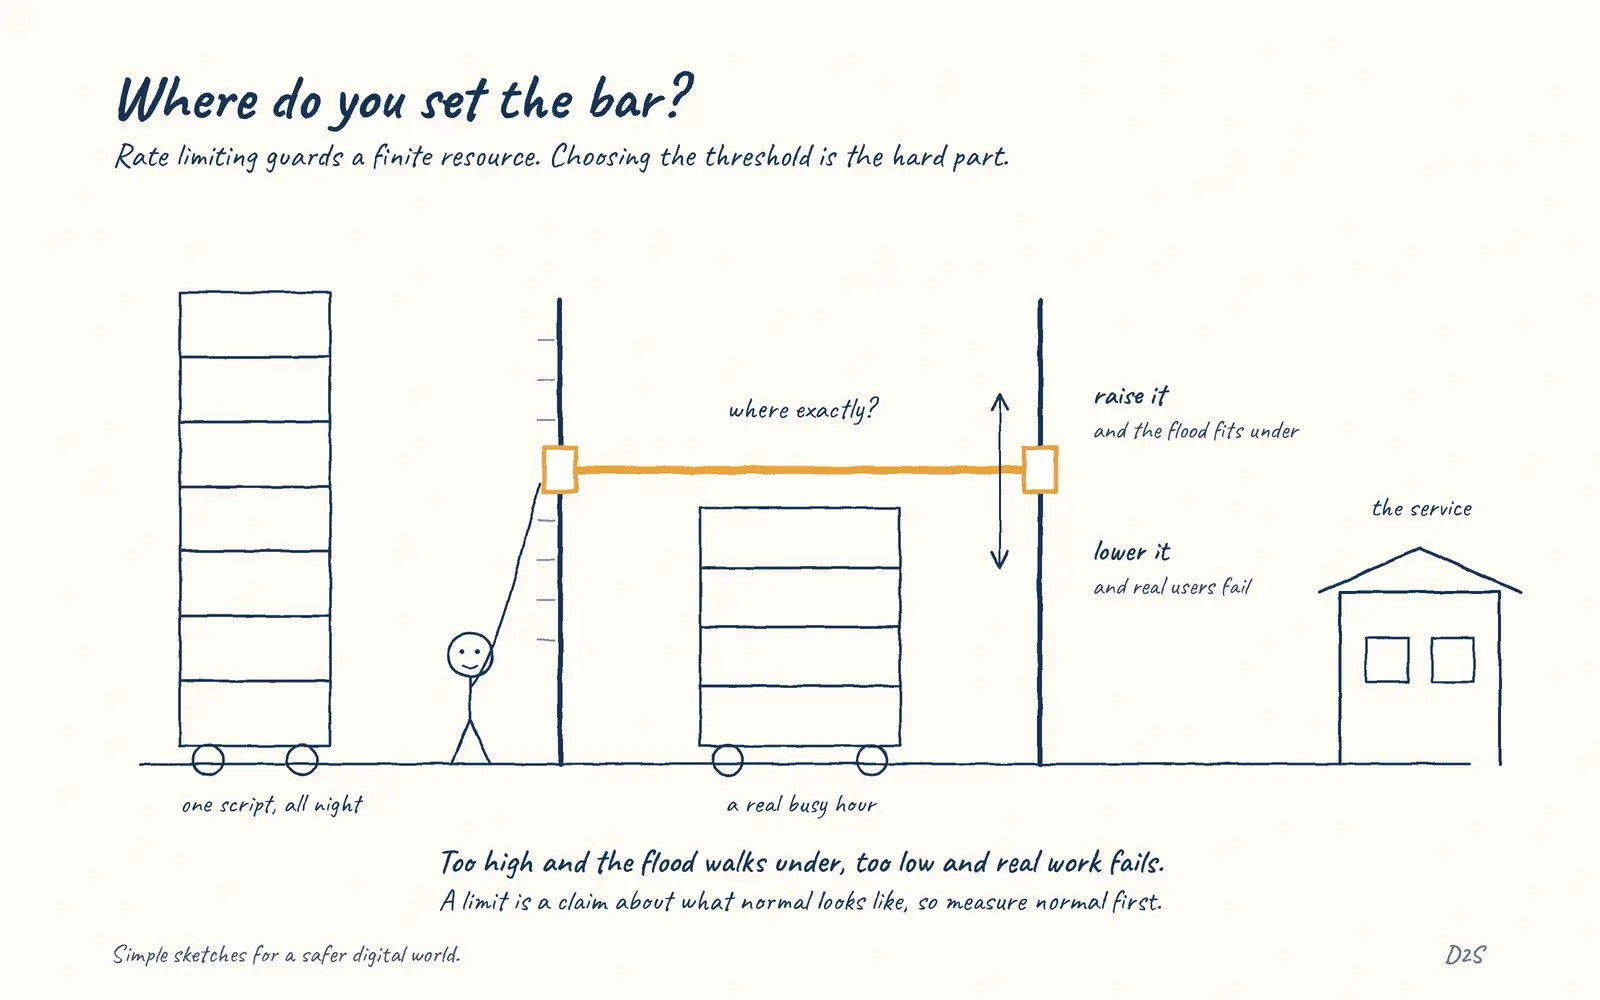 Rate limitsWhere do you set the bar?
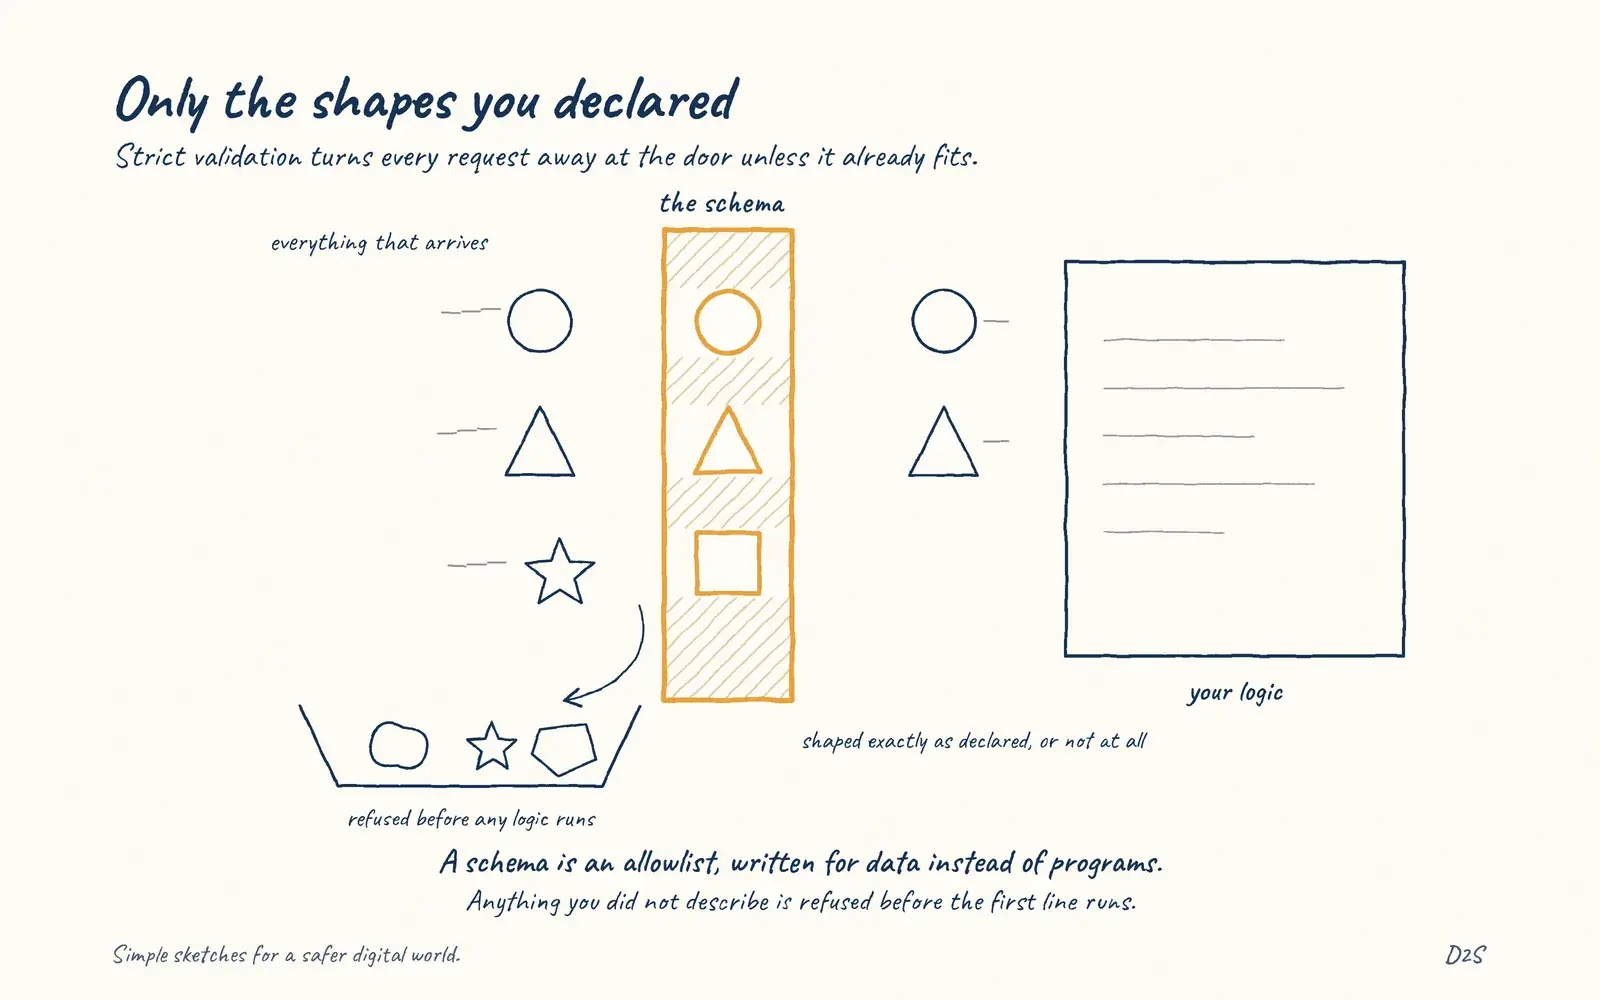 Schema validationOnly the shapes you declared
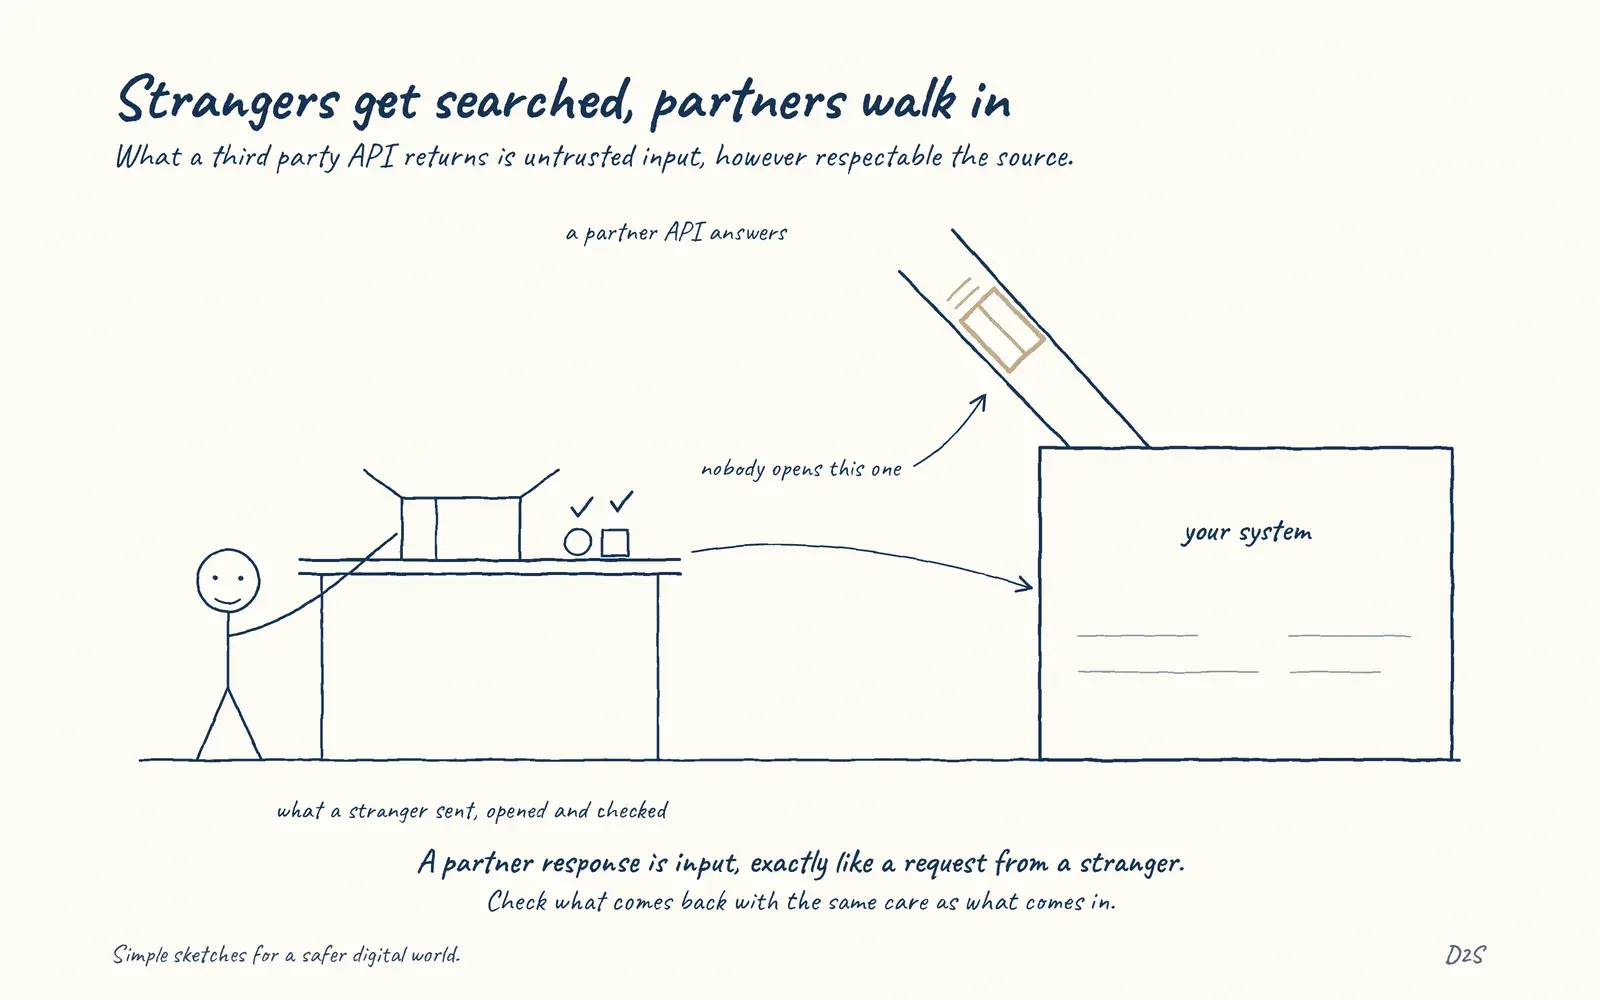 Unsafe consumption of APIsStrangers get searched, partners walk in
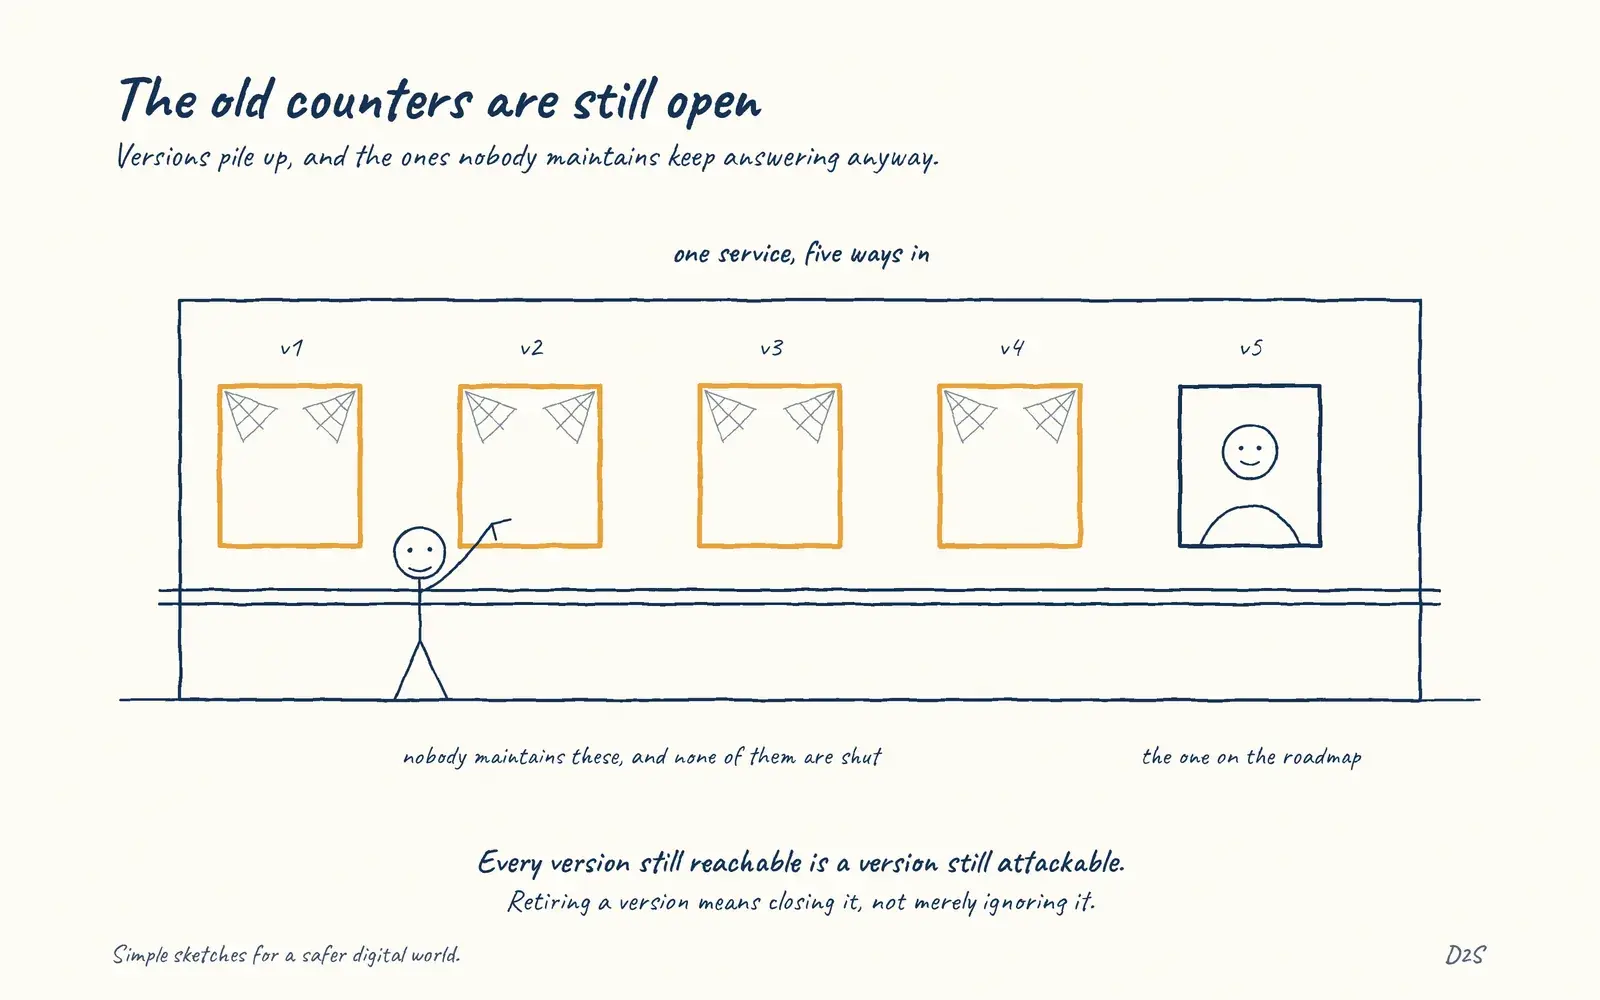 VersioningThe old counters are still open
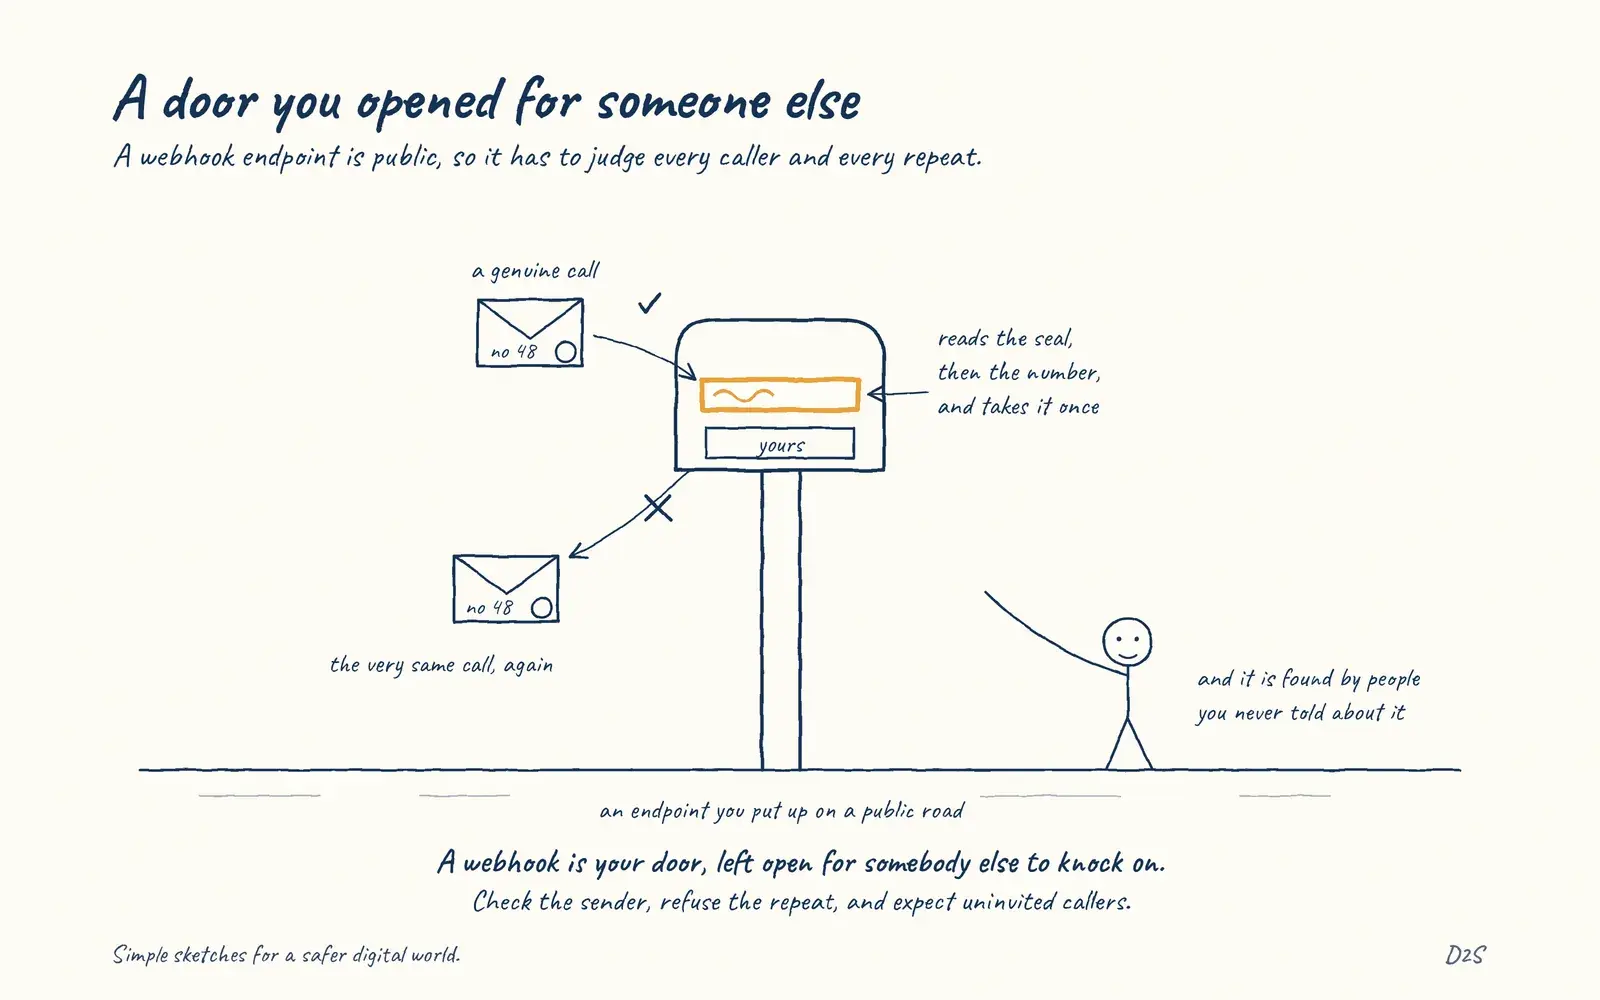 WebhooksA door you opened for someone else
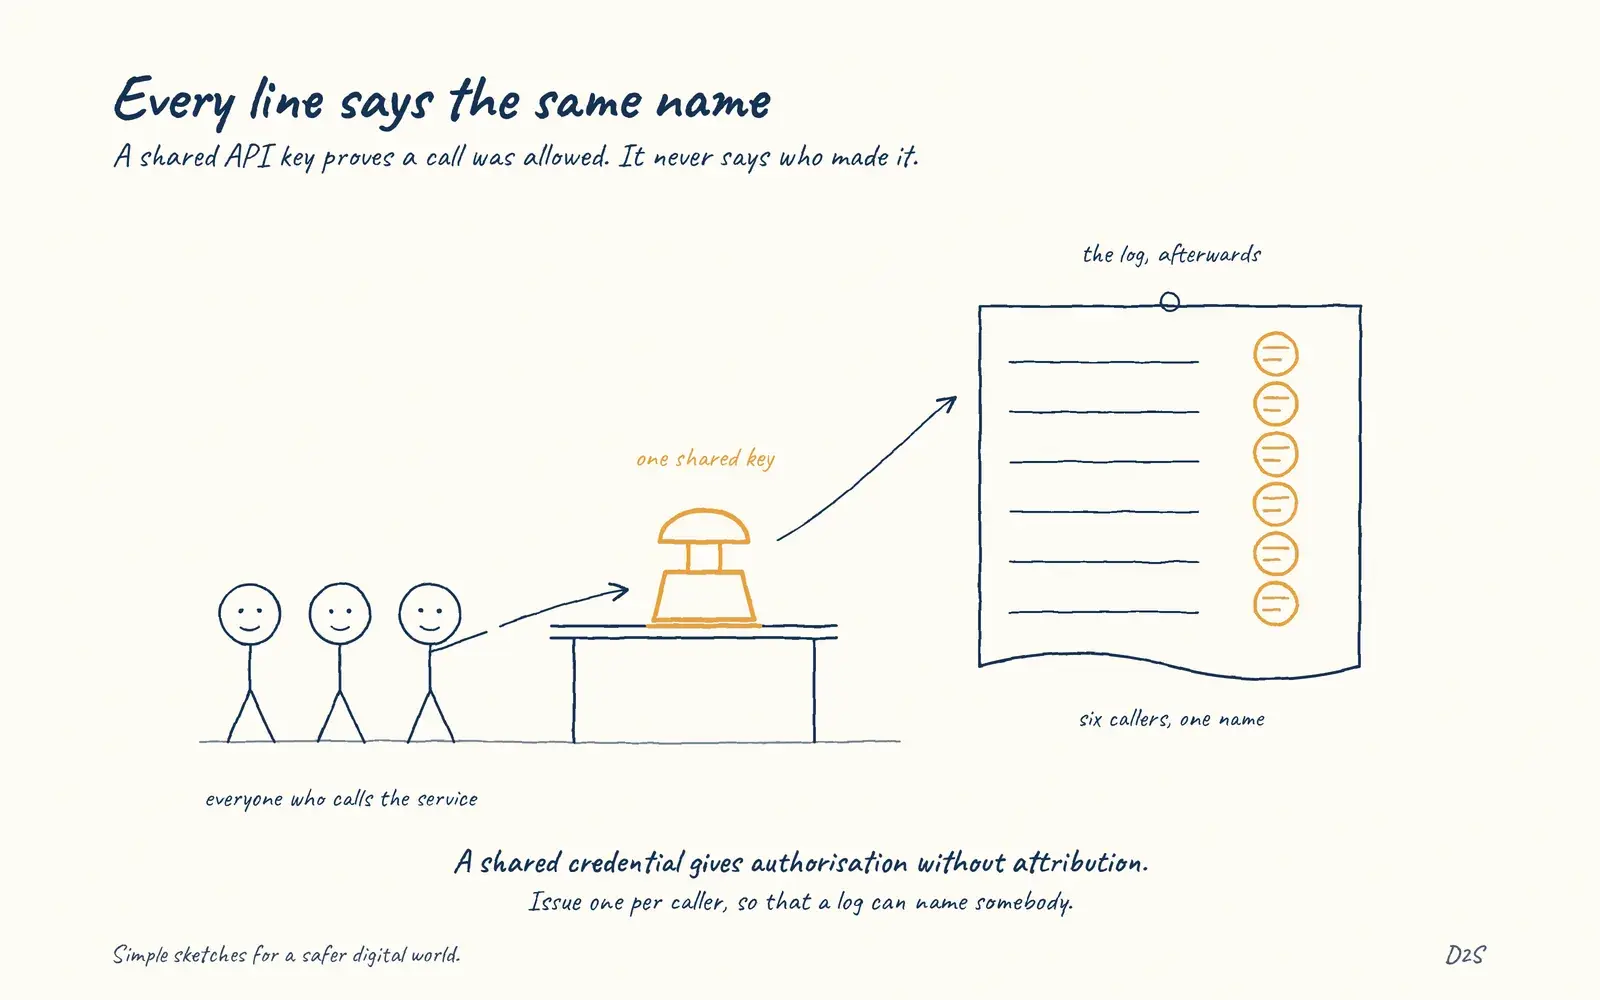 Shared API keys give coarse identityEvery line says the same name
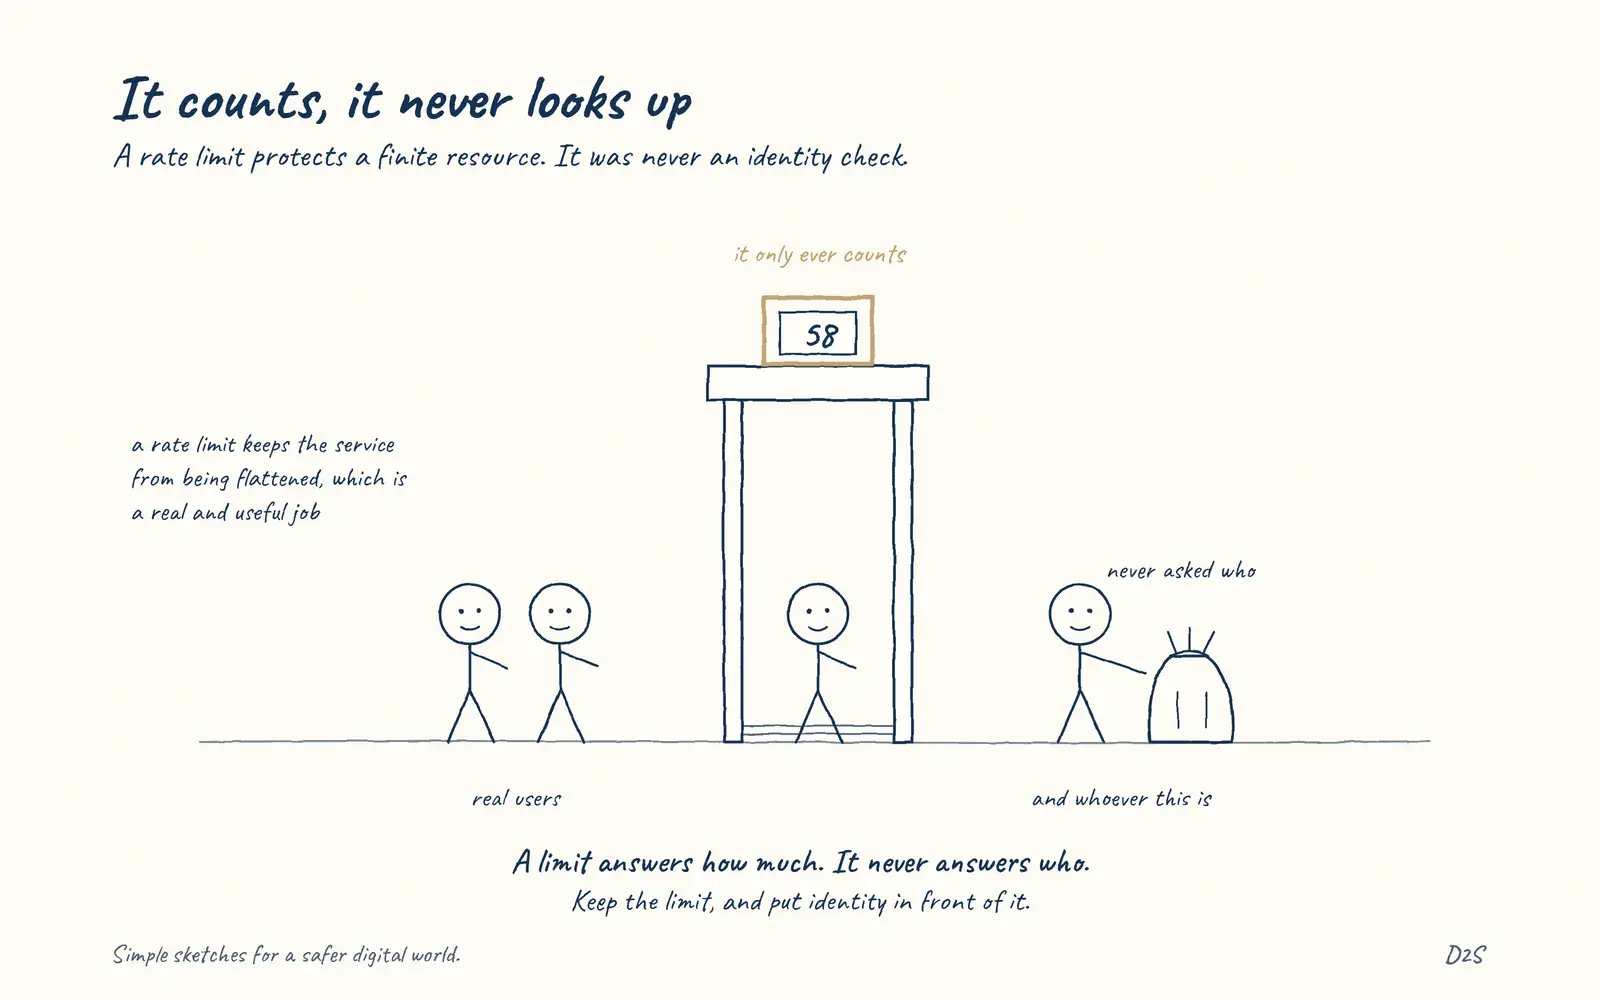 Rate limits are resource controls, not identity controlsIt counts, it never looks up
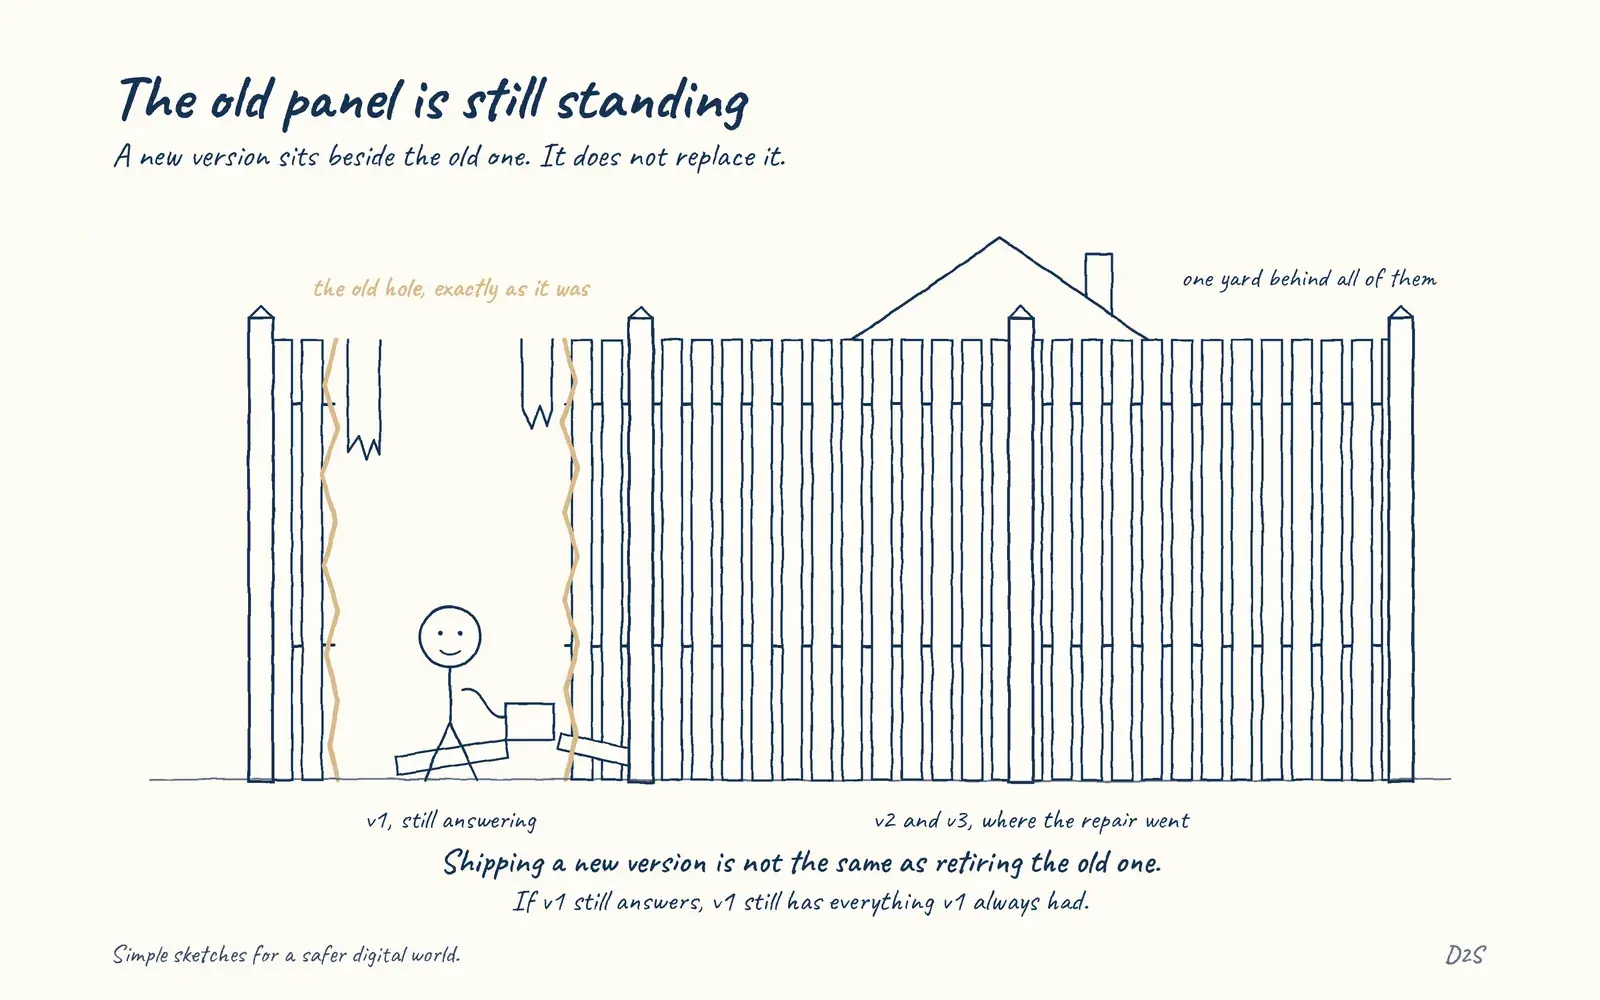 Old API versions can preserve old weaknessesThe old panel is still standing
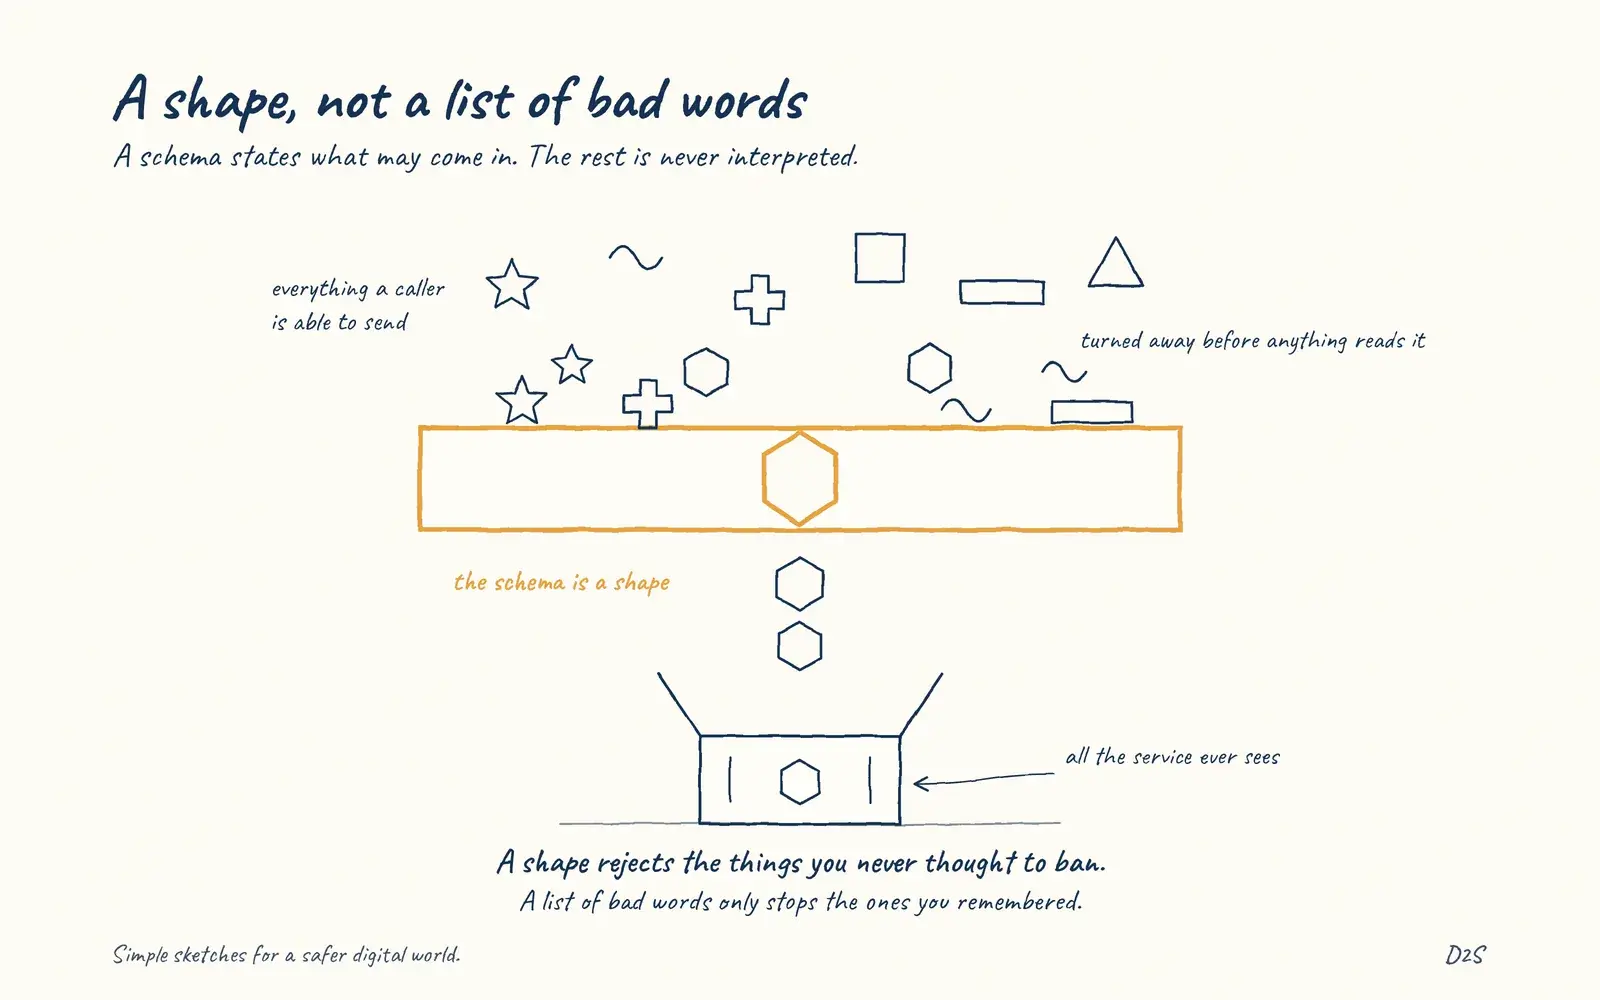 Schema validation narrows what an API interpretsA shape, not a list of bad words
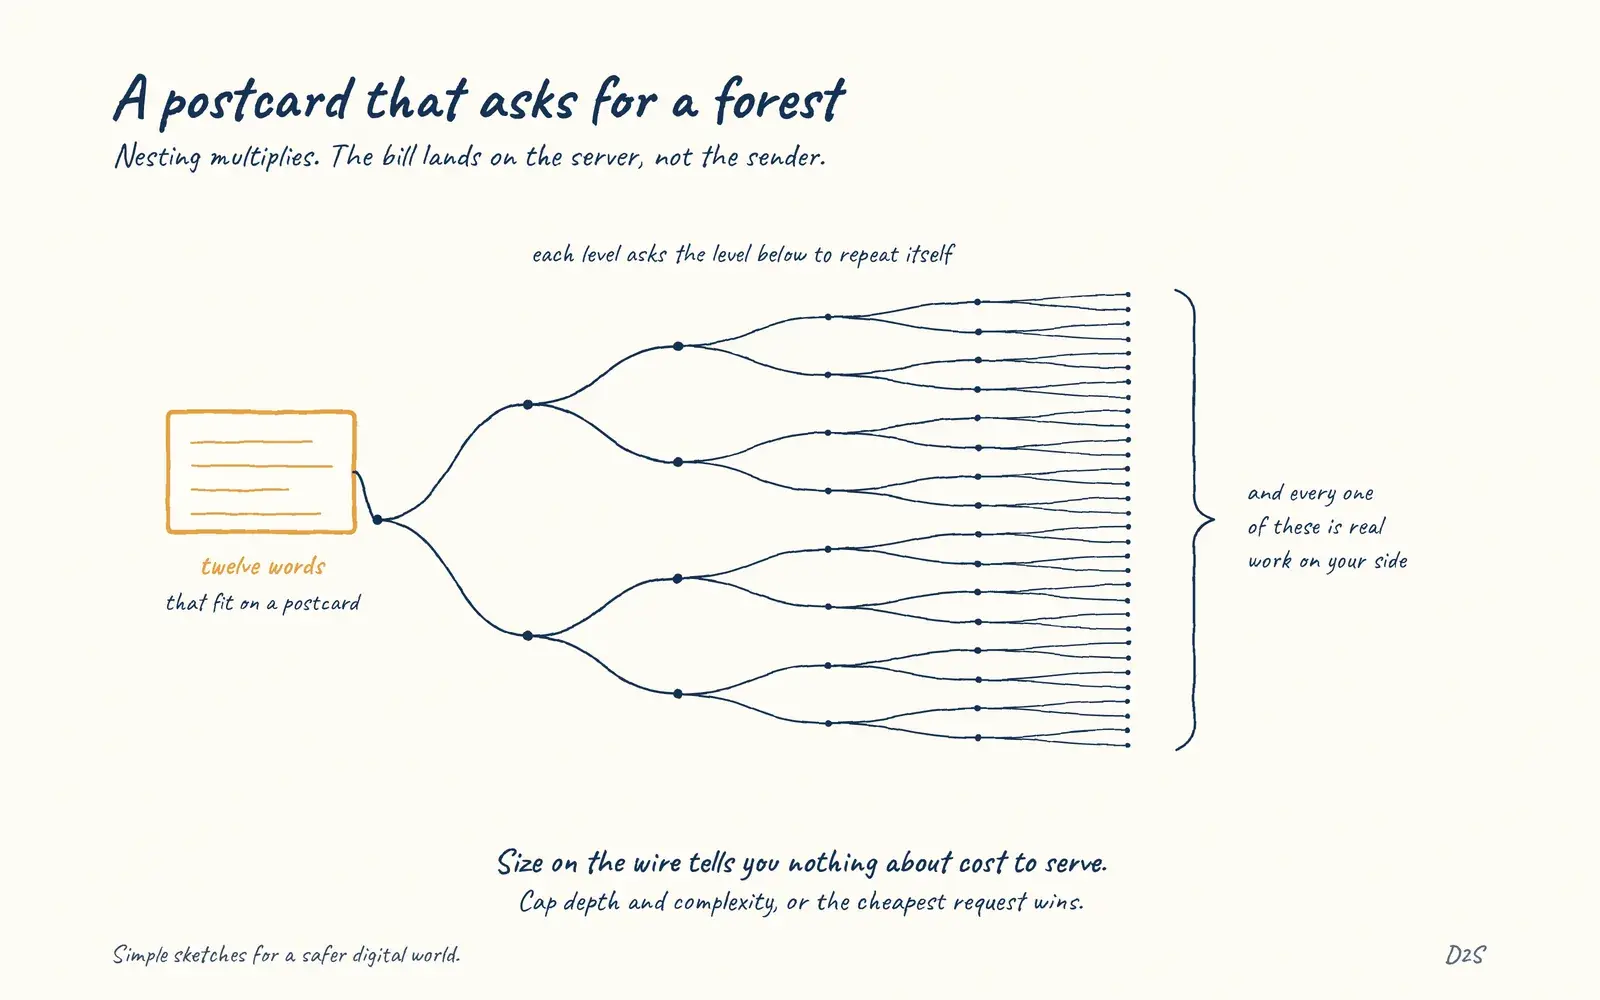 GraphQL depth can become a resource attackA postcard that asks for a forest
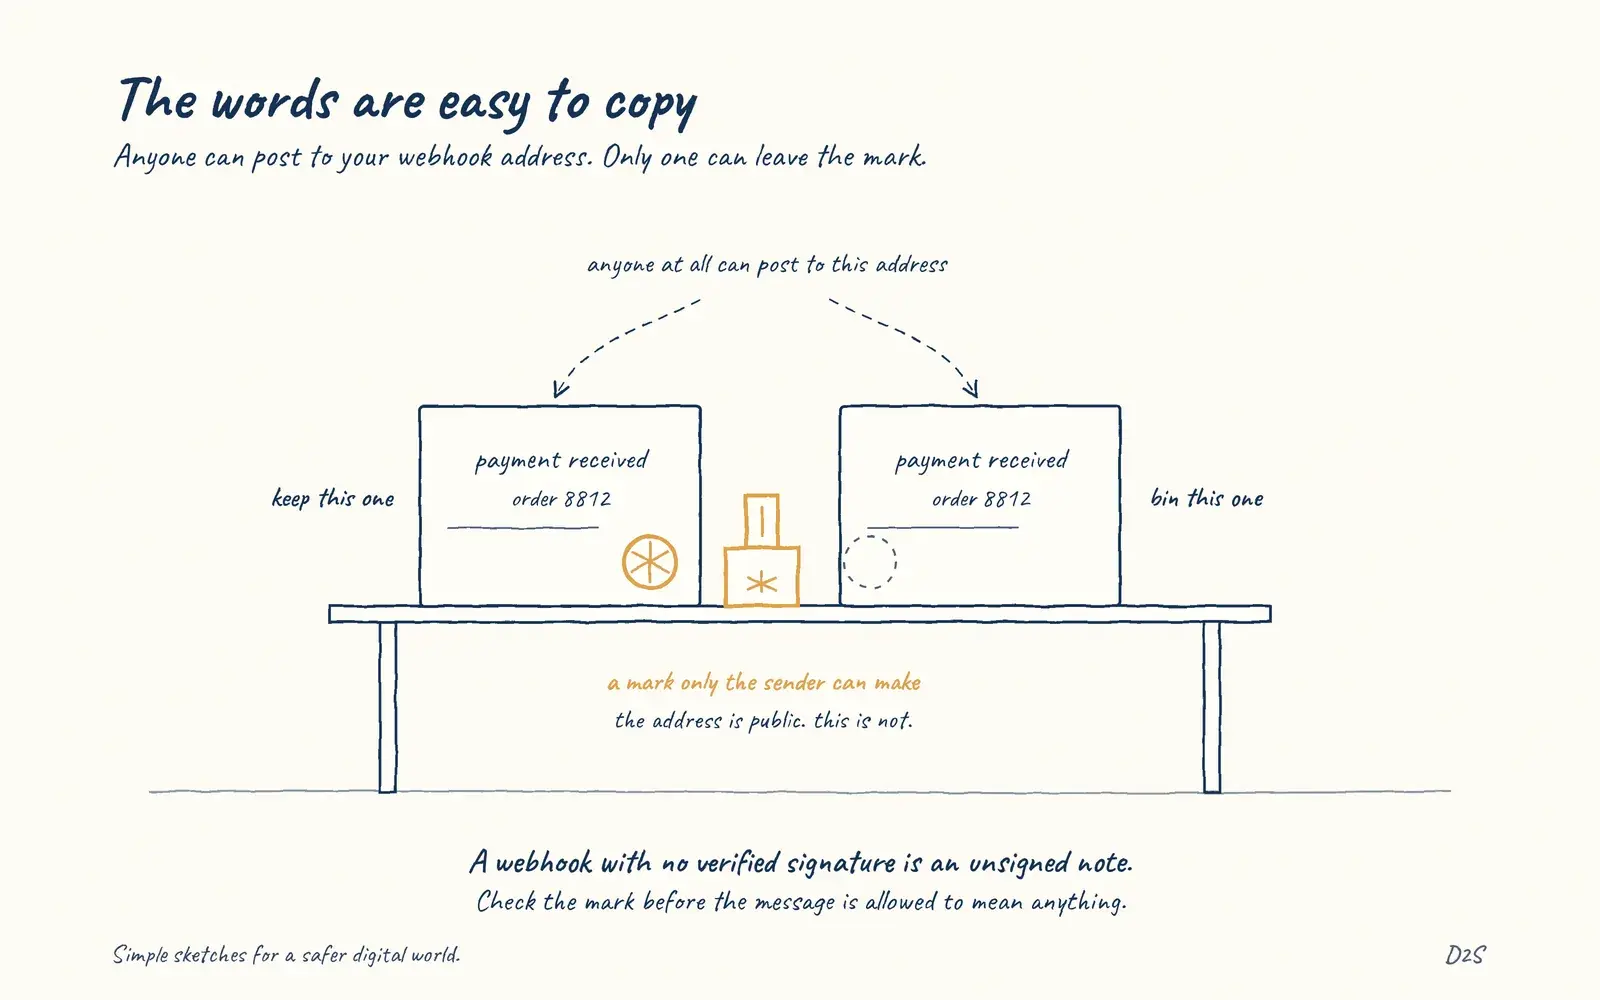 Webhook signatures authenticate provider messagesThe words are easy to copy
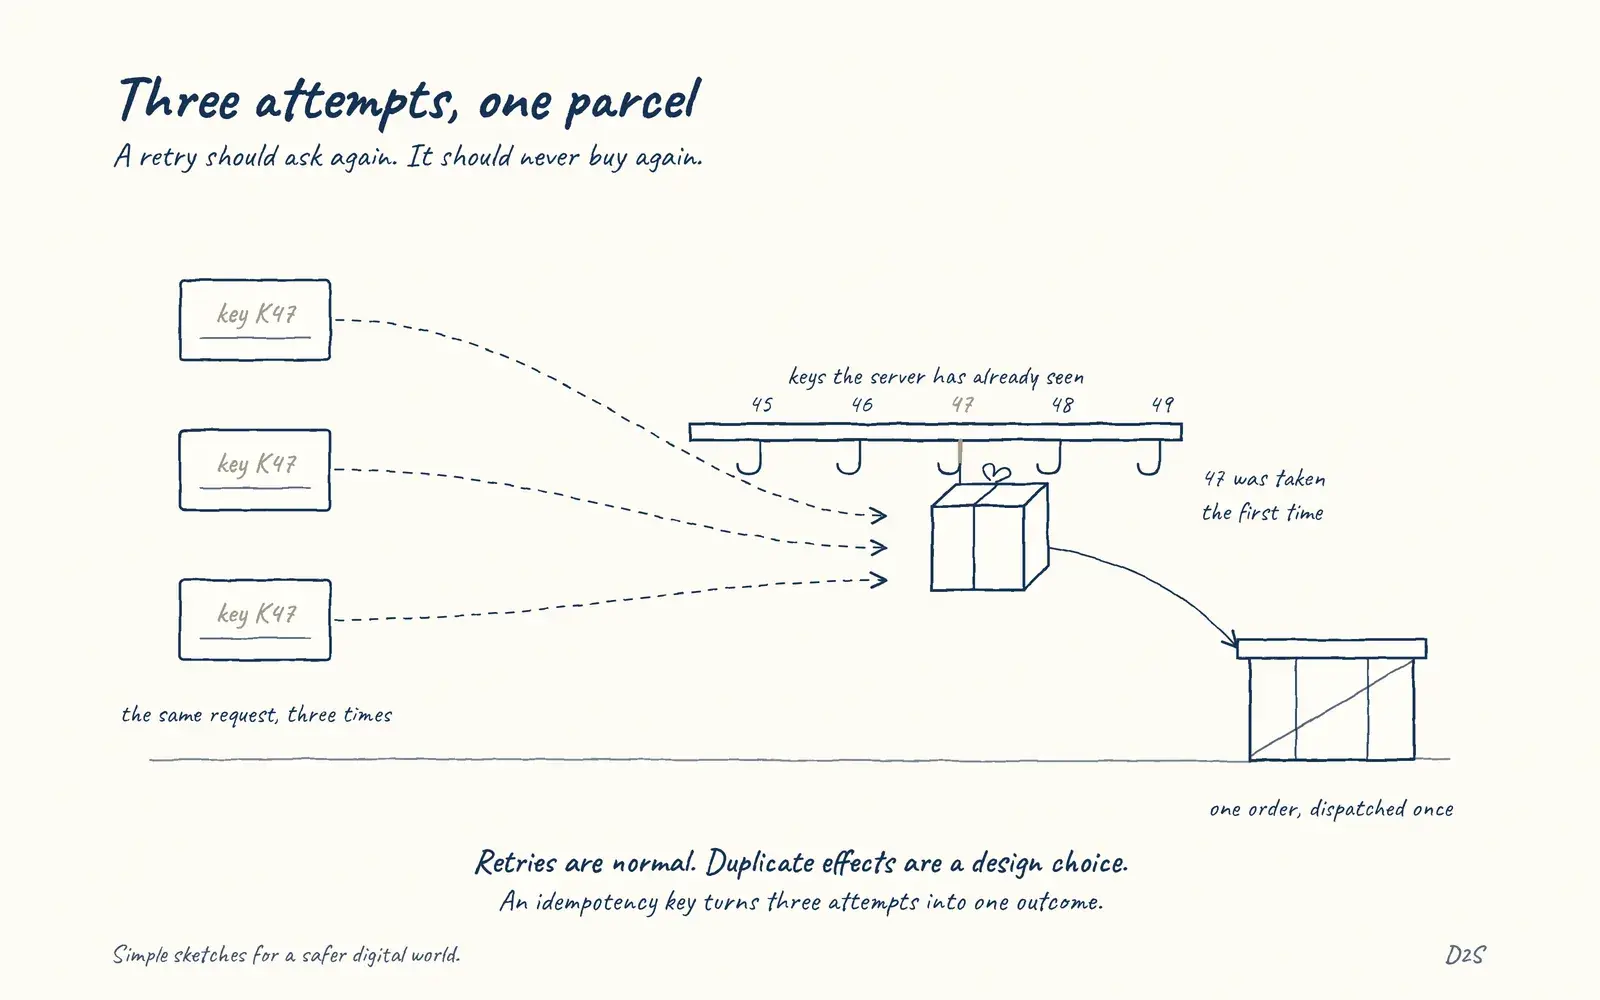 Idempotency prevents retries becoming duplicatesThree attempts, one parcel