
Email & browser security
The two places most users meet an attacker.
19 sketches
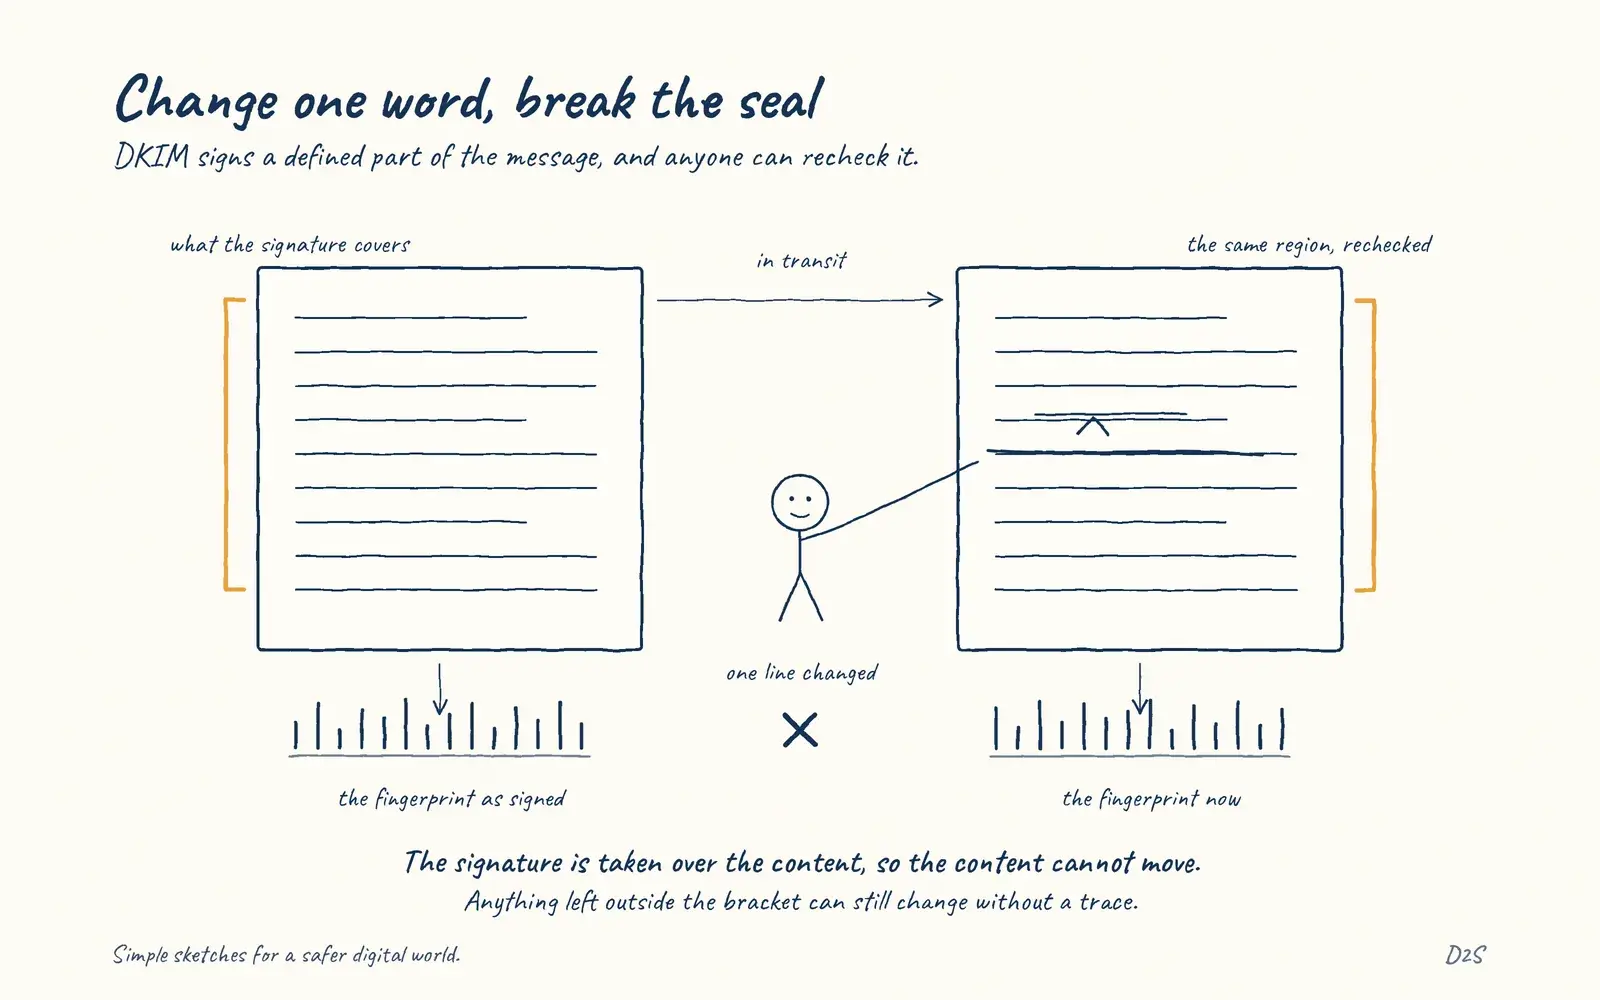 DKIM protects signed content against later modificationChange one word, break the seal
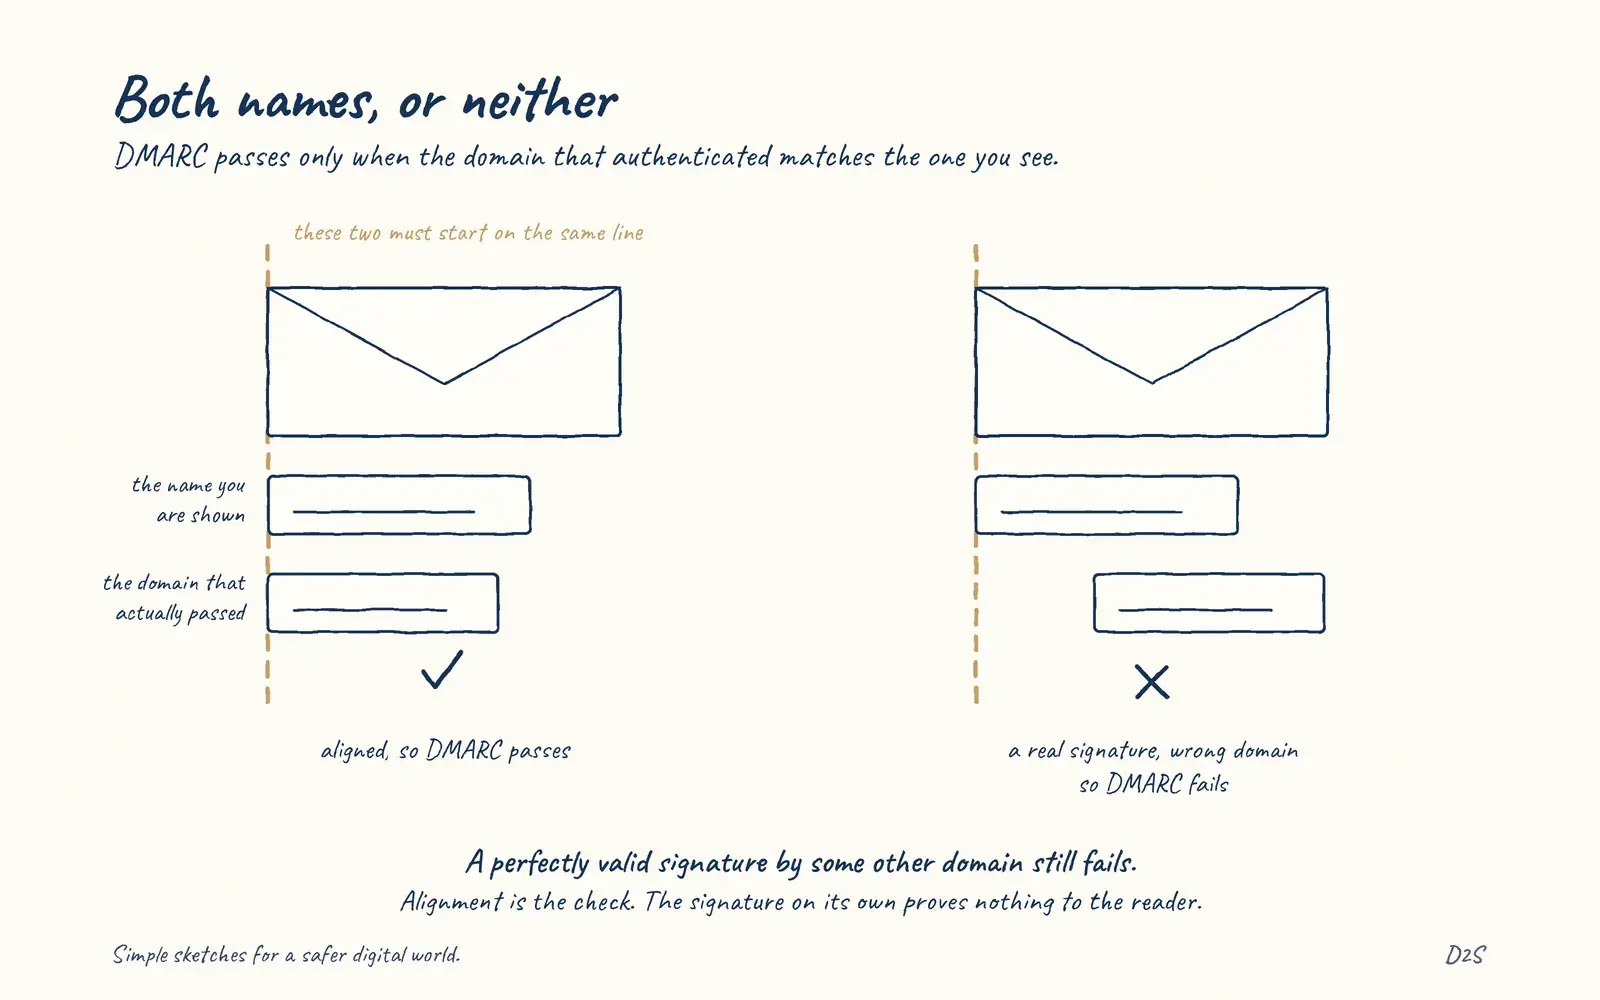 DMARC depends on alignmentBoth names, or neither
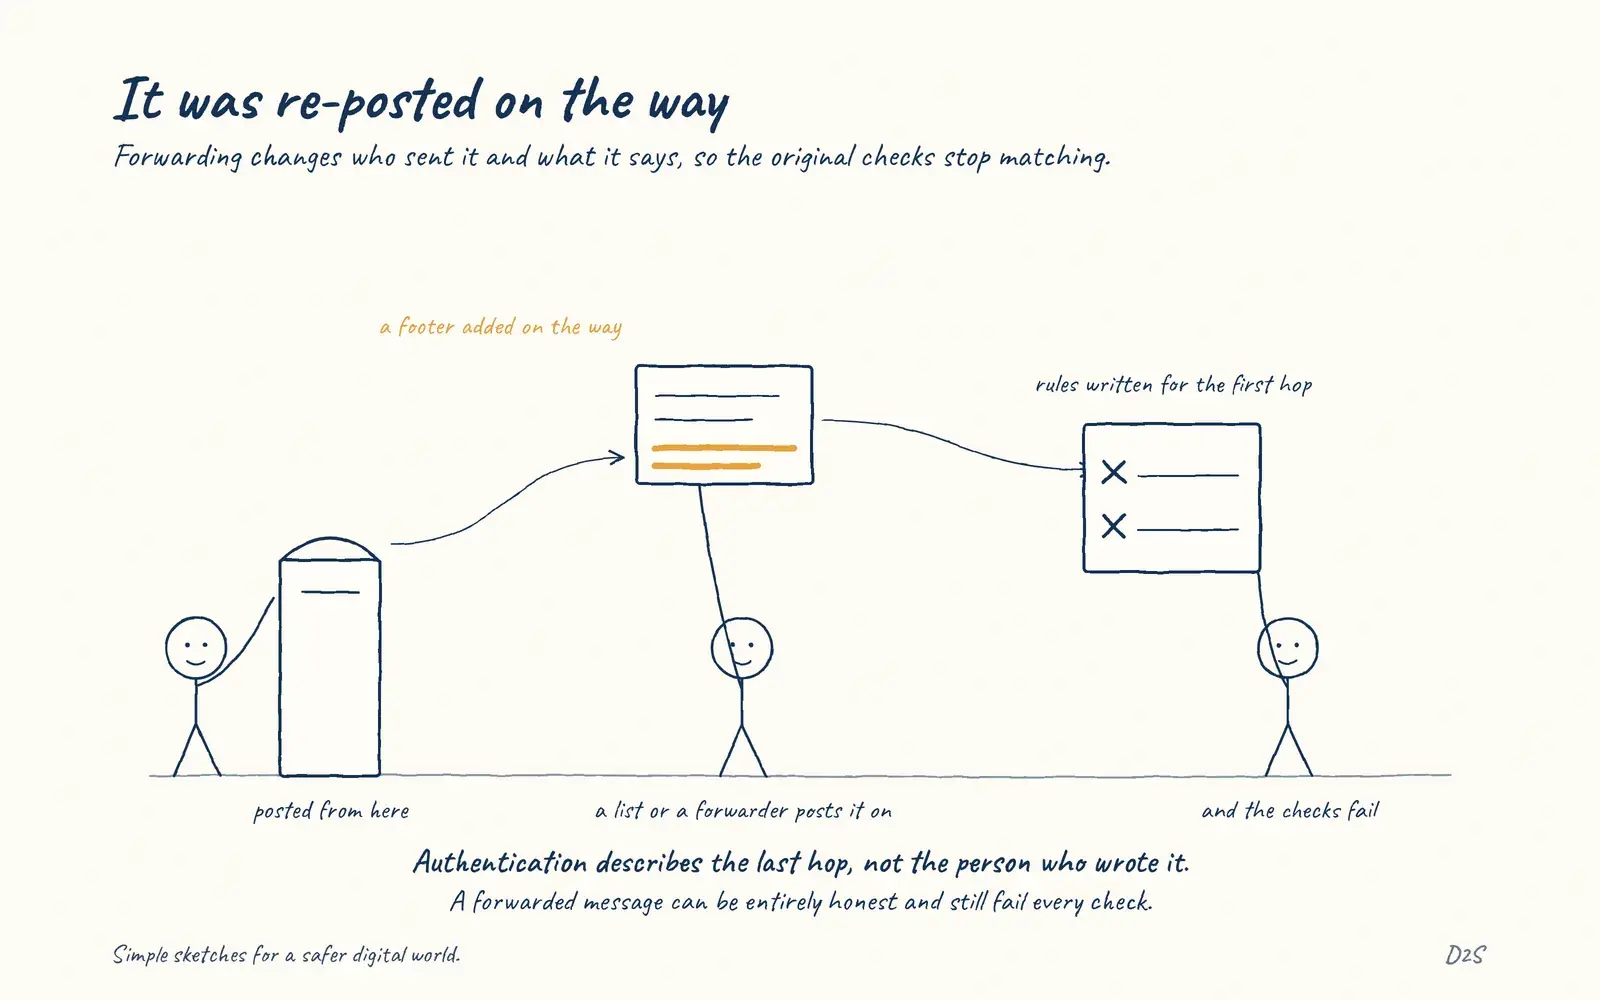 Forwarding can break email authentication assumptionsIt was re-posted on the way
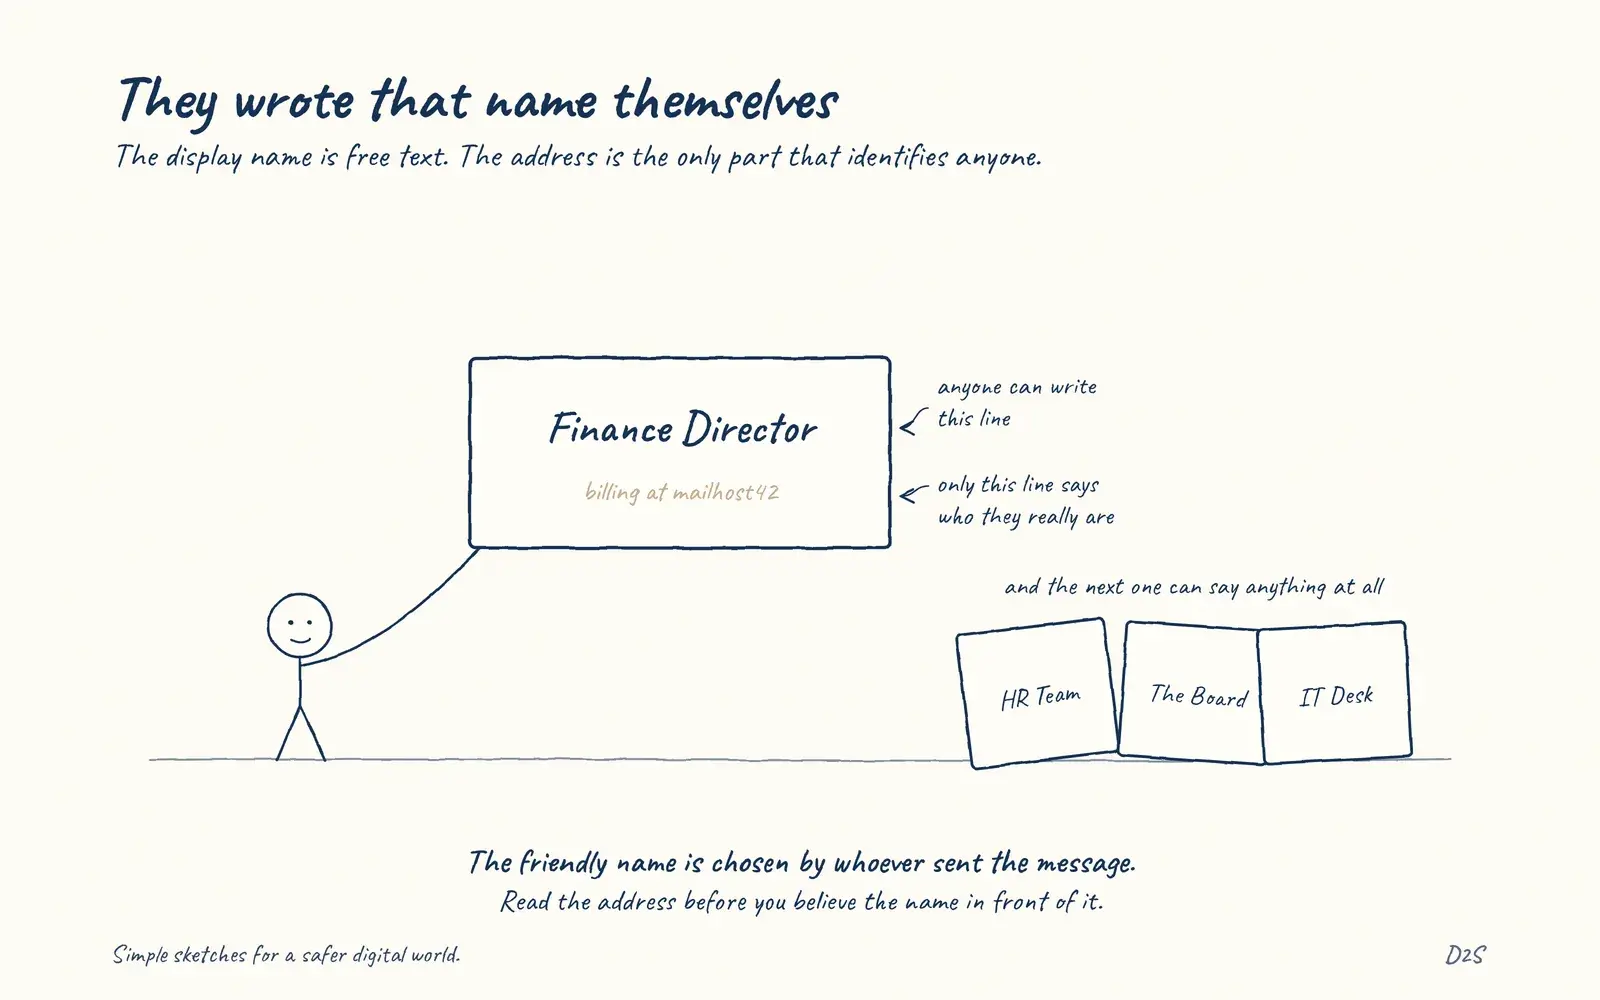 A display name is not an email addressThey wrote that name themselves
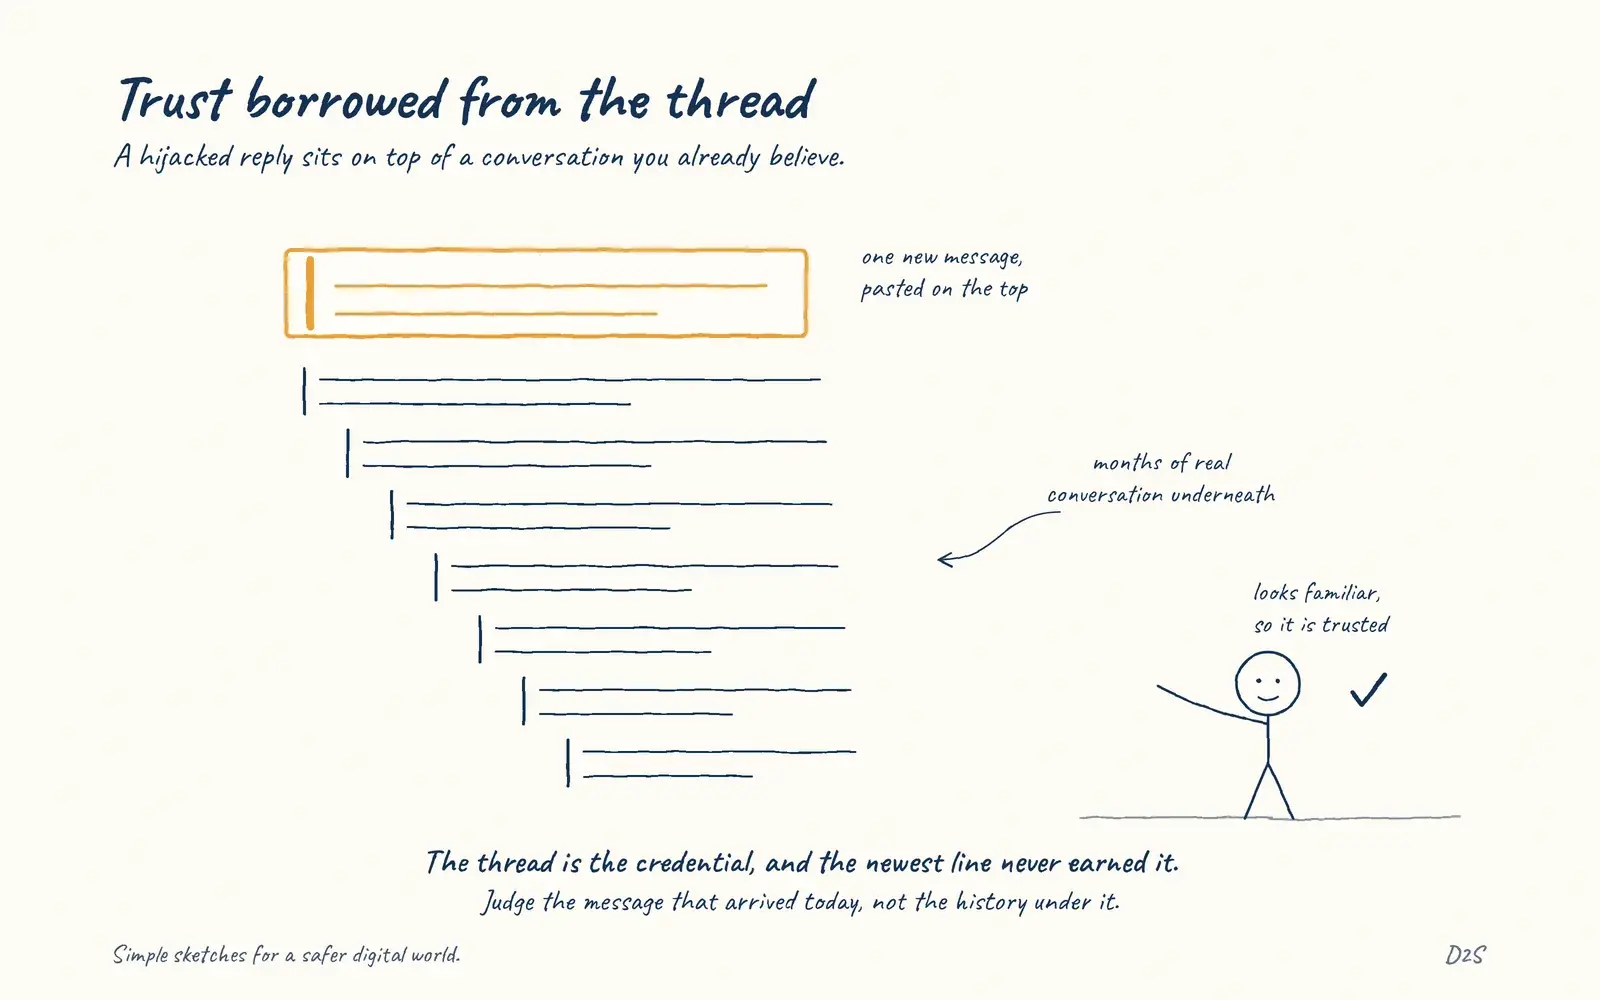 Reply-chain hijacking borrows existing trustTrust borrowed from the thread
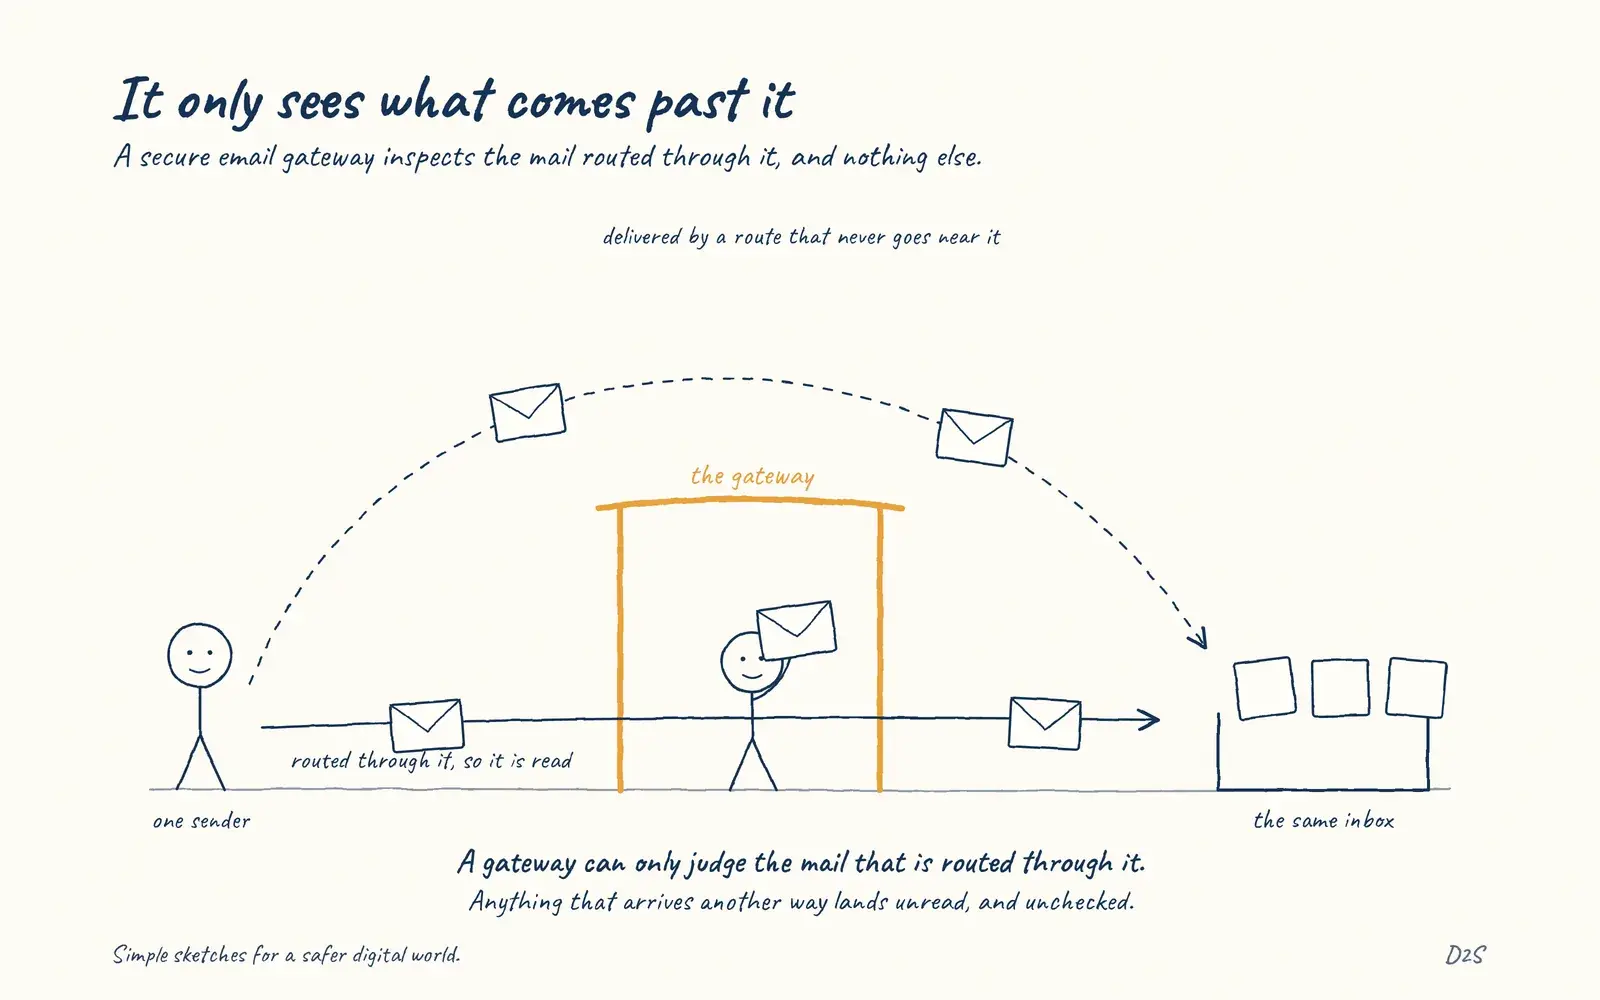 Secure email gateways see only traffic that reaches themIt only sees what comes past it
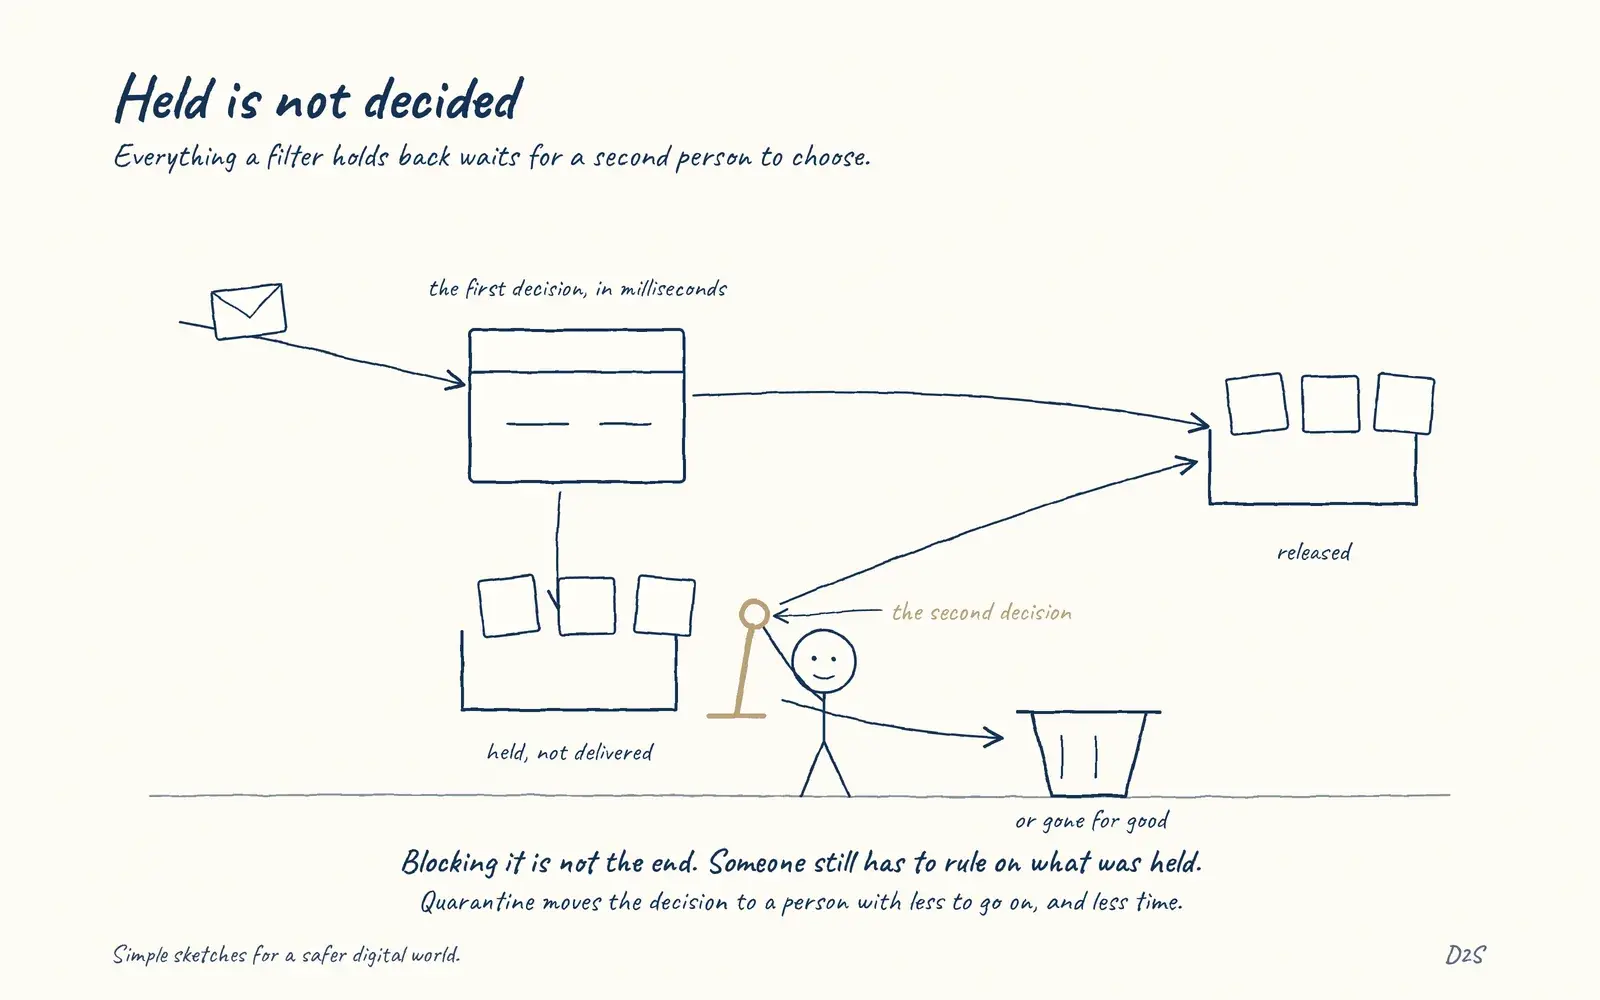 Quarantine creates a second security decisionHeld is not decided
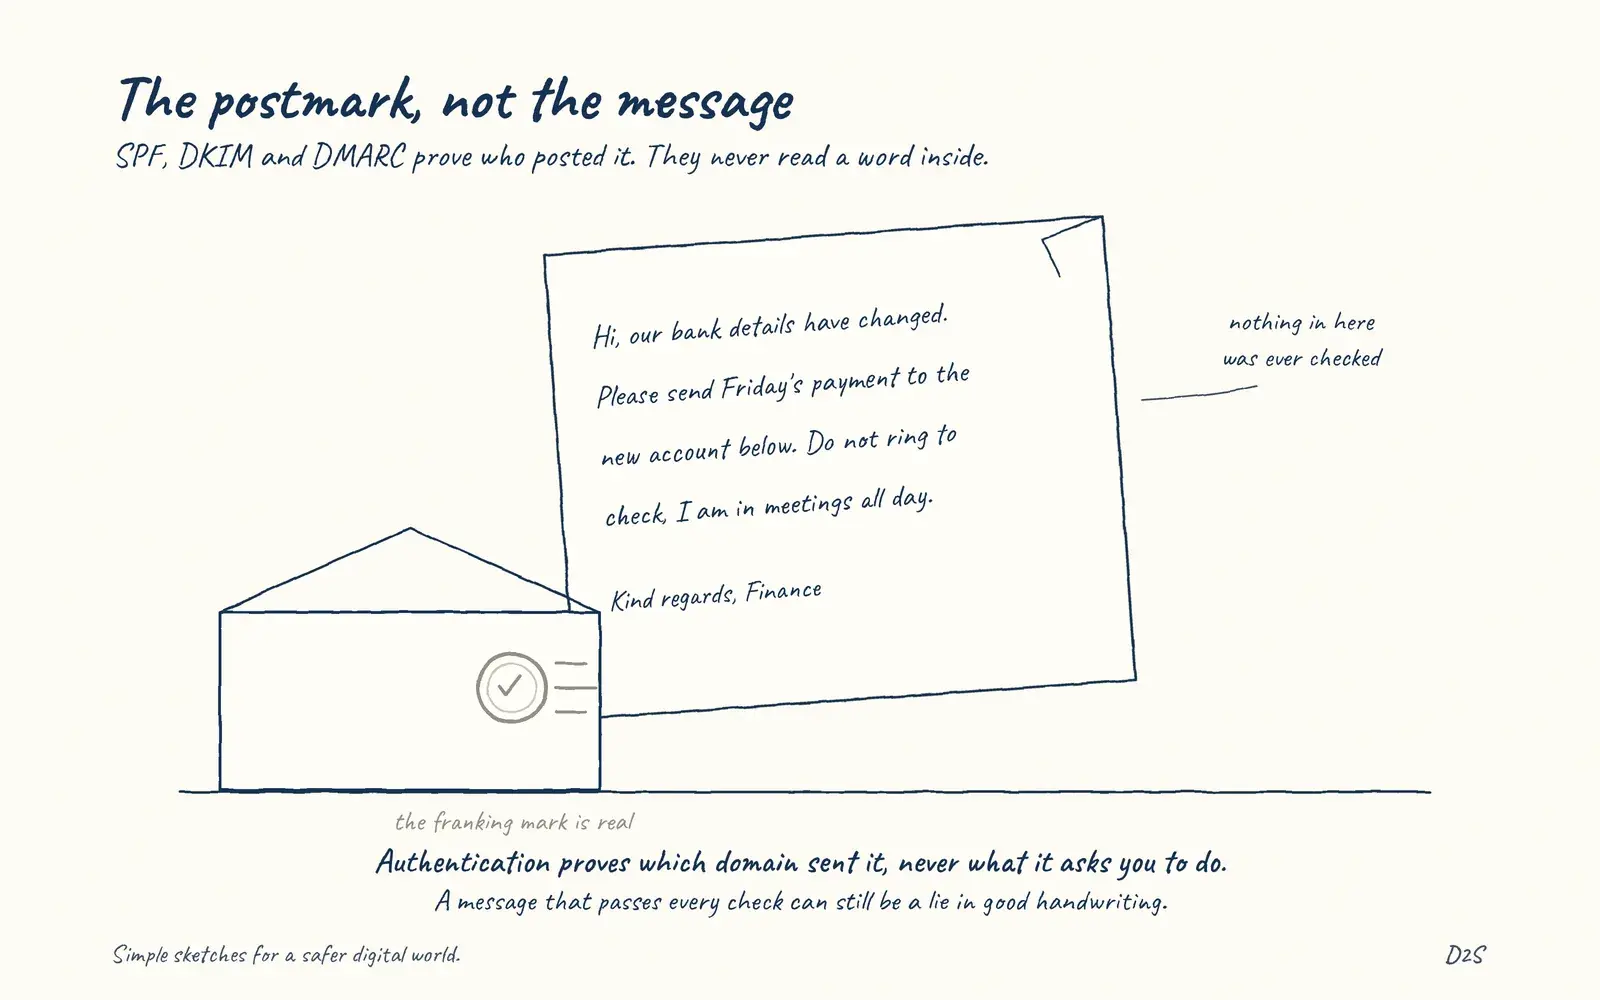 Authenticated email can still be maliciousThe postmark, not the message
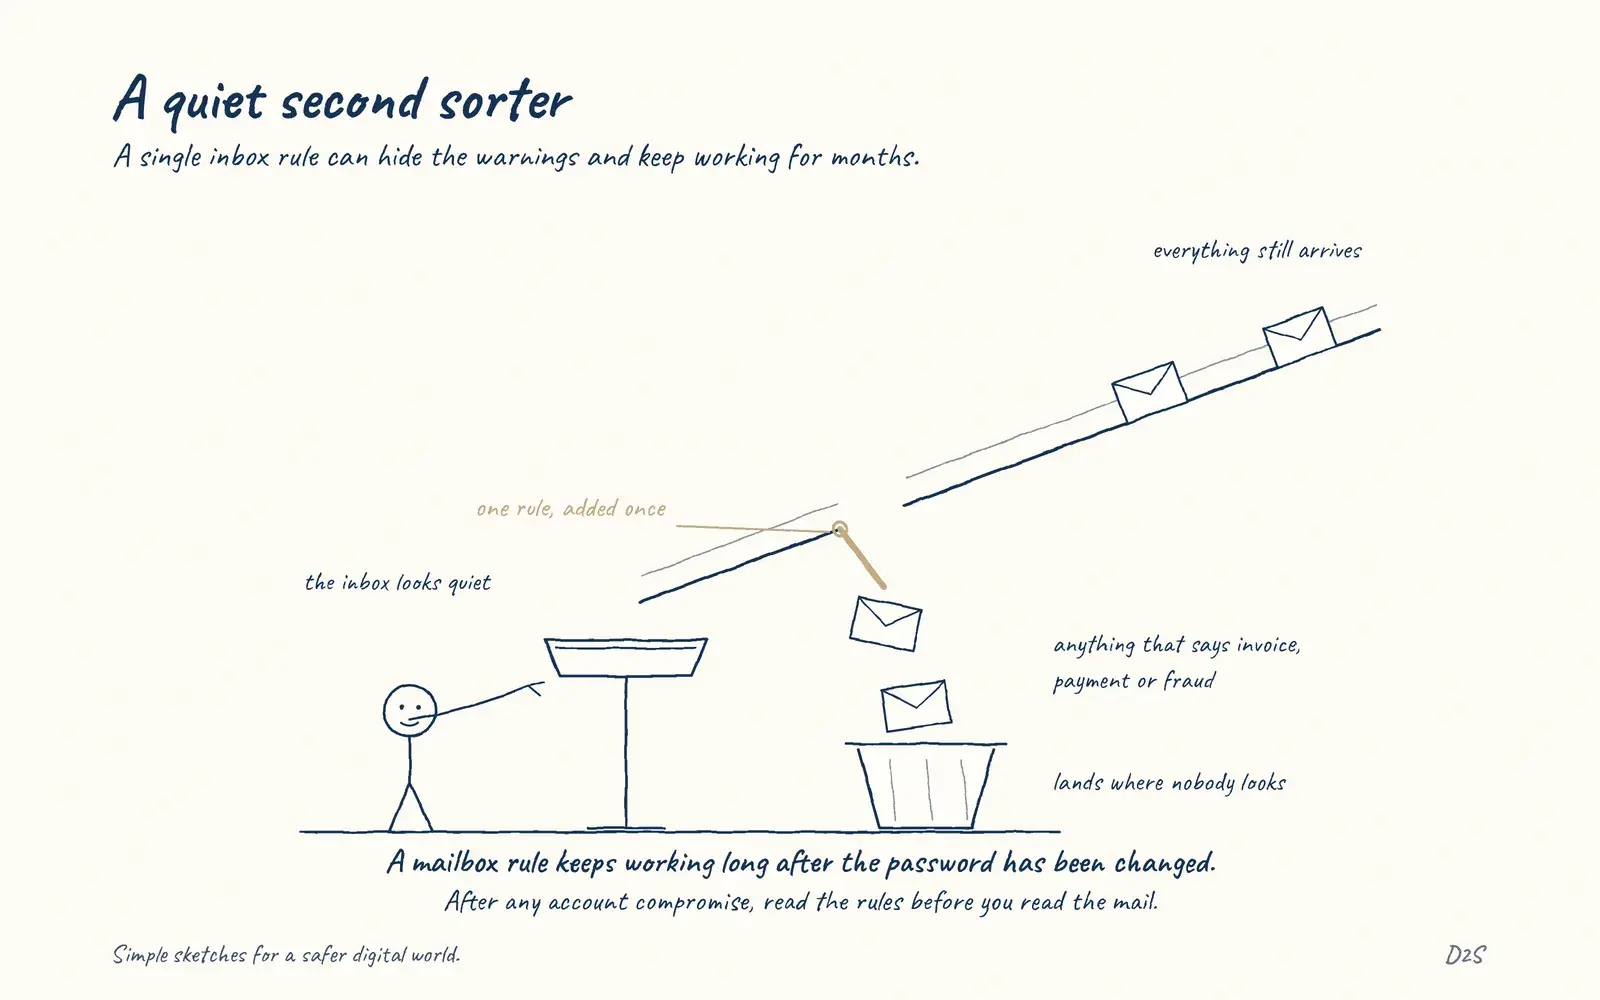 Mailbox rules can become persistenceA quiet second sorter
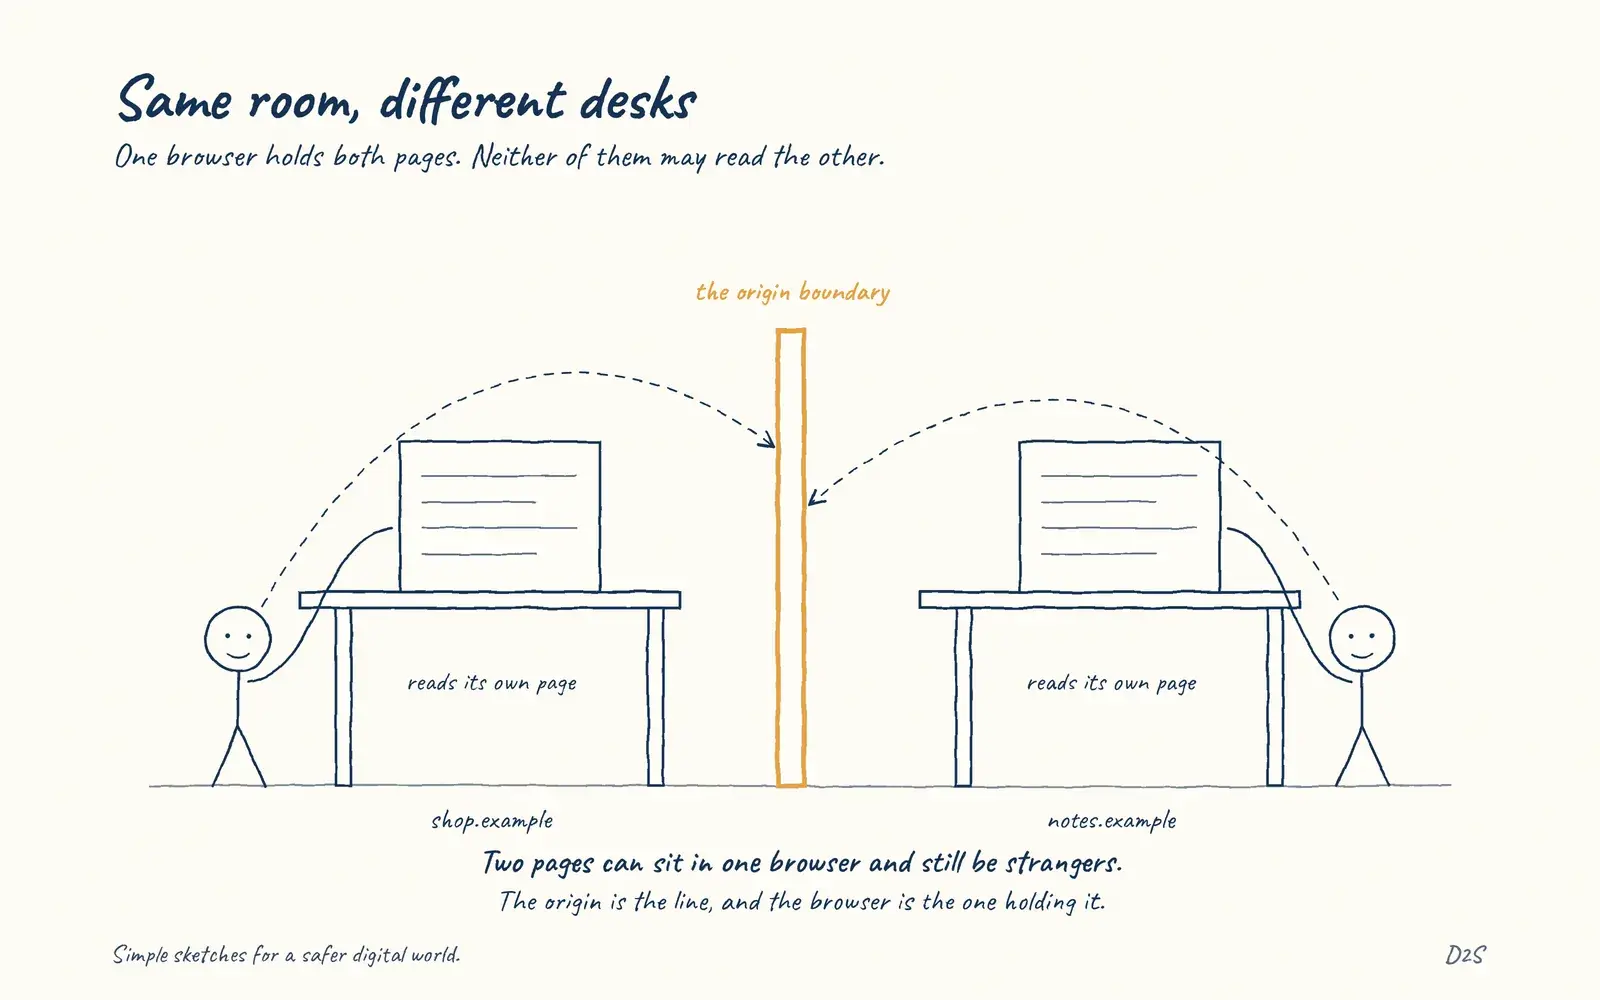 Same-origin policy limits which pages can read each otherSame room, different desks
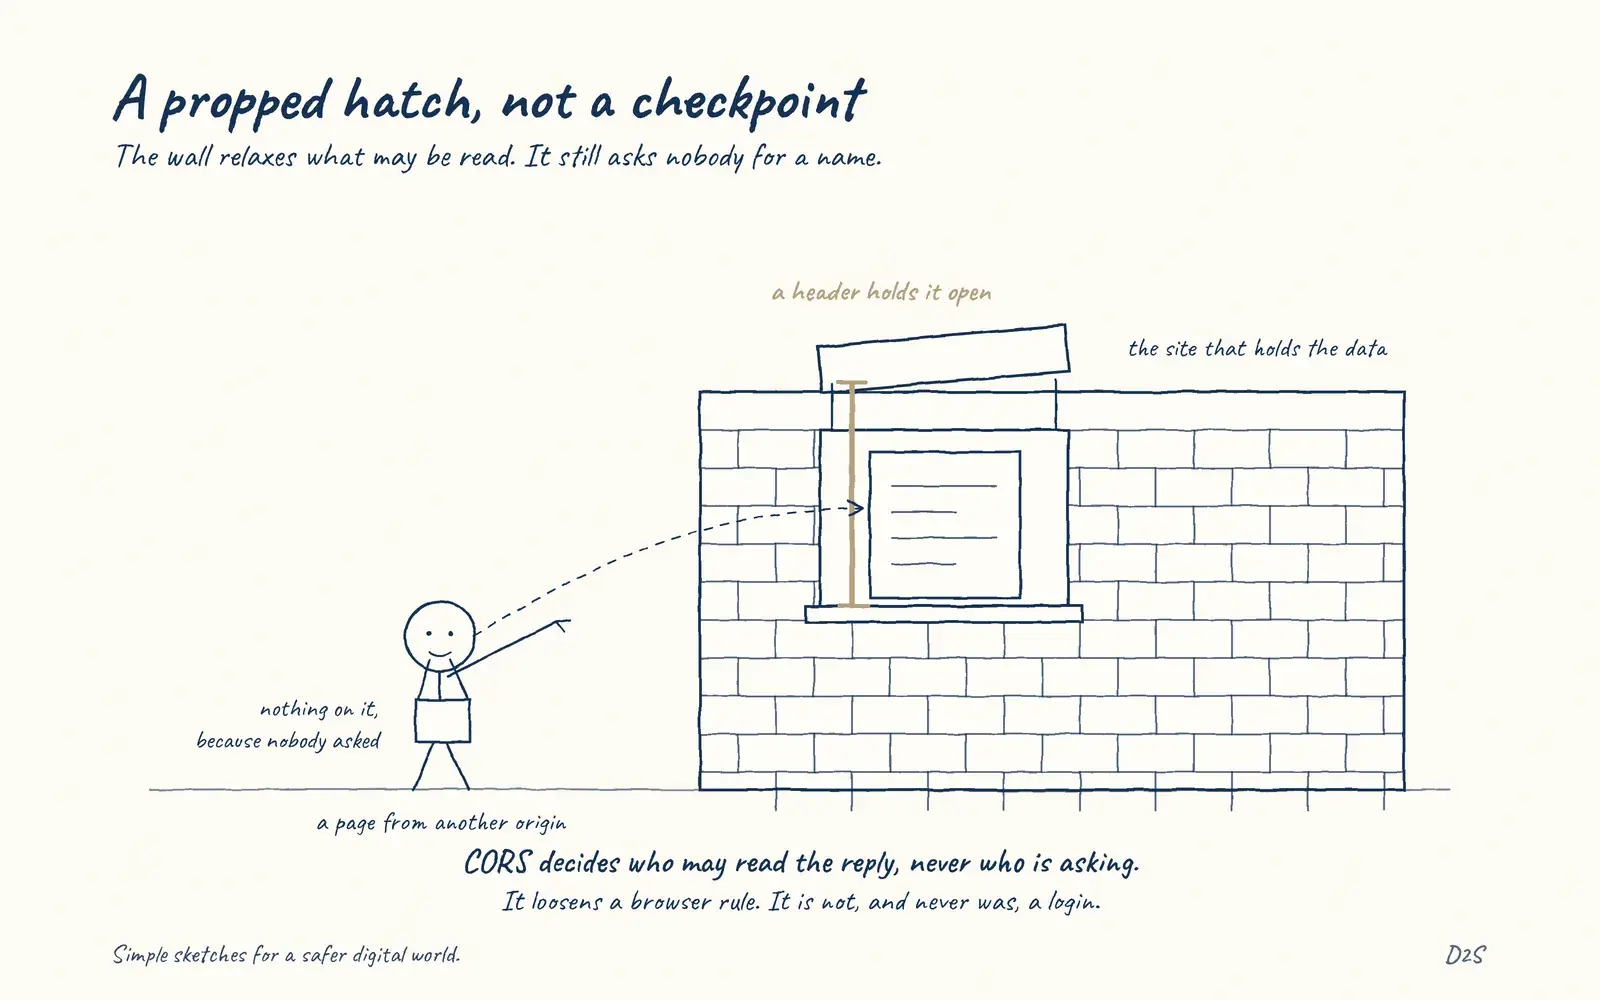 CORS relaxes browser reading rules, not authenticationA propped hatch, not a checkpoint
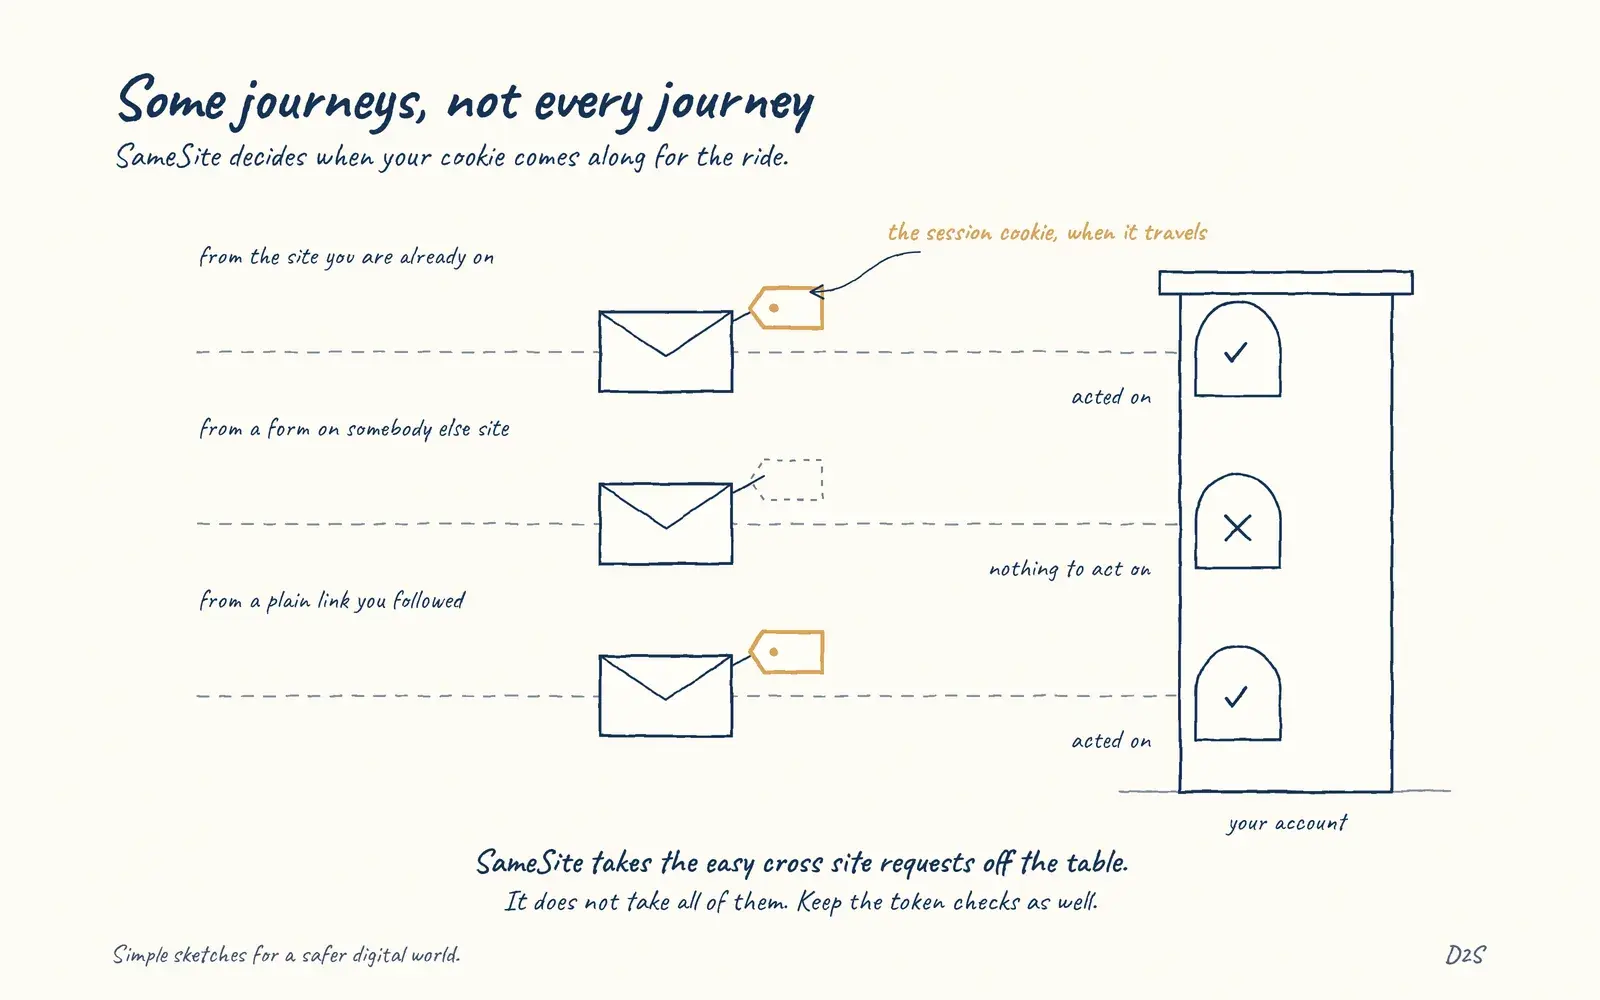 SameSite cookies reduce some cross-site request risksSome journeys, not every journey
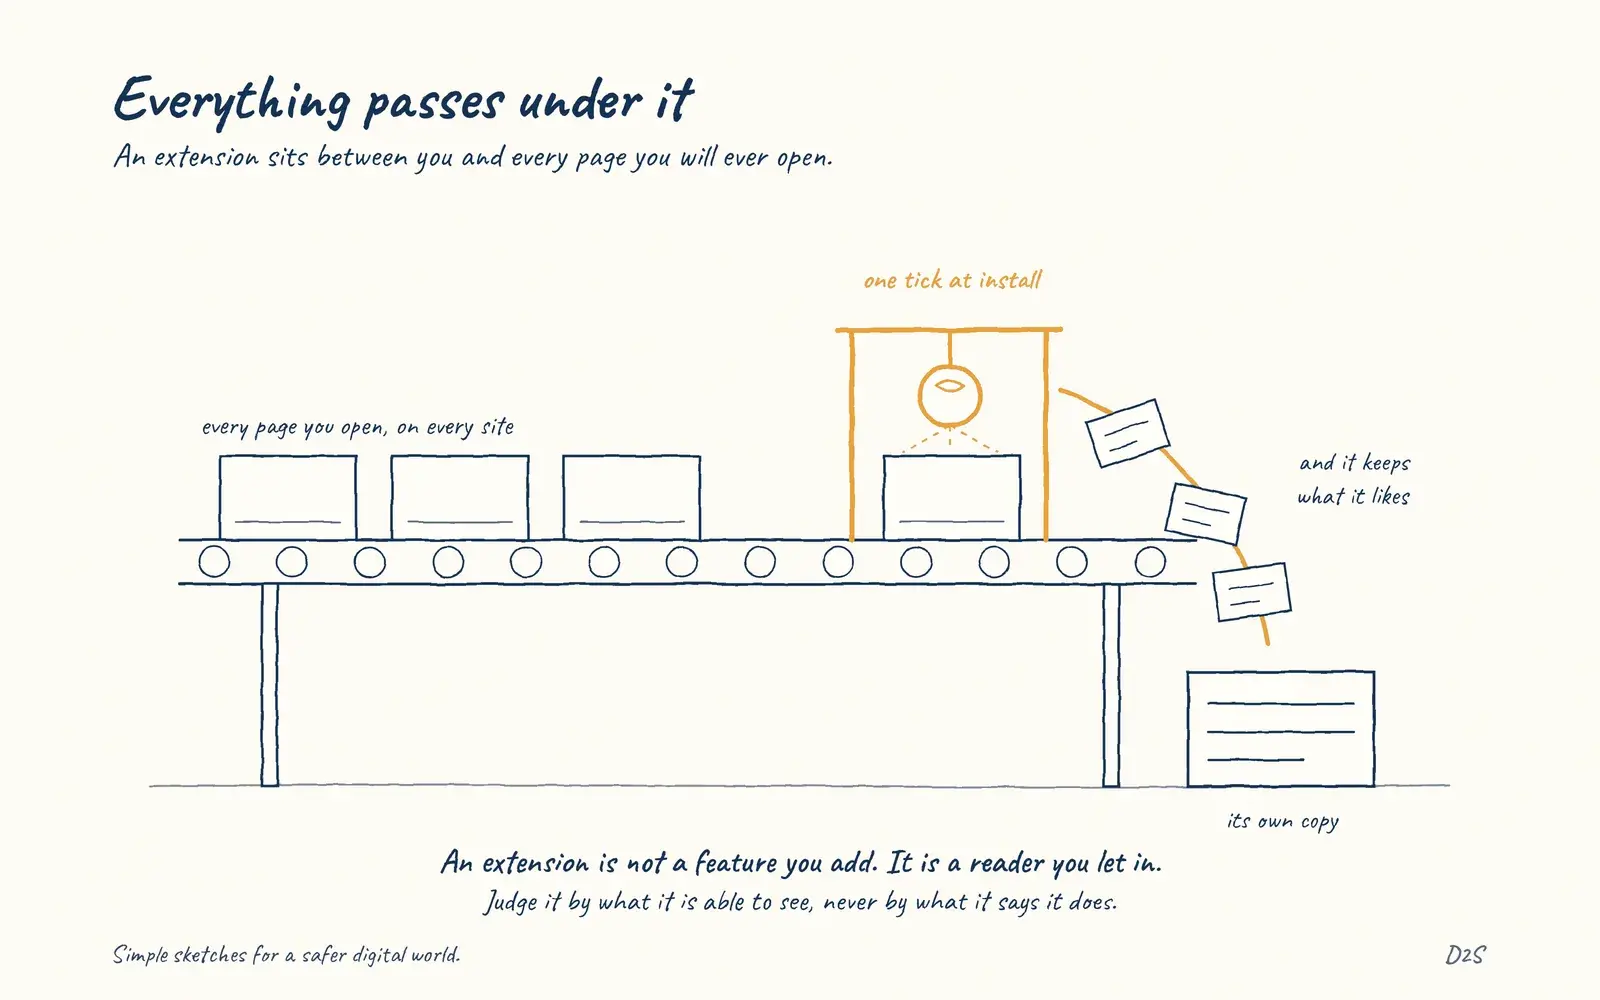 Browser extensions inherit powerful visibilityEverything passes under it
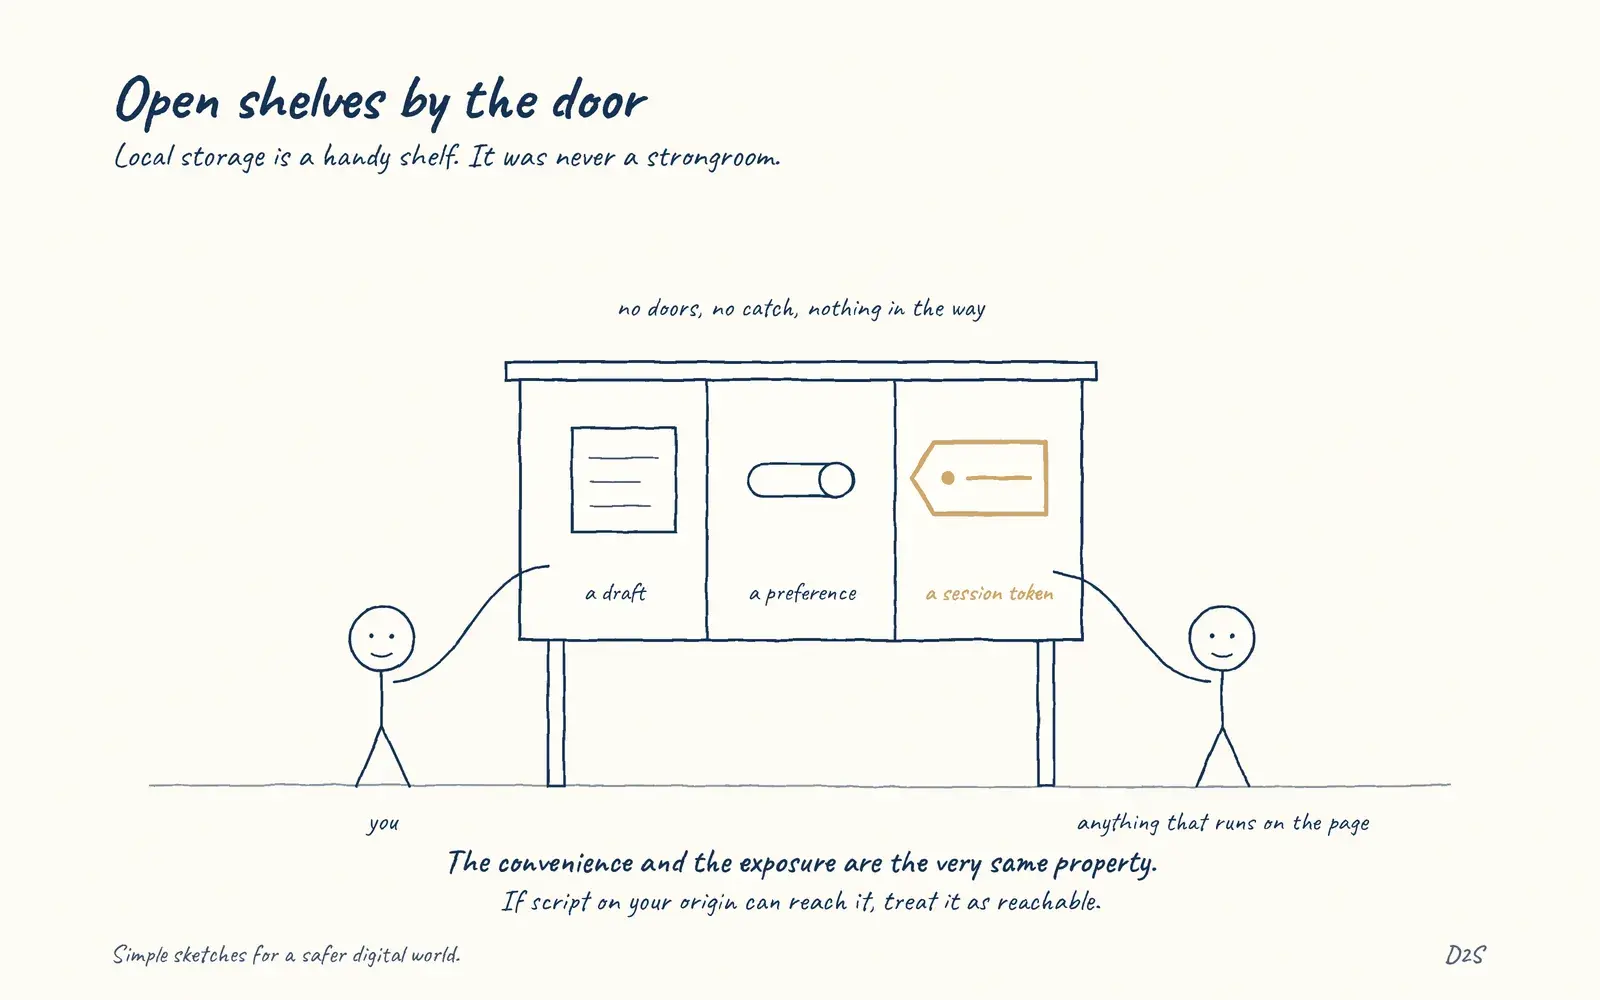 Local storage is convenient, not a secure vaultOpen shelves by the door
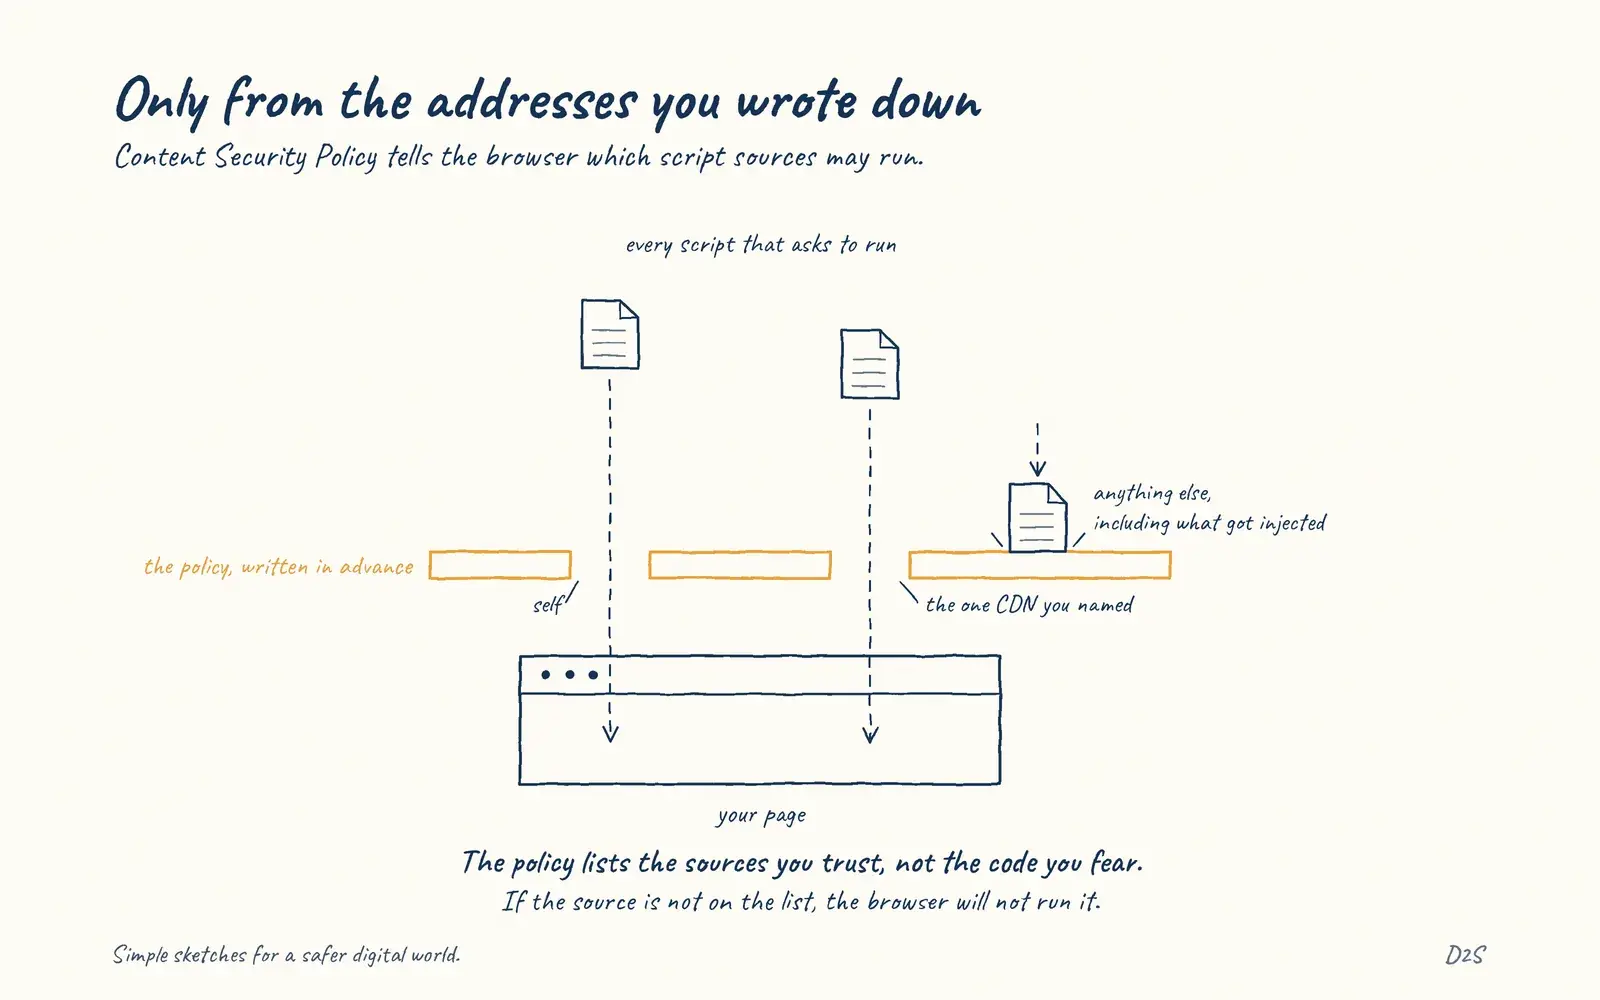 Content Security Policy constrains script sourcesOnly from the addresses you wrote down
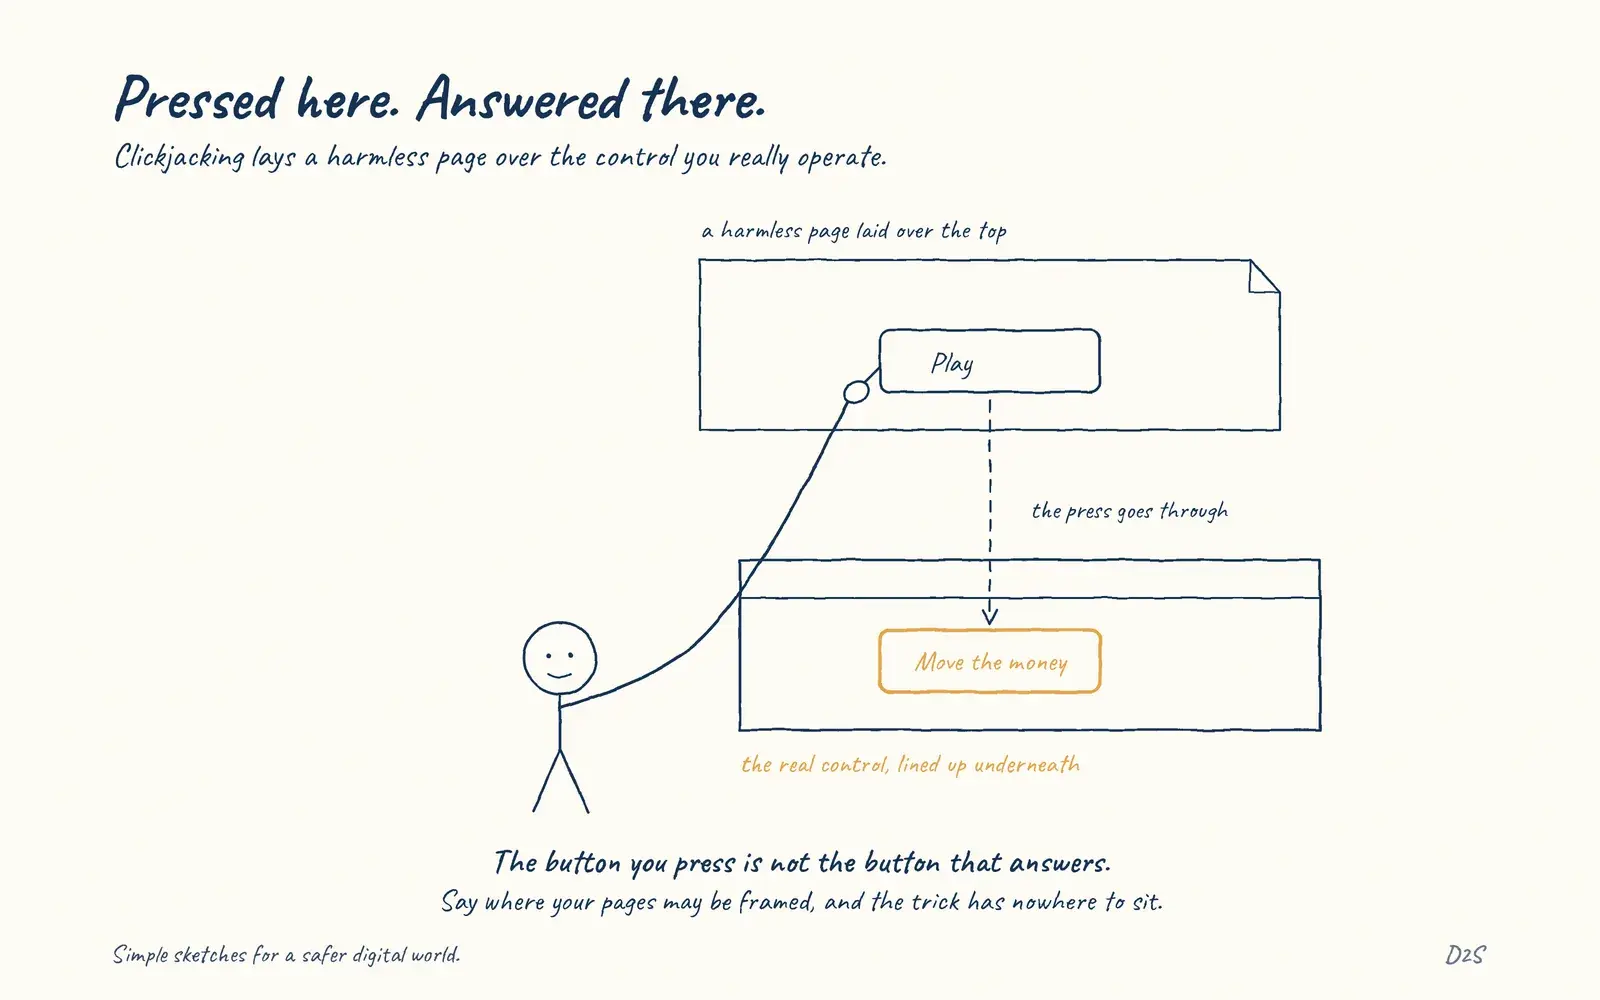 Clickjacking hides the real control beneath the clickPressed here. Answered there
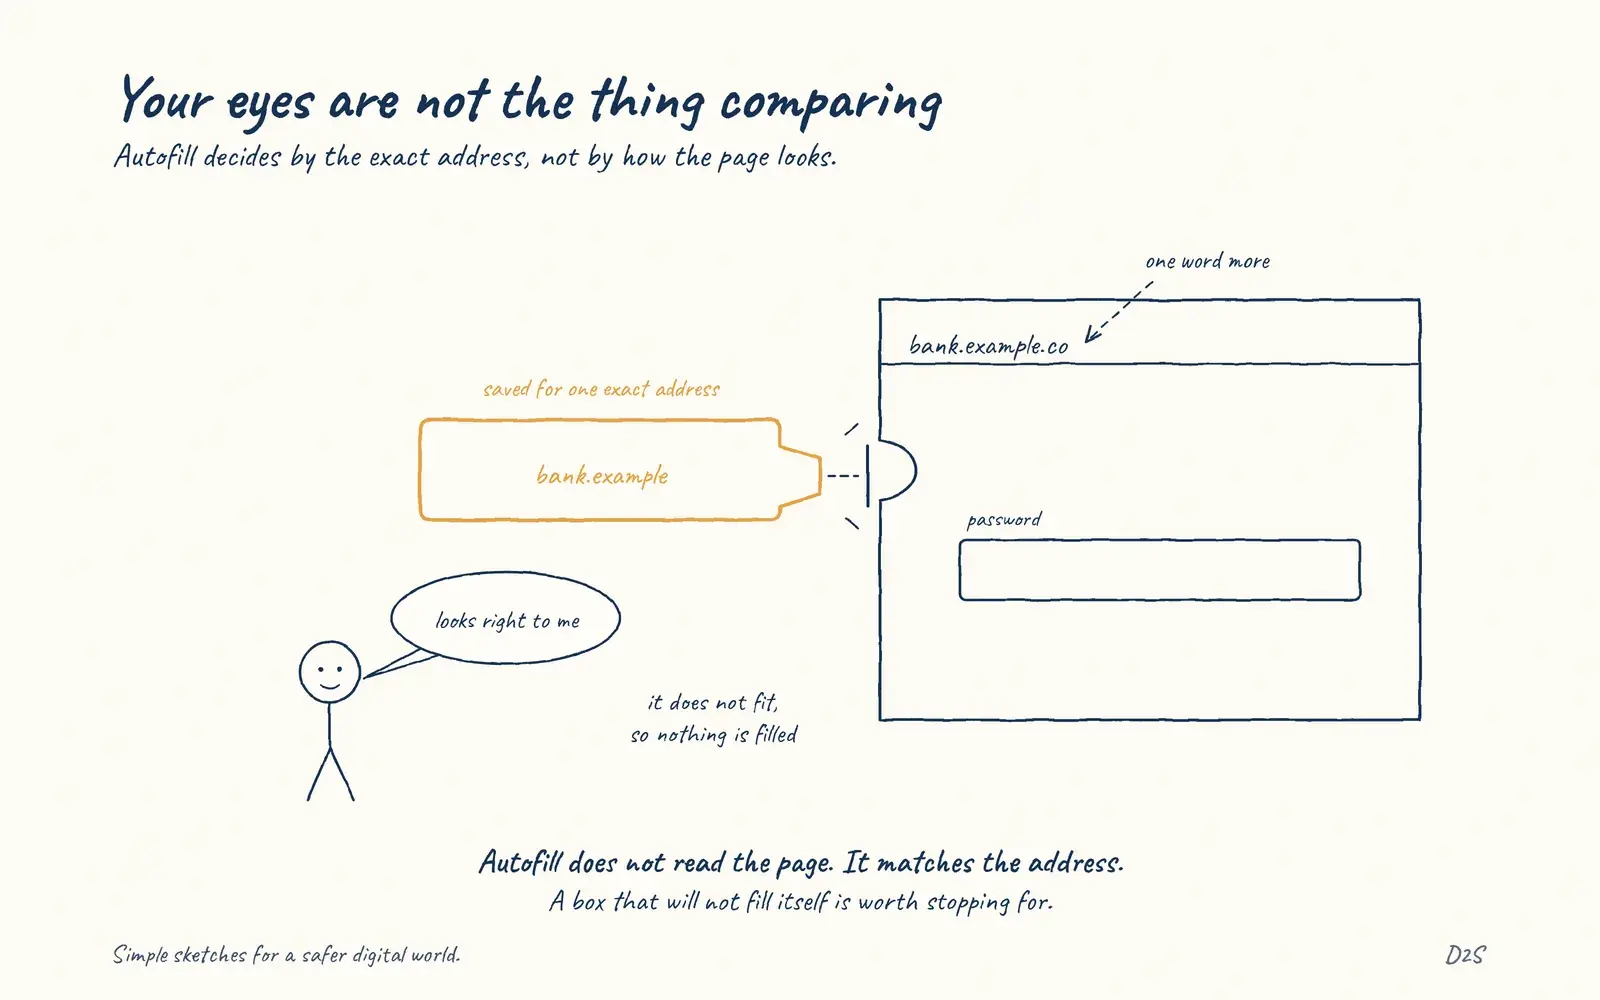 Autofill changes the phishing surfaceYour eyes are not the thing comparing
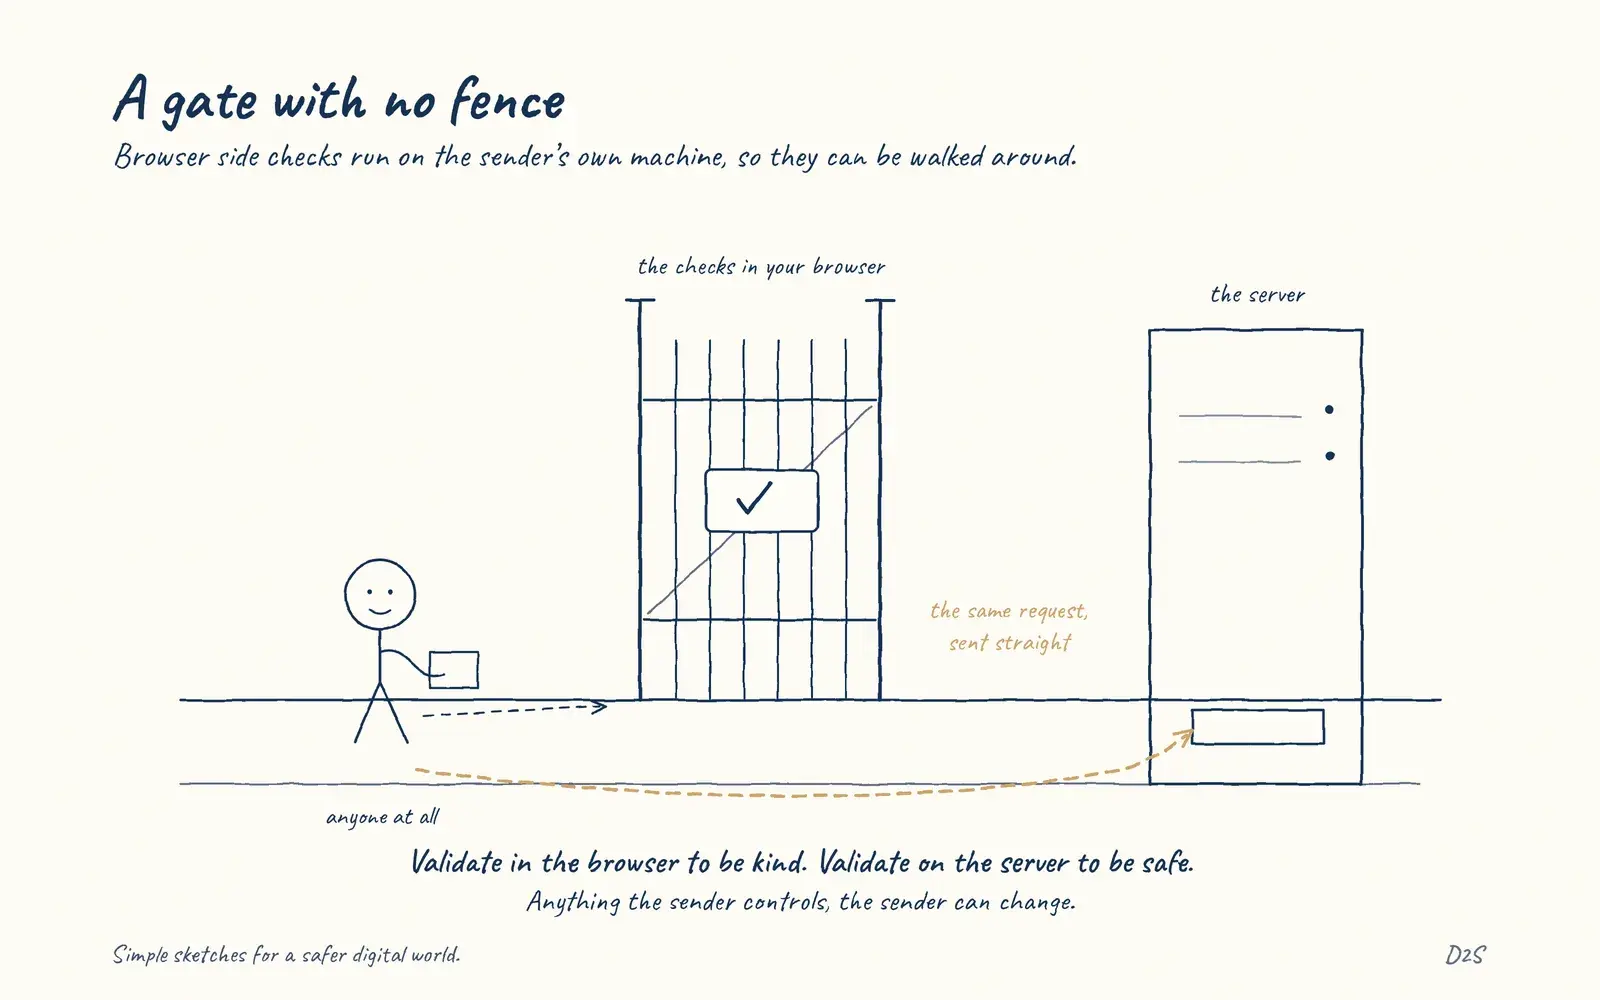 Client-side validation is not a security boundaryA gate with no fence
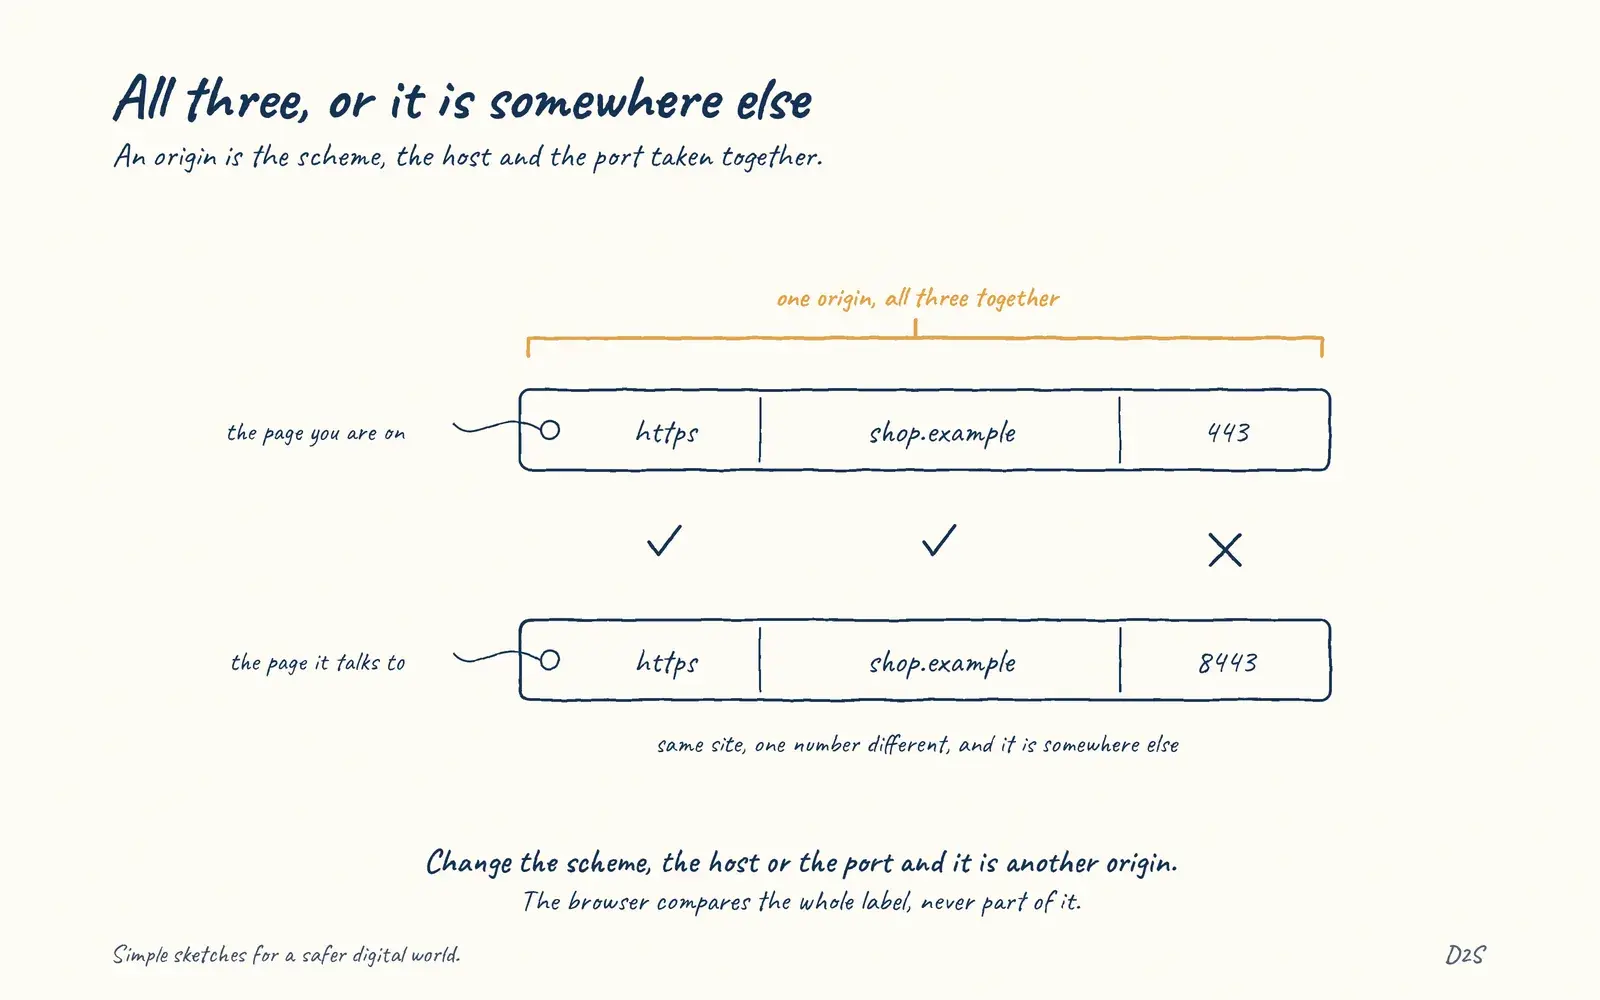 Origin means scheme, host and port togetherAll three, or it is somewhere else