
Containers & Kubernetes
Orchestration, isolation, and the defaults that are not safe ones.
24 sketches
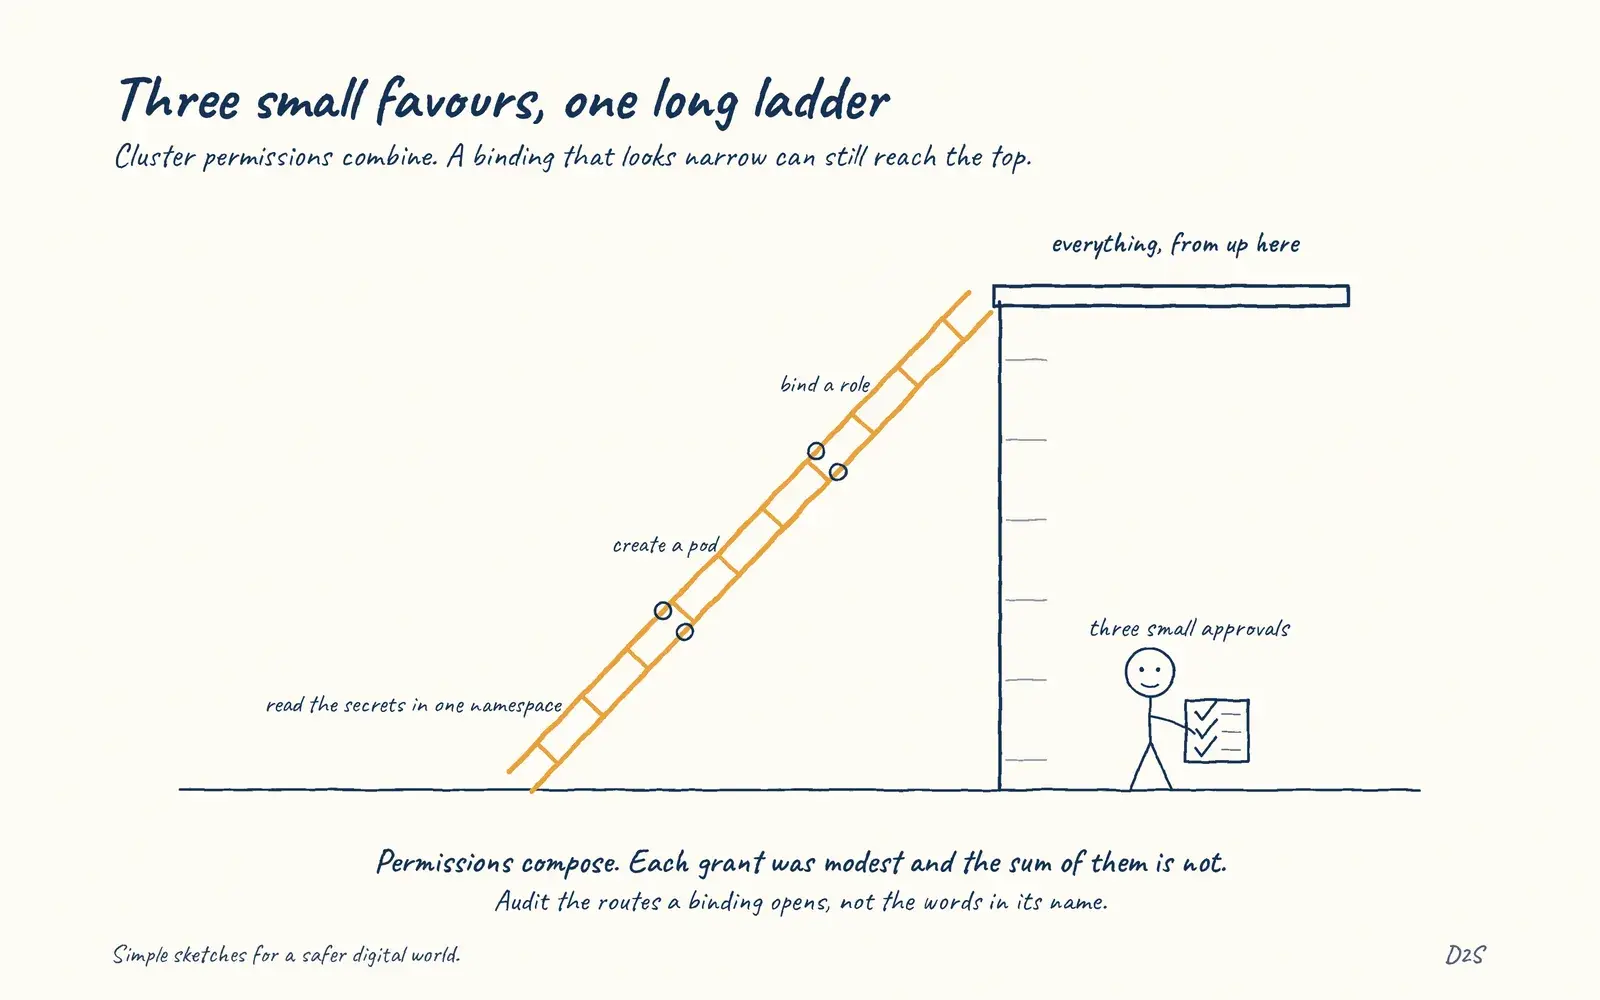 Kubernetes RBACThree small favours, one long ladder
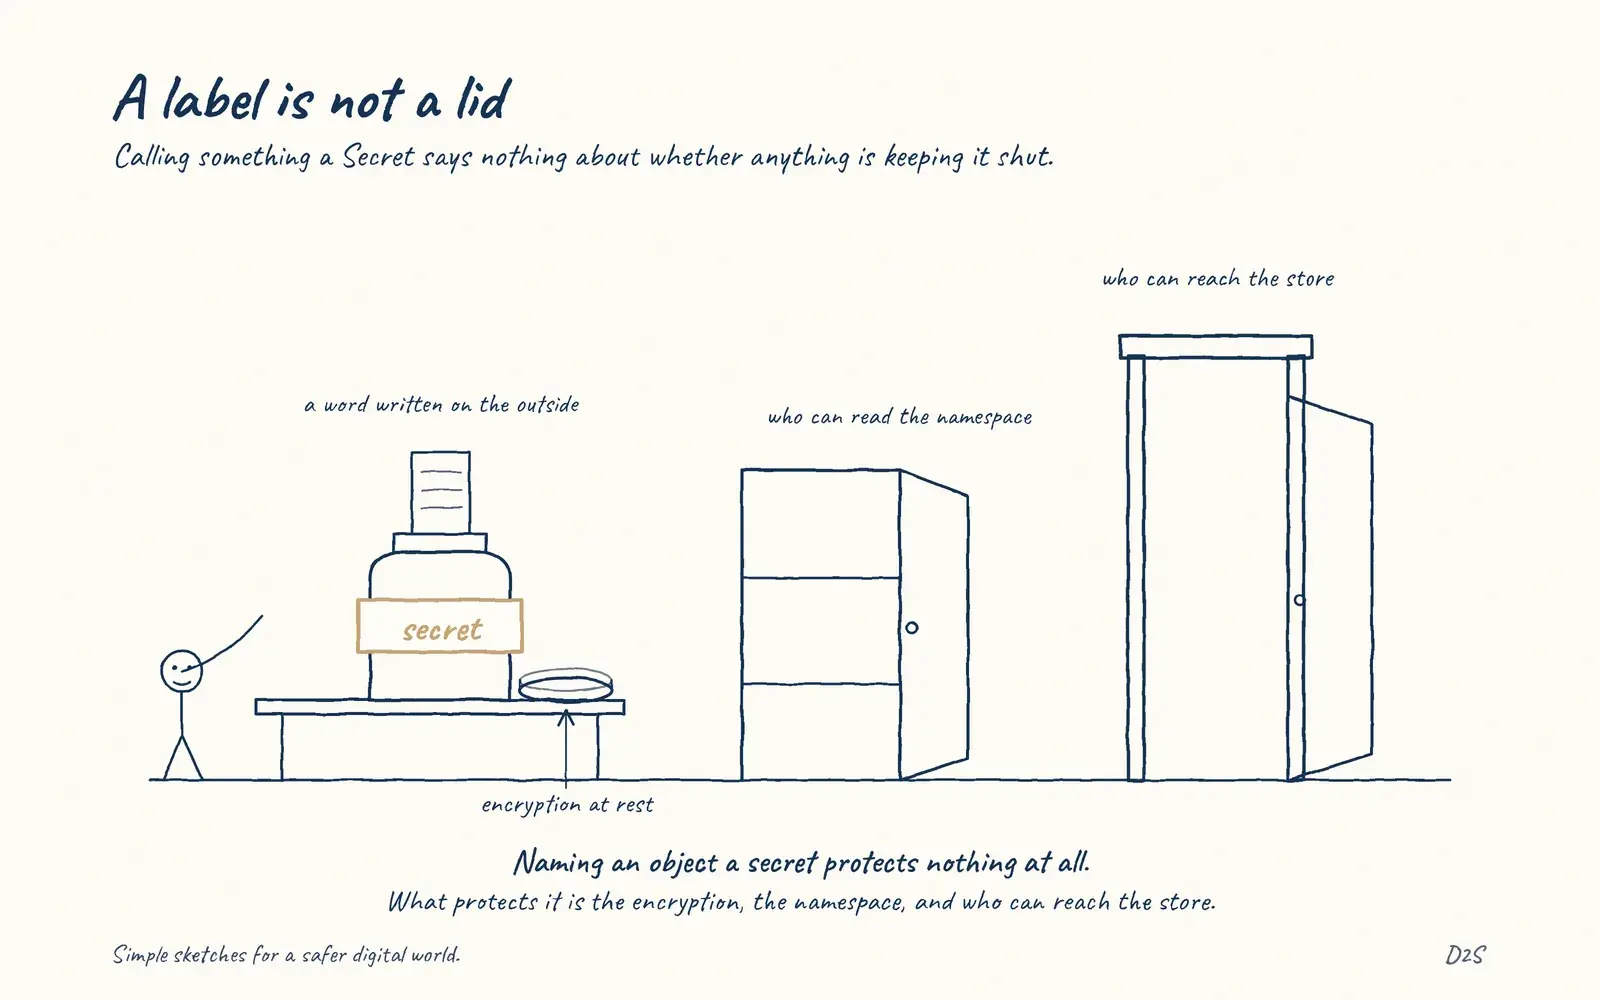 Kubernetes secretsA label is not a lid
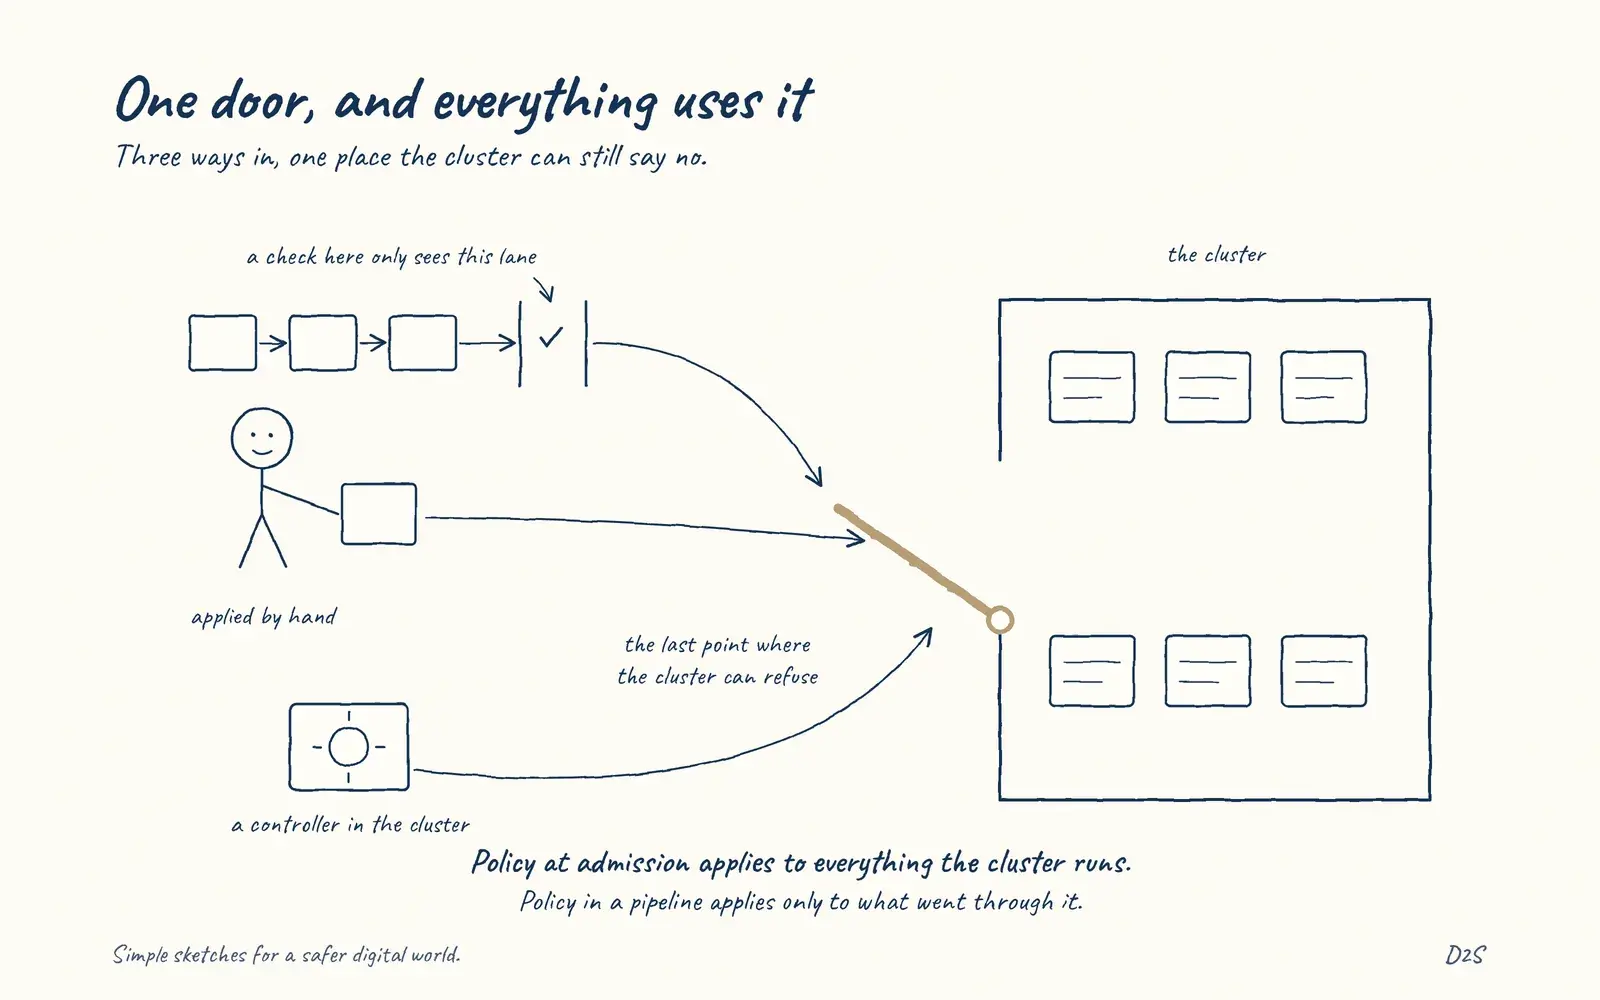 Admission controlOne door, and everything uses it
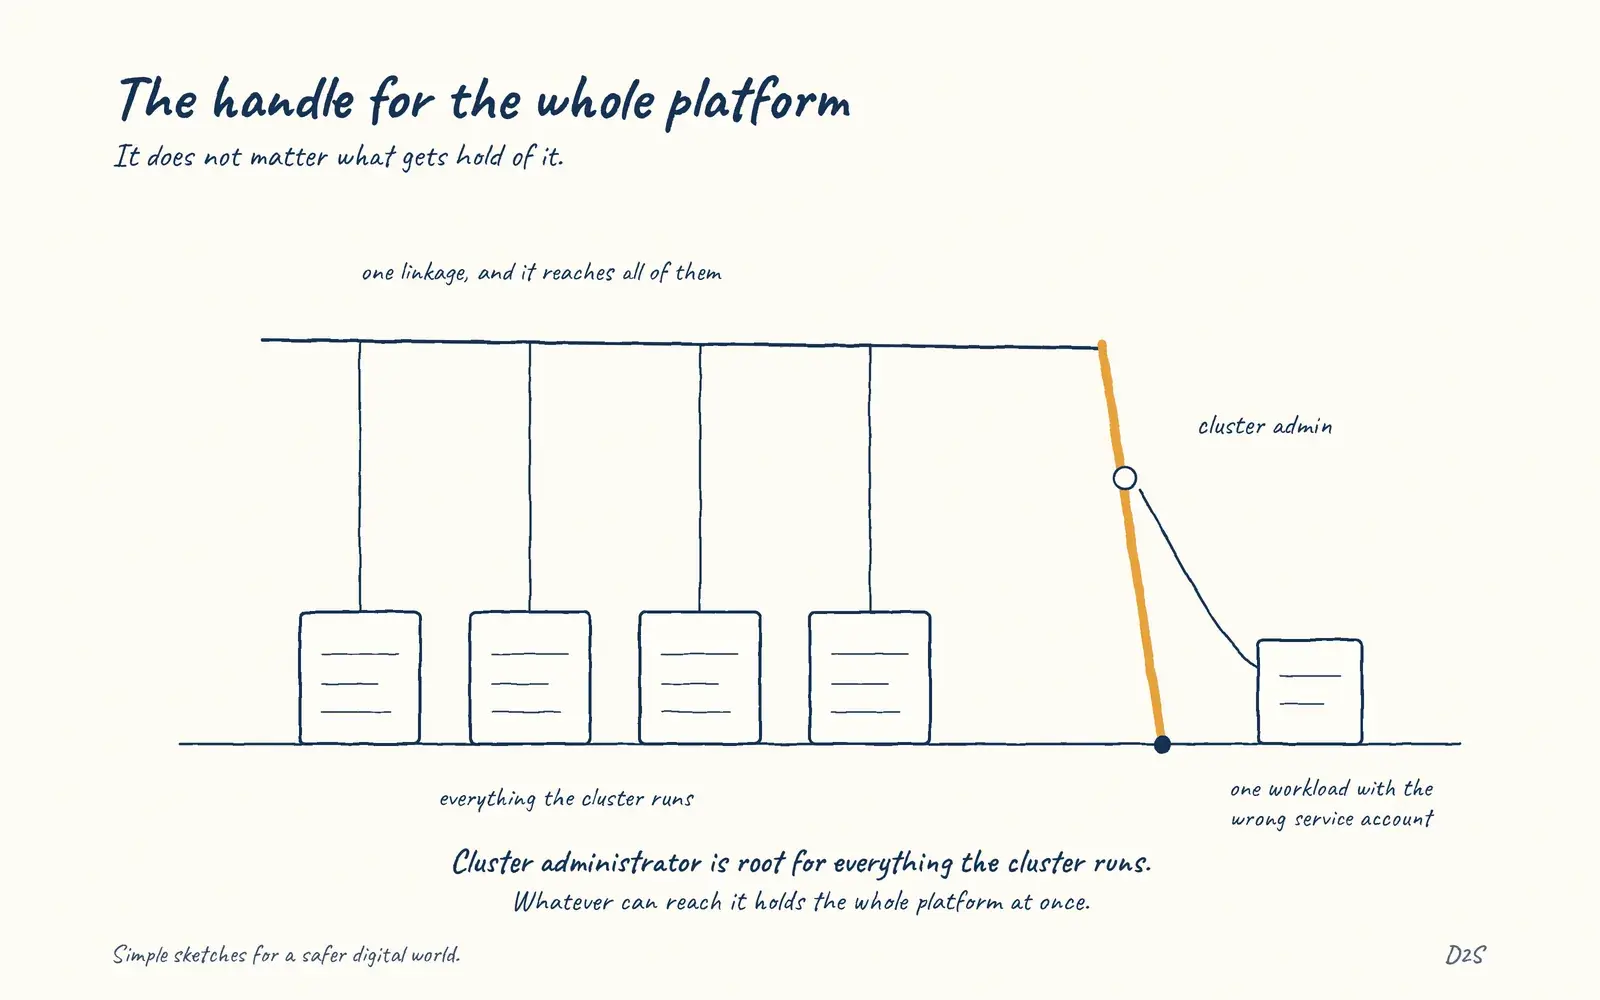 Cluster adminThe handle for the whole platform
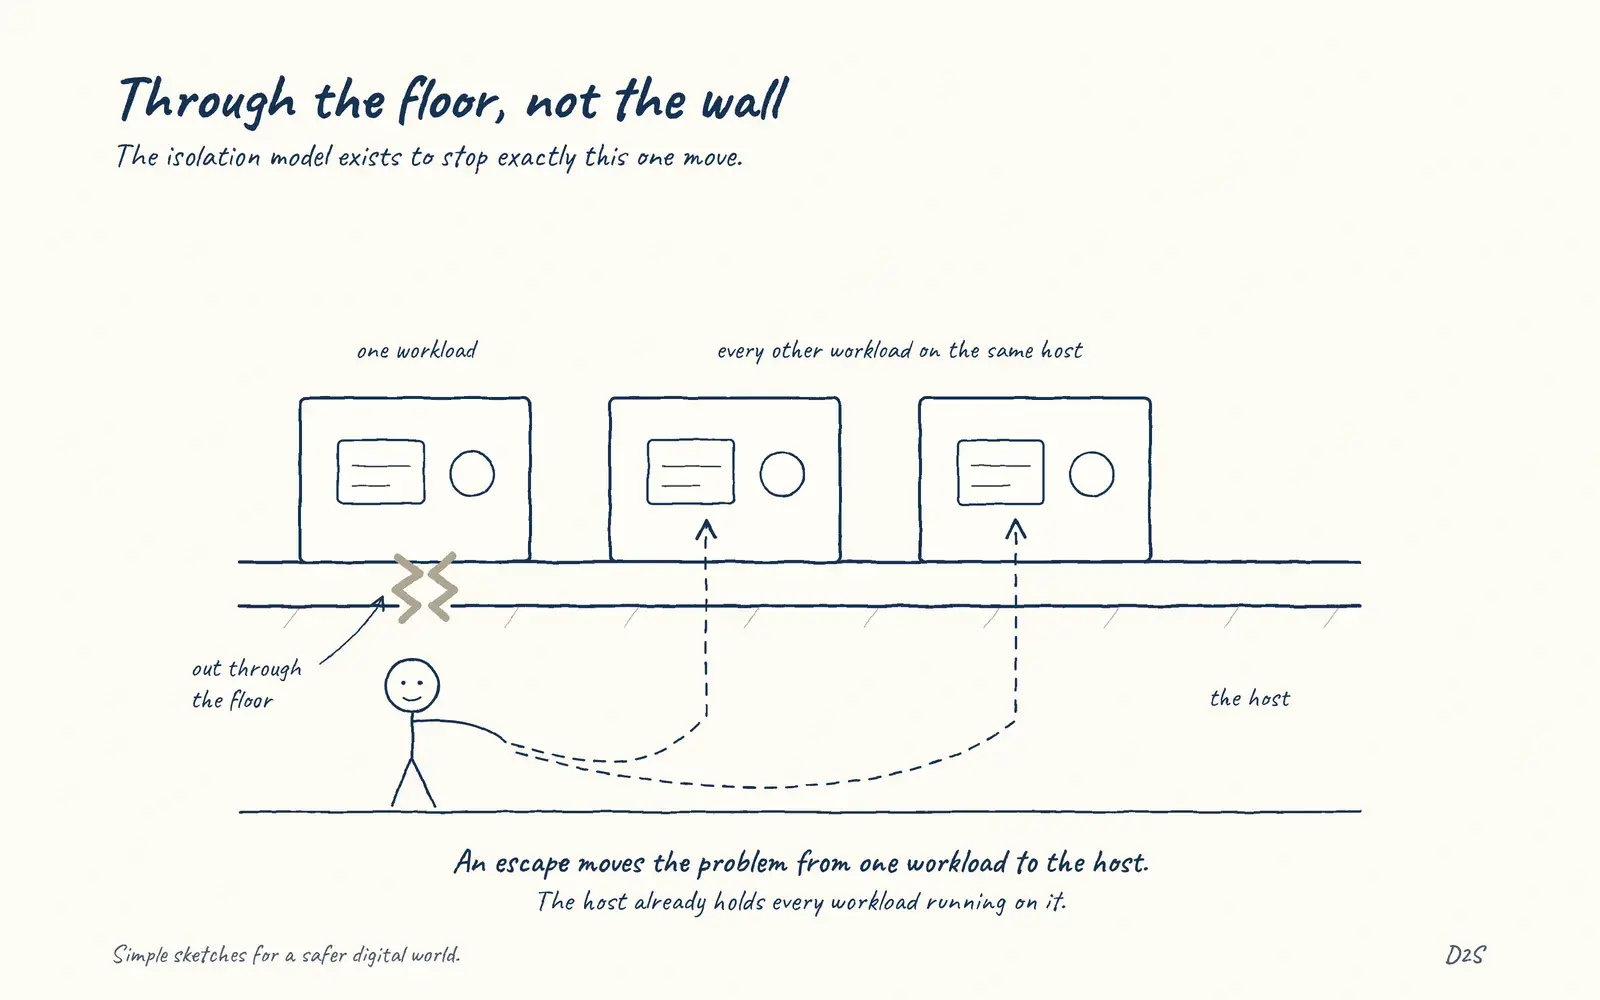 Container escapeThrough the floor, not the wall
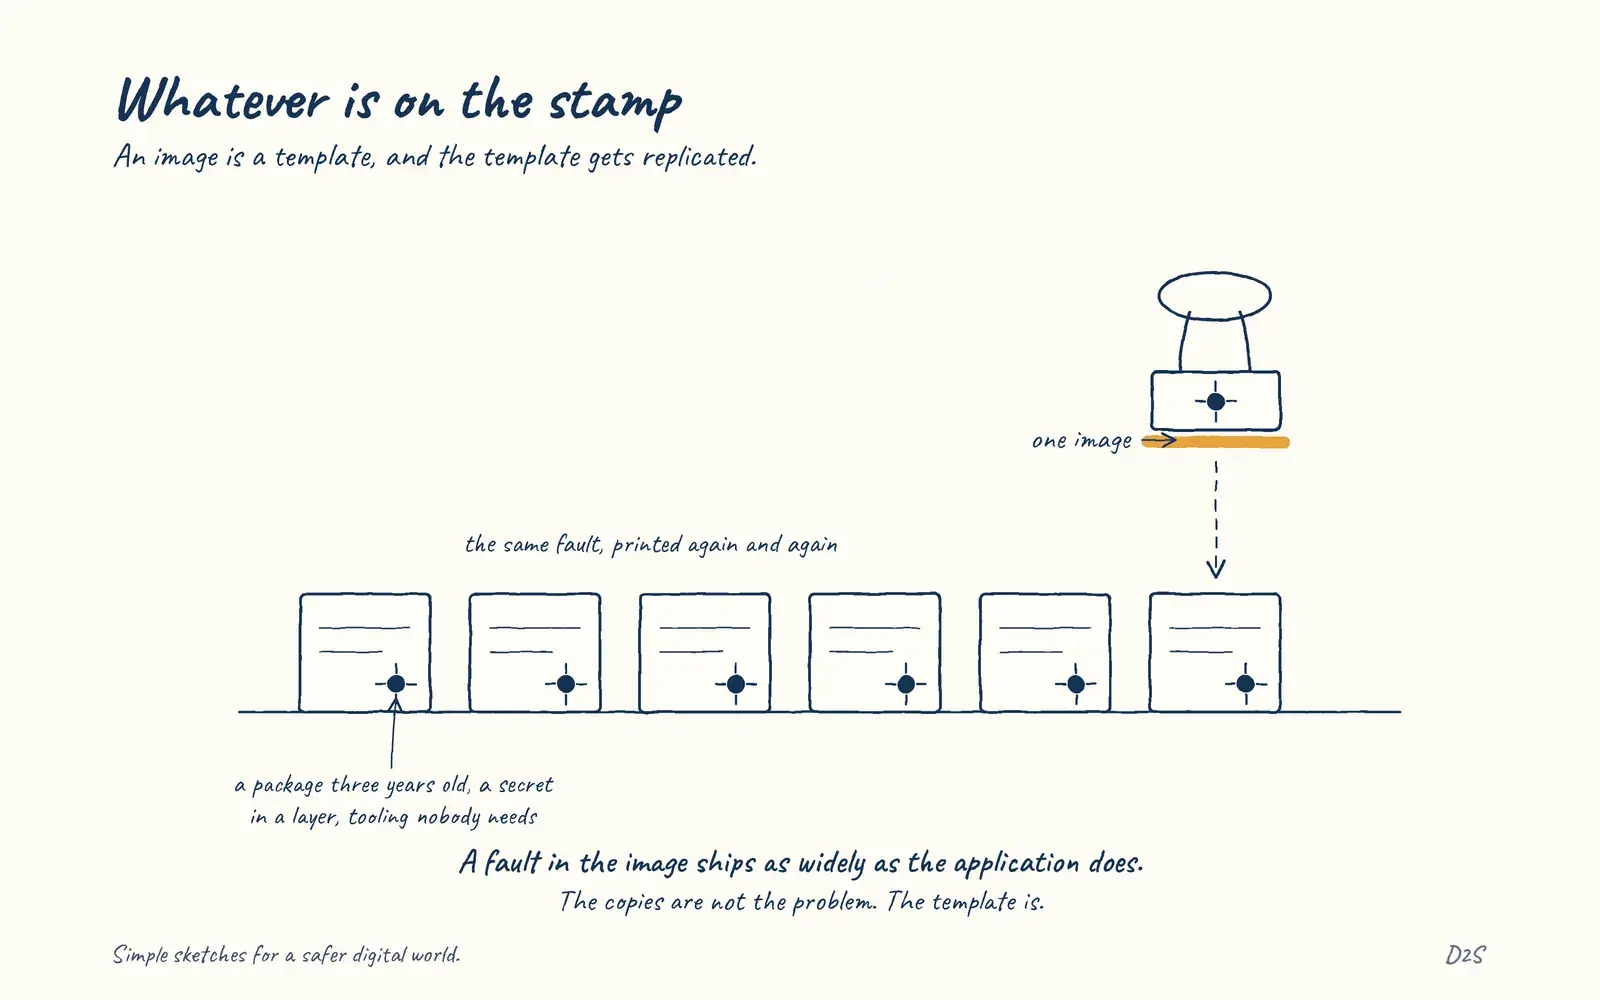 Container imagesWhatever is on the stamp
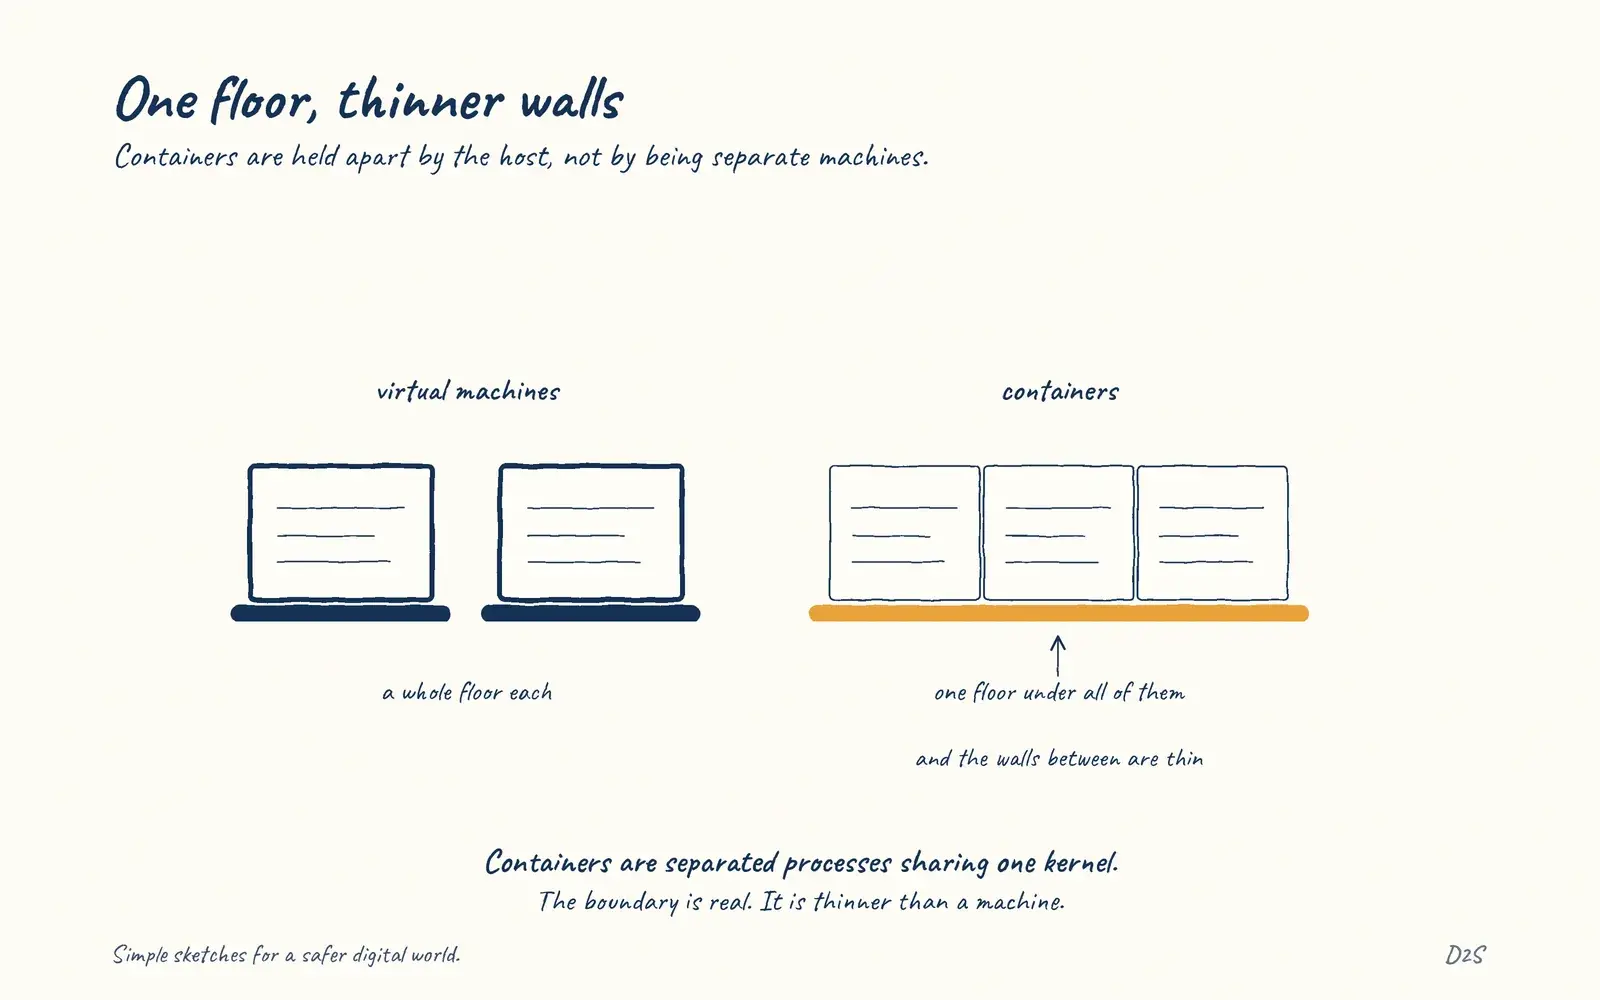 ContainersOne floor, thinner walls
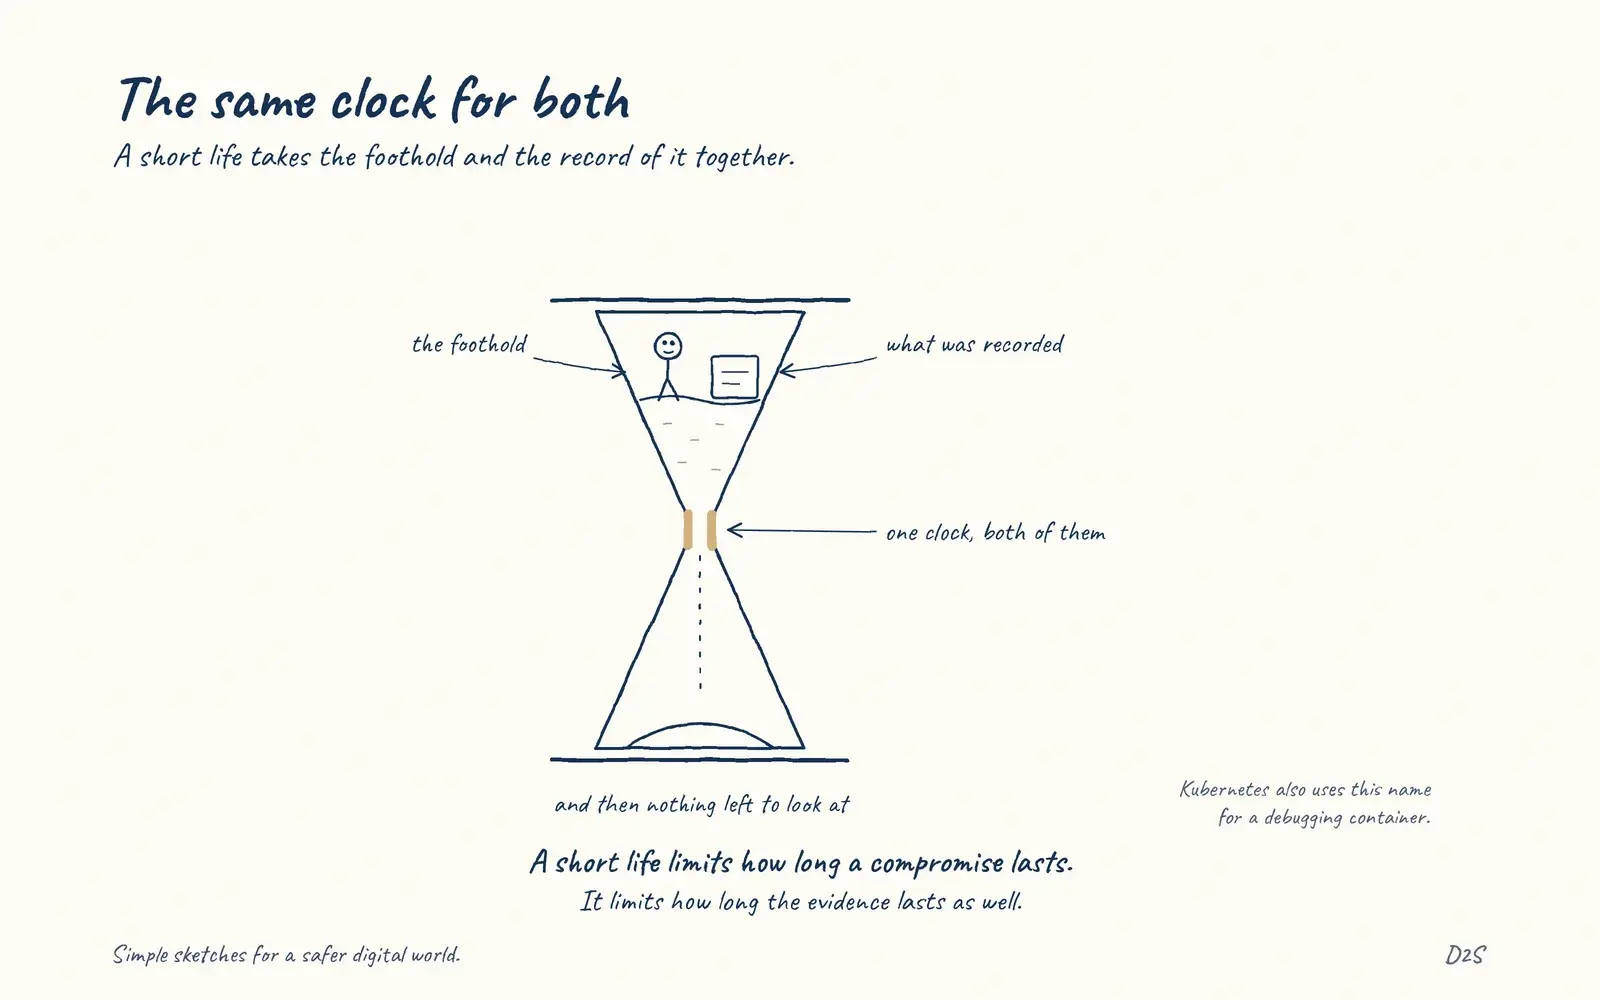 Ephemeral containersThe same clock for both
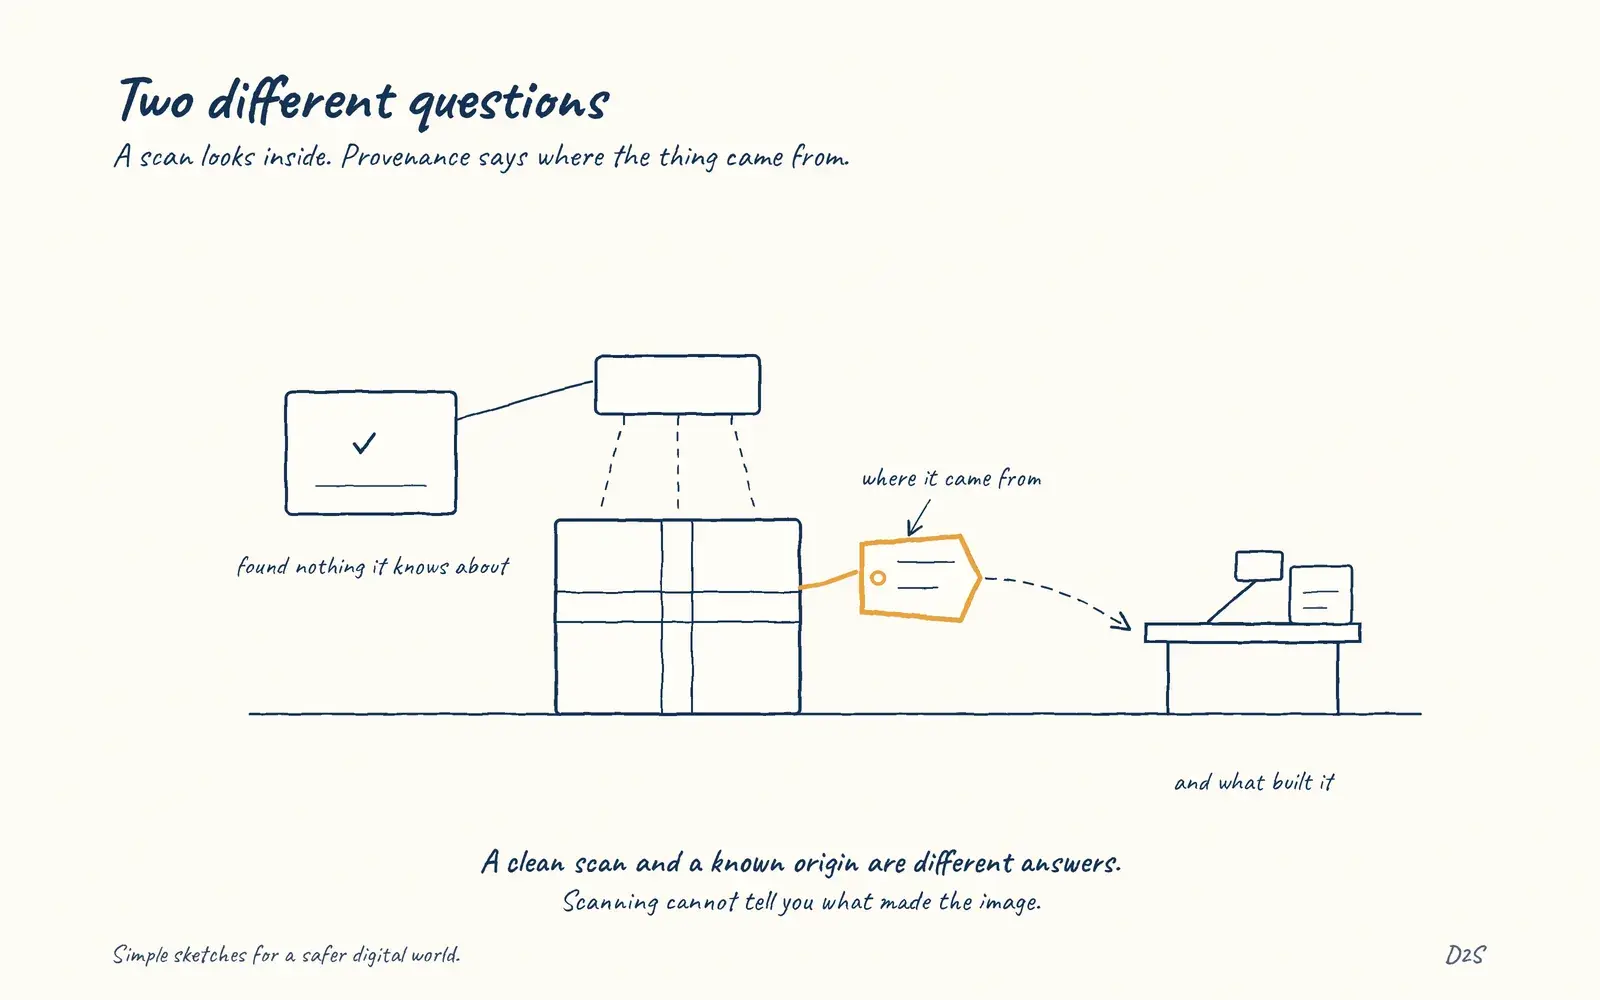 Image provenanceTwo different questions
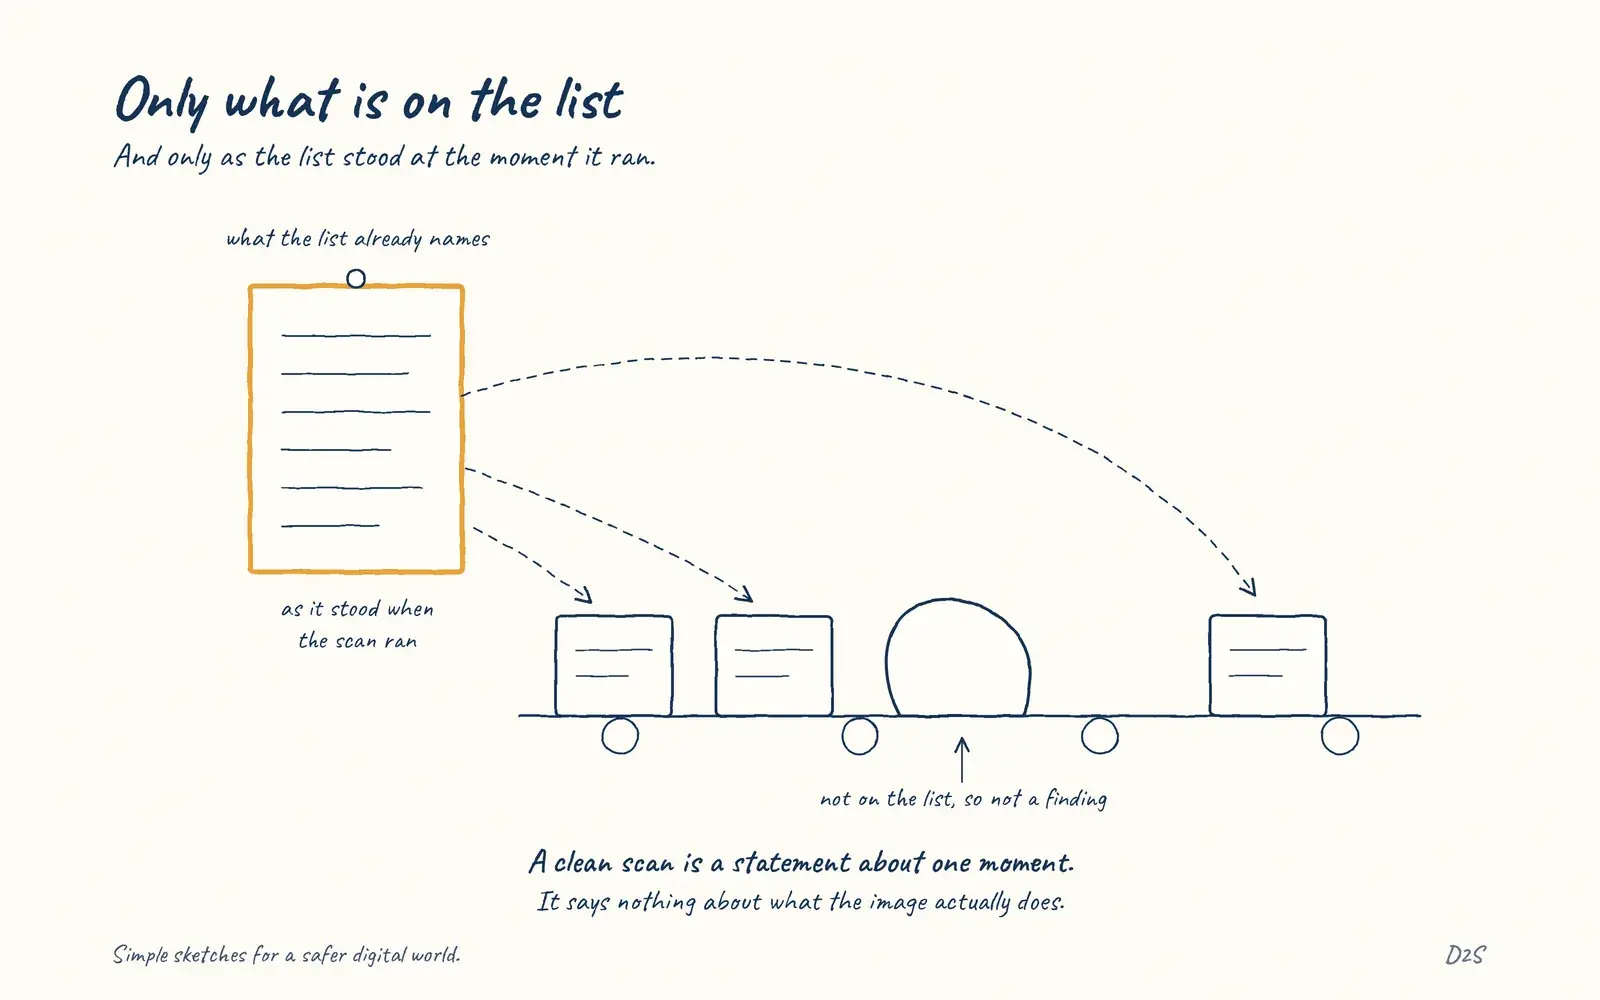 Image scanningOnly what is on the list
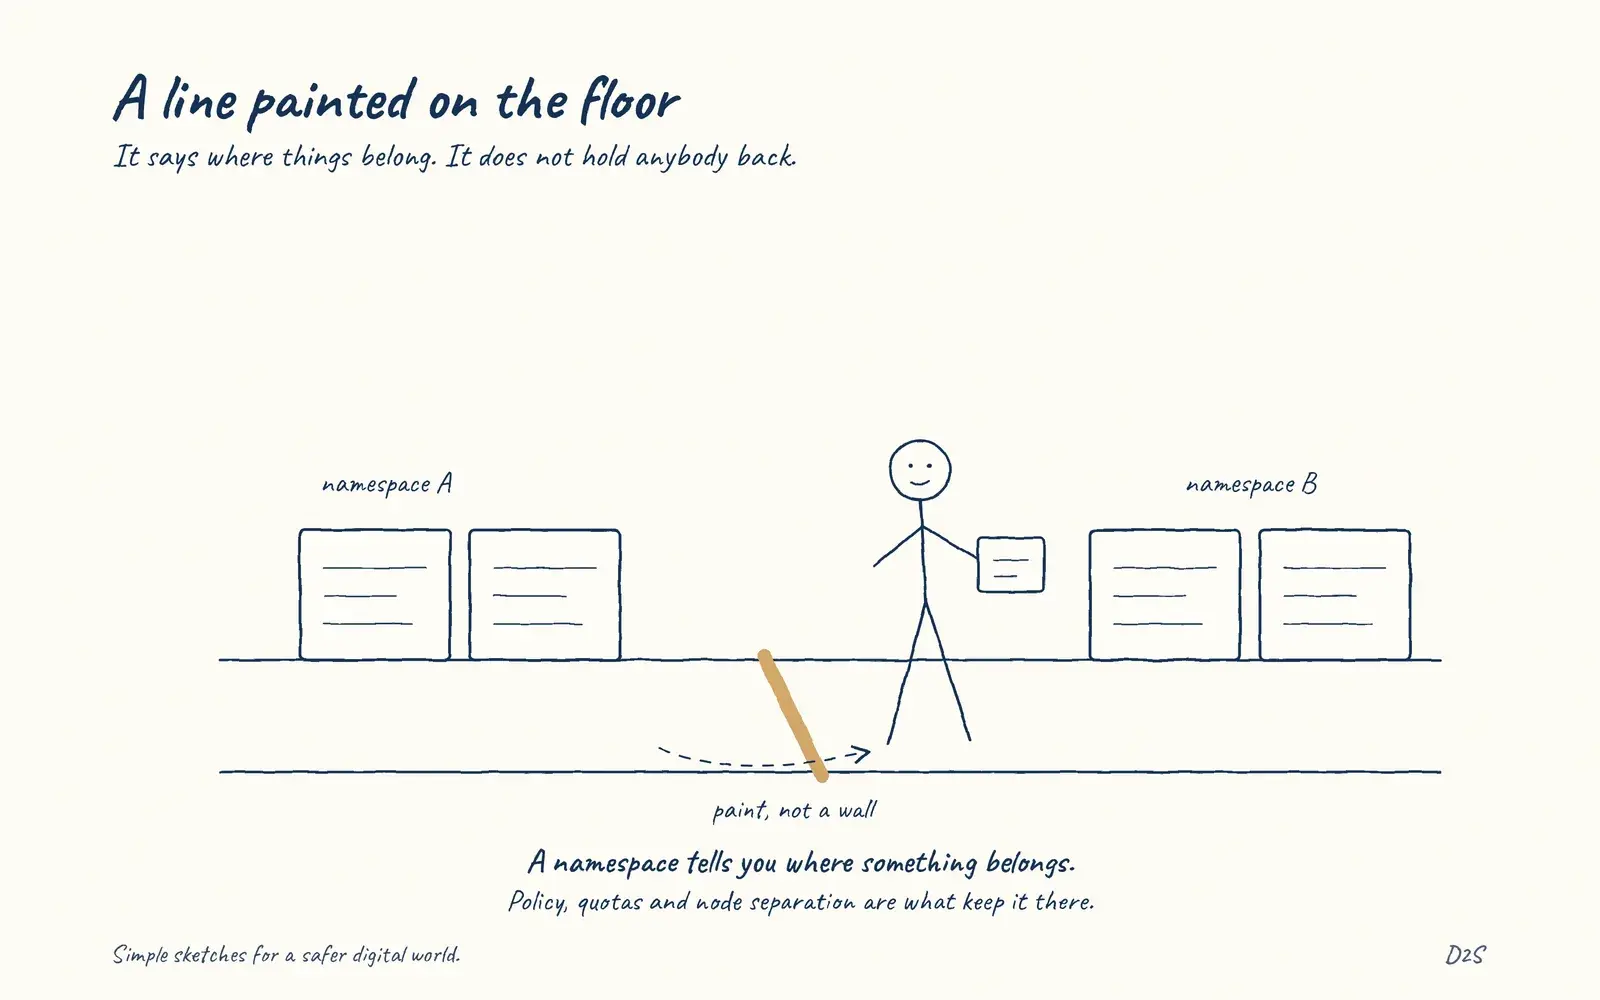 Namespace isolationA line painted on the floor
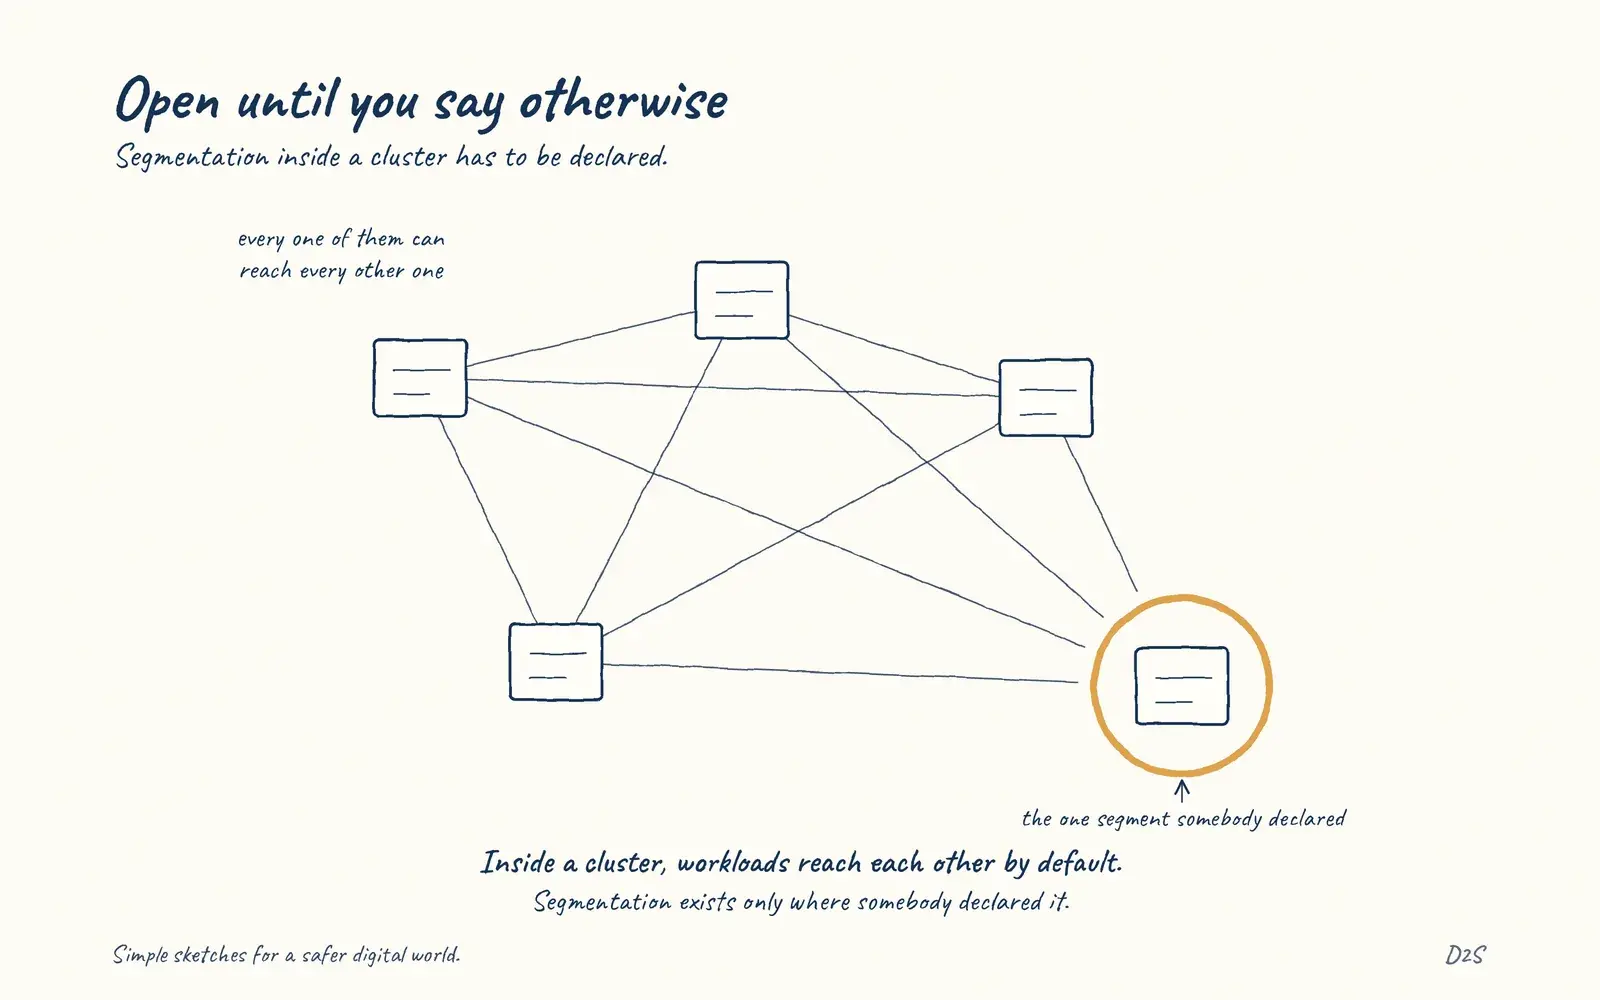 Network policiesOpen until you say otherwise
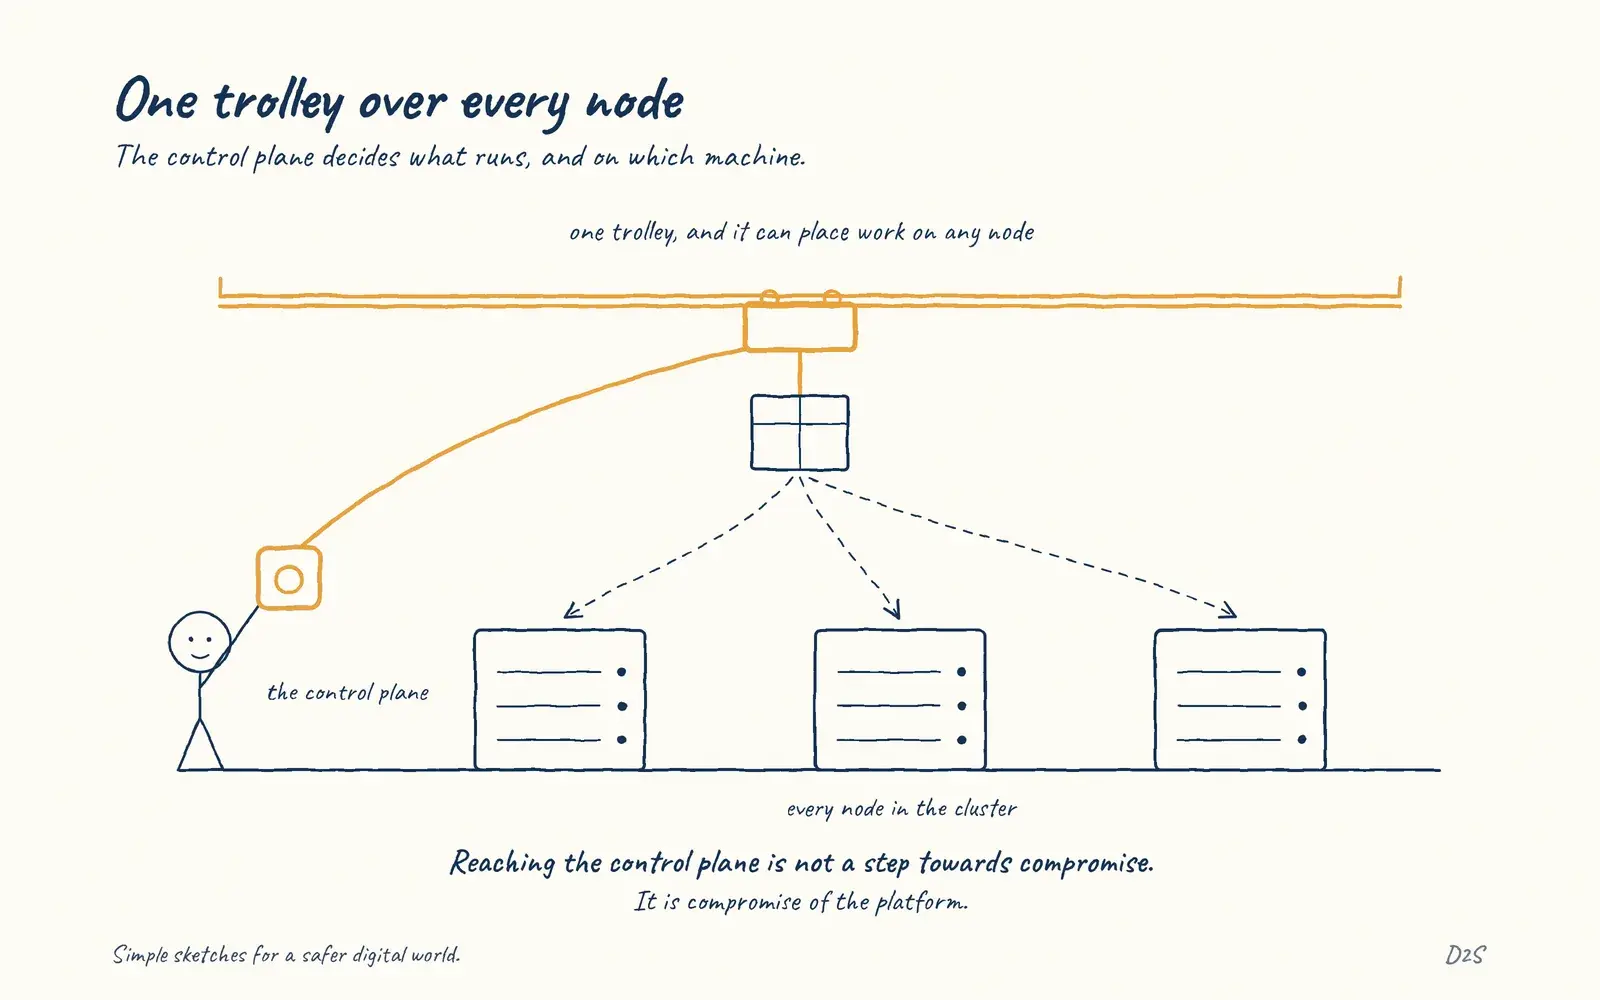 Orchestrator control planeOne trolley over every node
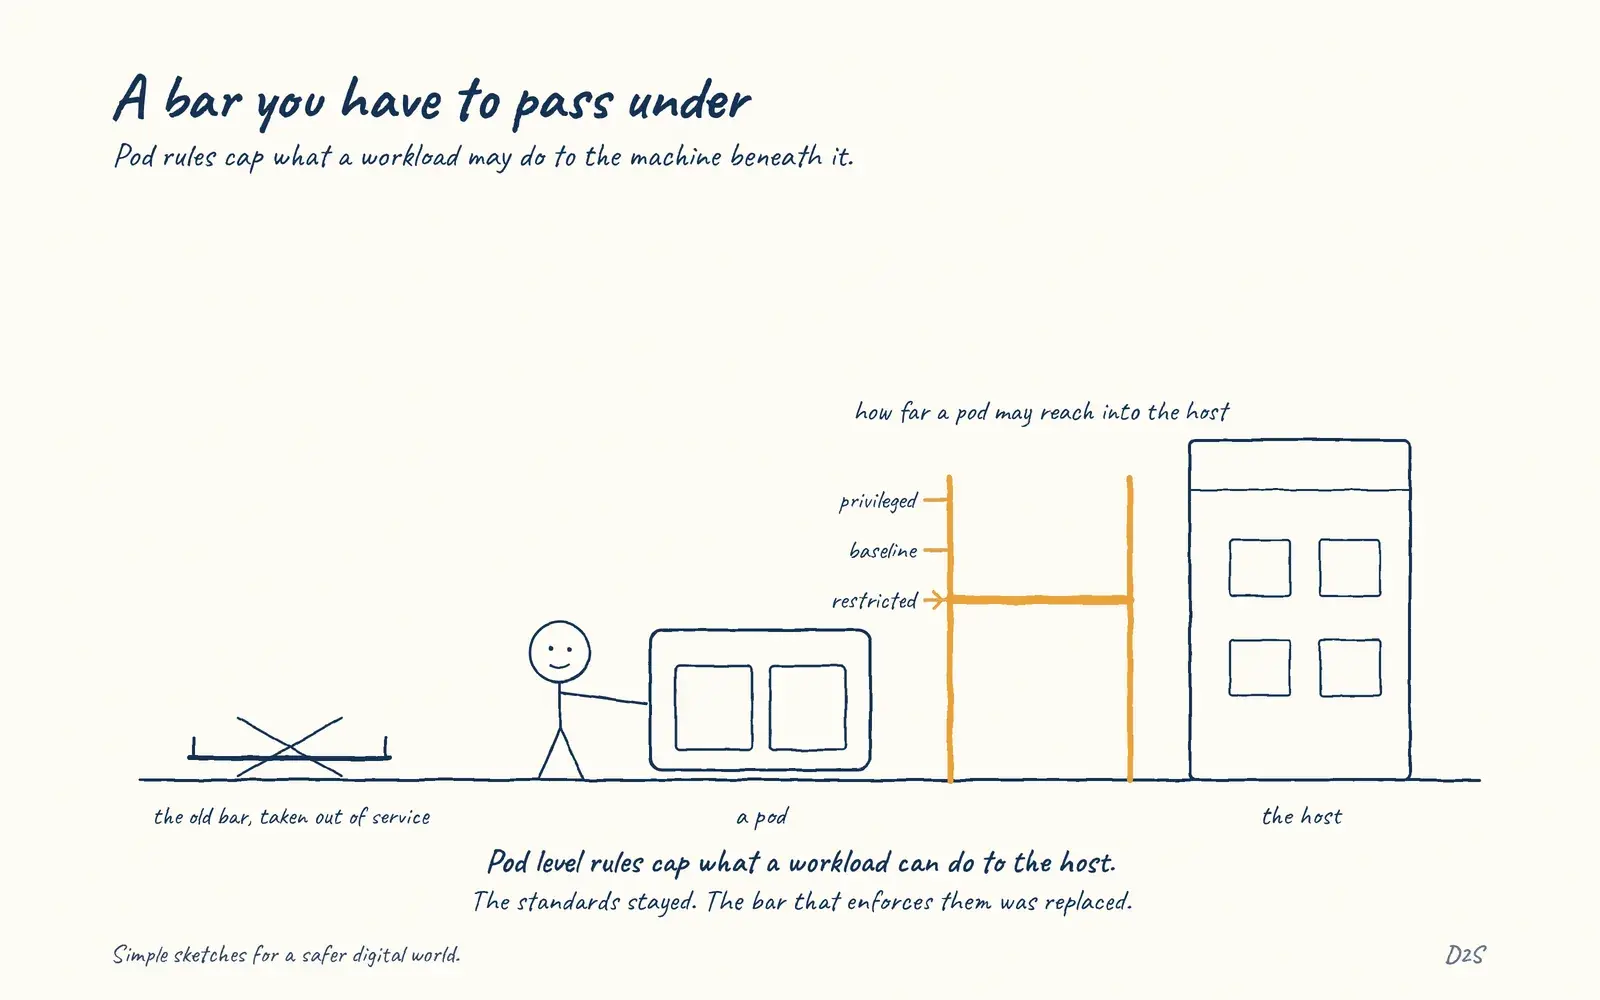 Pod securityA bar you have to pass under
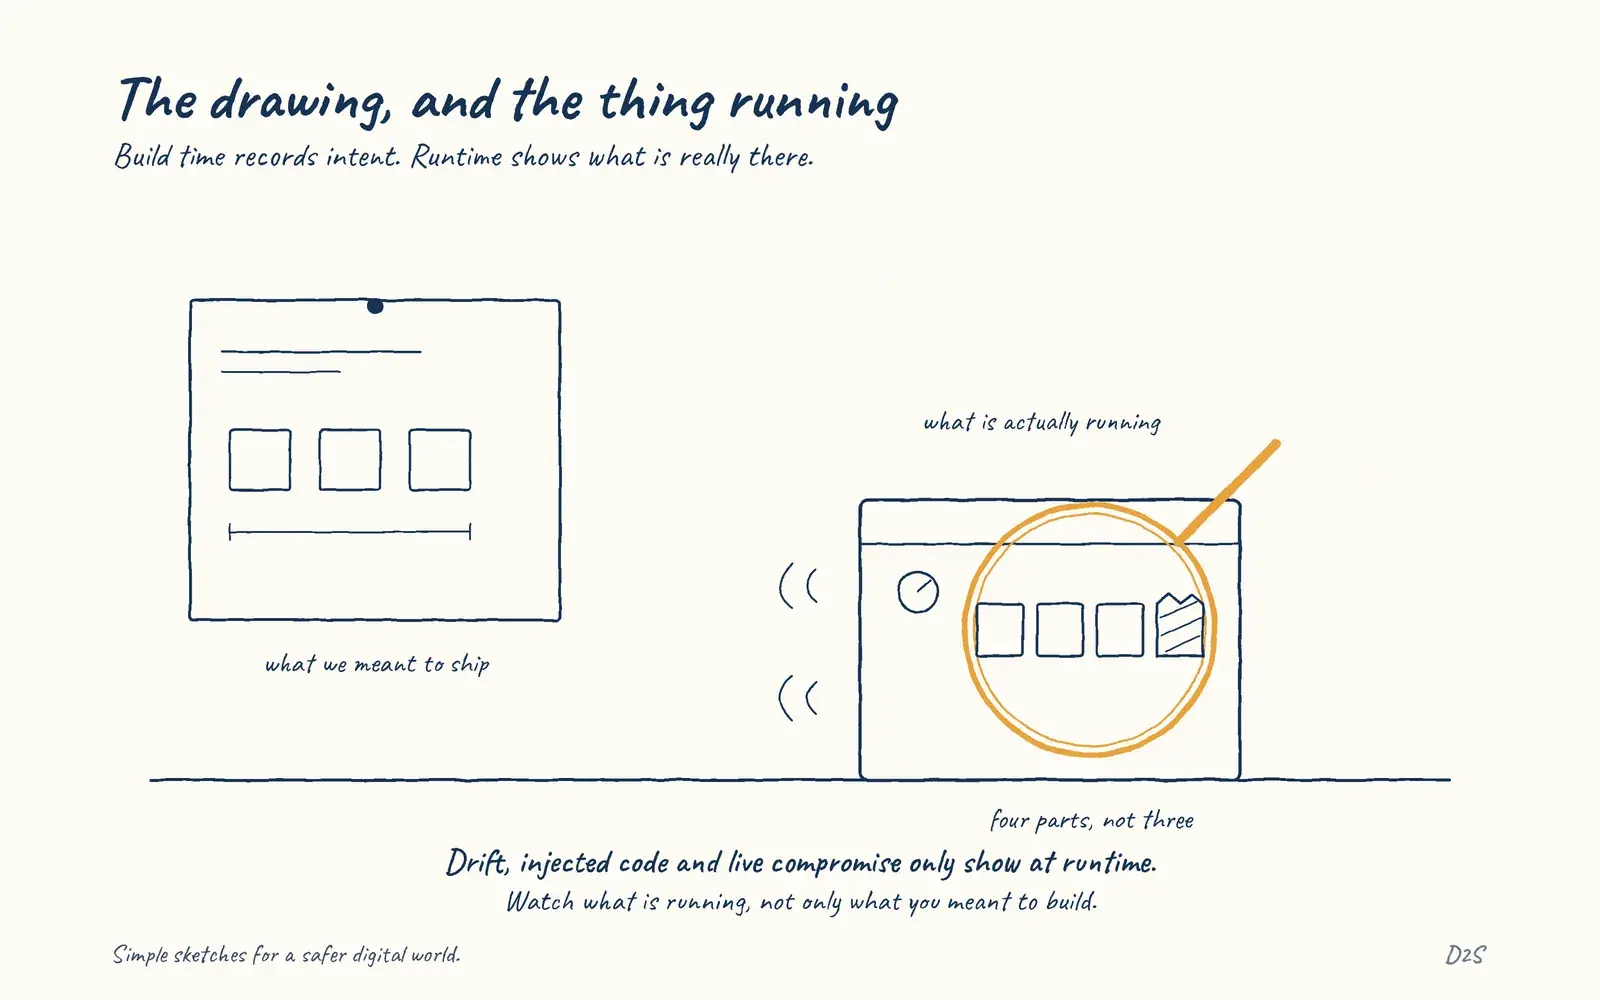 Runtime securityThe drawing, and the thing running
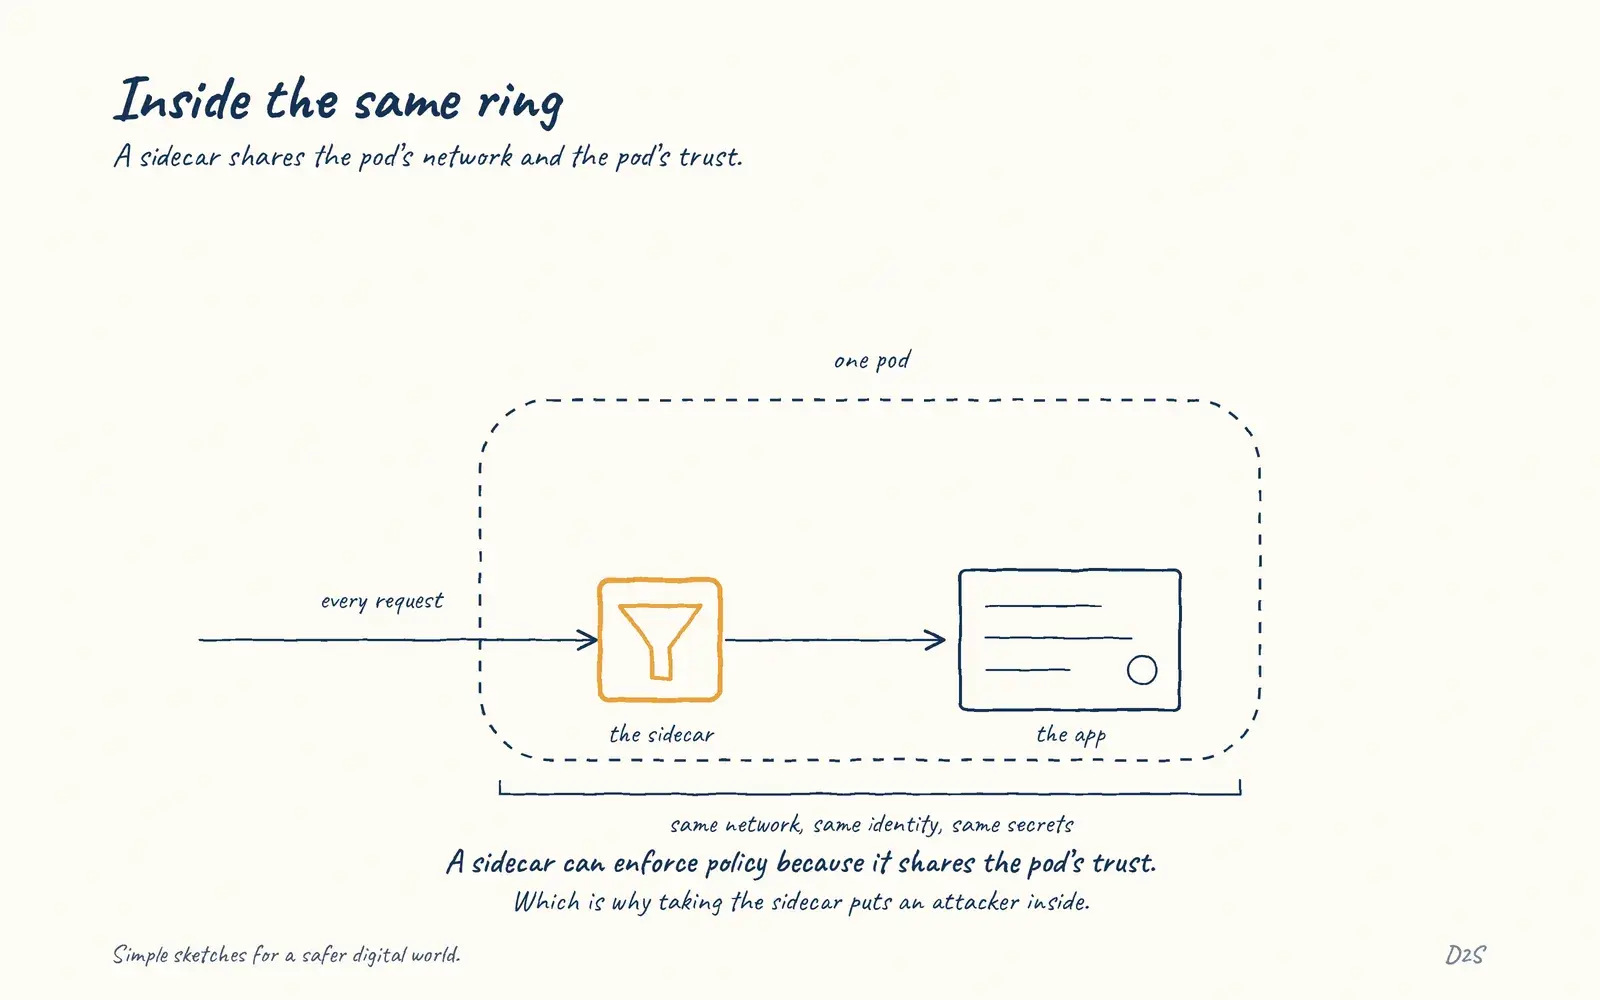 SidecarsInside the same ring
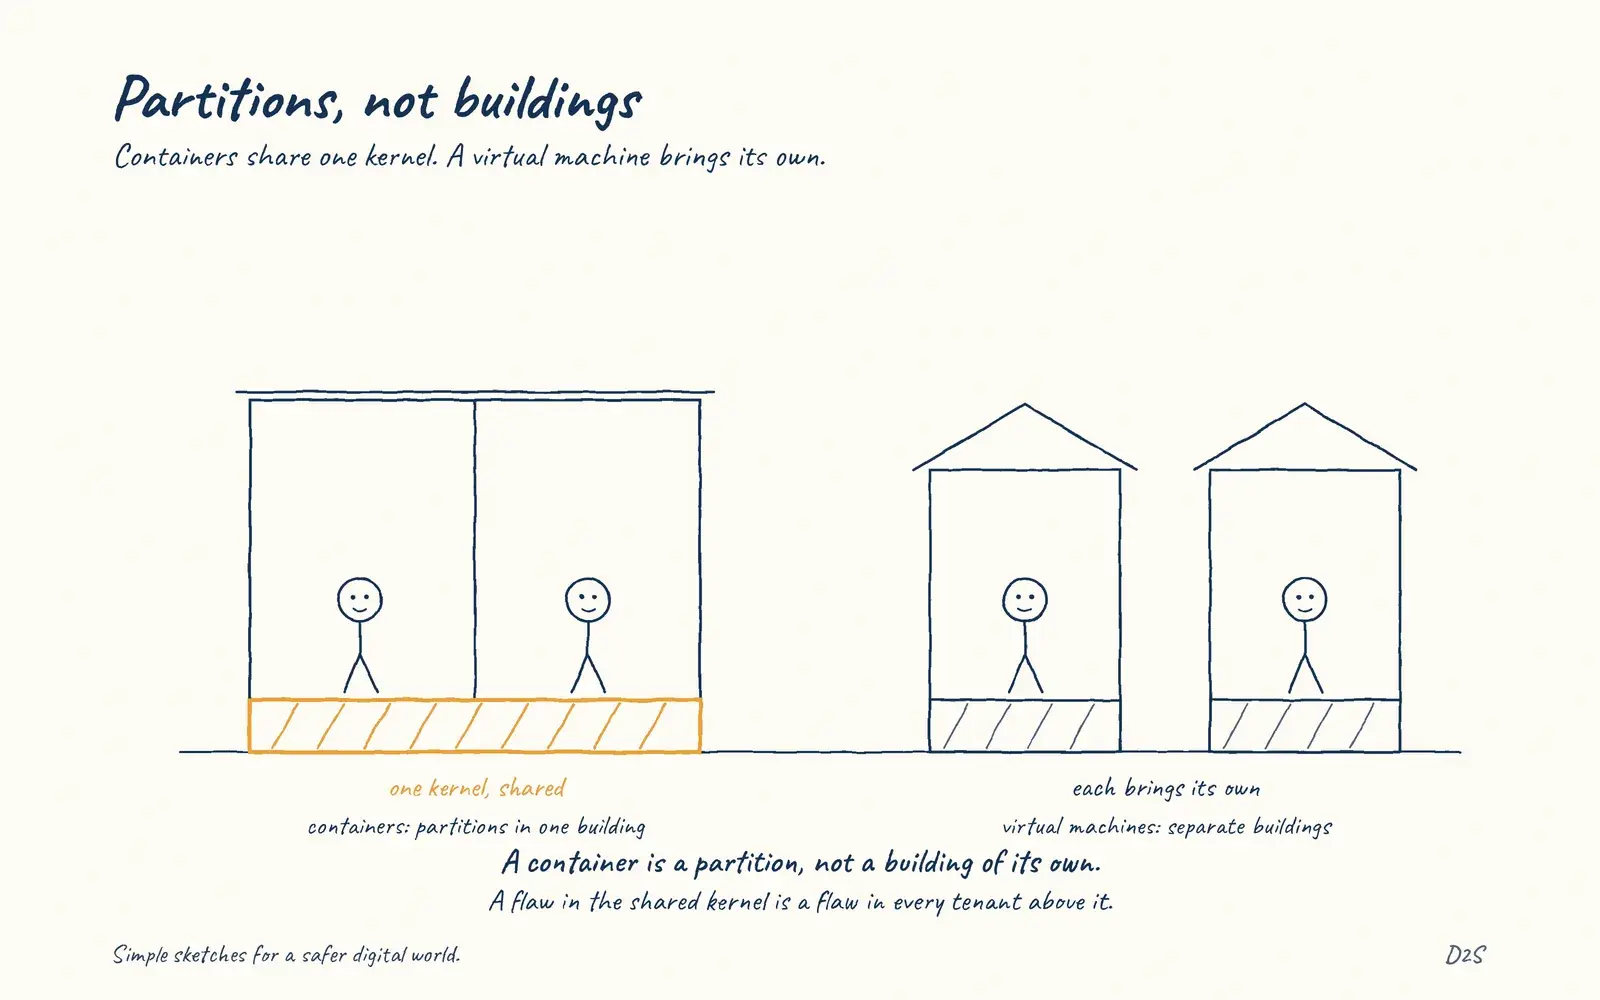 A container is isolation, not a tiny virtual machinePartitions, not buildings
 Kubernetes RBAC controls API actions, not what a running container can then doChecked at the hatch, not inside the room
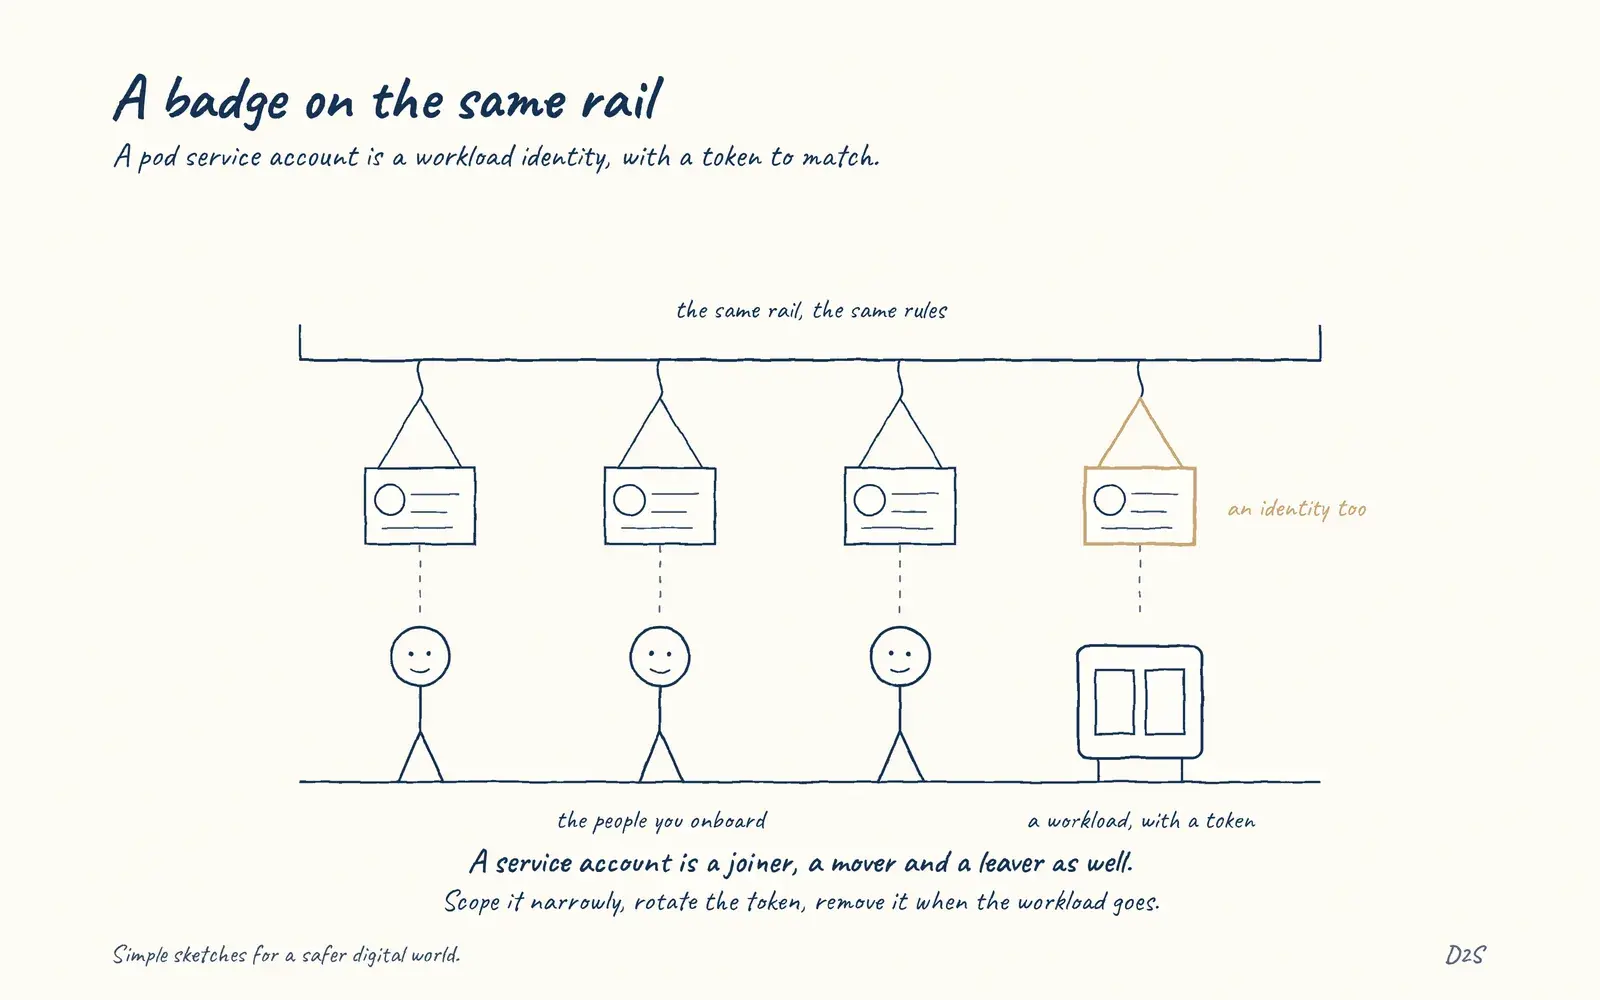 A pod service account is an identityA badge on the same rail
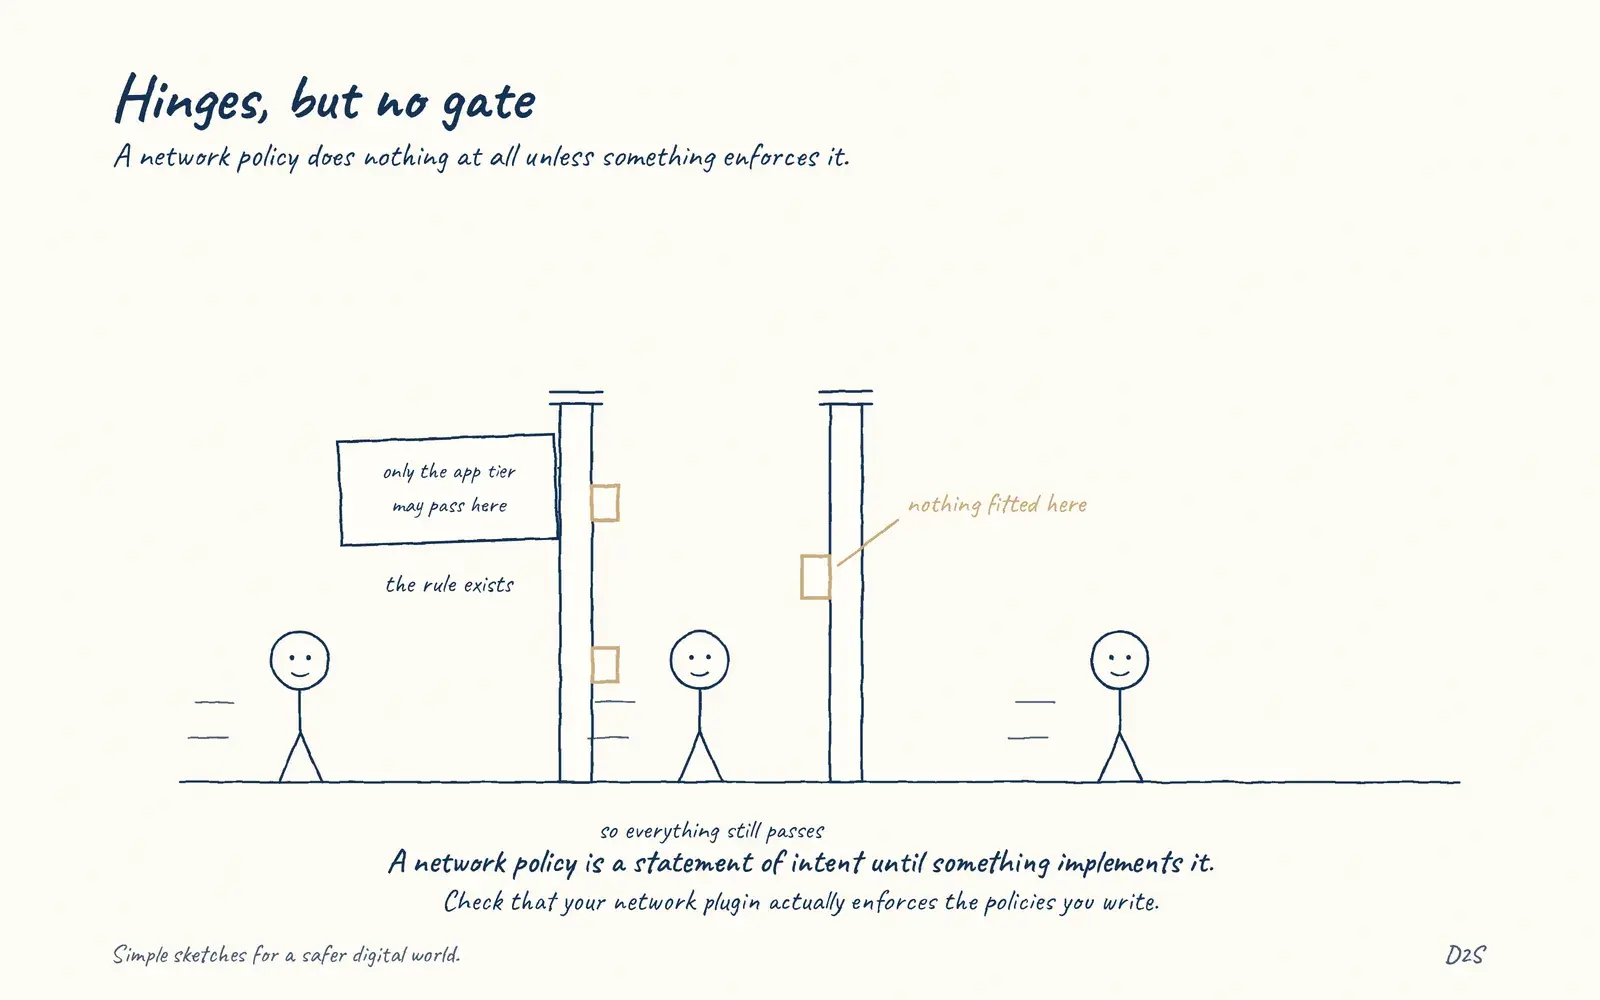 NetworkPolicy needs an enforcement engineHinges, but no gate
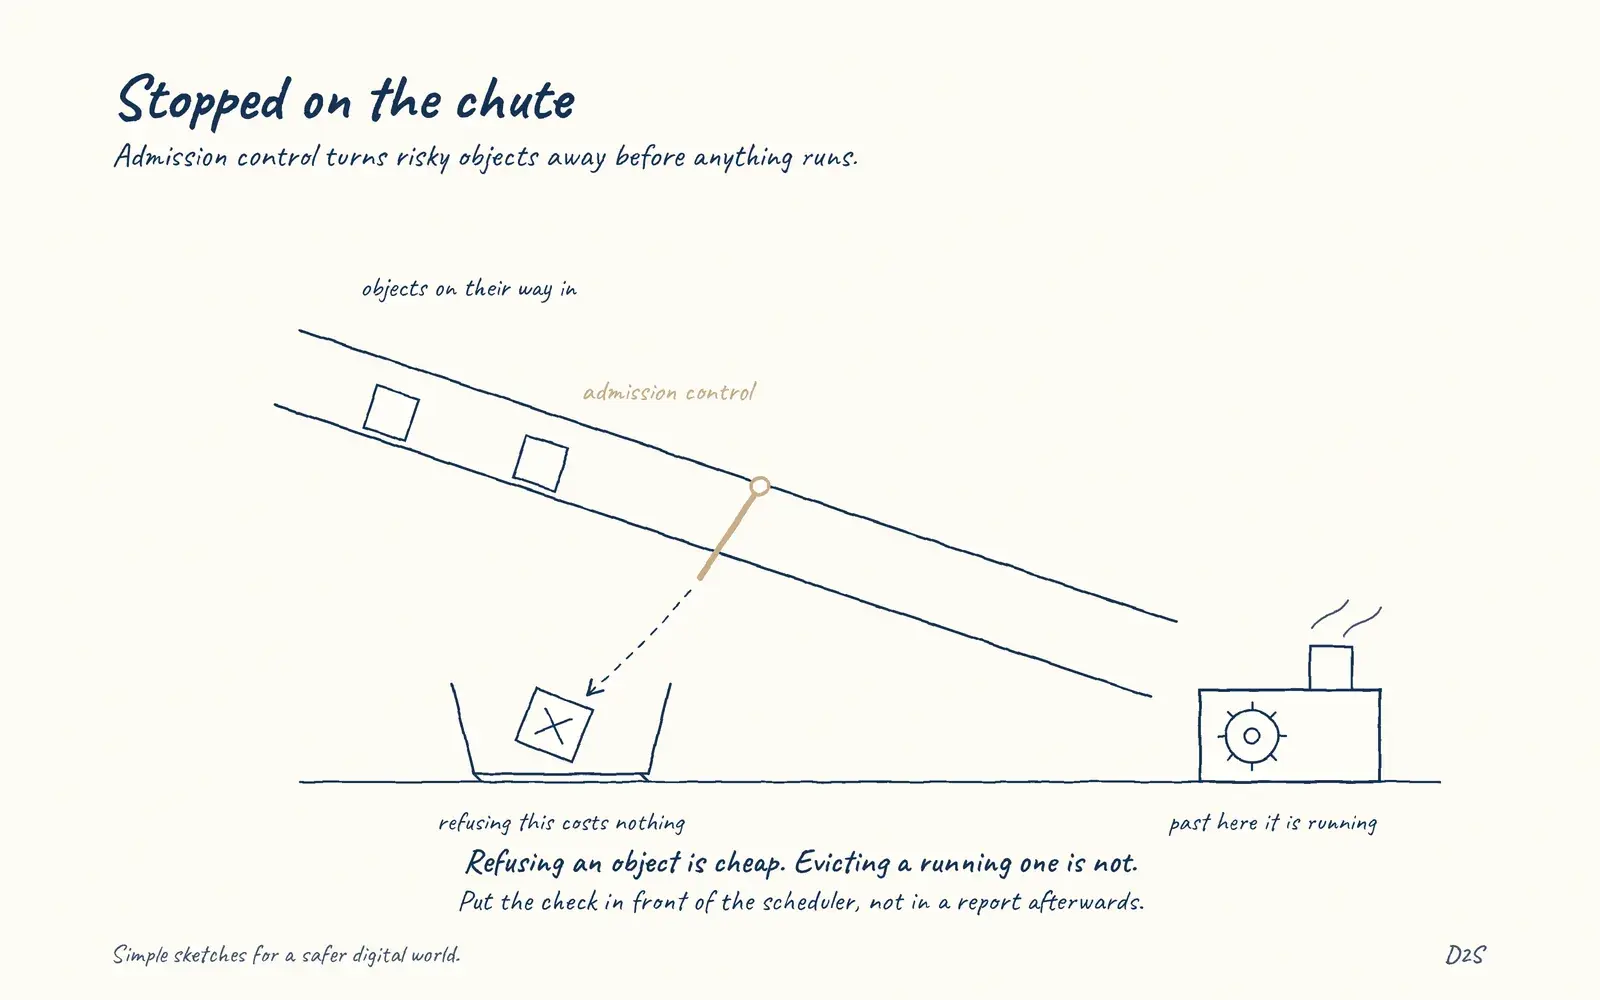 Admission control can stop risky objects before they runStopped on the chute
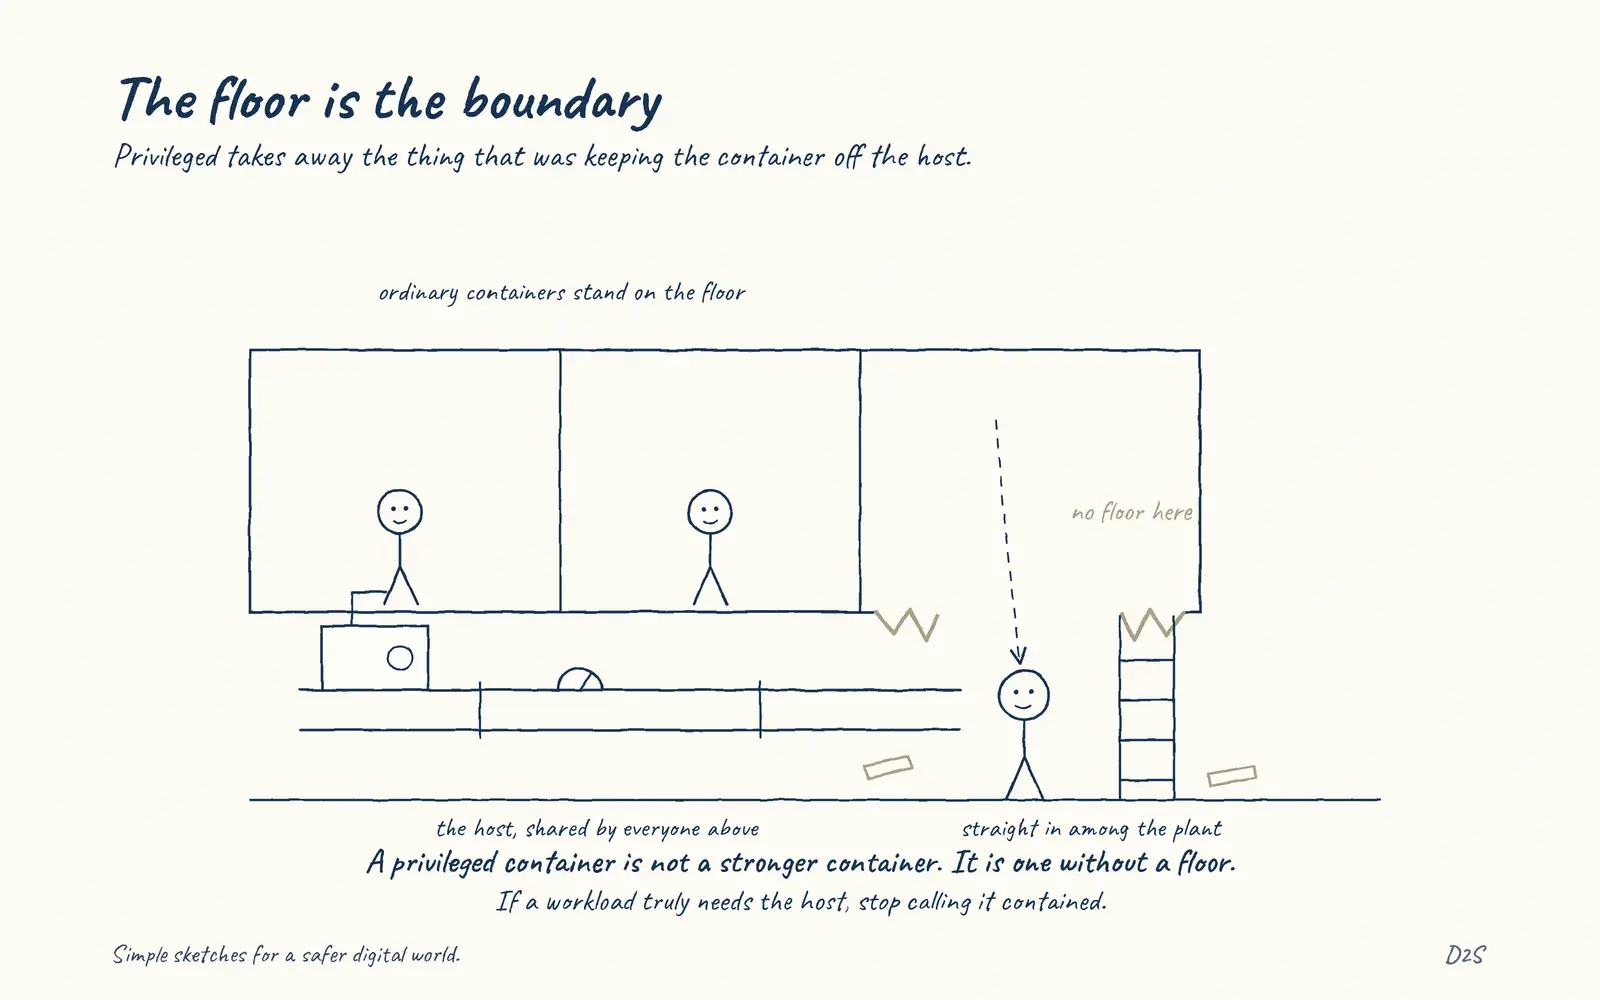 Privileged containers weaken the host boundaryThe floor is the boundary
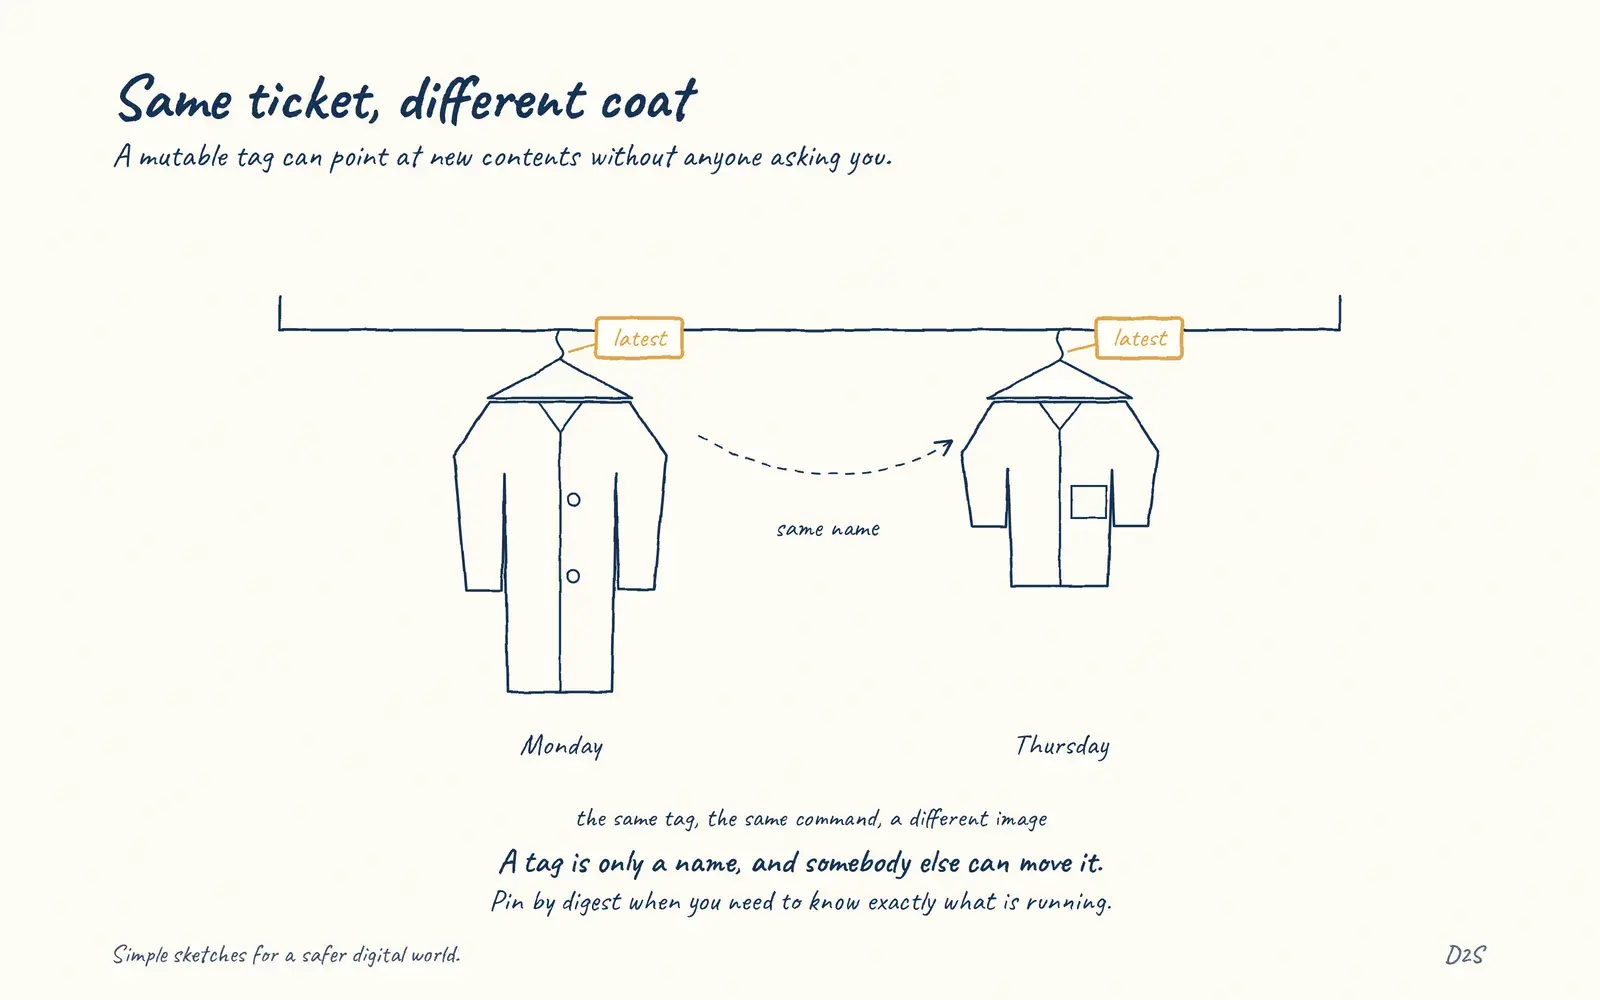 Mutable image tags can move underneath youSame ticket, different coat
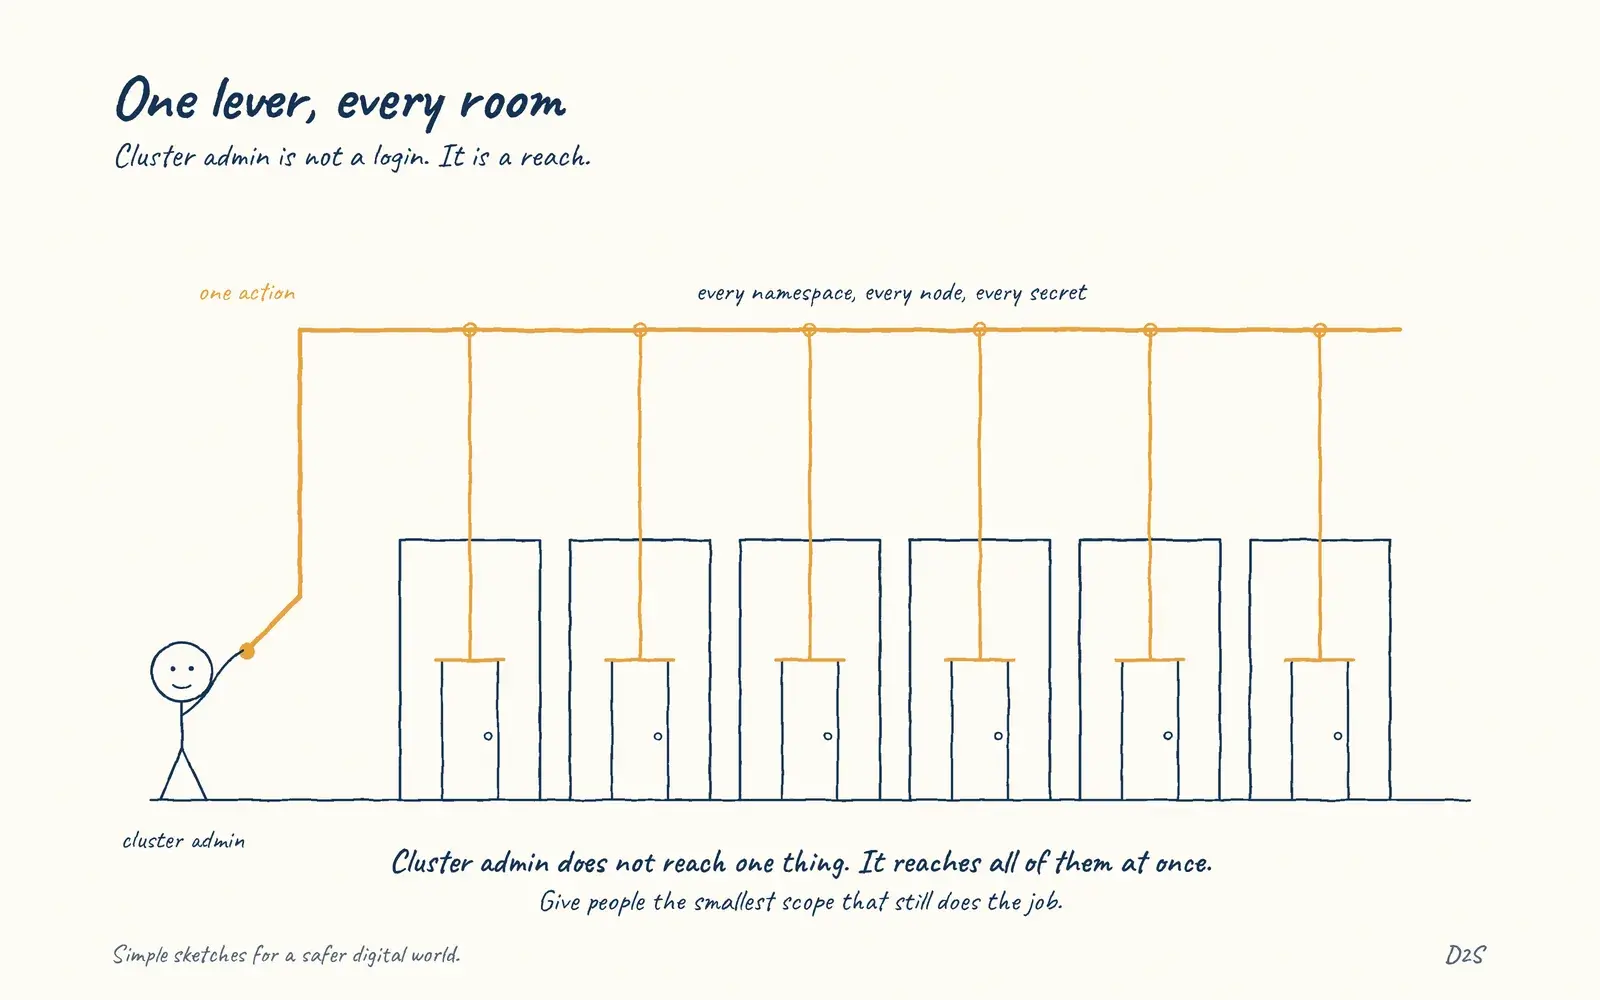 Cluster admin has a very large blast radiusOne lever, every room