
Threat actors & ATT&CK
Who does this, how they work, and how to model it before they arrive.
25 sketches
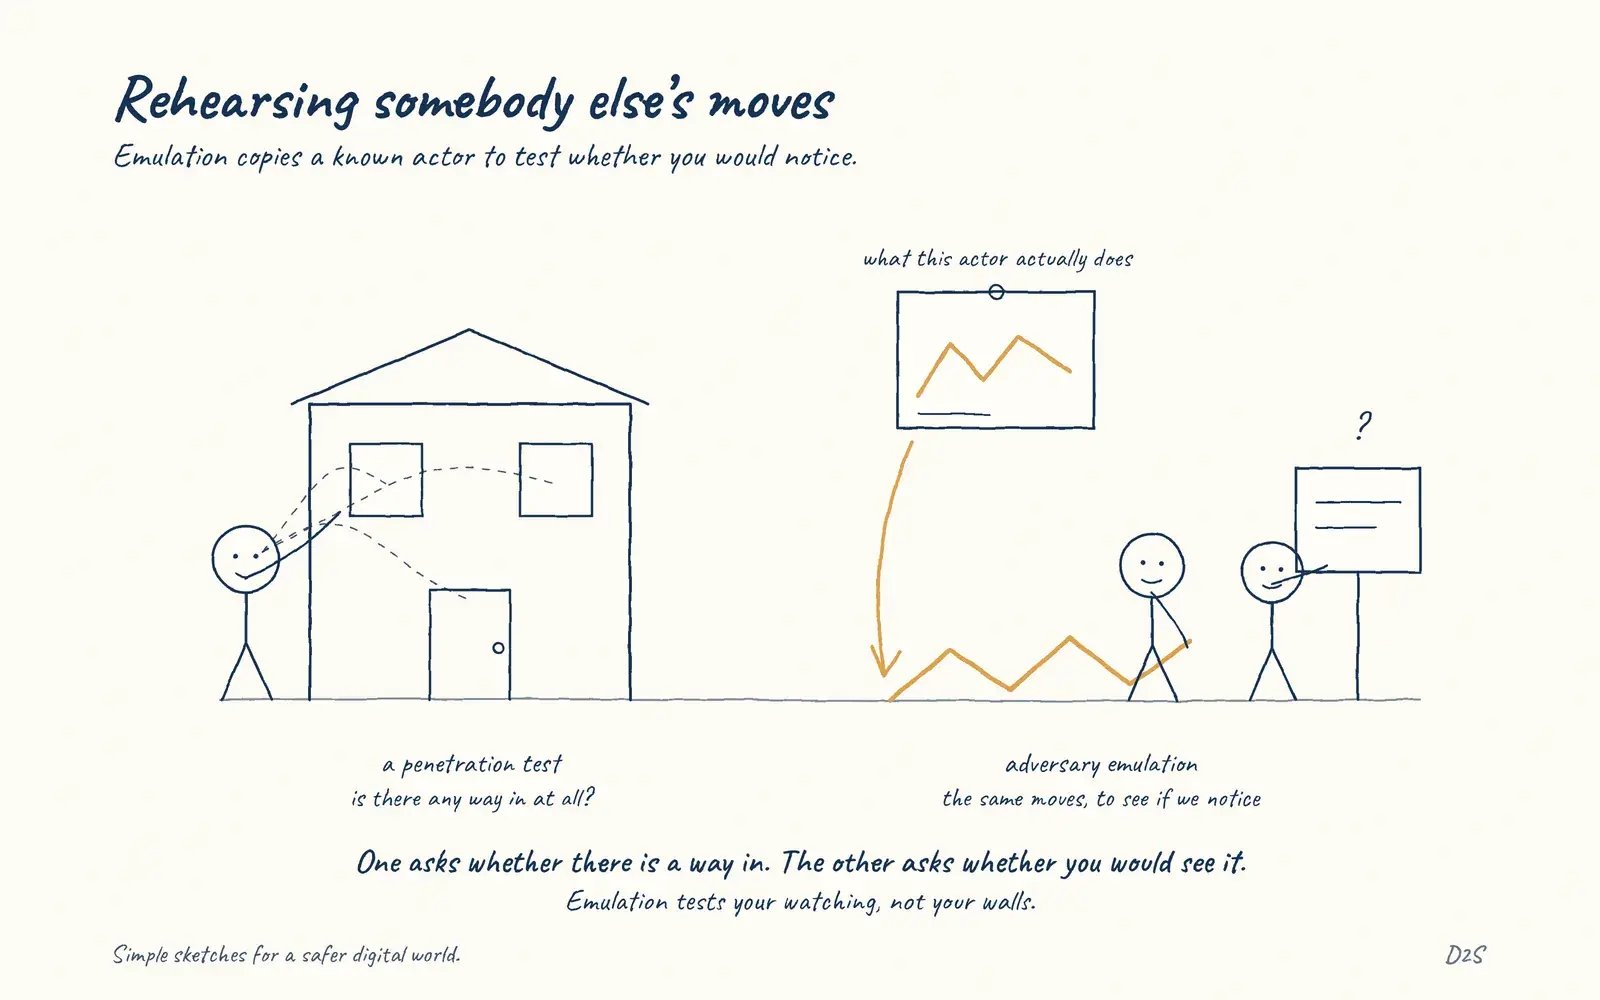 Adversary emulationRehearsing somebody else's moves
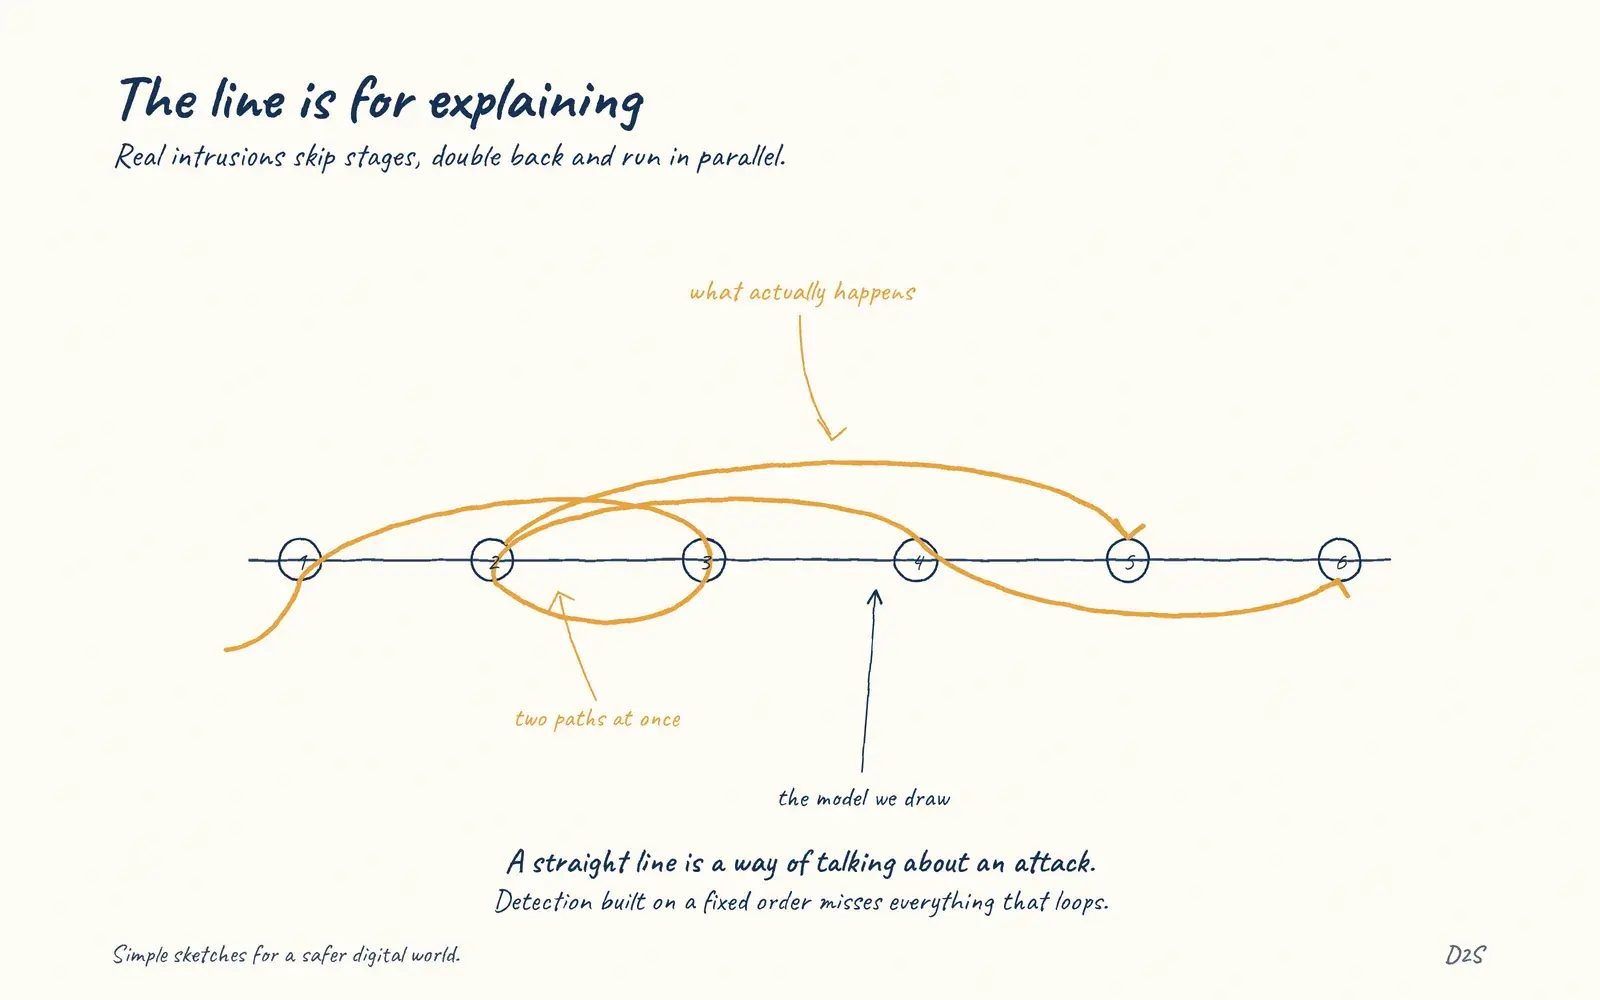 Attack chainsThe line is for explaining
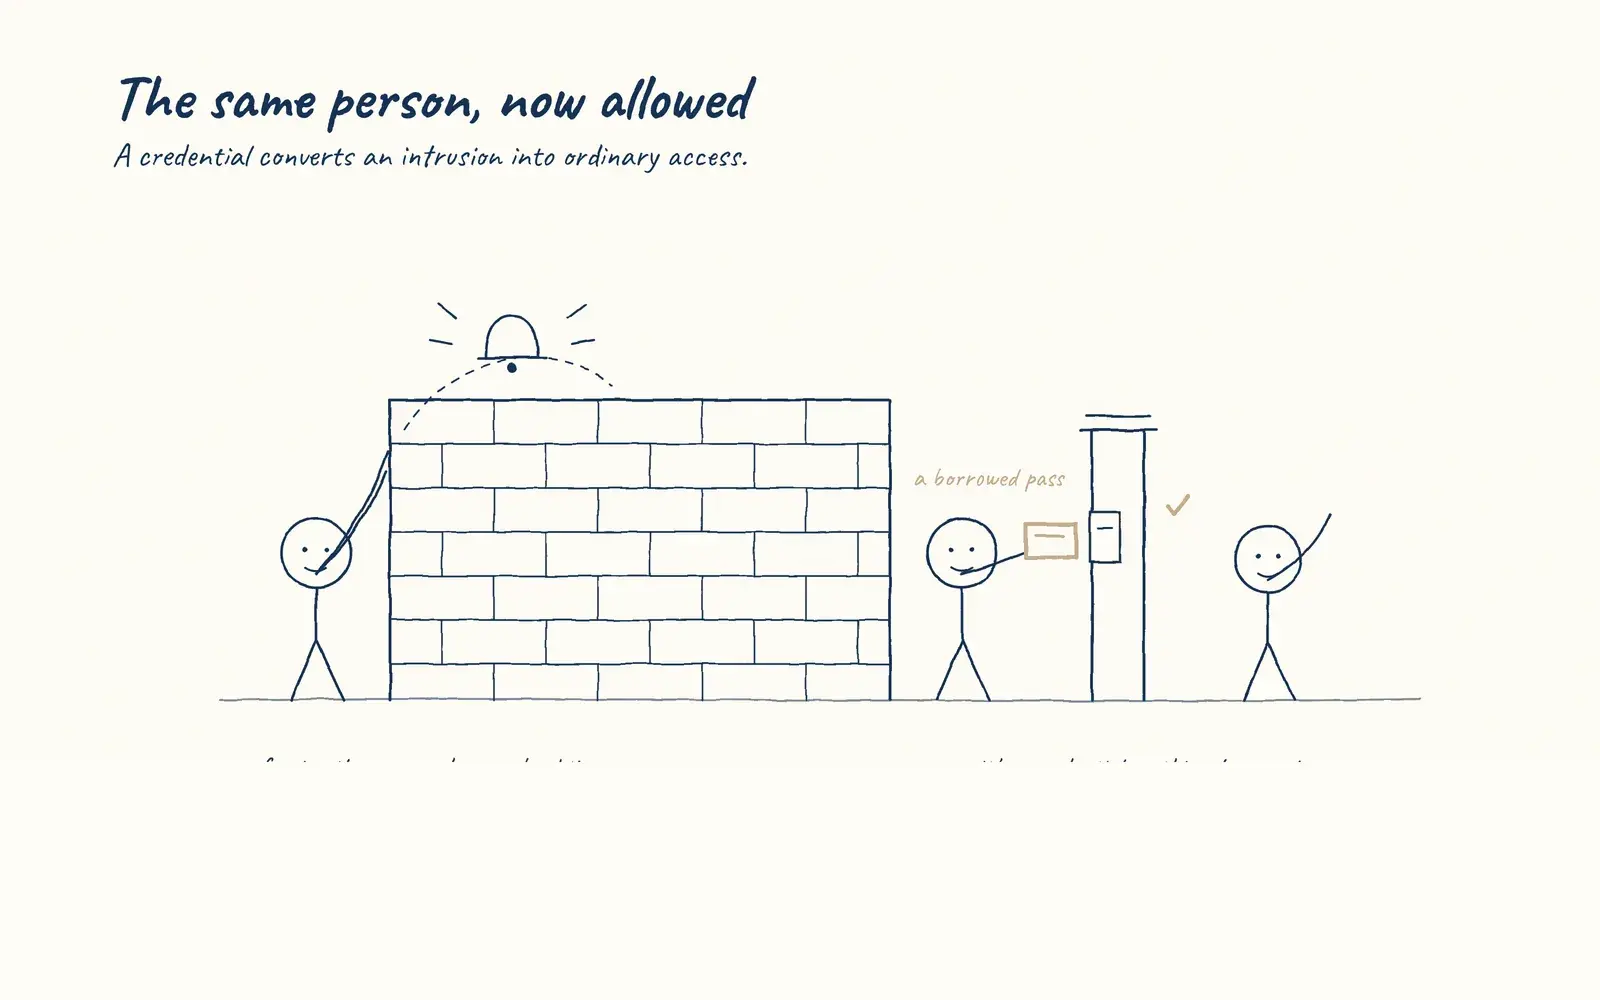 Credential accessThe same person, now allowed
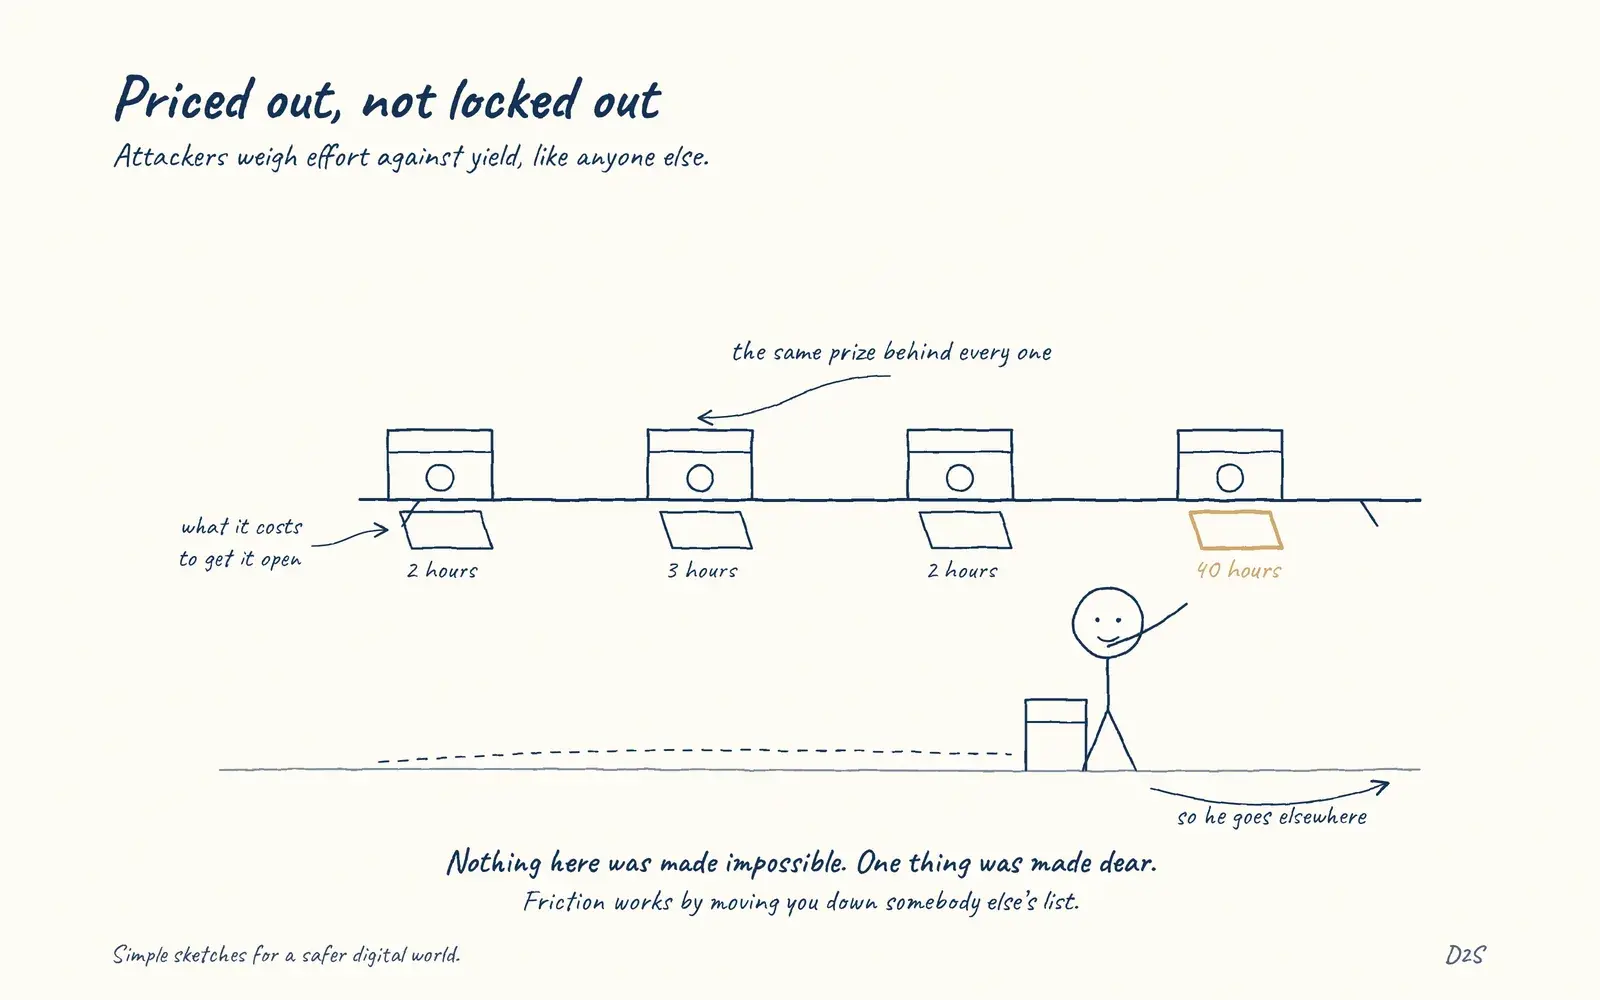 Cybercrime economicsPriced out, not locked out
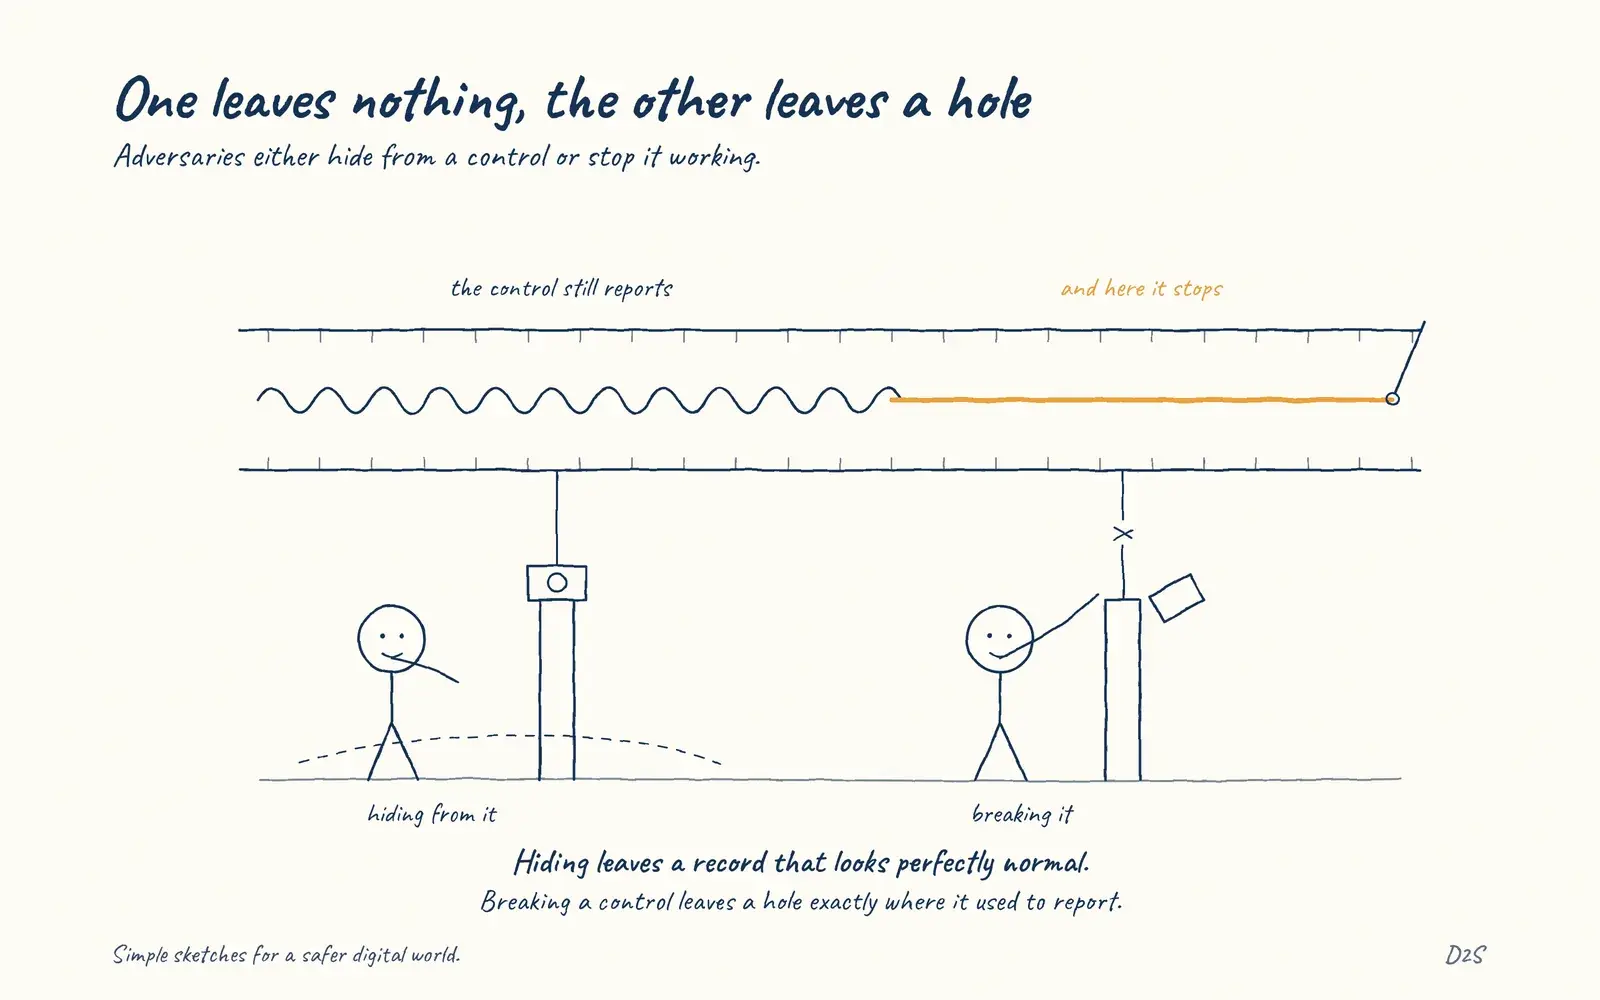 Defence evasionOne leaves nothing, the other leaves a hole
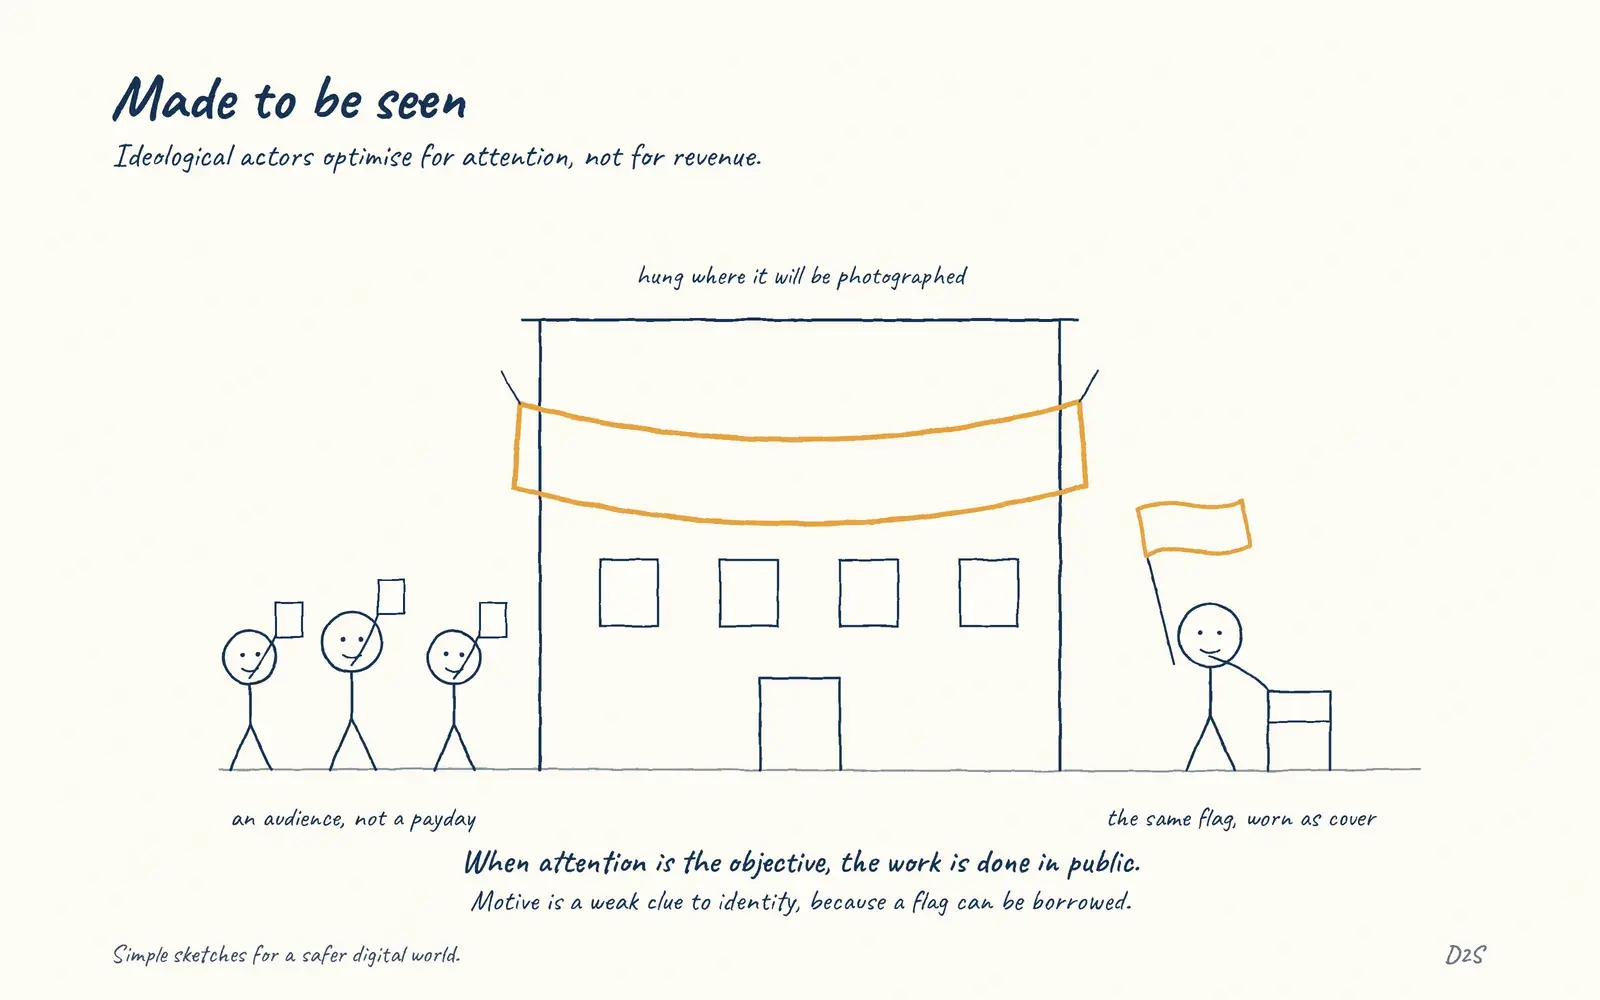 HacktivismMade to be seen
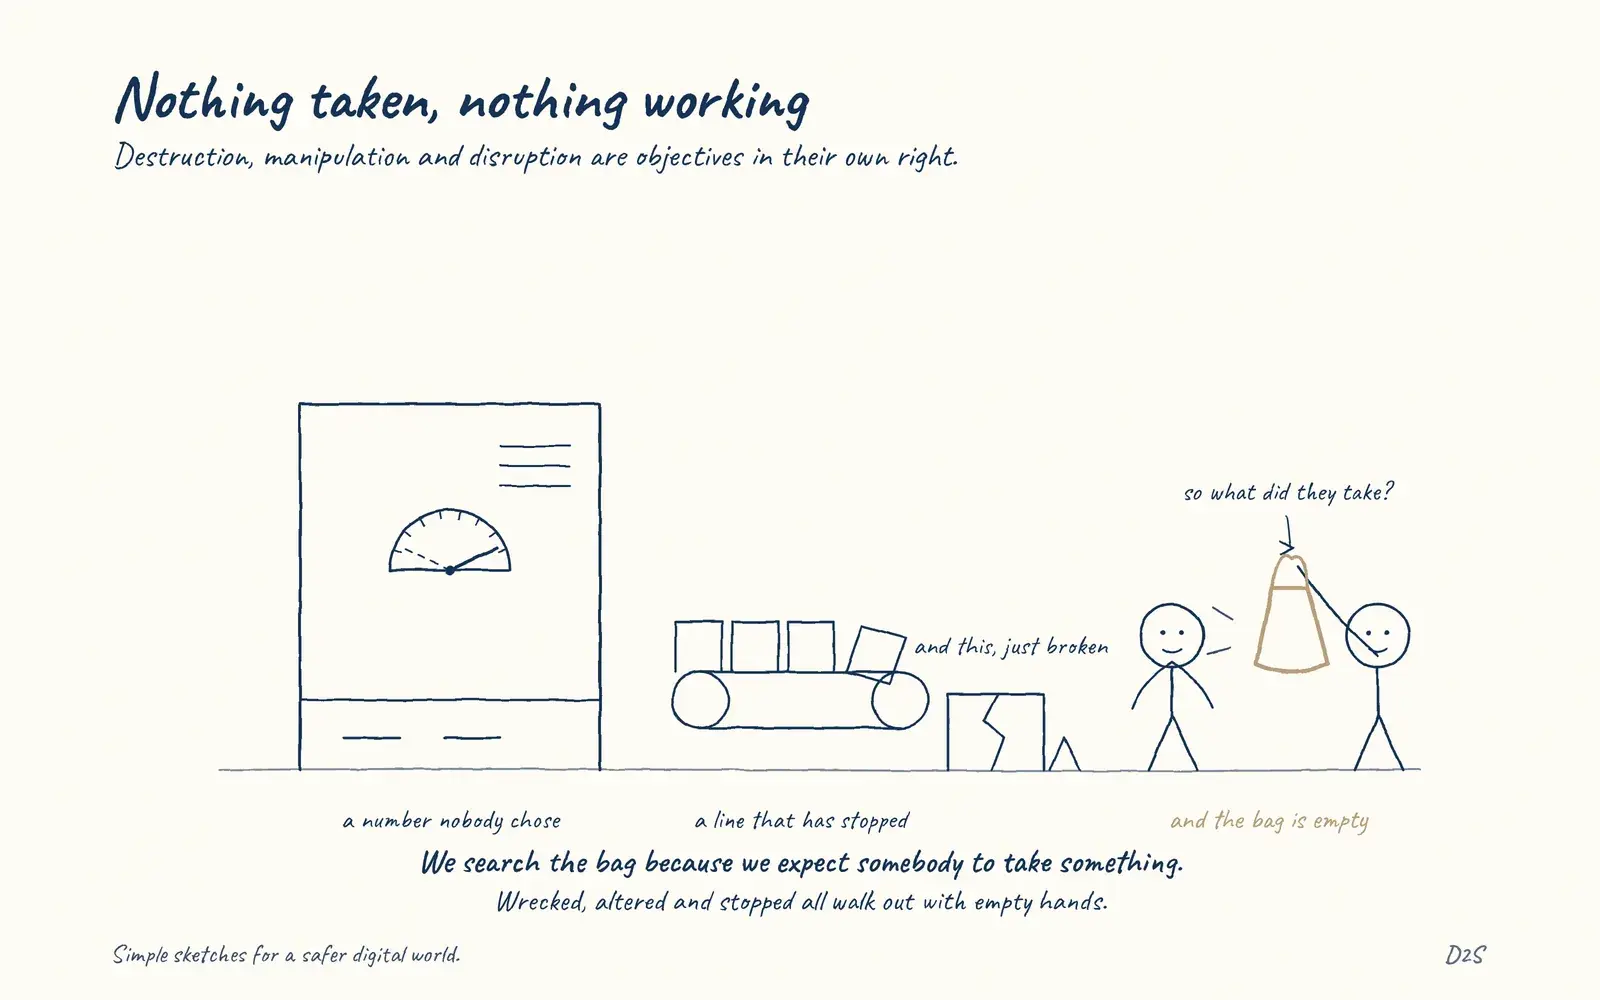 ImpactNothing taken, nothing working
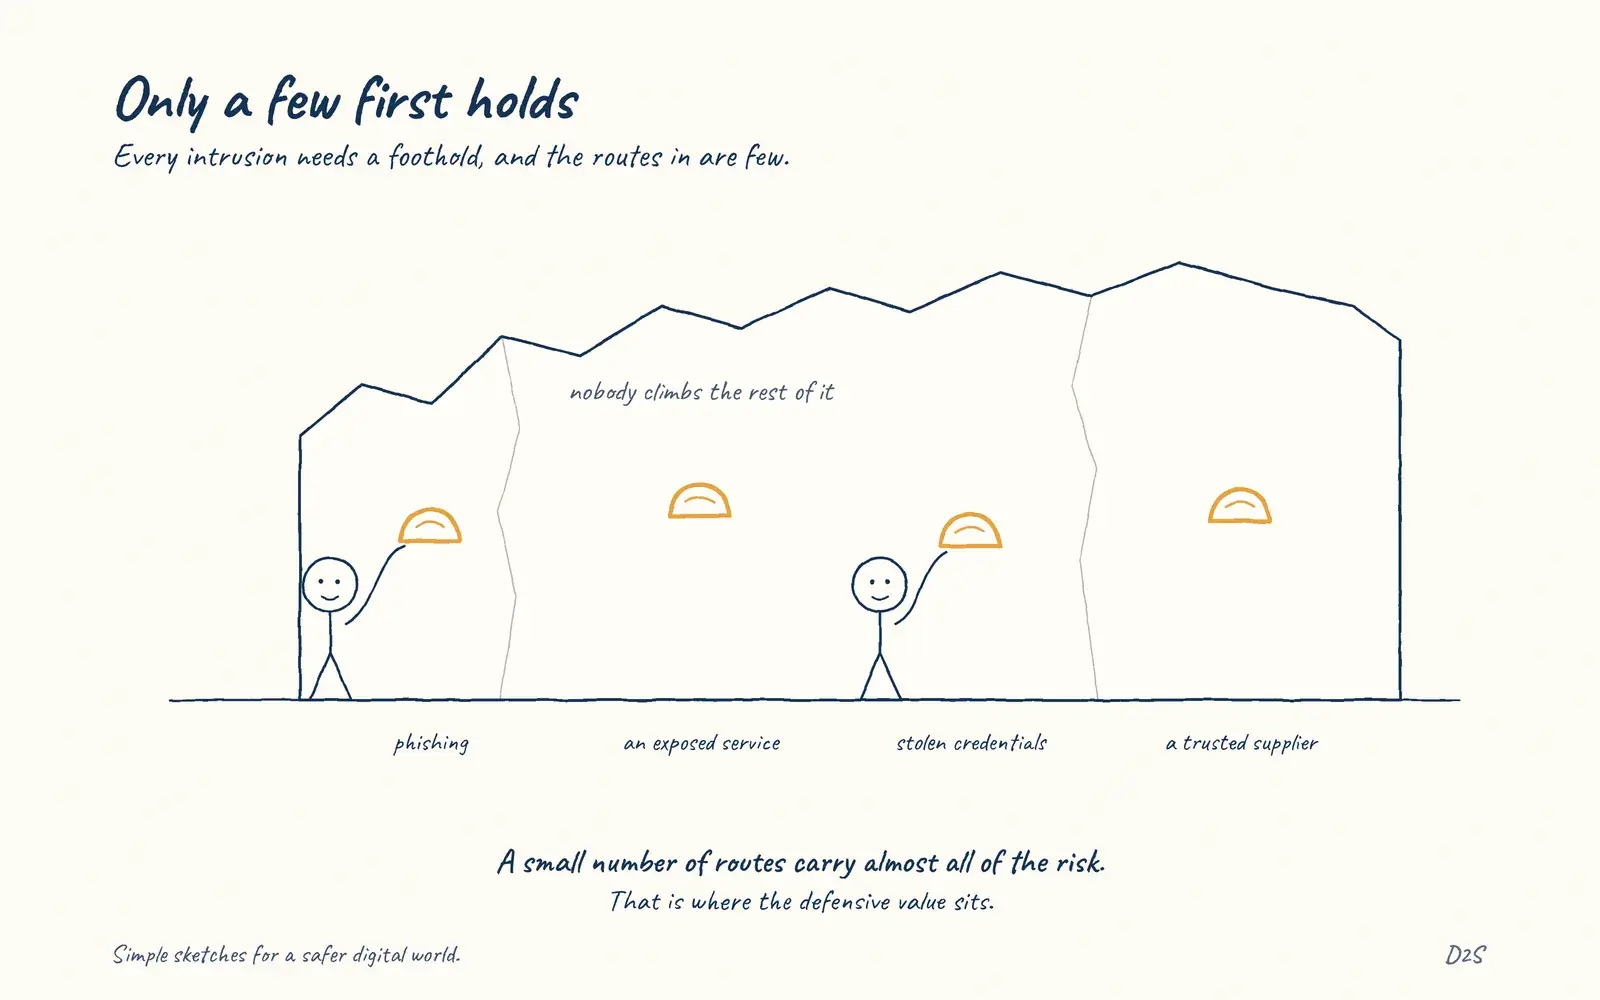 Initial accessOnly a few first holds
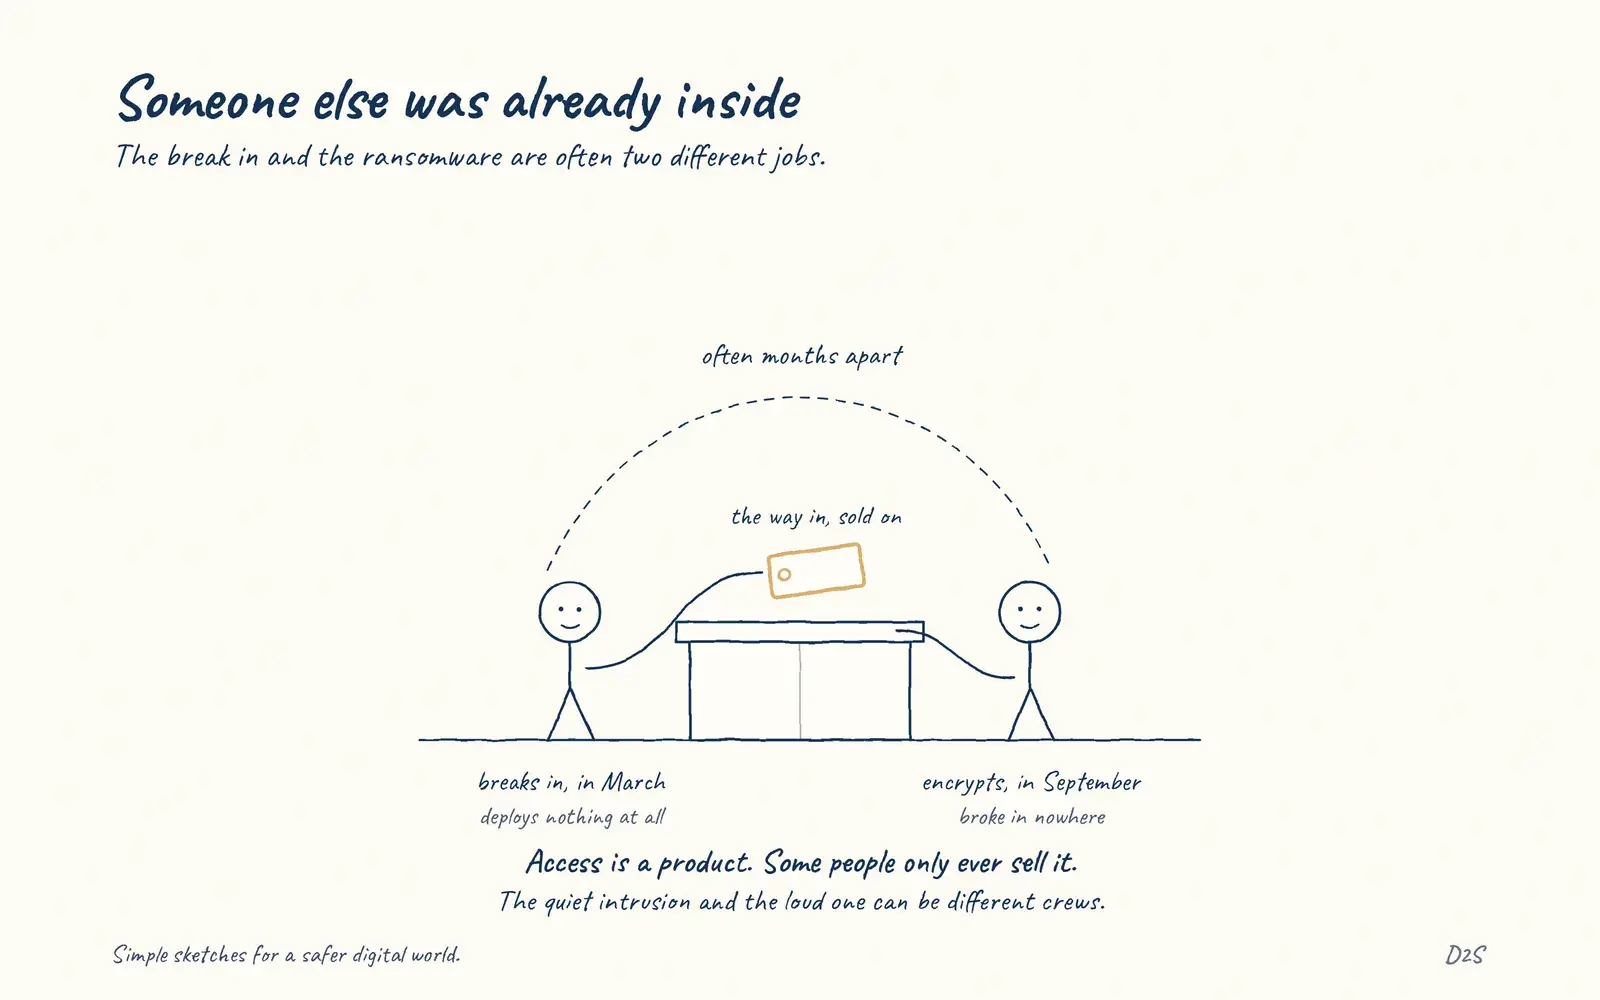 Initial access brokersSomeone else was already inside
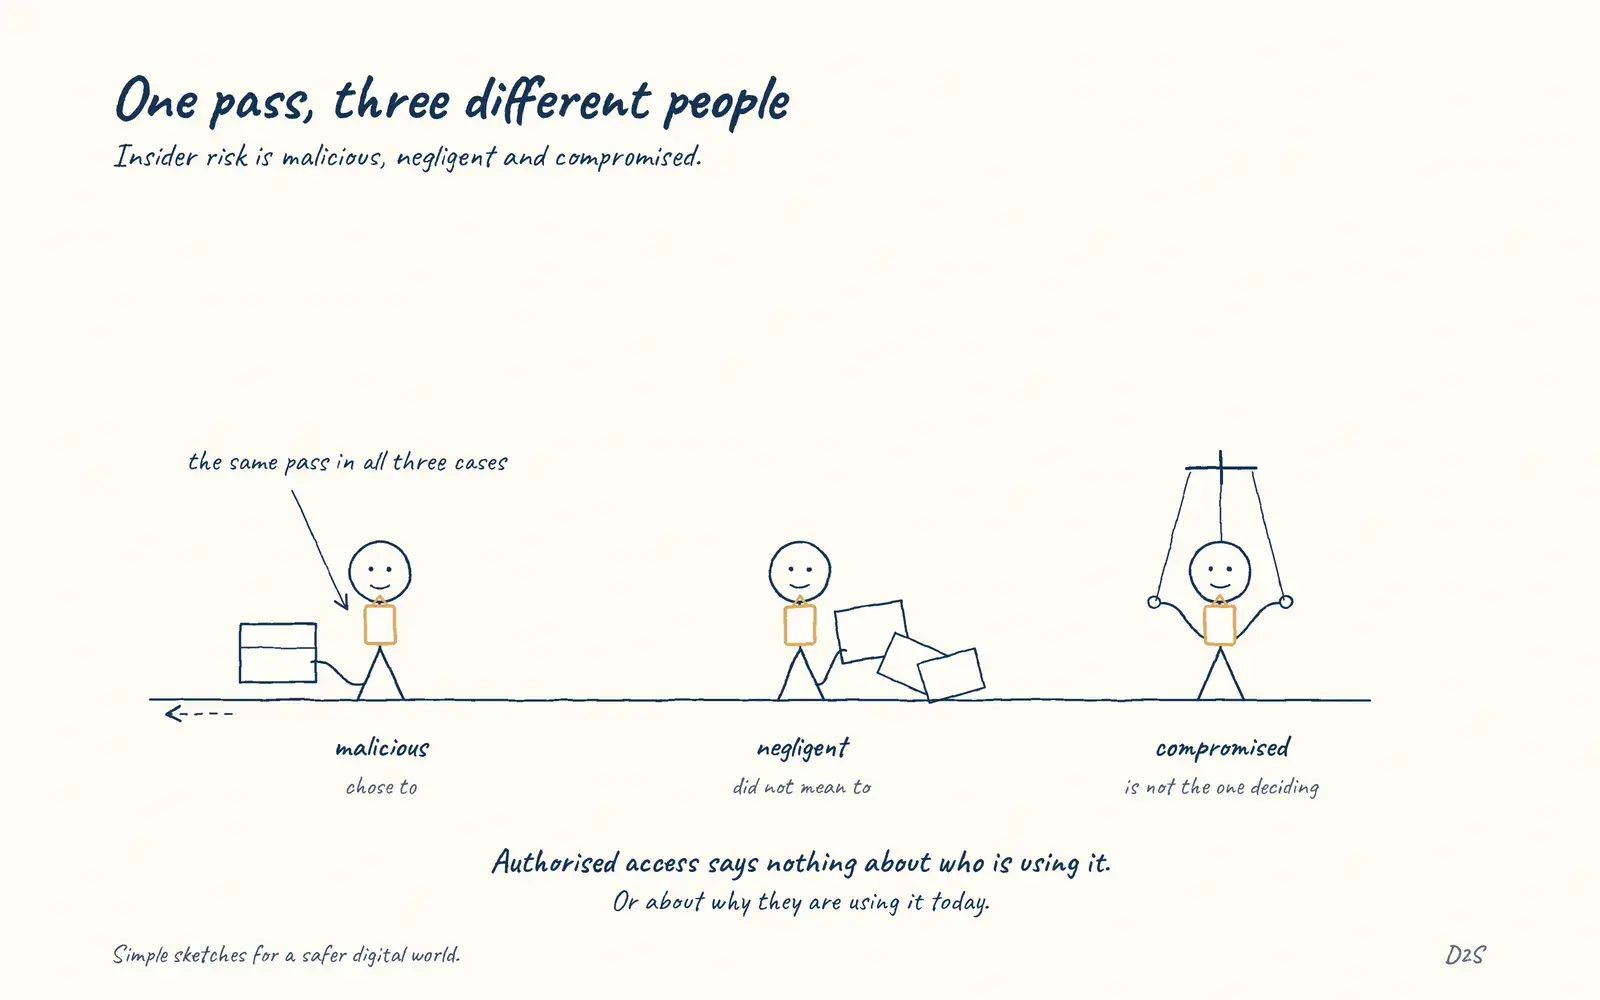 Insider threatOne pass, three different people
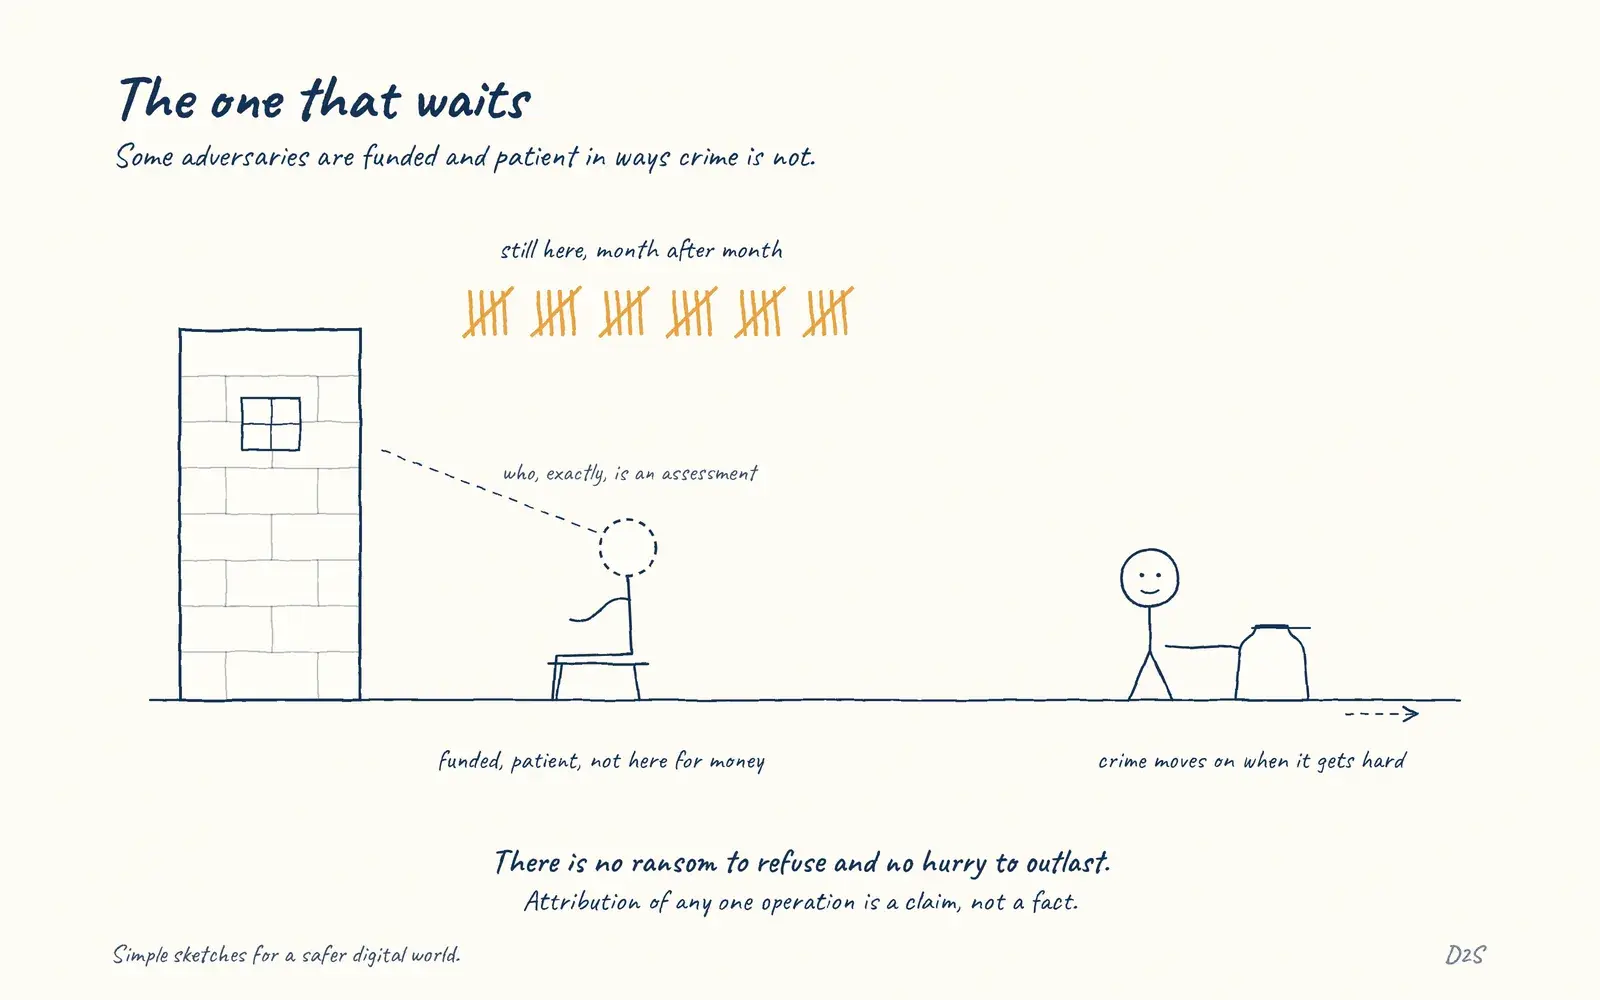 Nation-state operationsThe one that waits
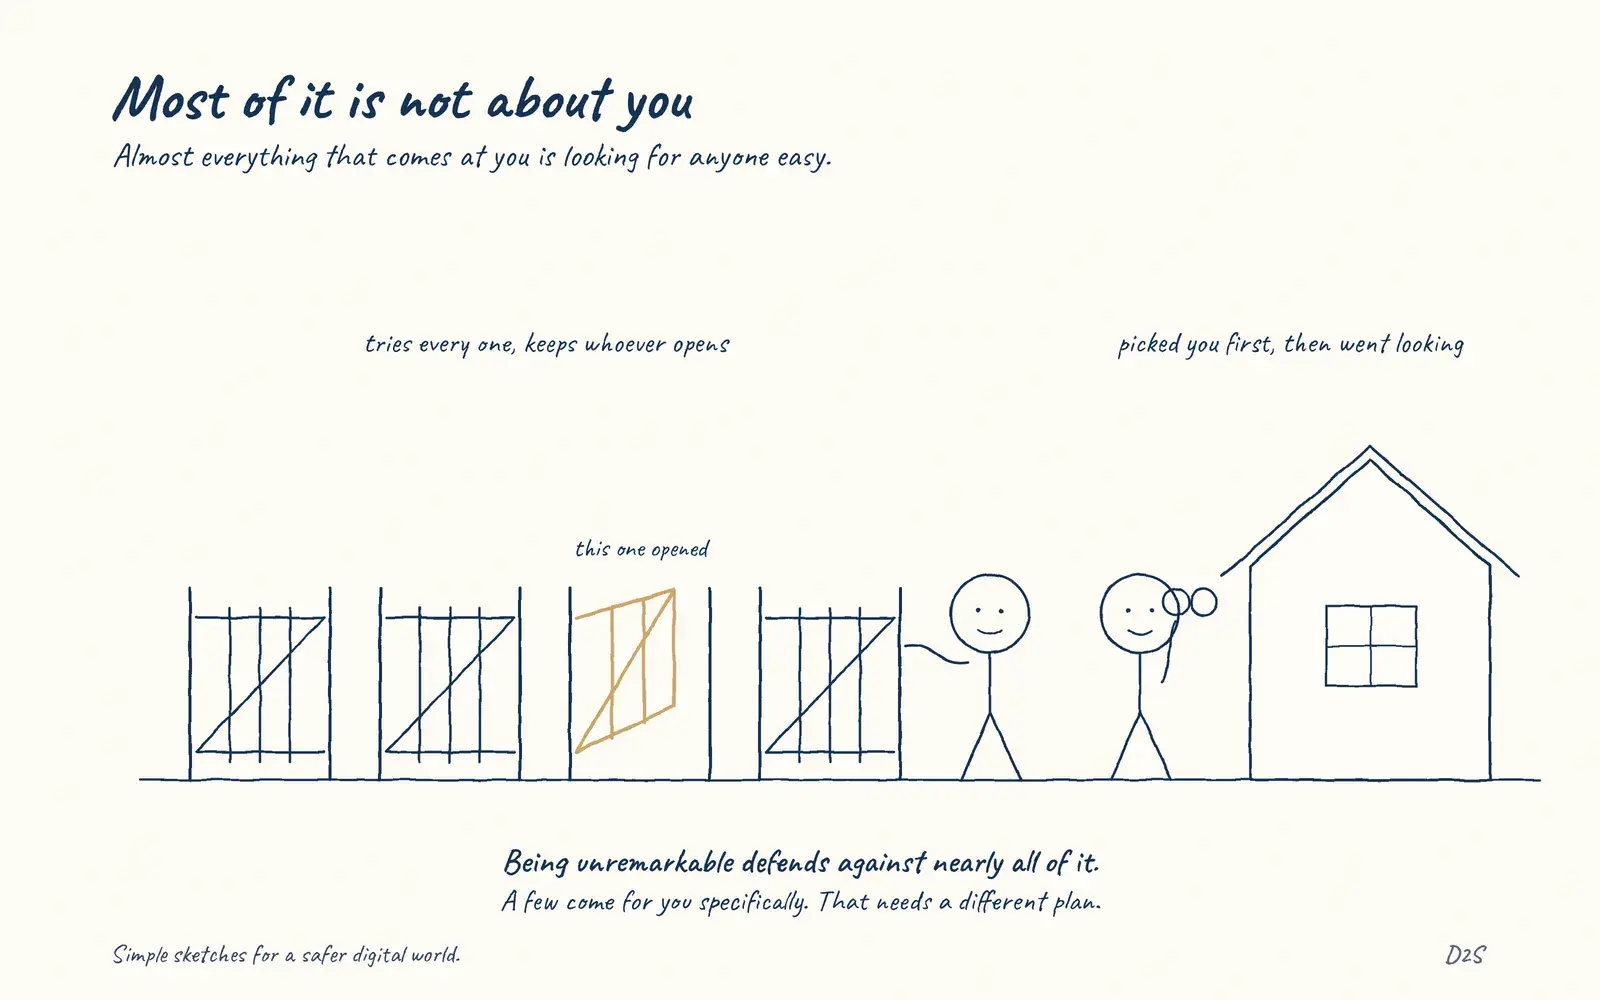 Opportunistic attacksMost of it is not about you
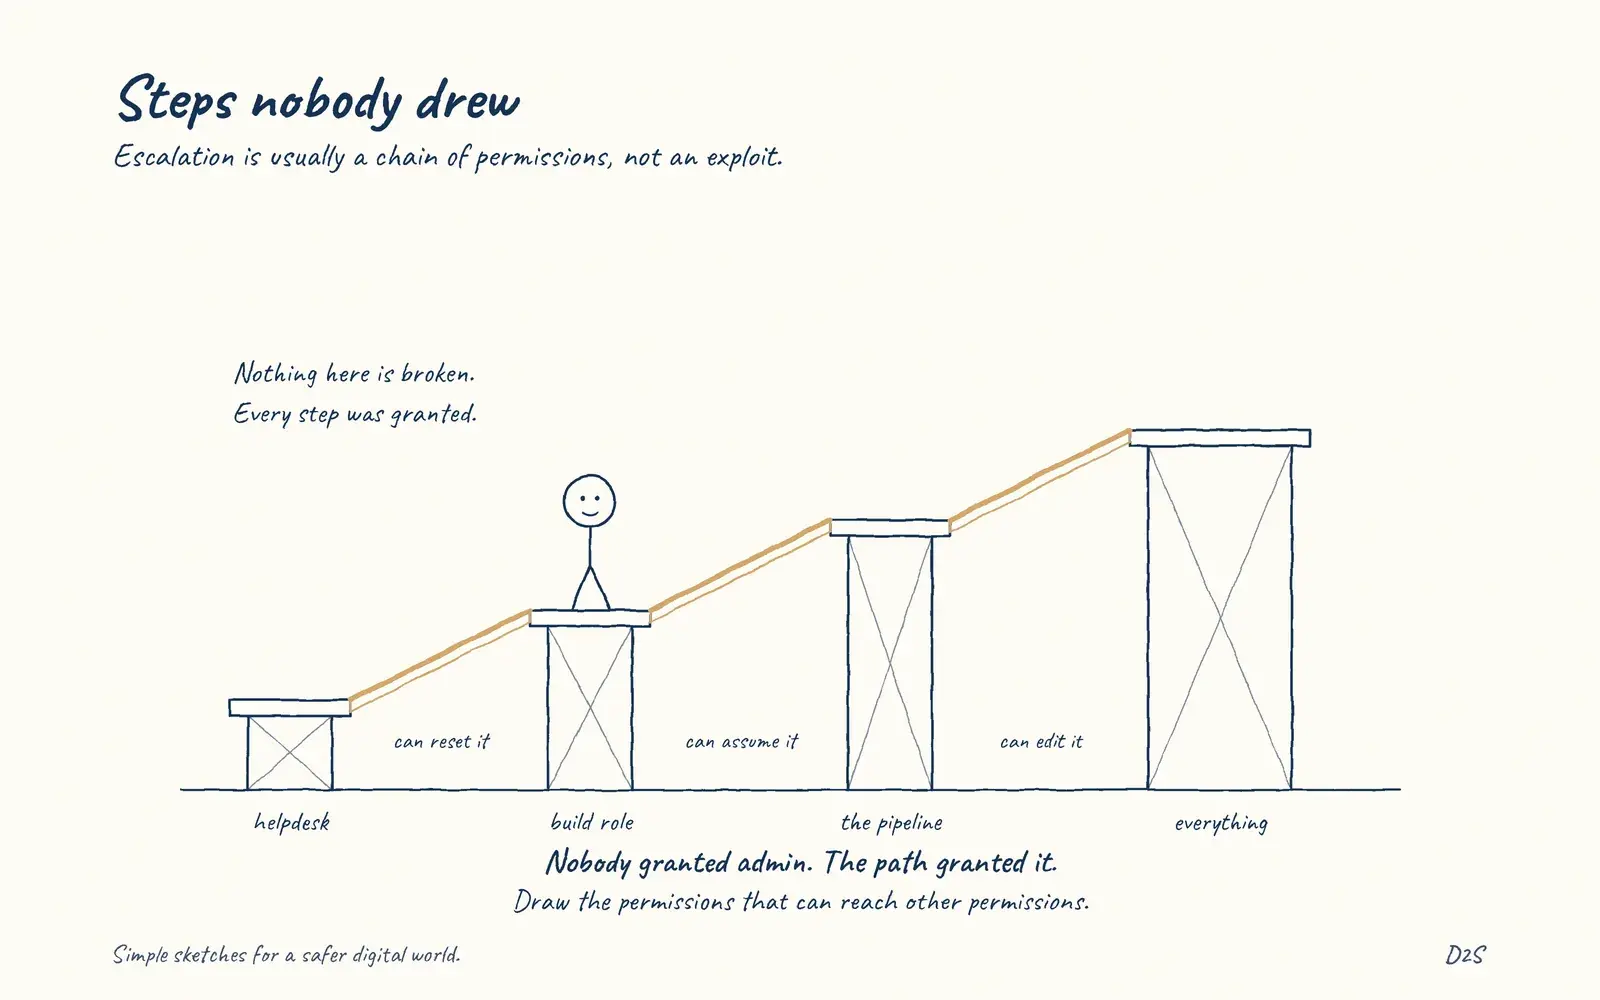 Privilege escalationSteps nobody drew
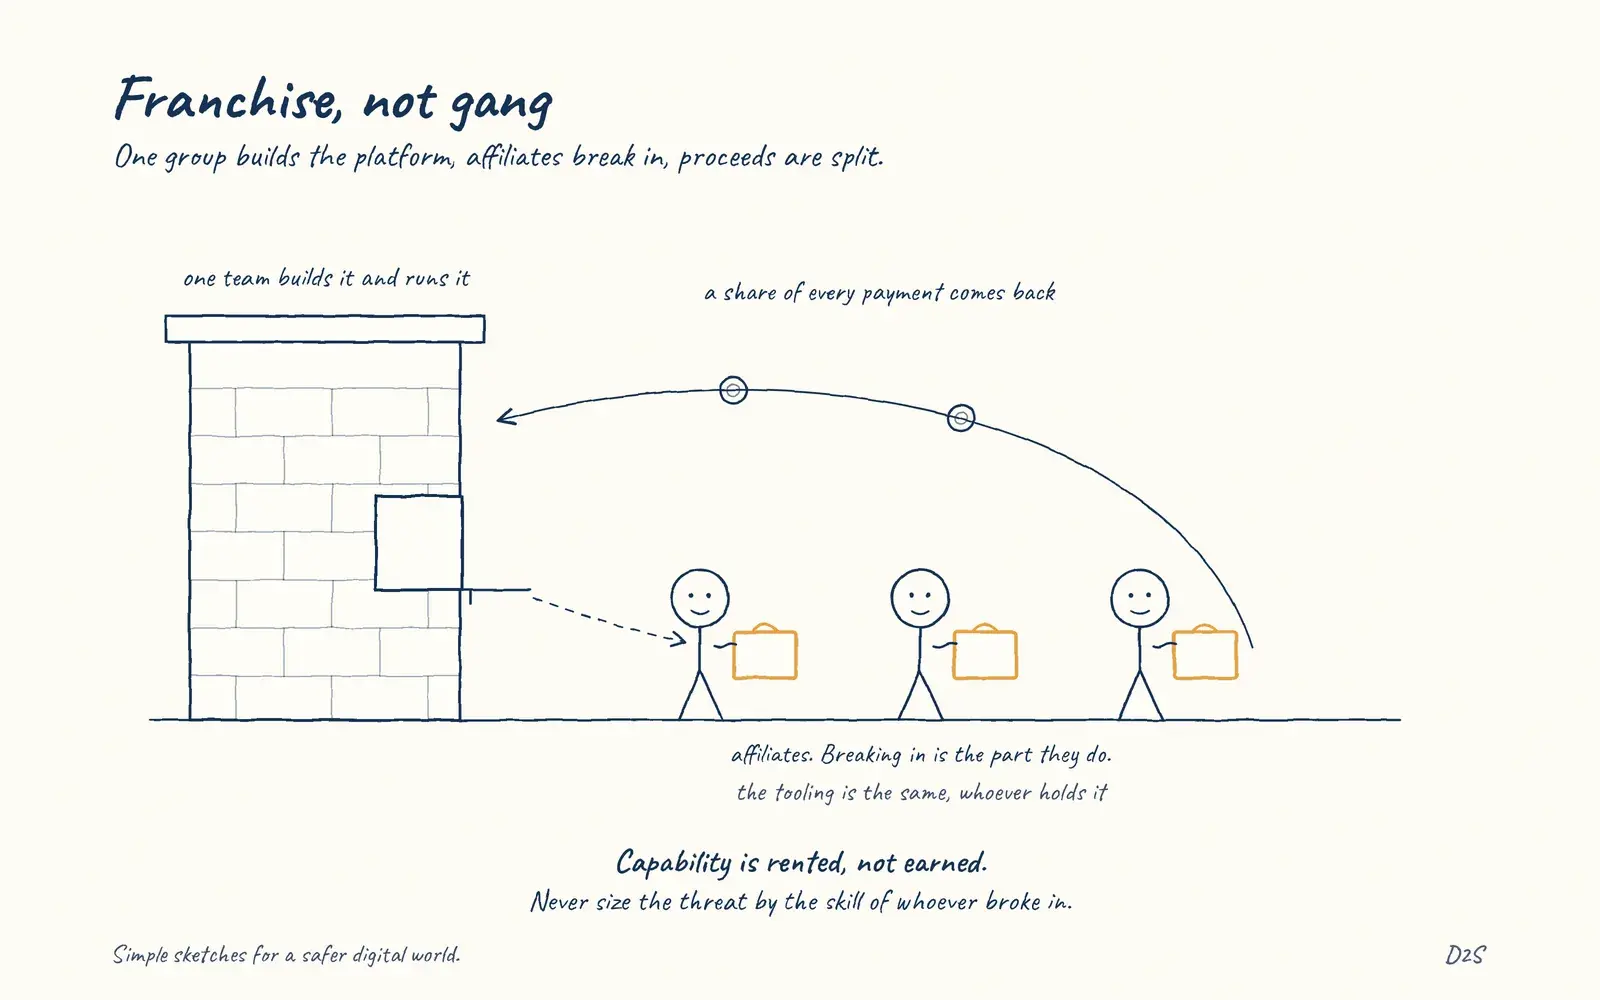 Ransomware-as-a-serviceFranchise, not gang
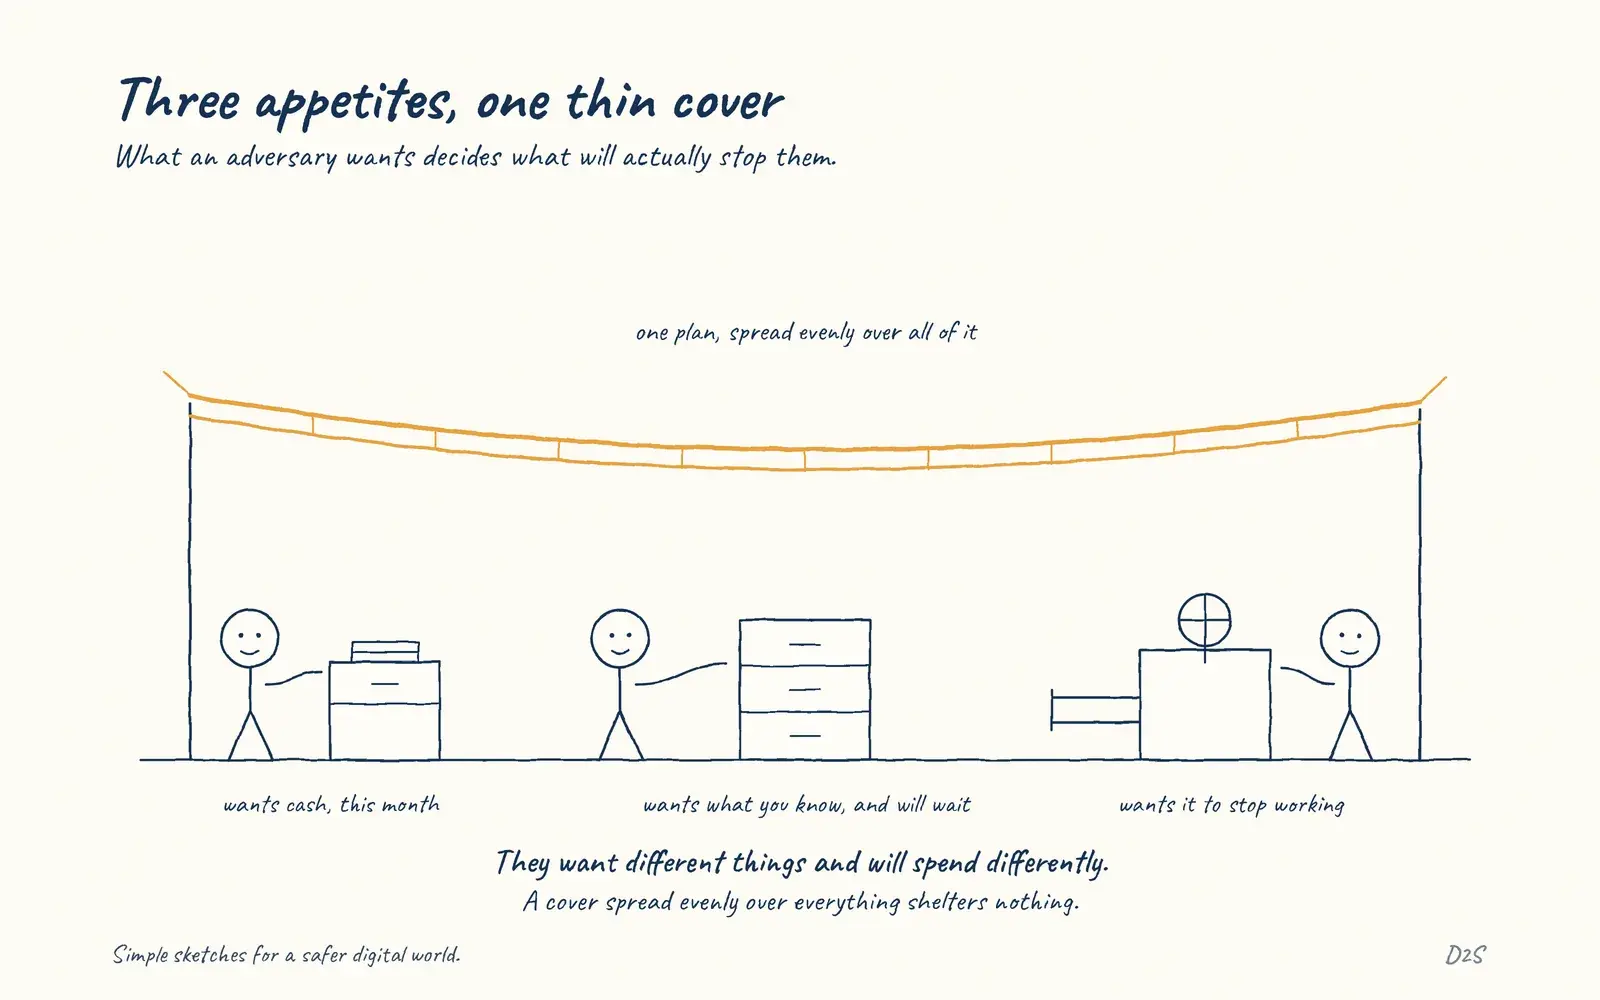 Threat actorsThree appetites, one thin cover
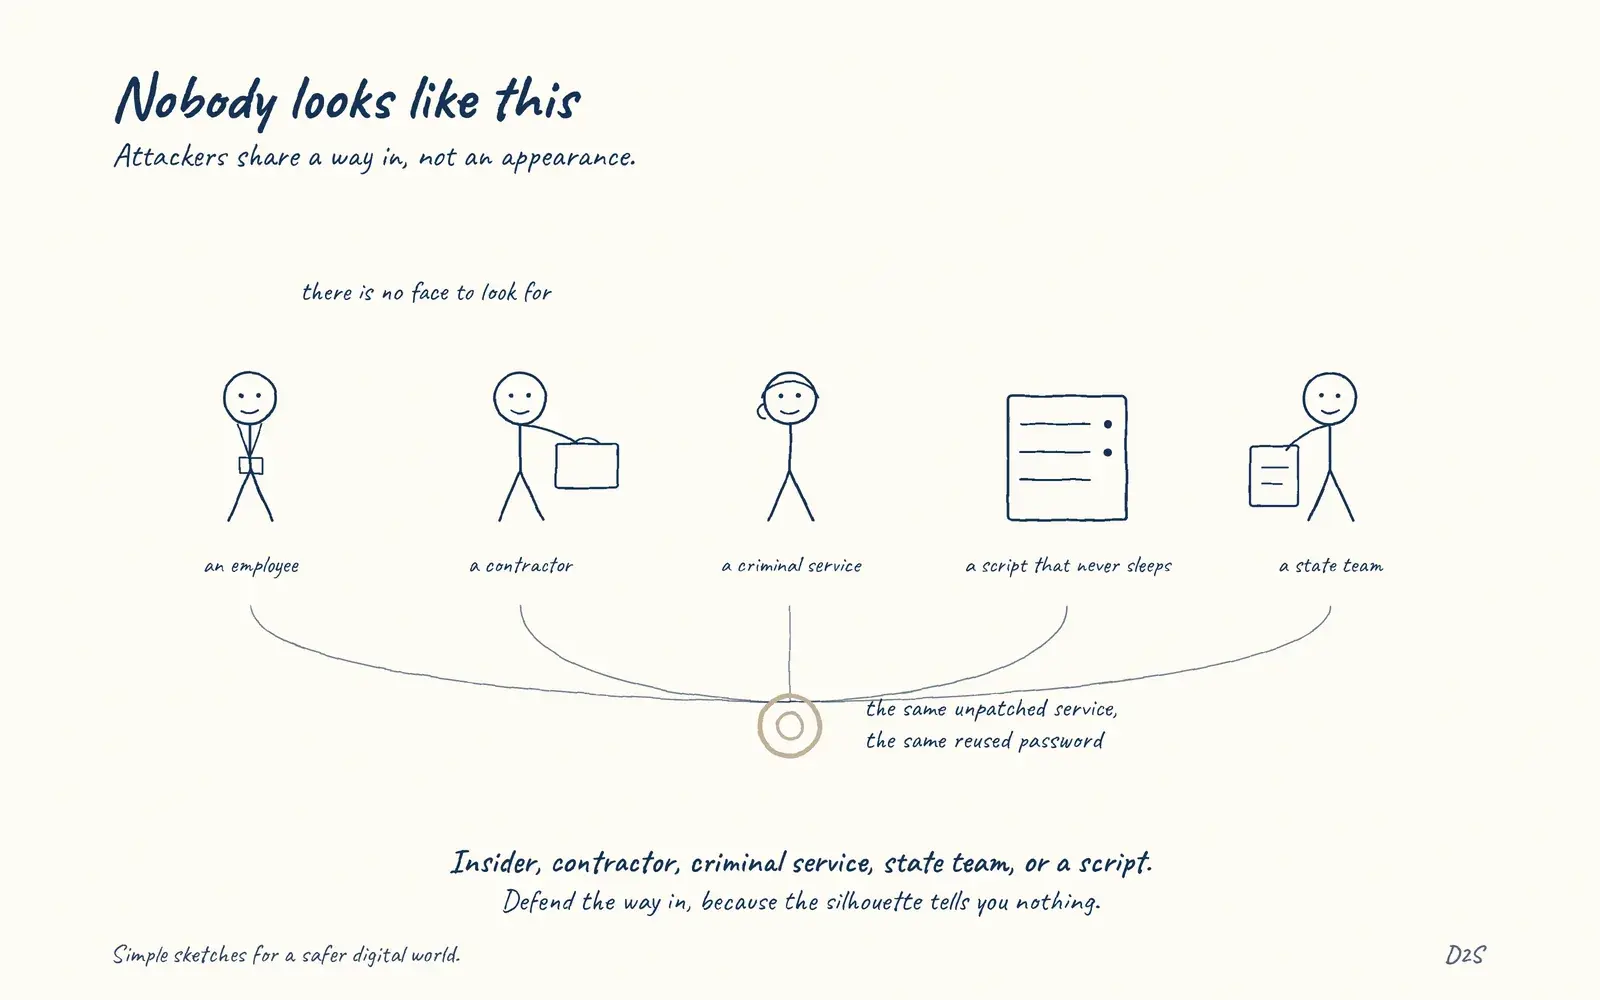 'hackers always wear hoodies'Nobody looks like this
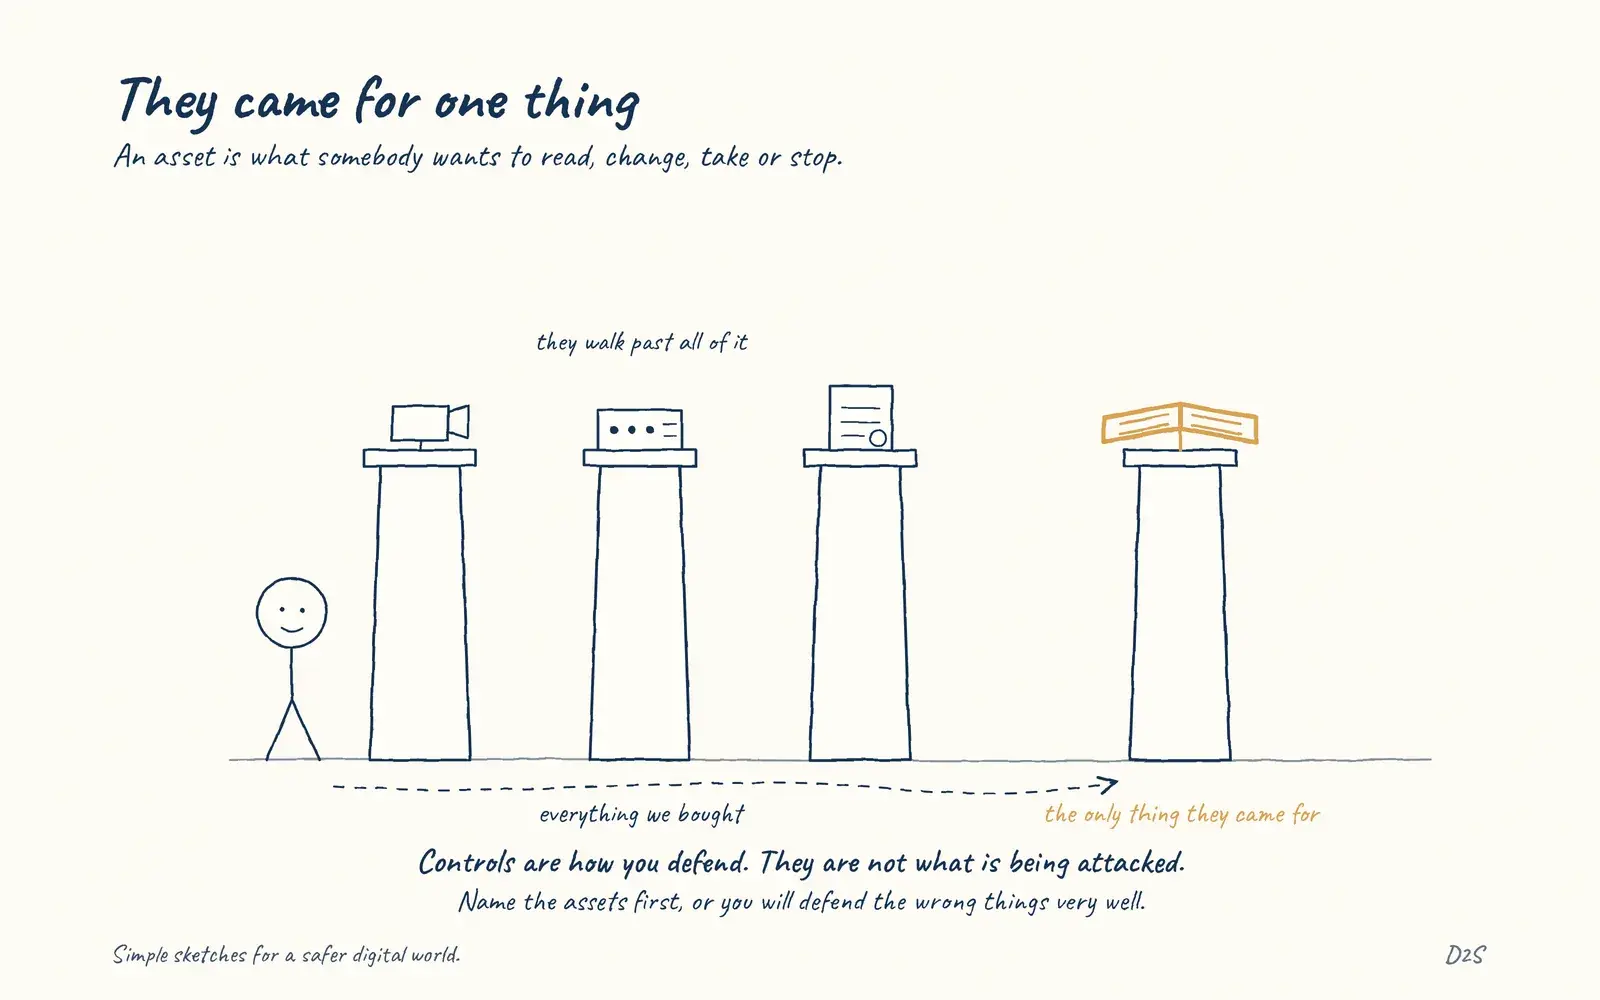 Assets are what attackers want to affectThey came for one thing
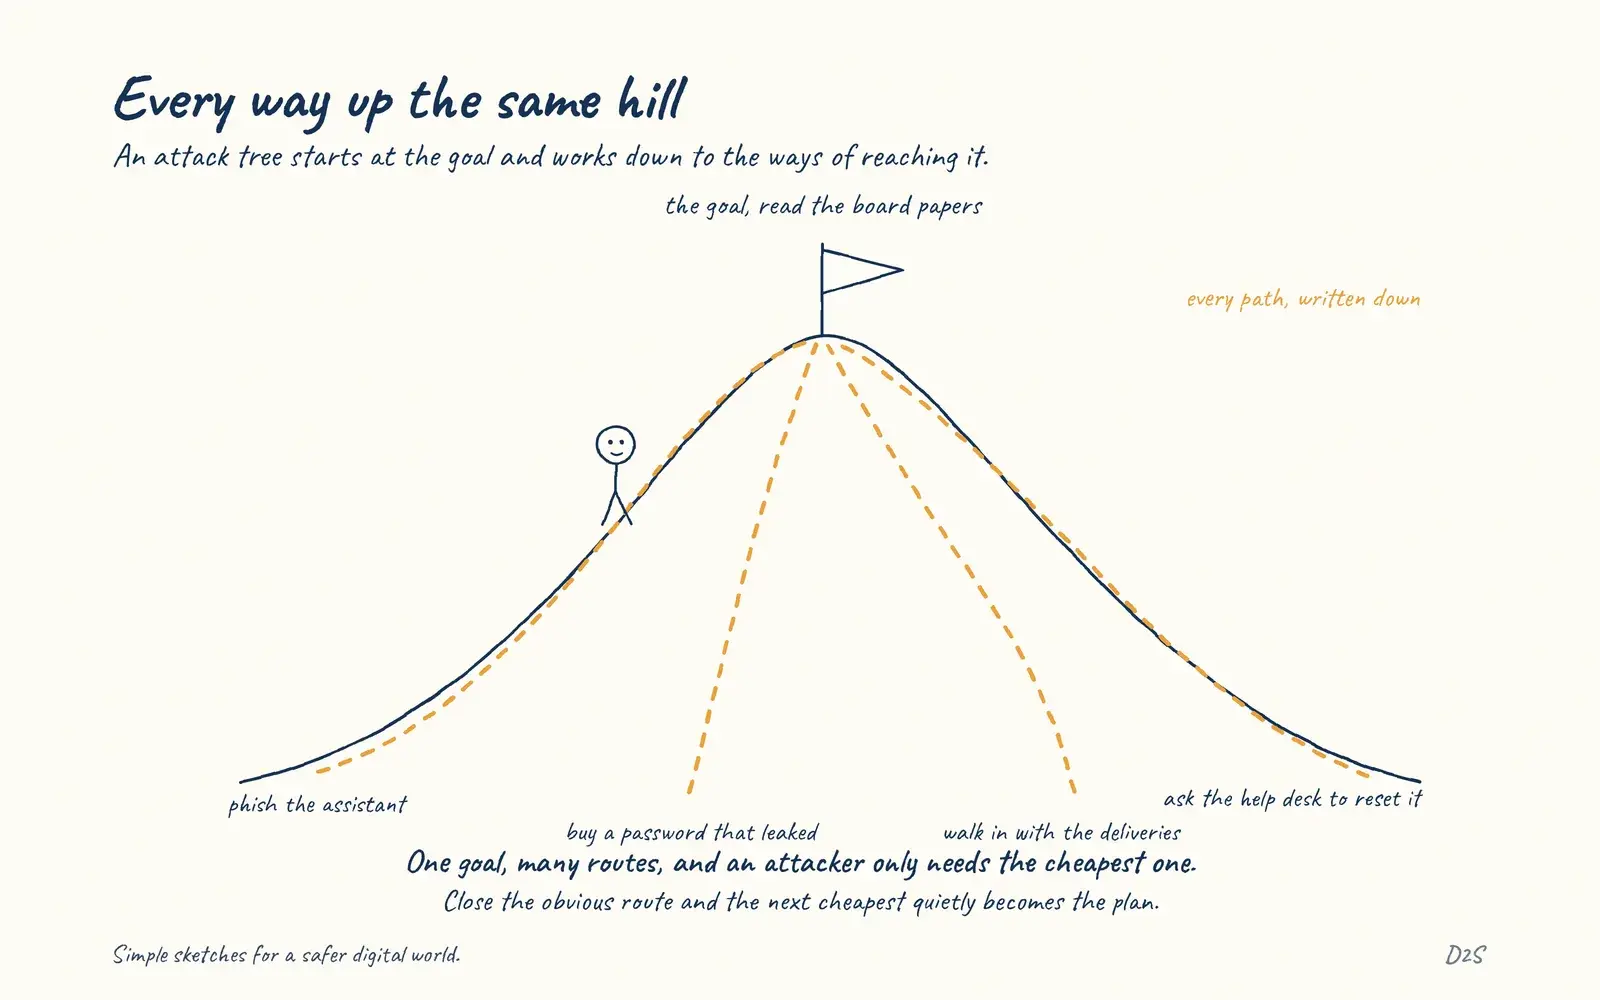 Attack trees decompose goals into possible pathsEvery way up the same hill
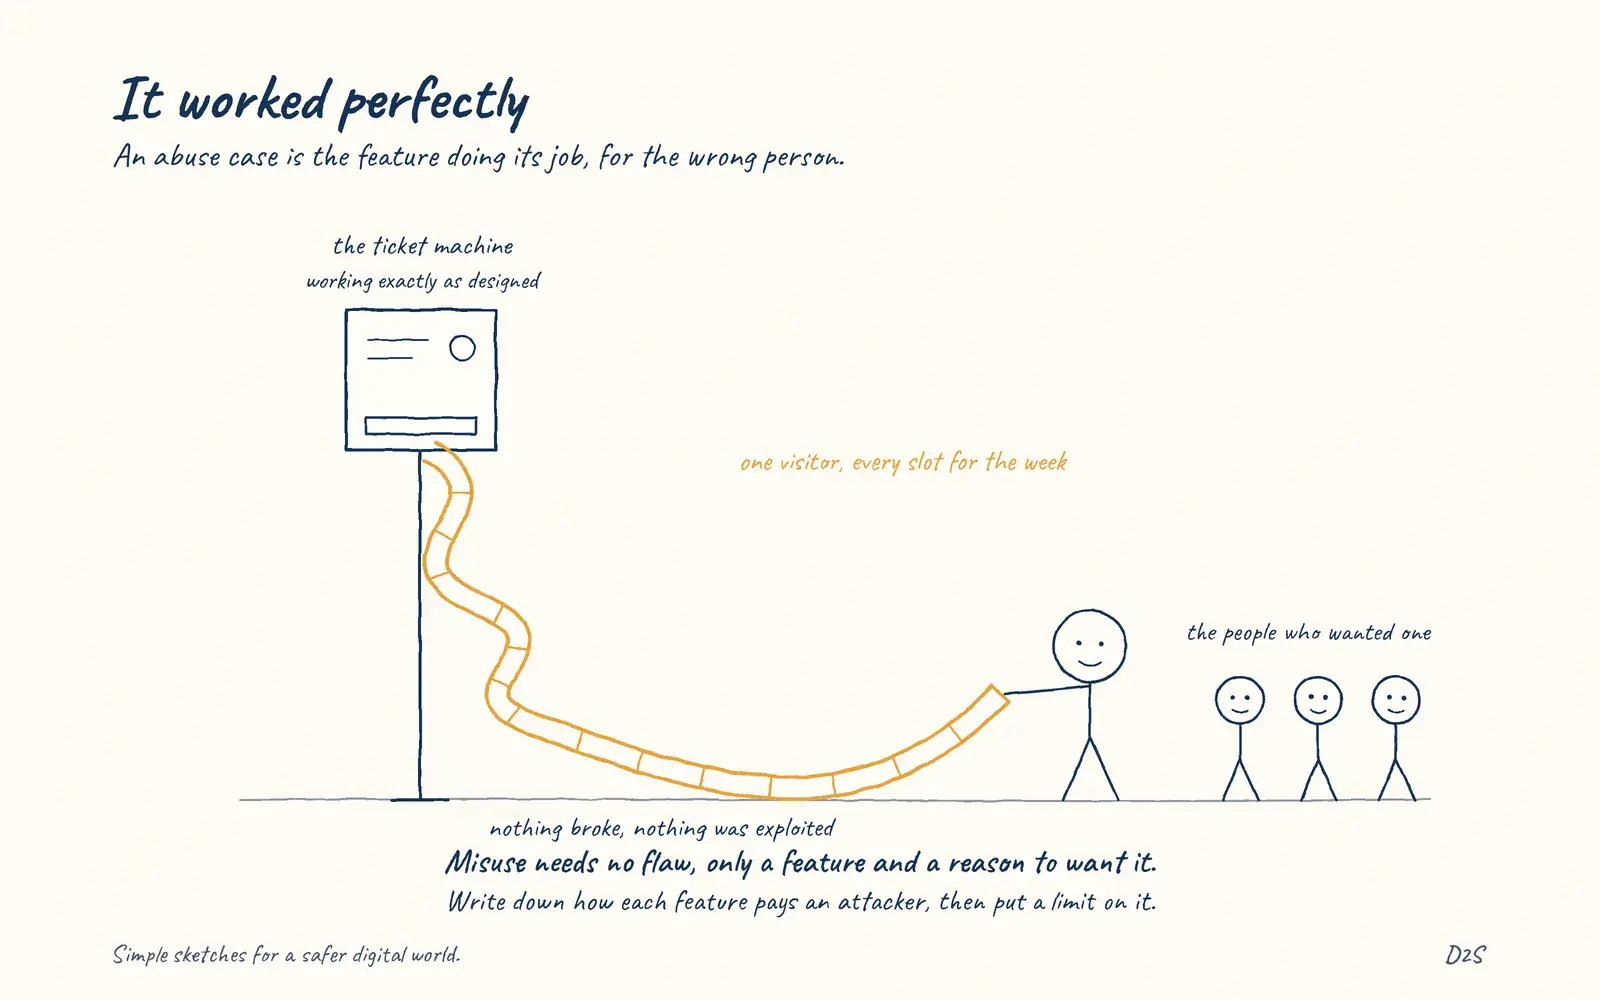 Abuse cases describe intentional misuseIt worked perfectly
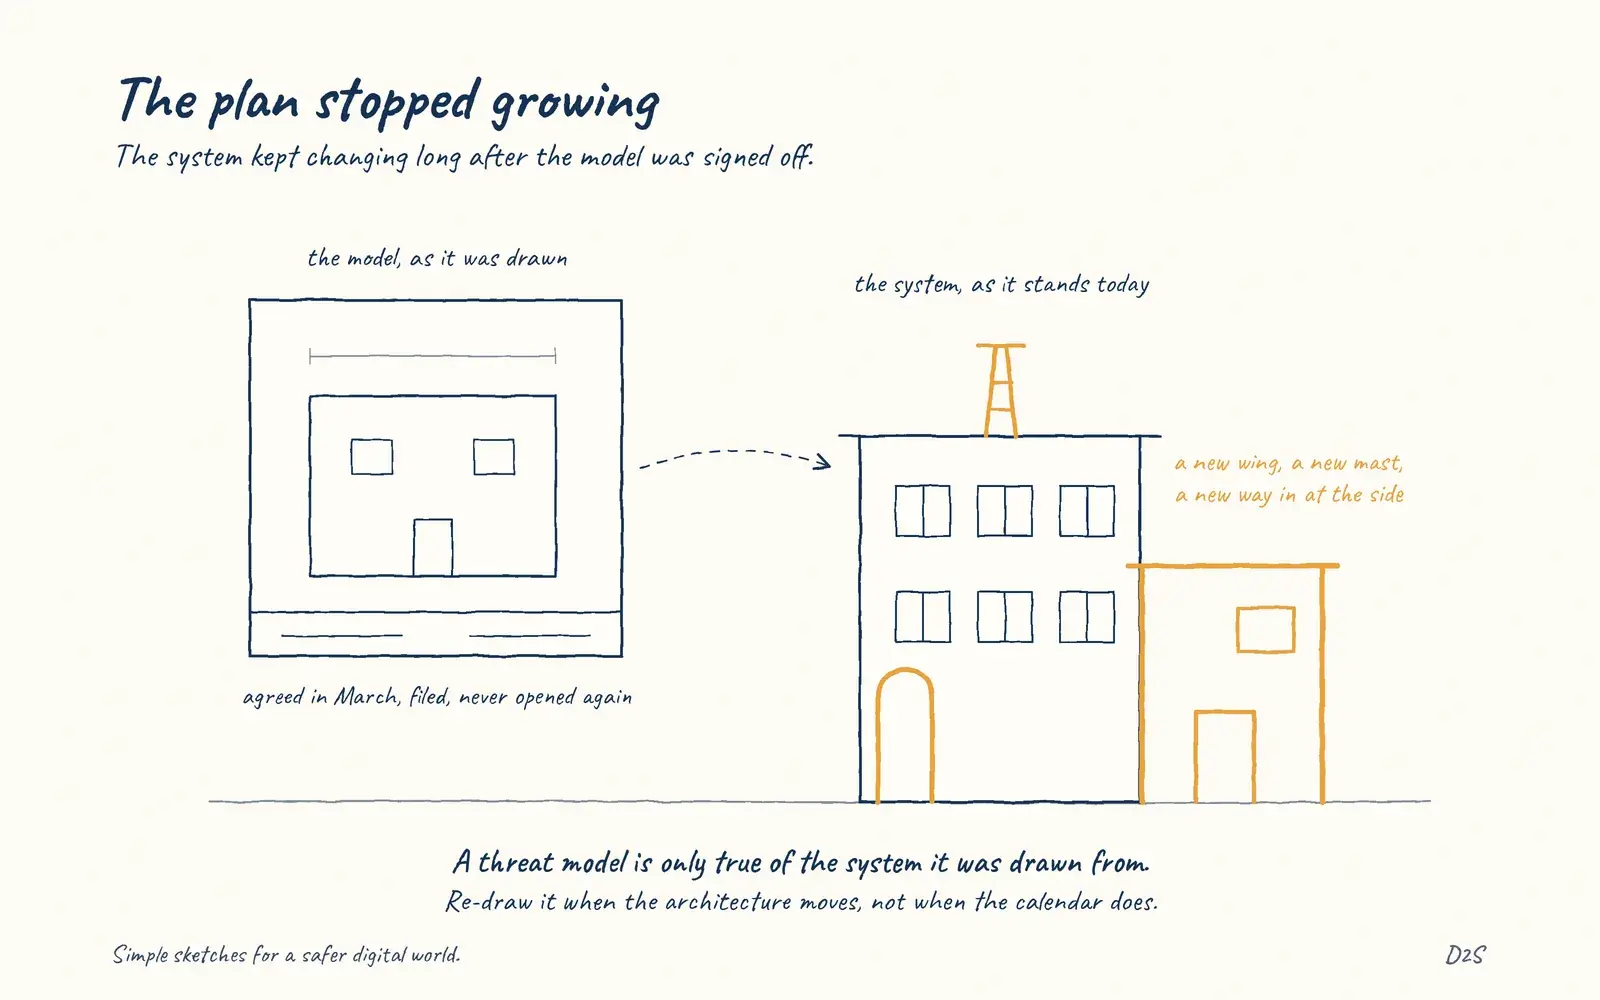 Threat models expire as systems changeThe plan stopped growing
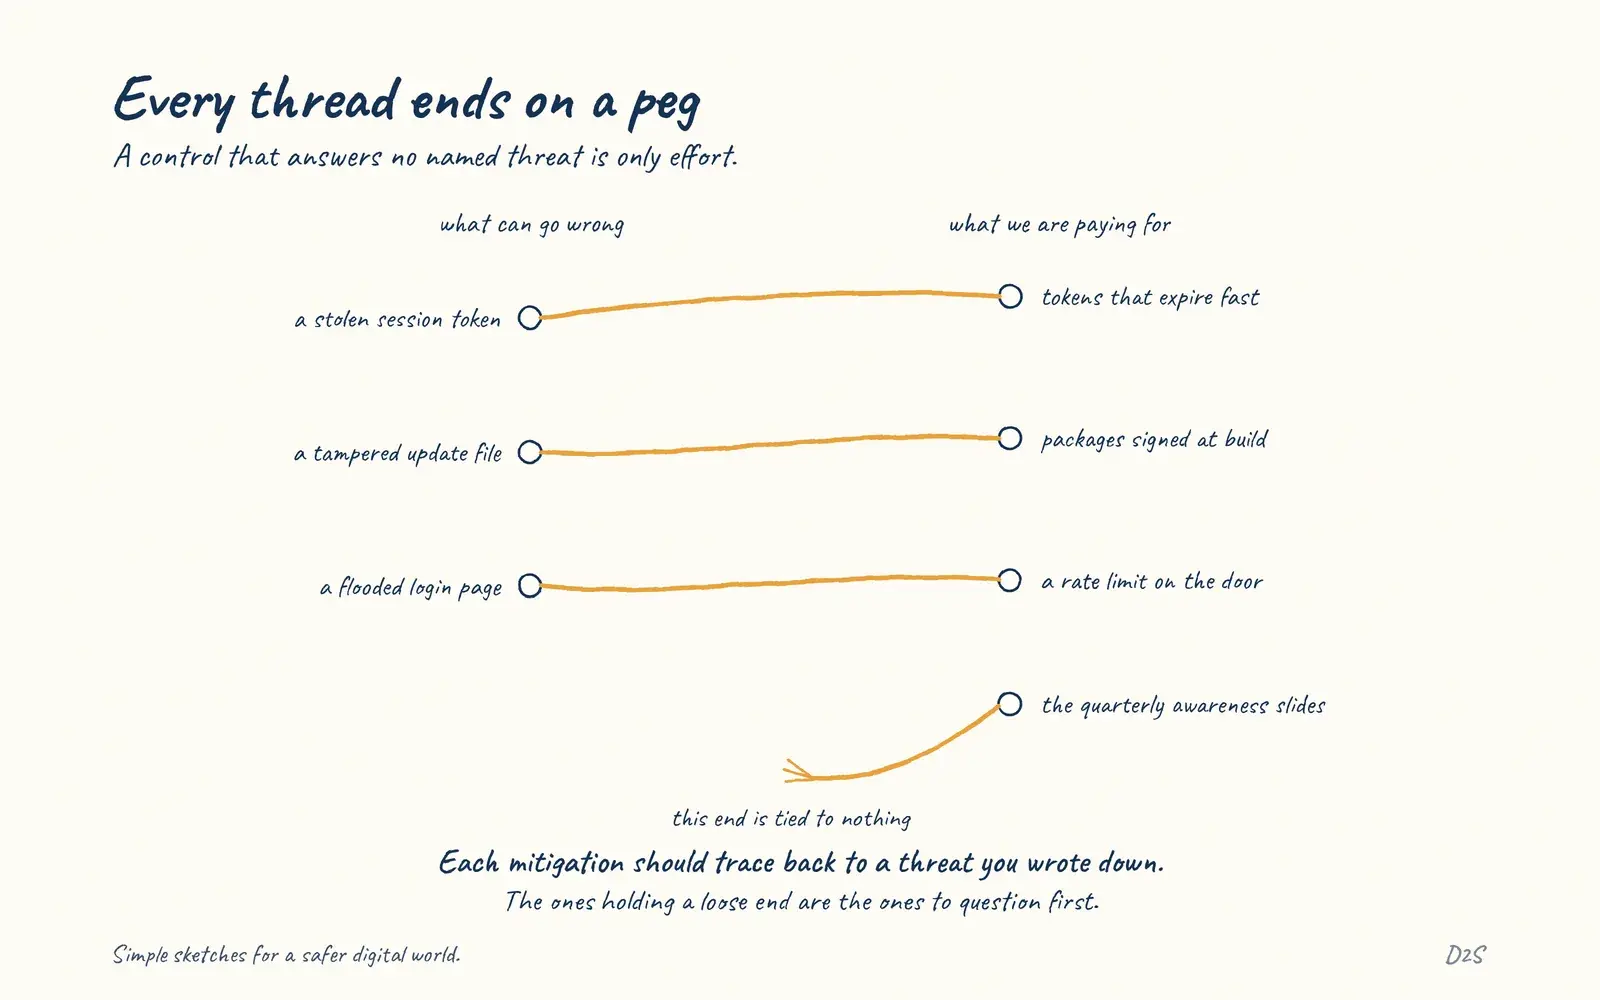 Mitigations should connect to specific threatsEvery thread ends on a peg
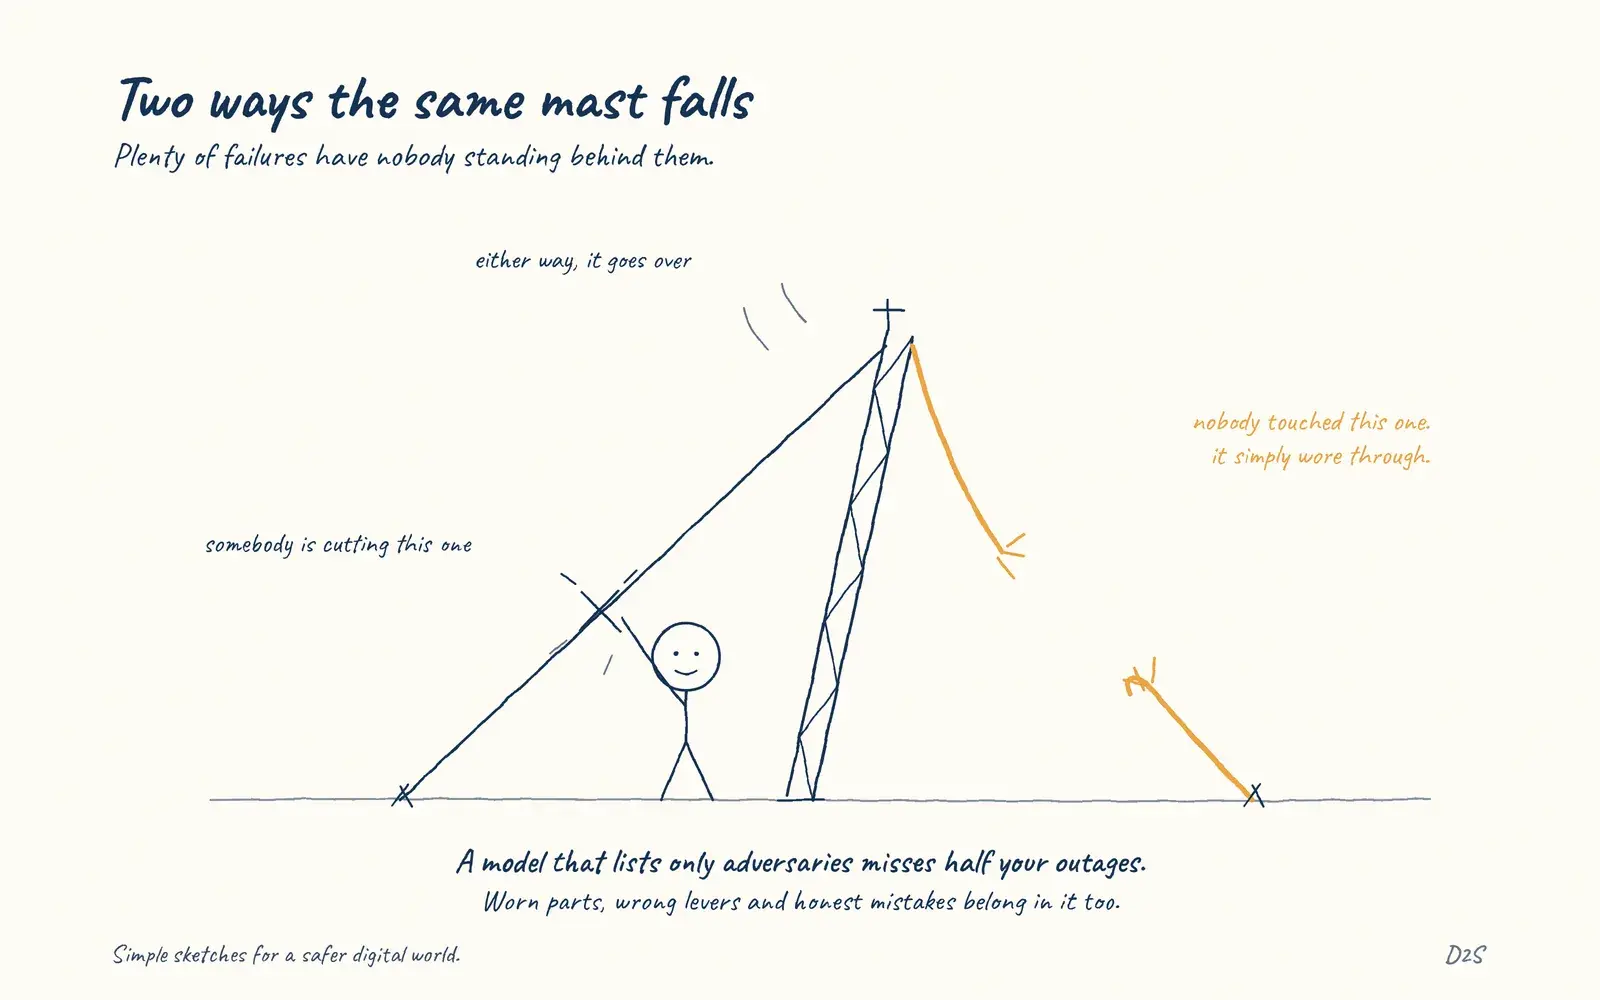 Threat models include failure without an attackerTwo ways the same mast falls
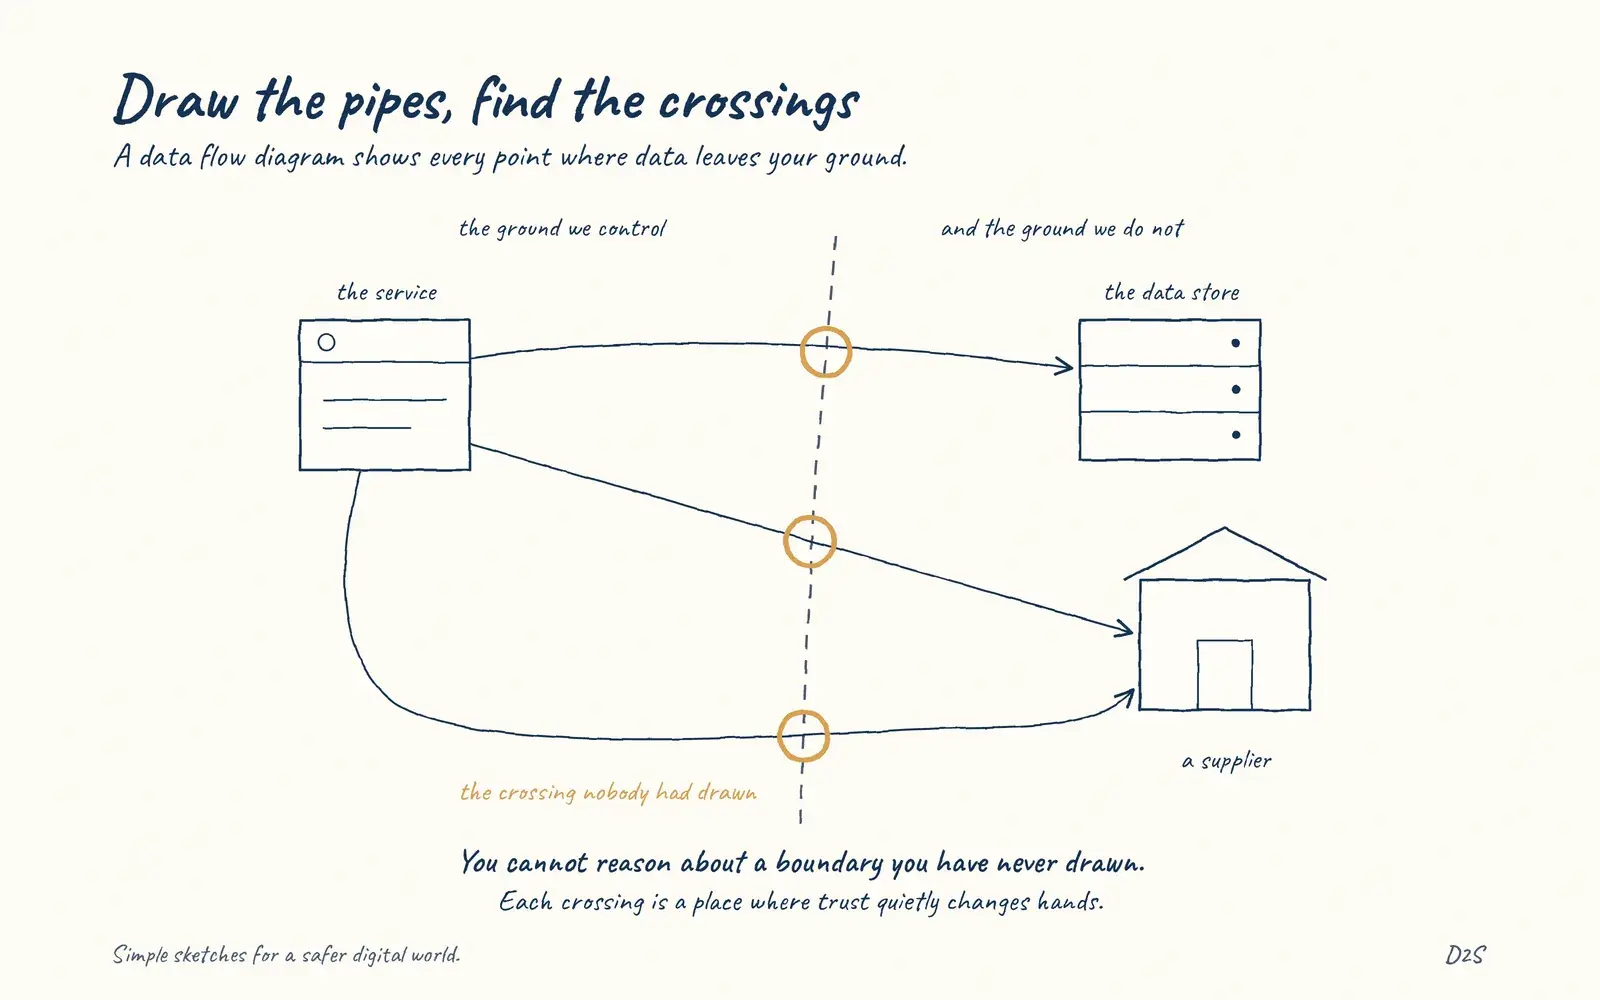 Data-flow diagrams reveal hidden crossingsDraw the pipes, find the crossings
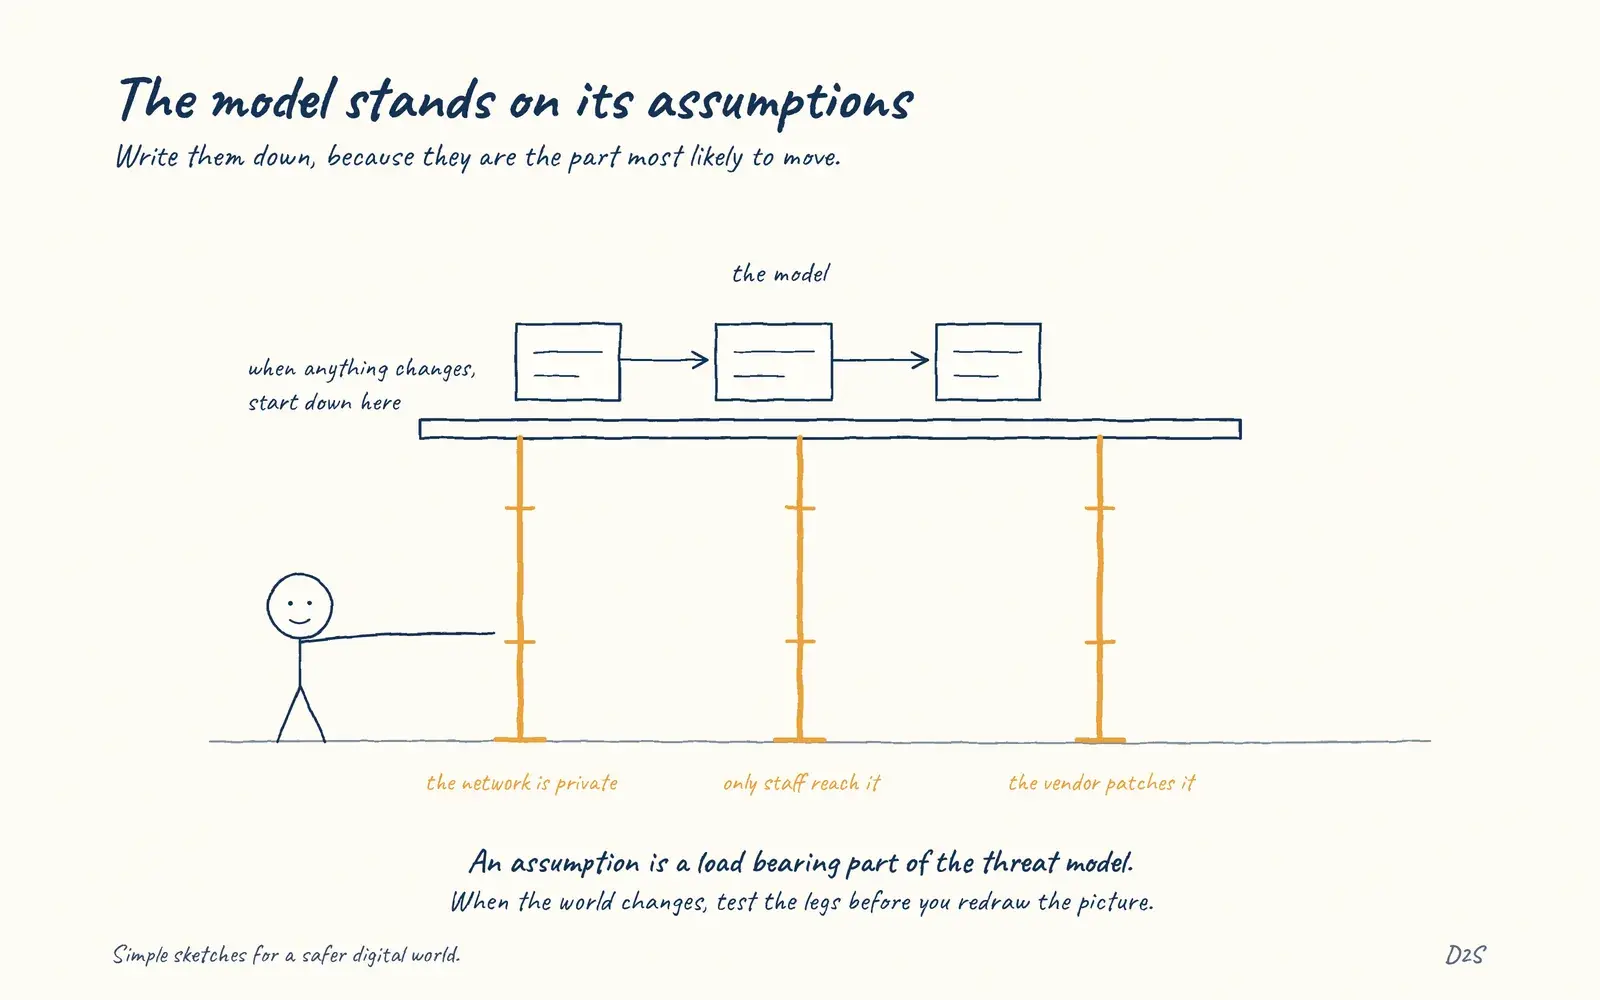 Assumptions are part of the threat modelThe model stands on its assumptions
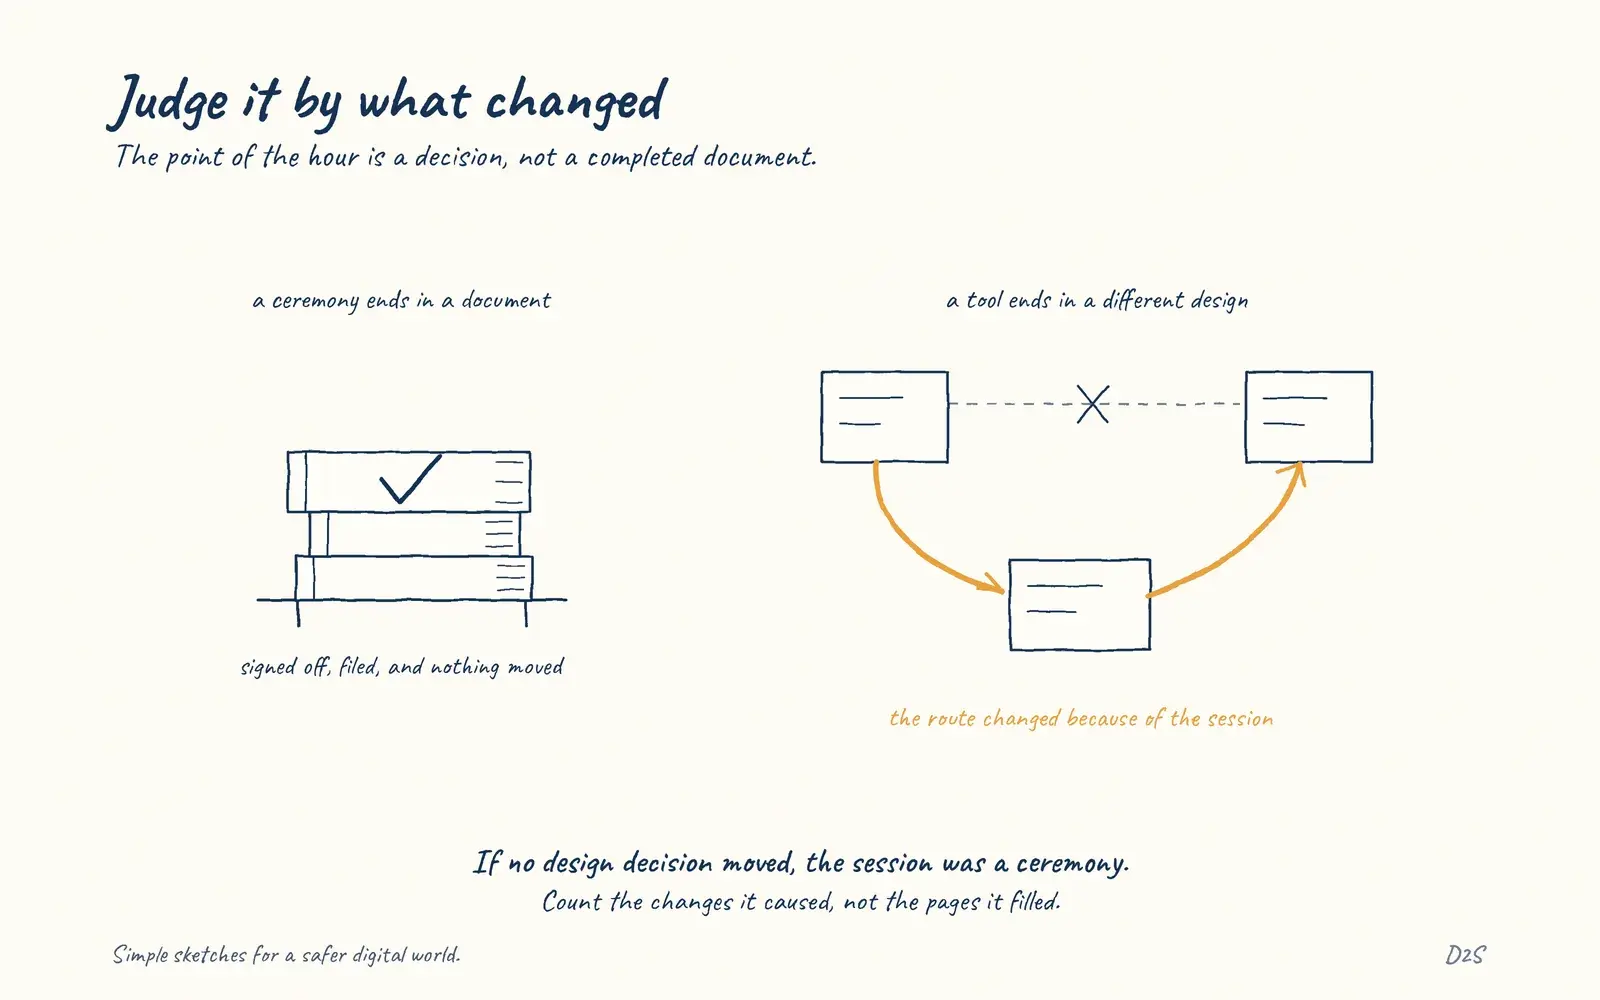 Threat modelling is a decision tool, not a ceremonyJudge it by what changed