
Supply chain & third parties
The risk you inherit from people you do not employ.
21 sketches
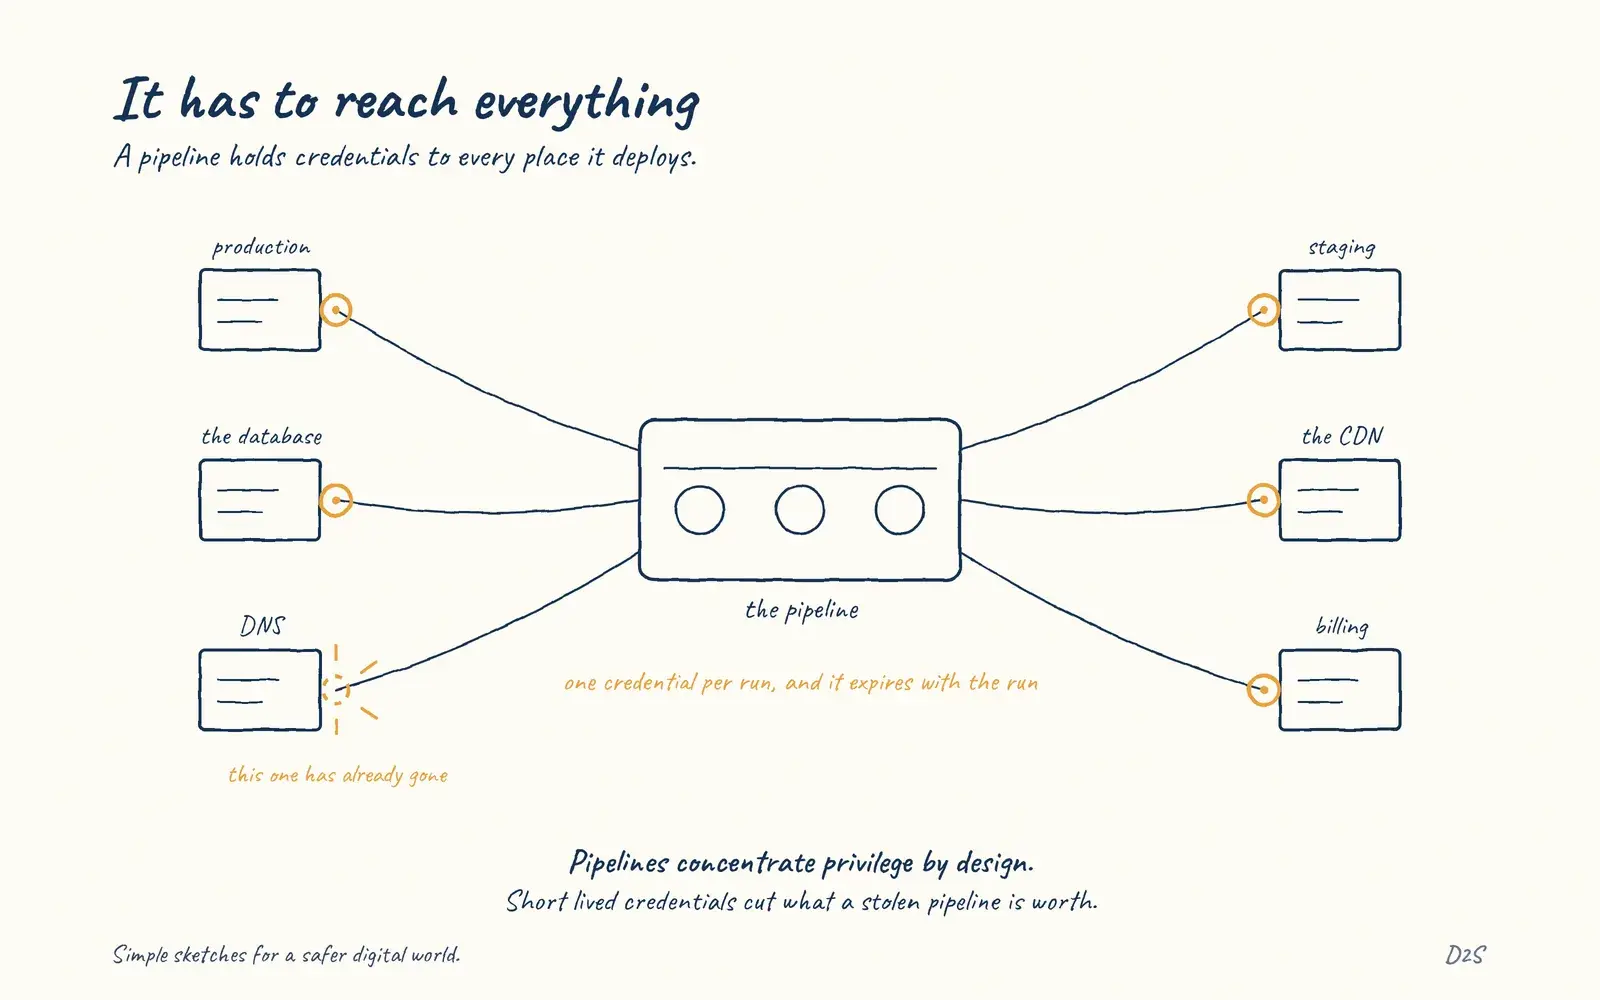 CI/CD secretsIt has to reach everything
 SBOMsThe list, and the verdict
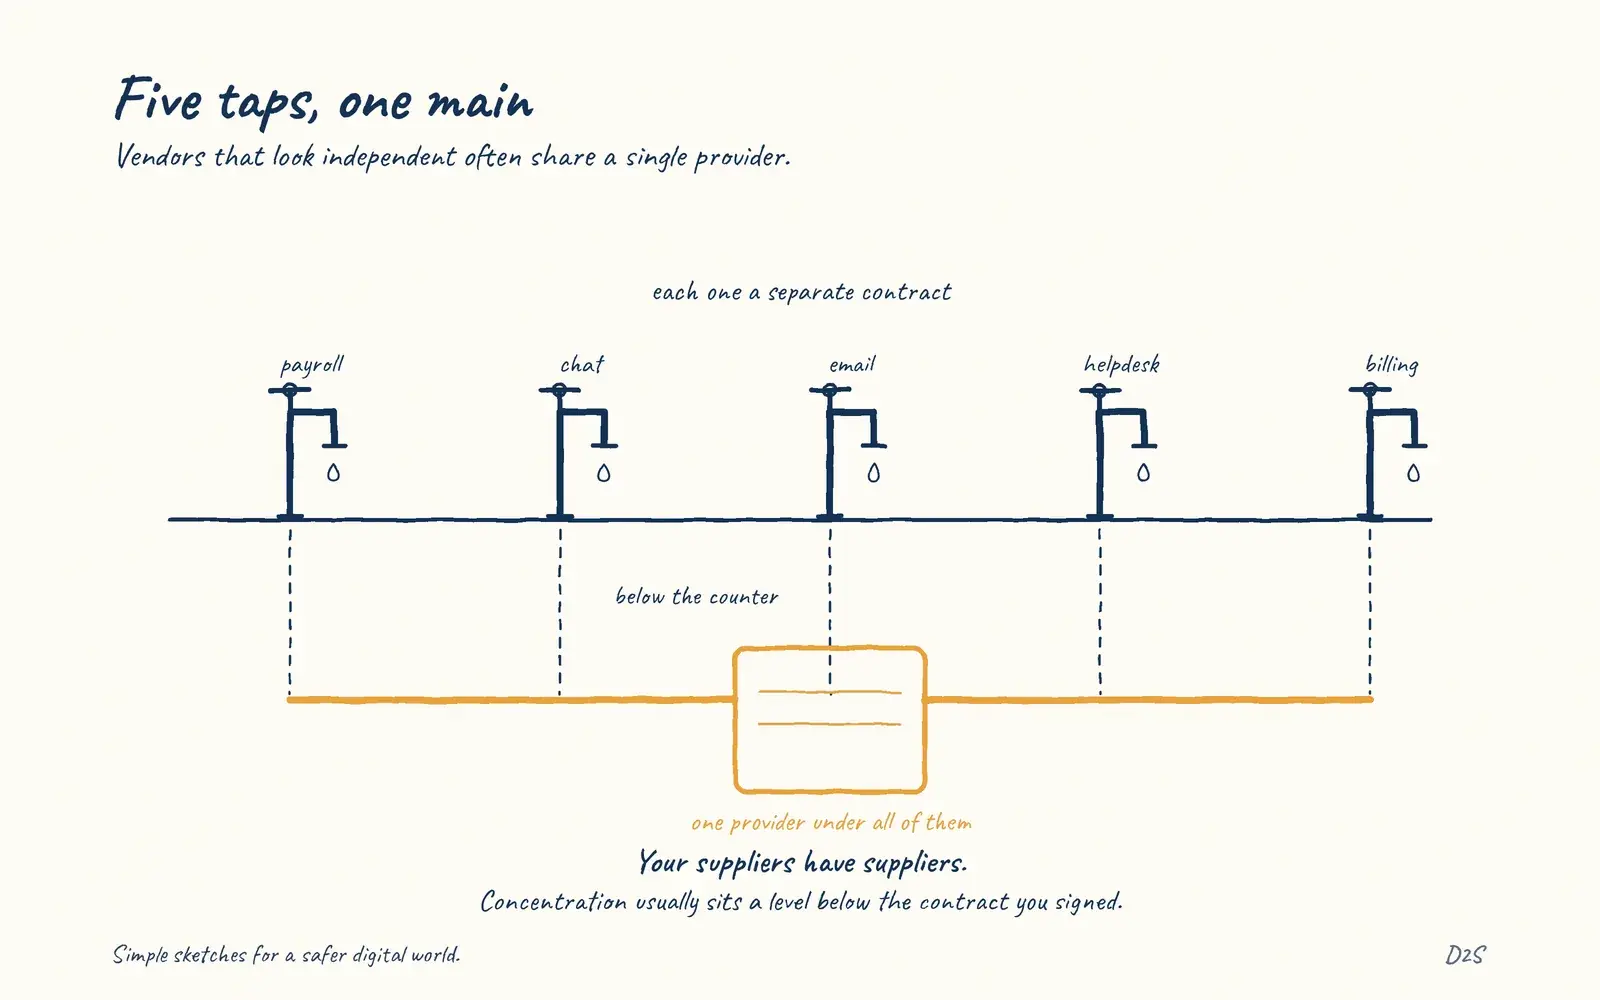 Fourth-party riskFive taps, one main
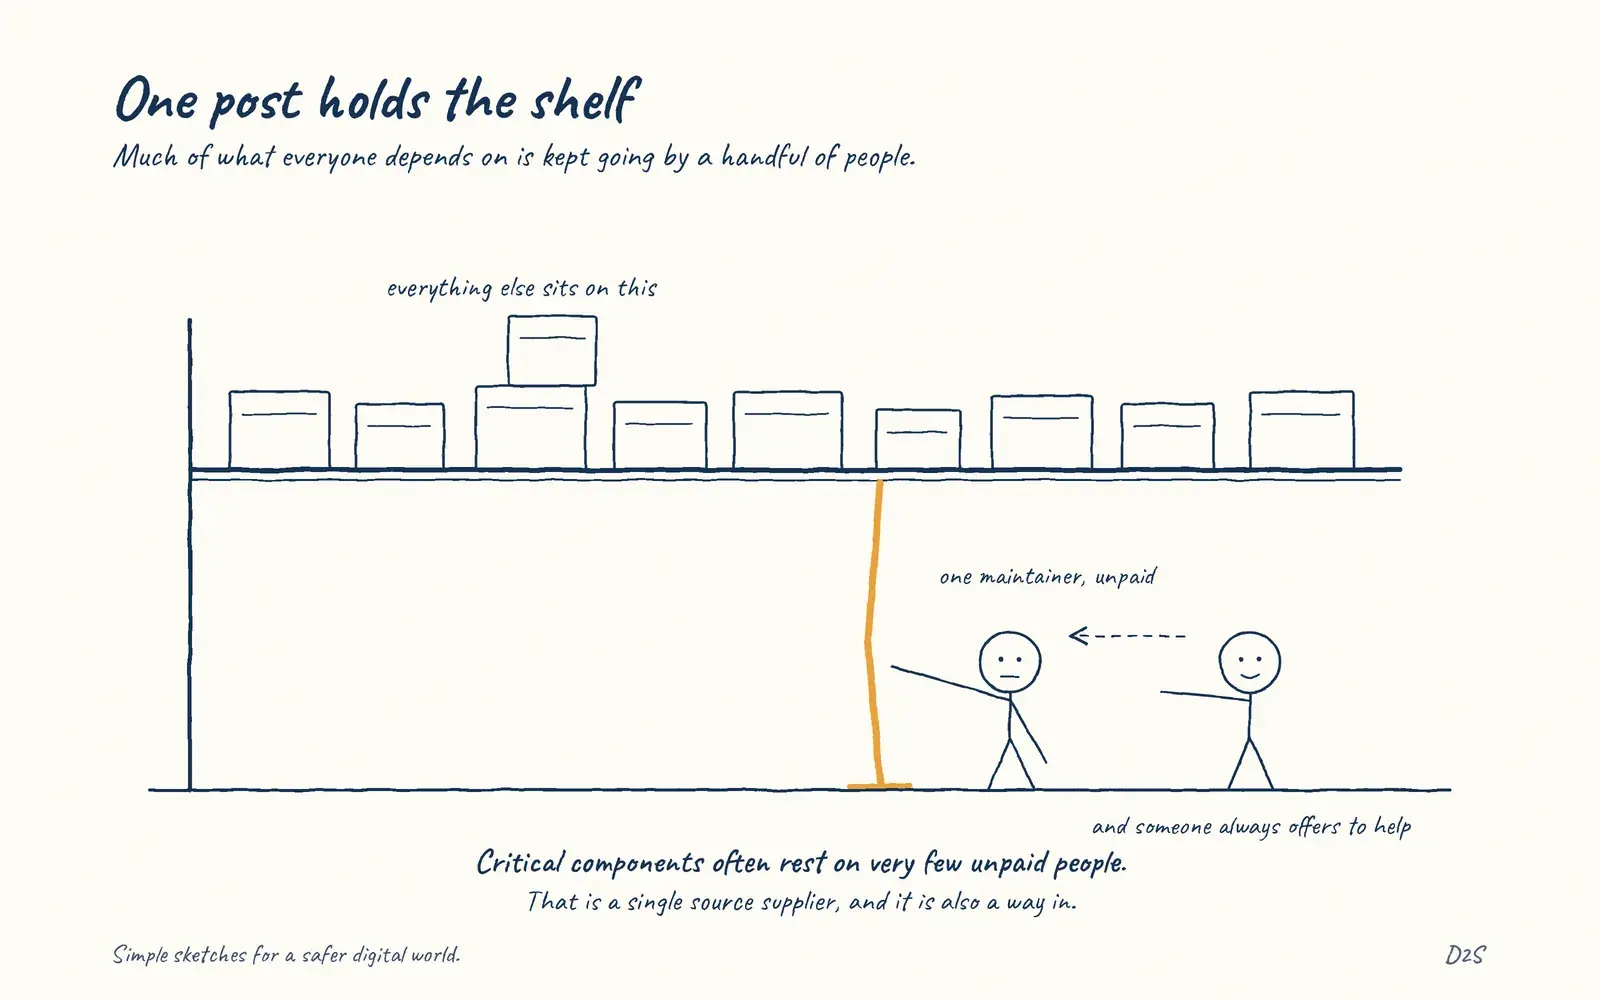 Maintainer burnoutOne post holds the shelf
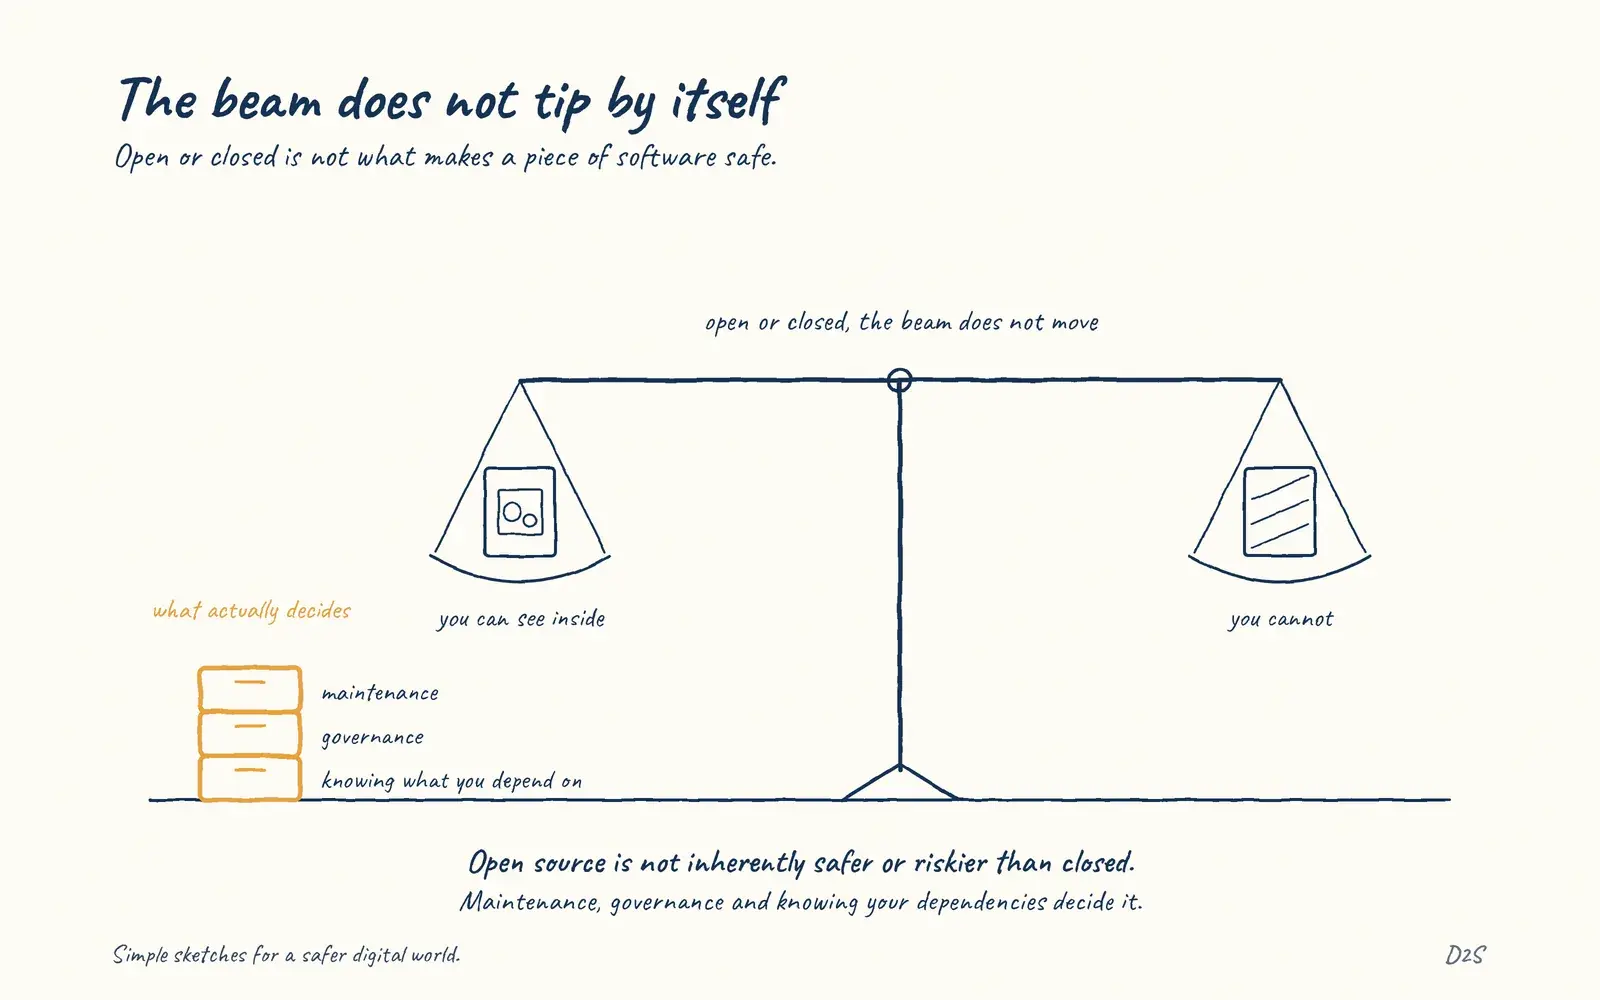 Open-source riskThe beam does not tip by itself
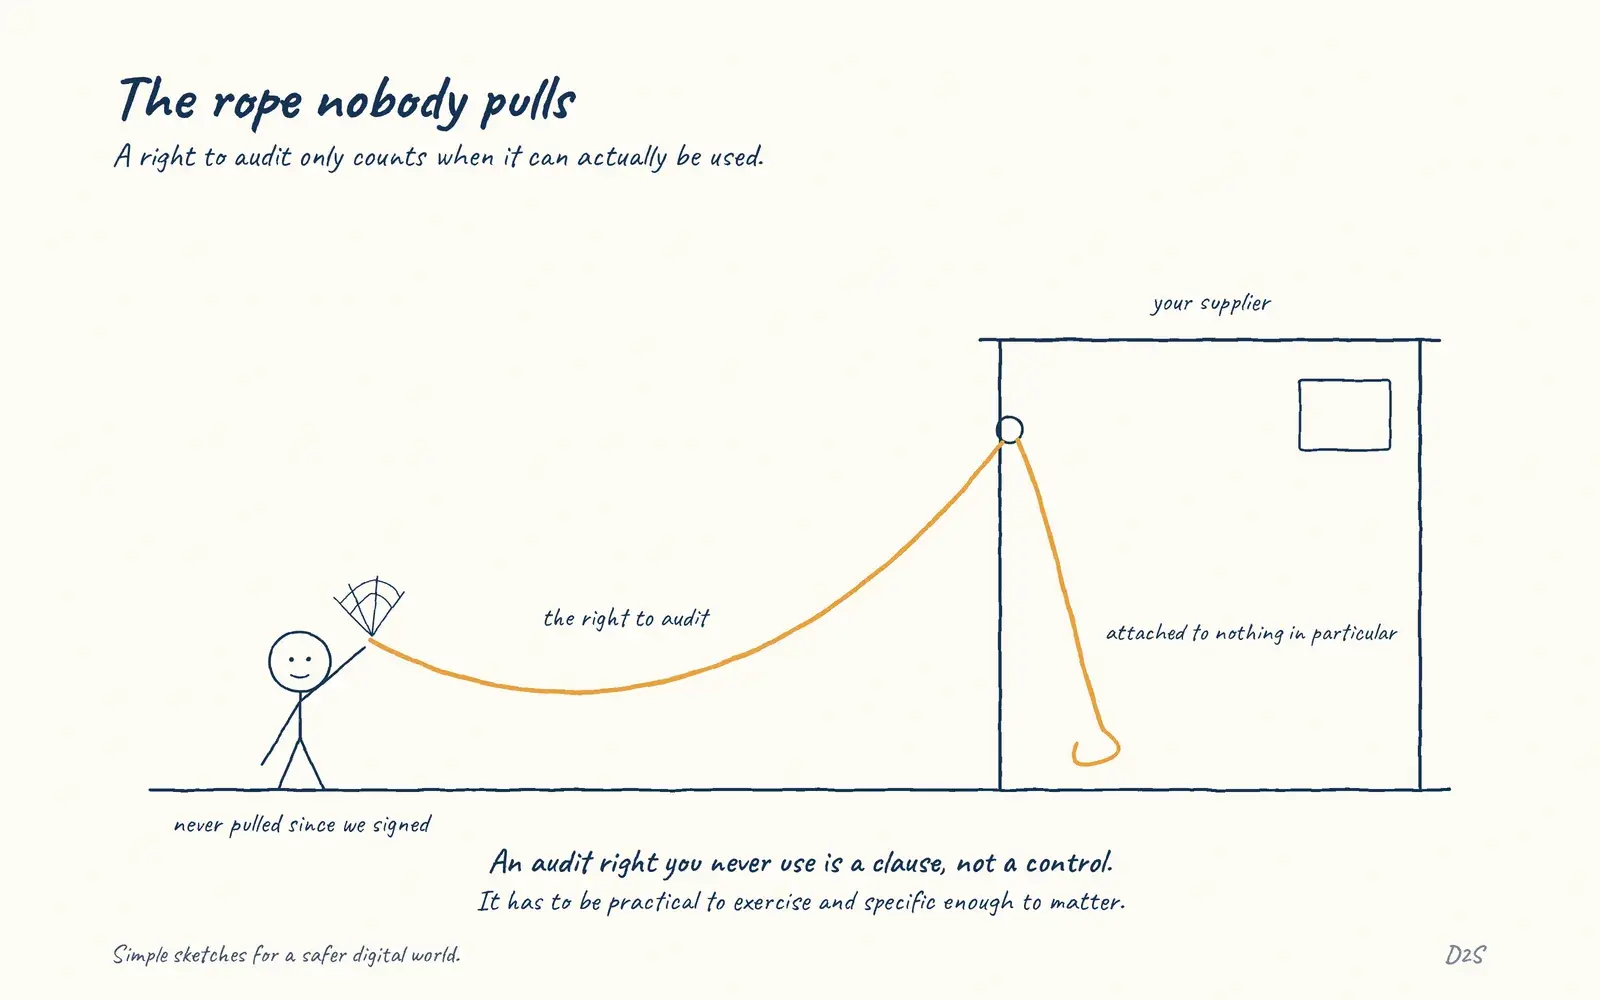 Right to auditThe rope nobody pulls
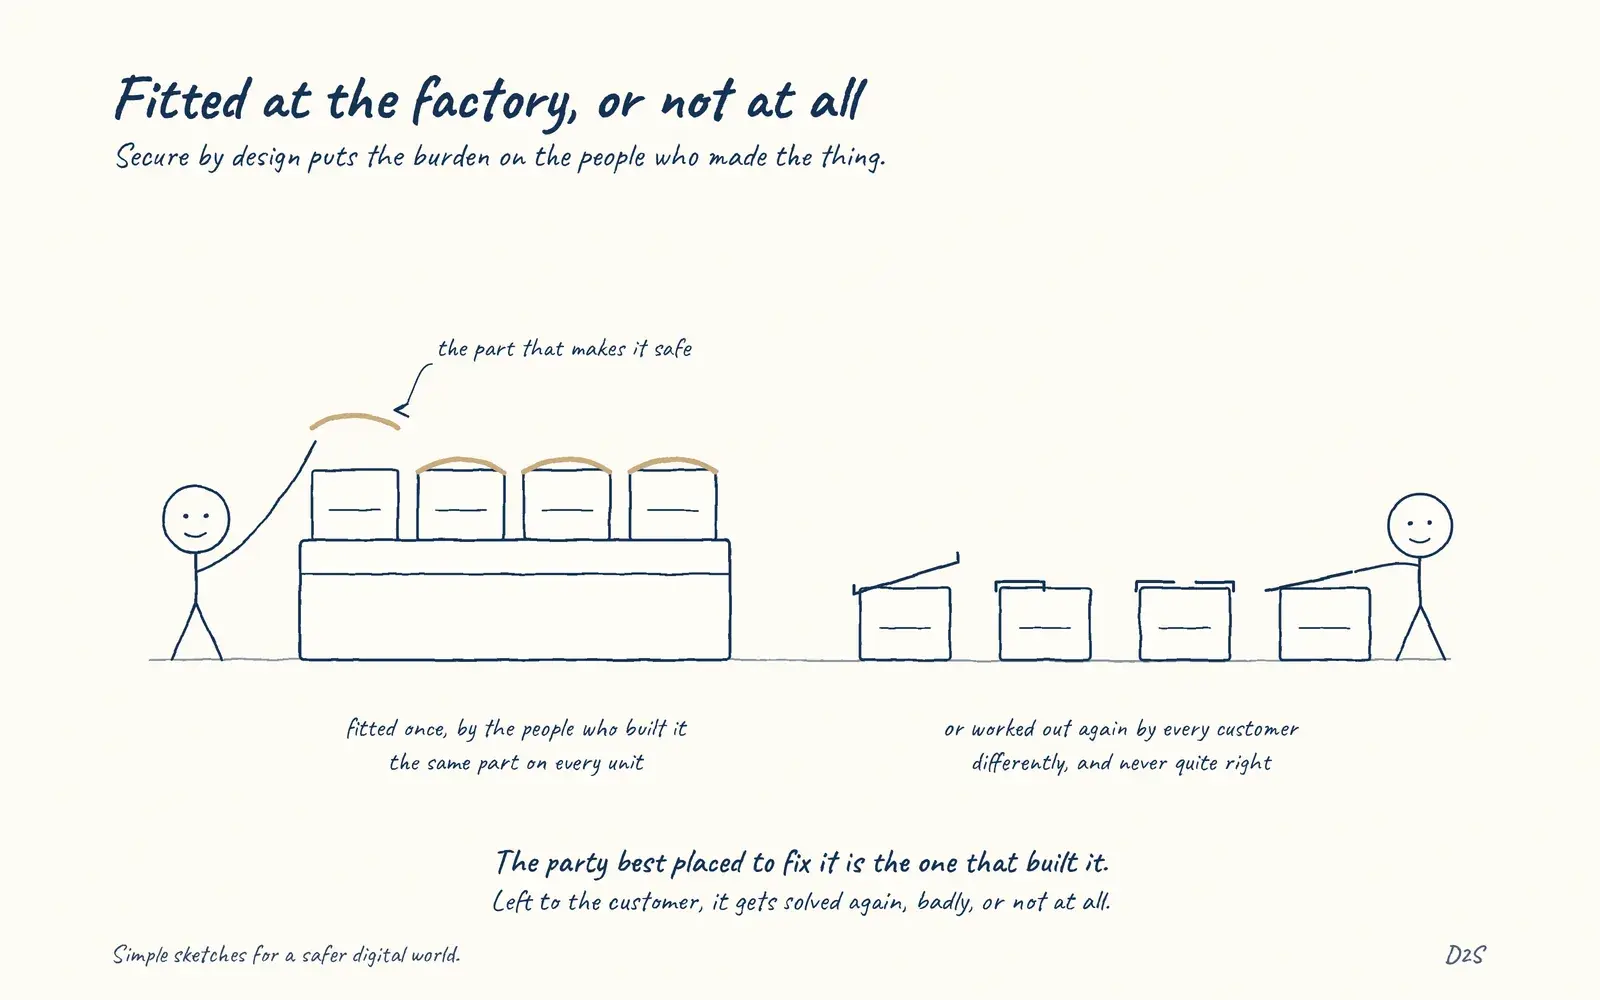 Secure by designFitted at the factory, or not at all
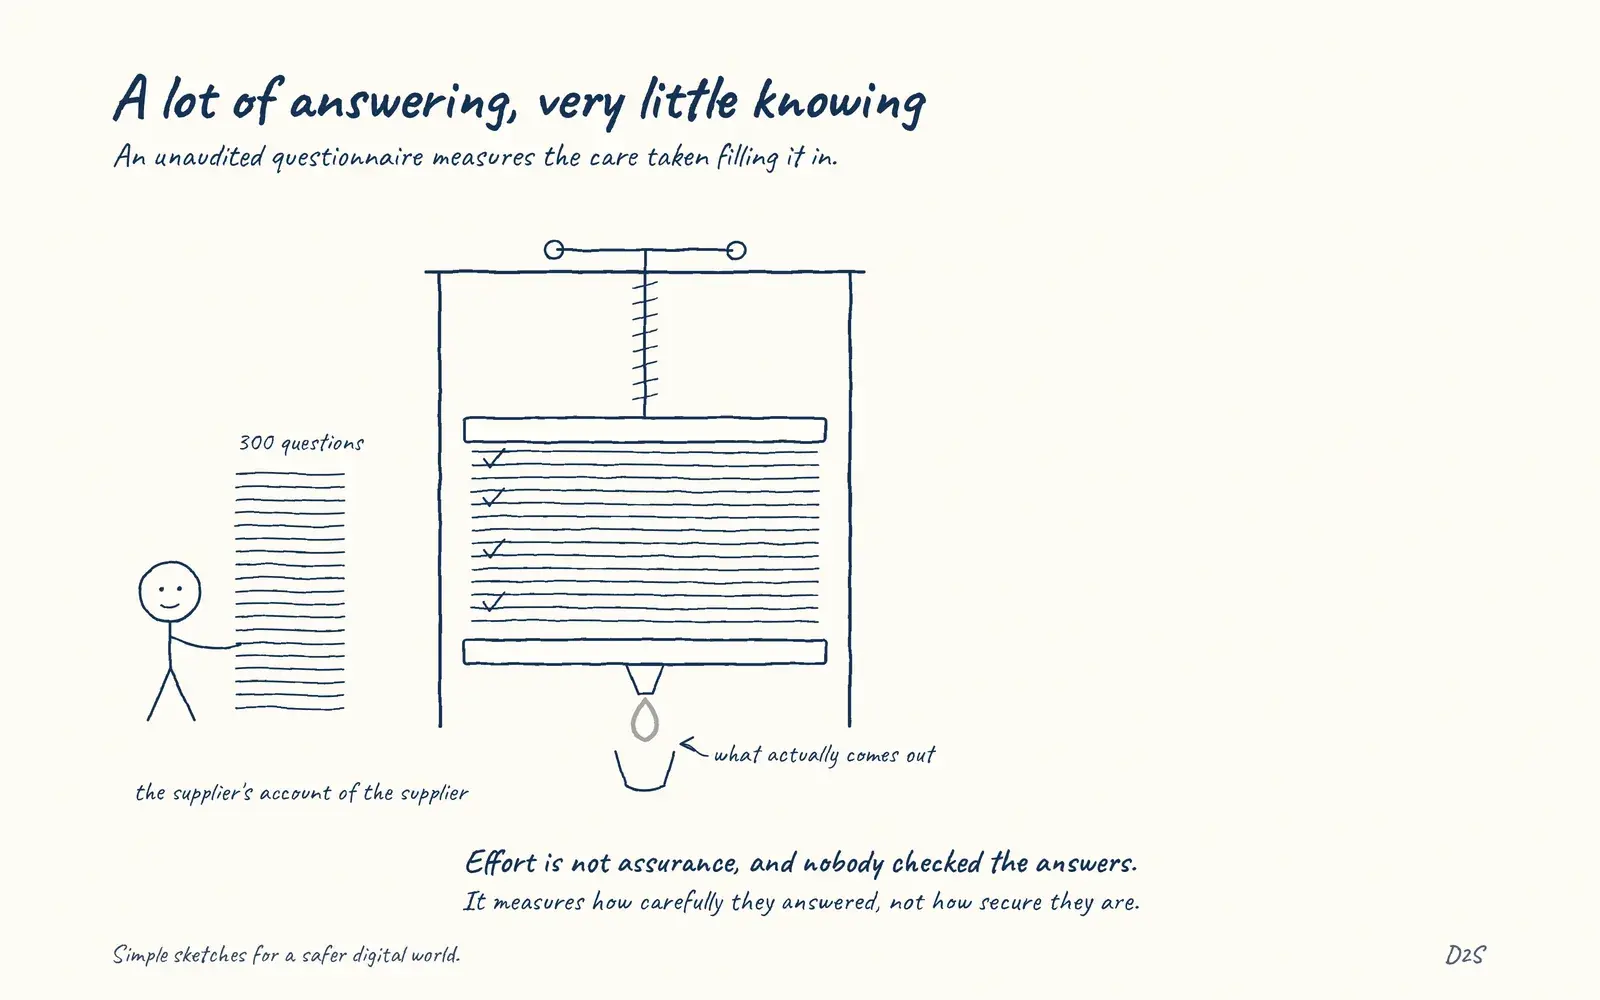 Security questionnairesA lot of answering, very little knowing
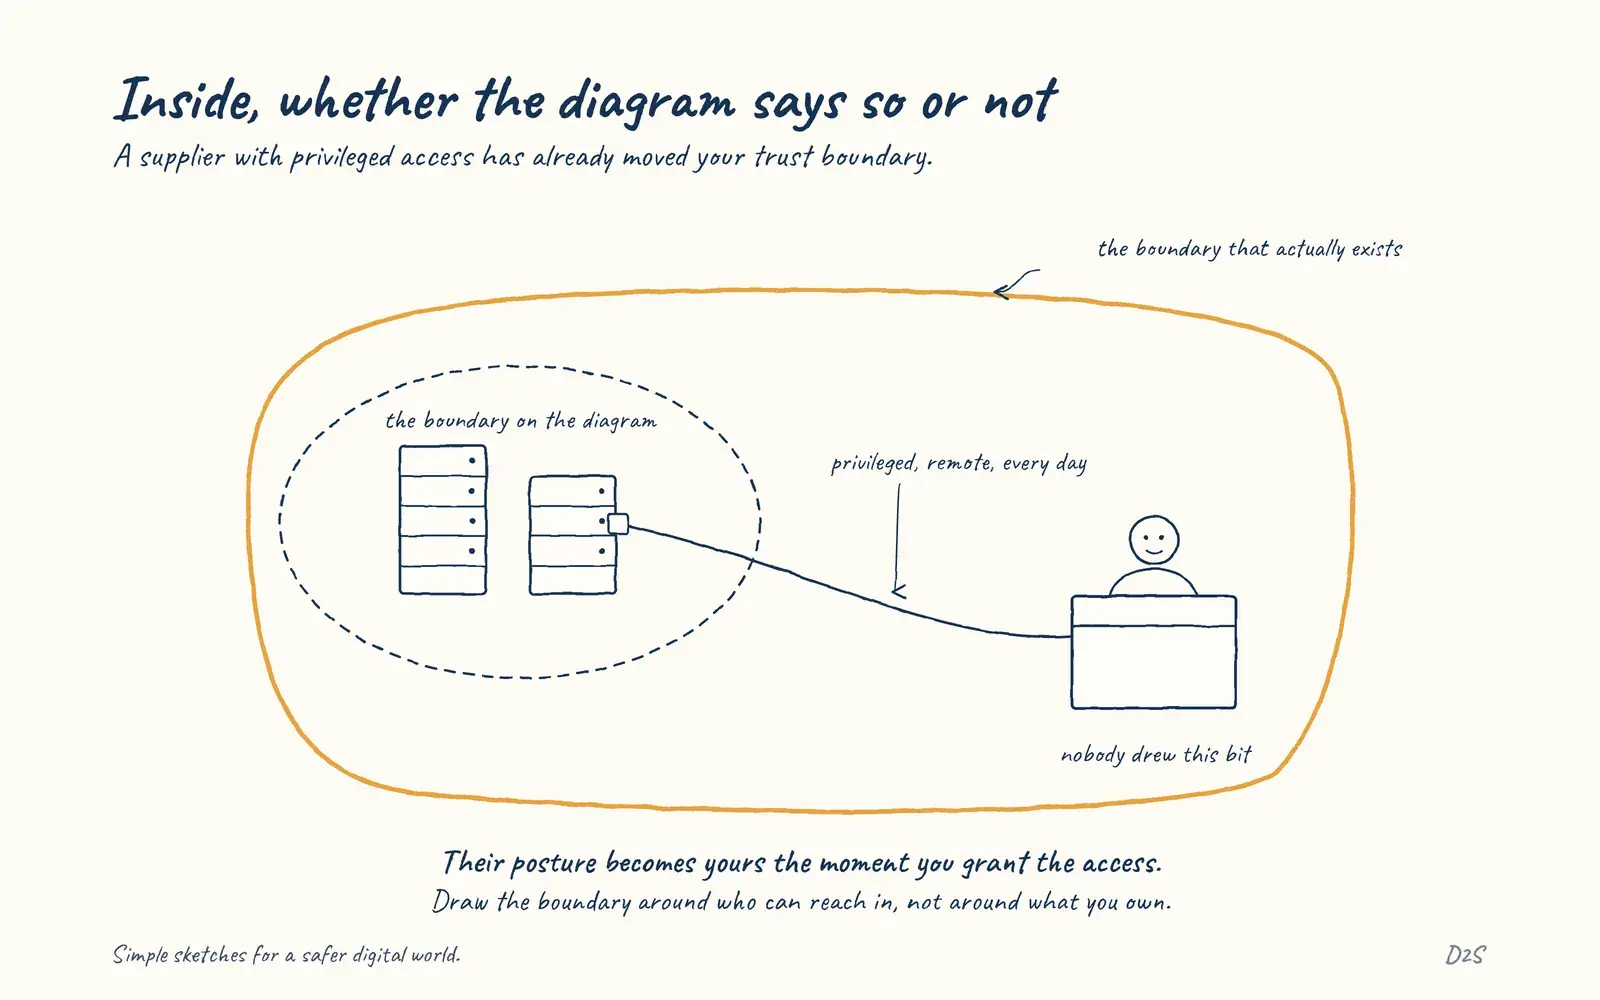 Supplier accessInside, whether the diagram says so or not
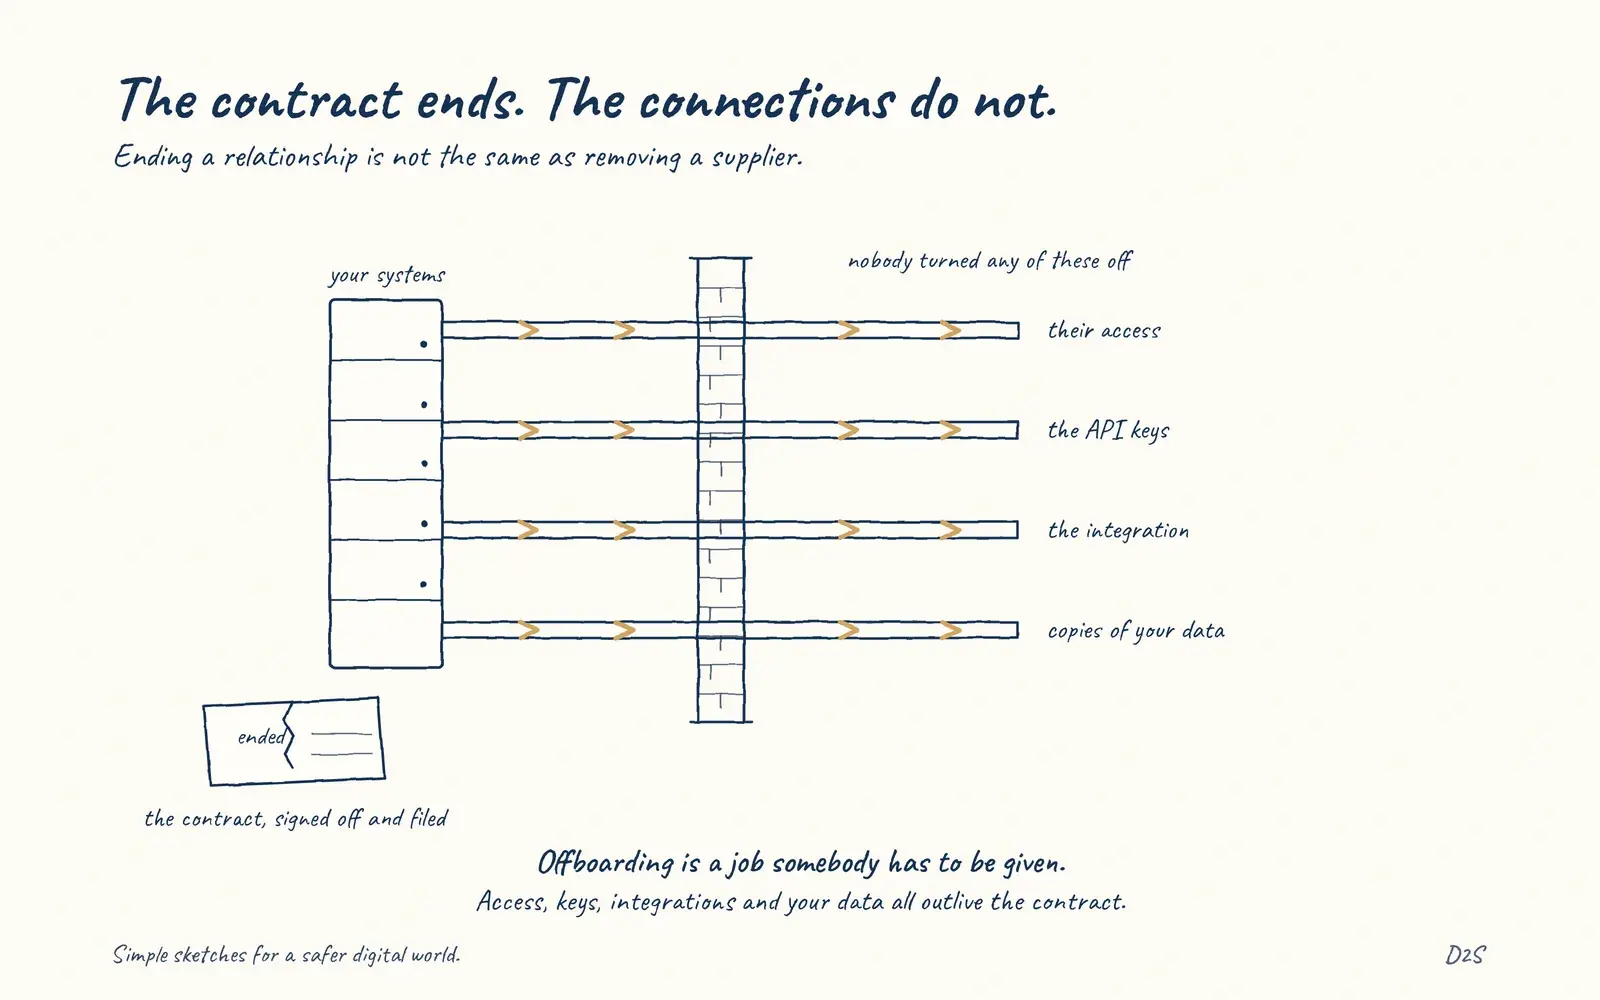 Supplier offboardingThe contract ends. The connections do not
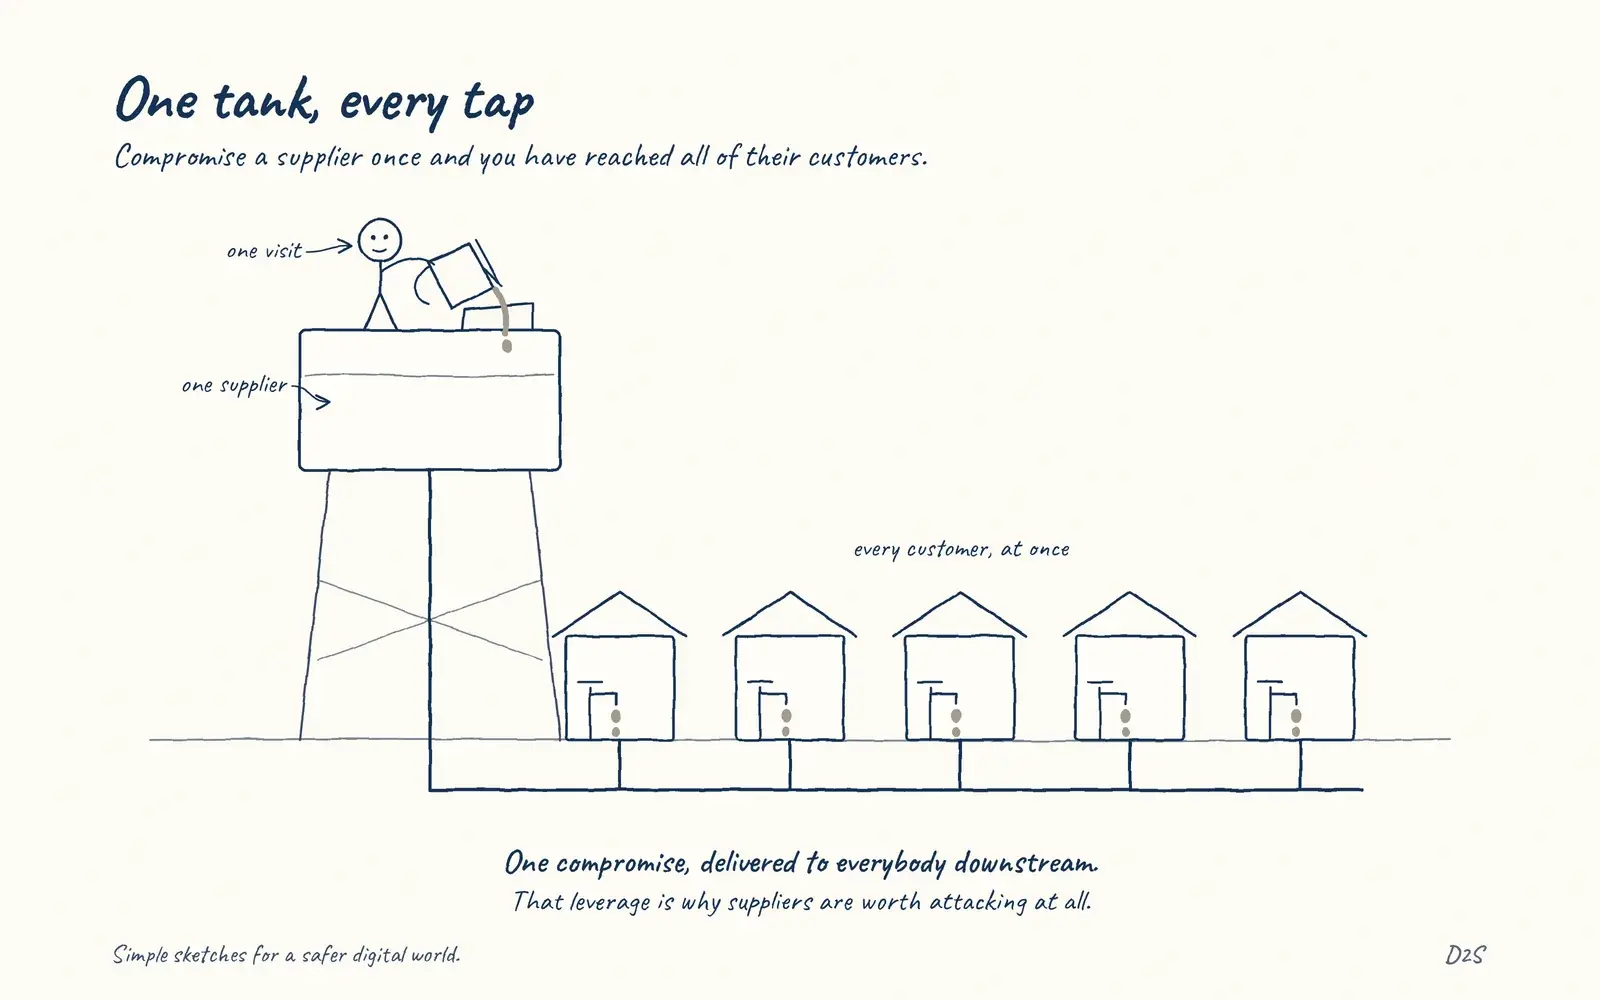 Supply-chain attacksOne tank, every tap
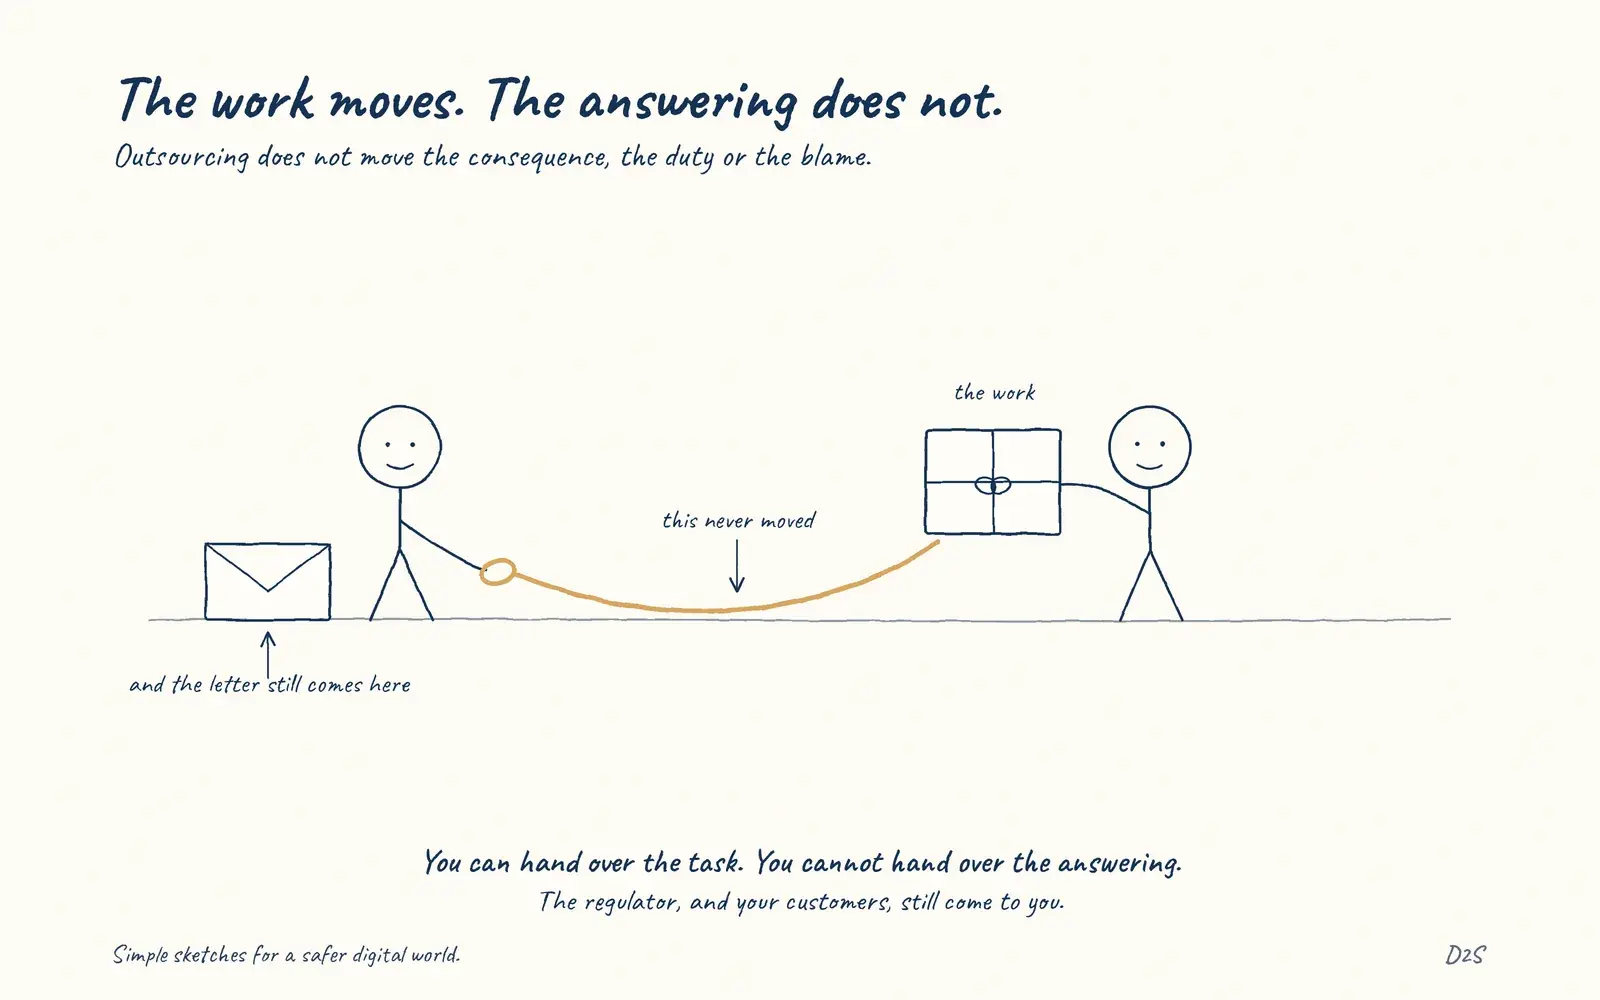 Third-party riskThe work moves. The answering does not
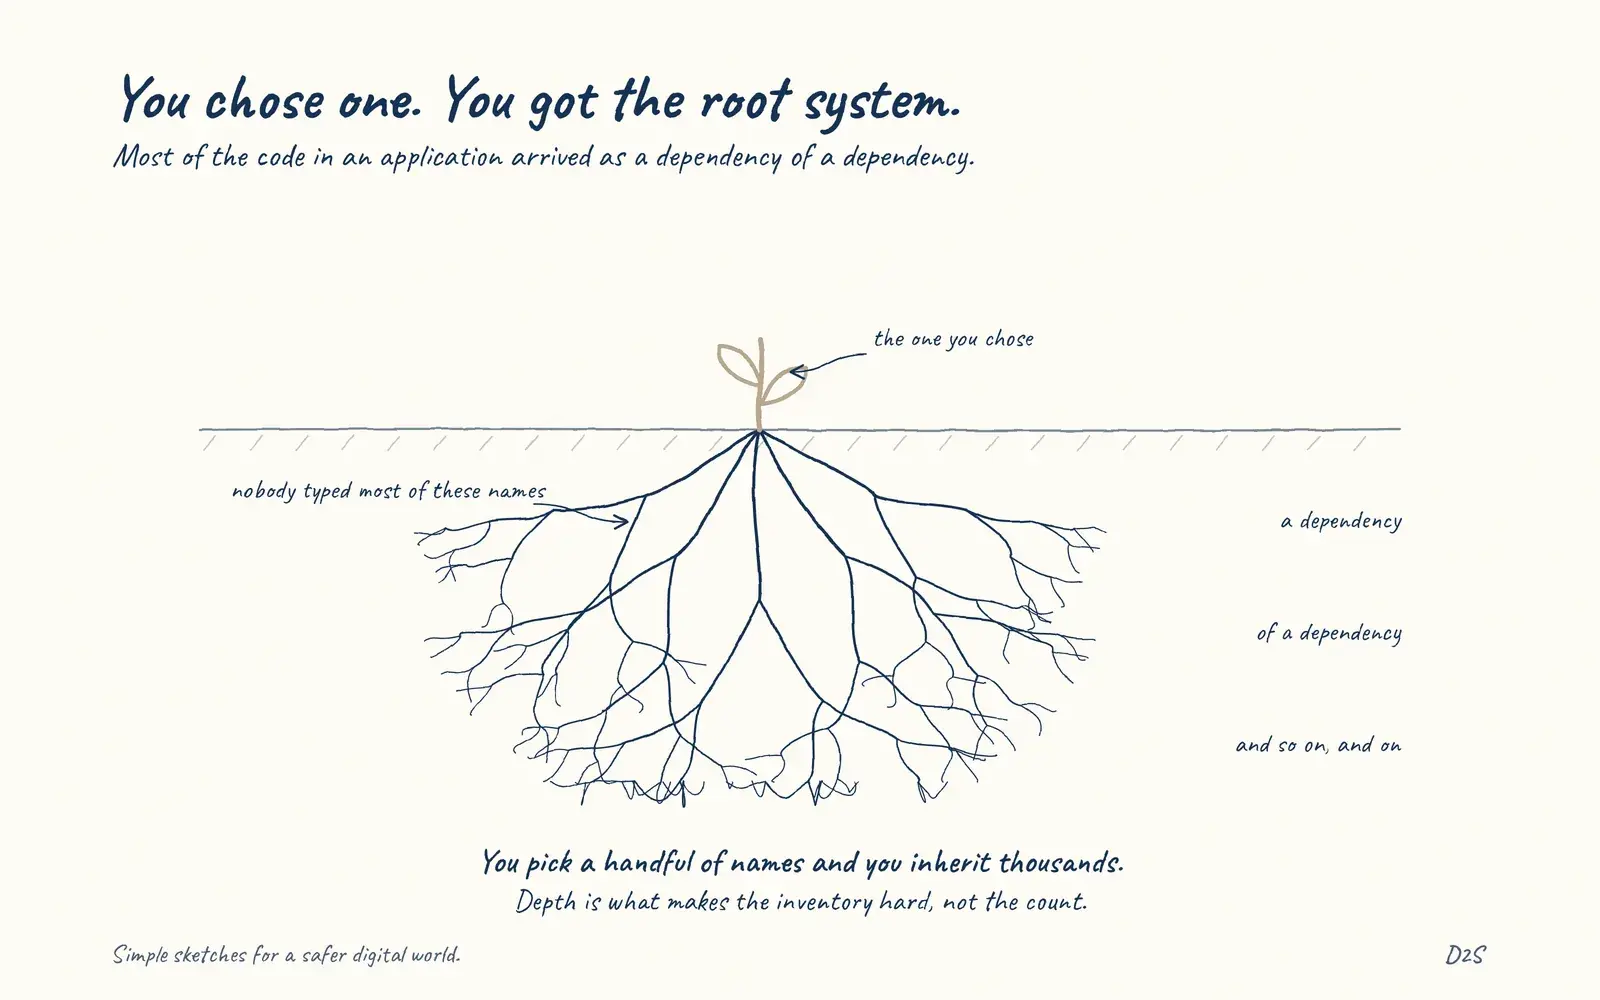 Transitive dependenciesYou chose one. You got the root system
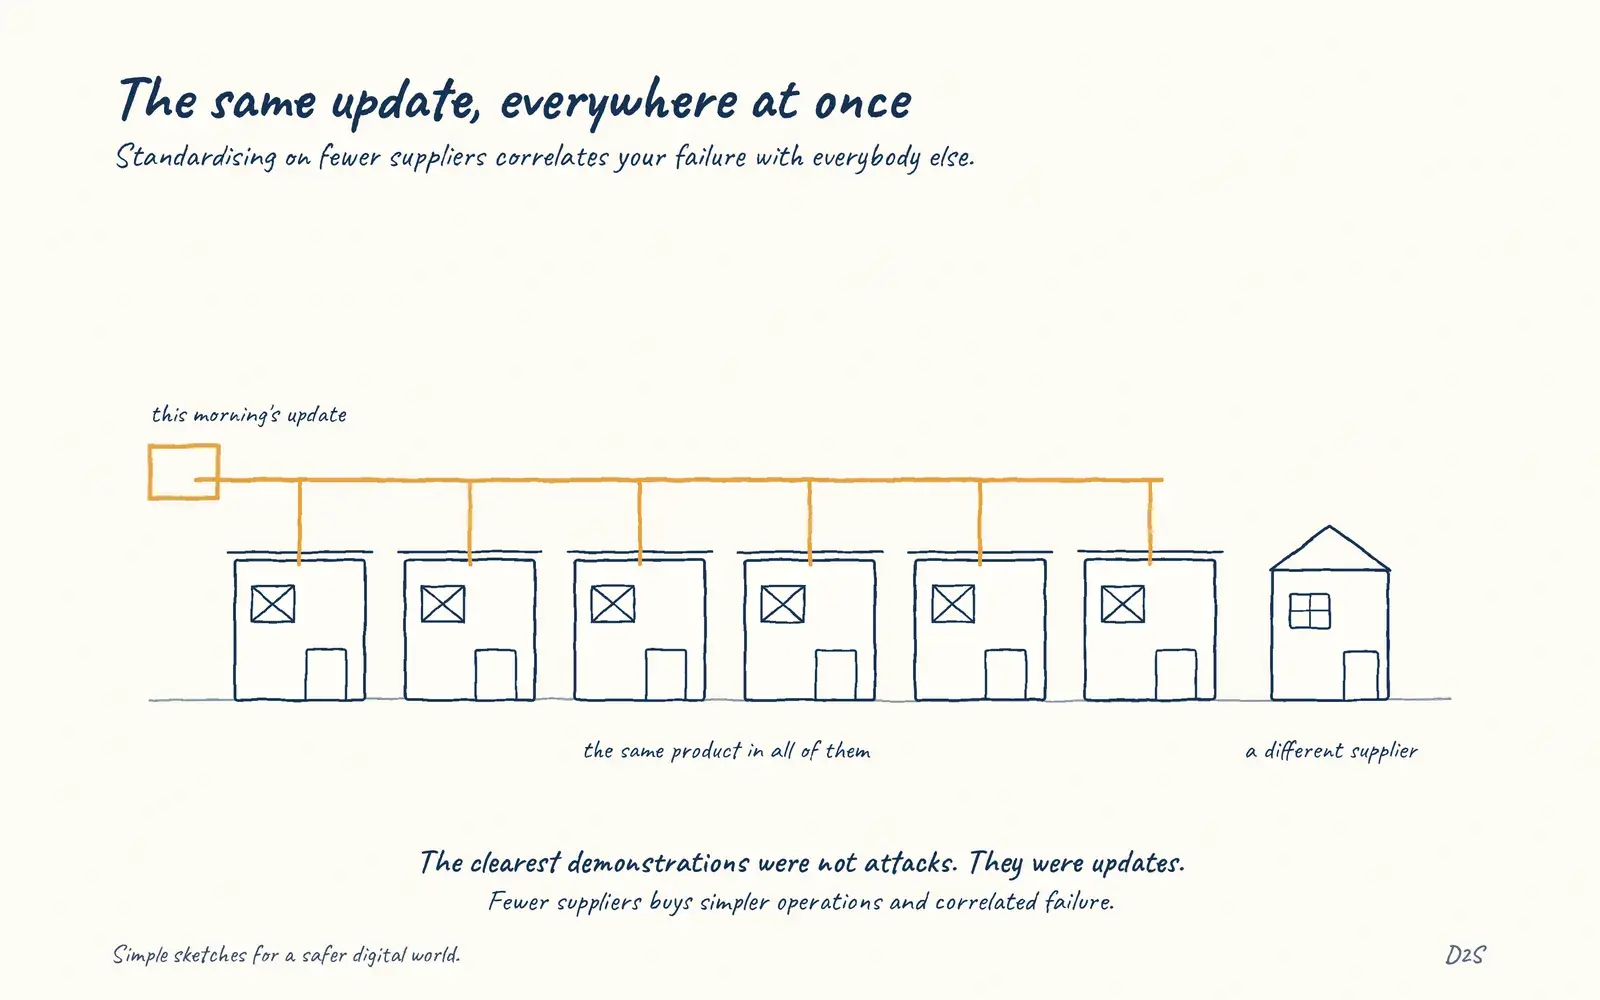 Vendor concentrationThe same update, everywhere at once
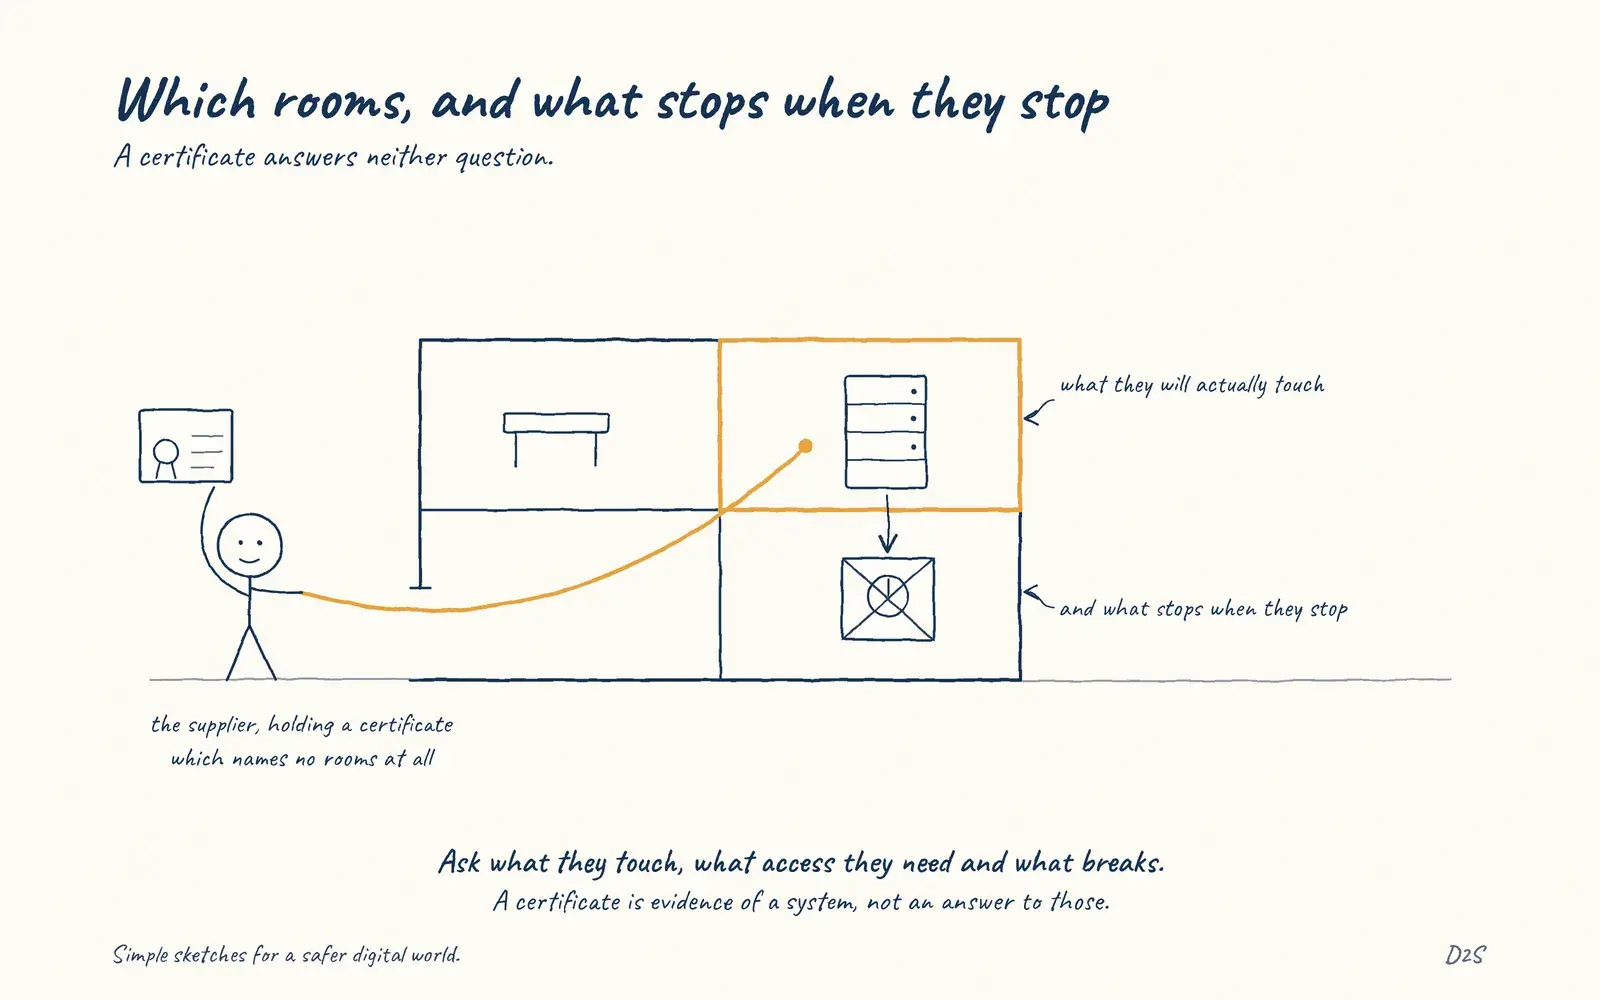 Vendor due diligenceWhich rooms, and what stops when they stop
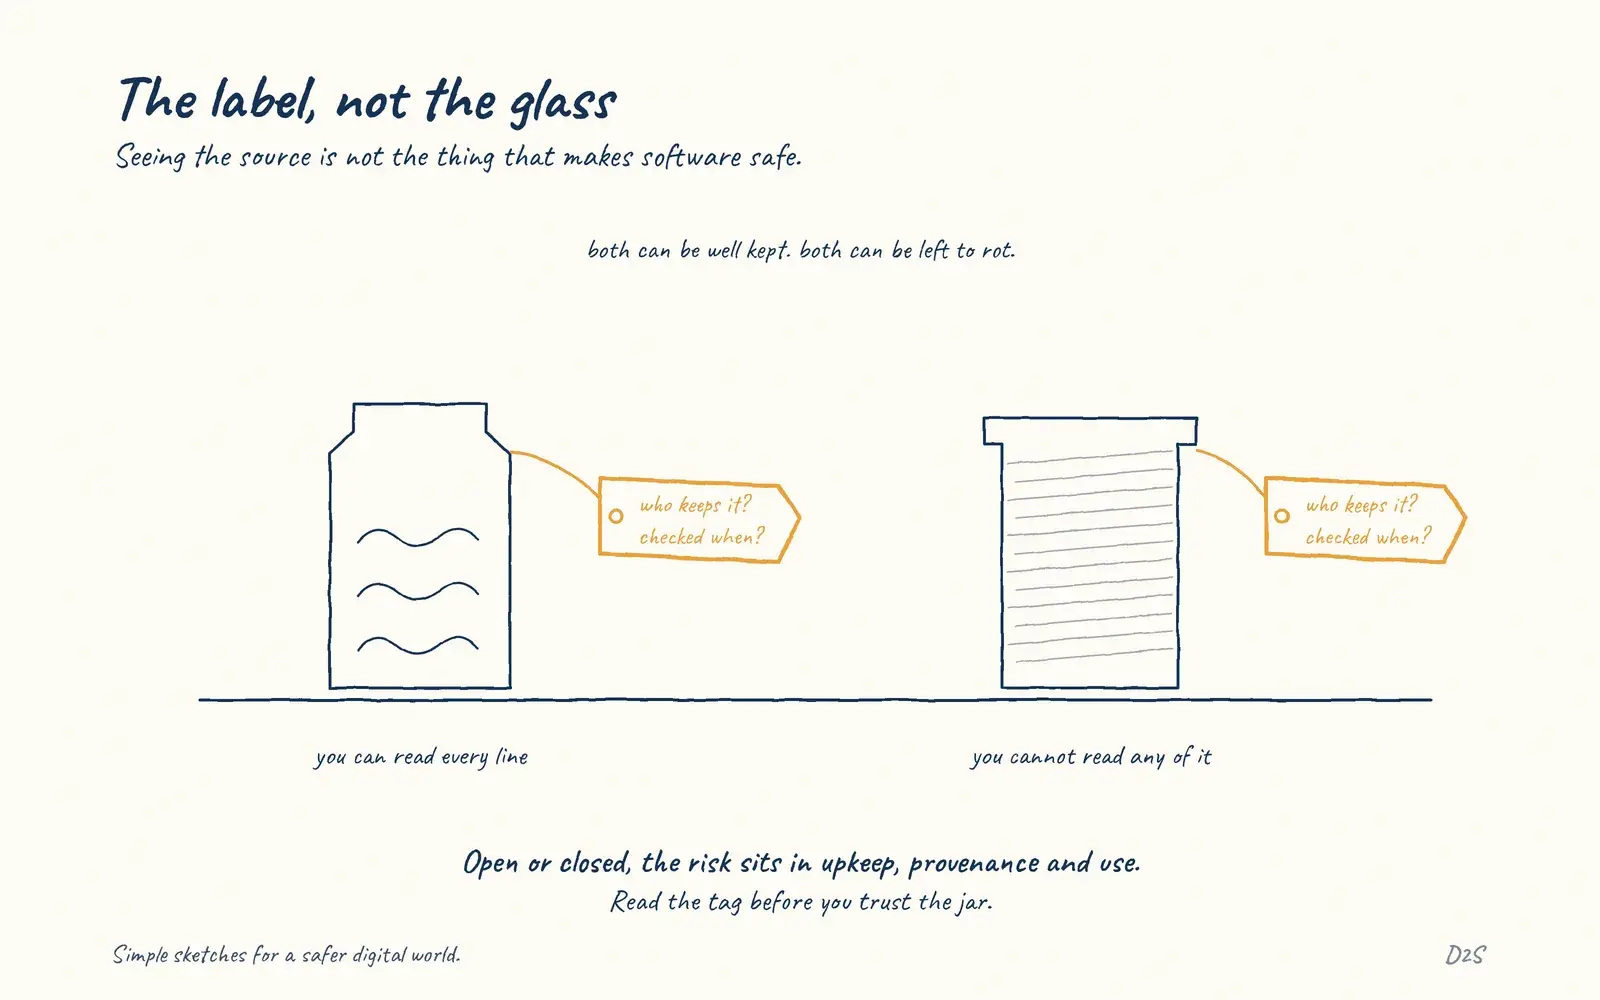 'open source is less secure'The label, not the glass
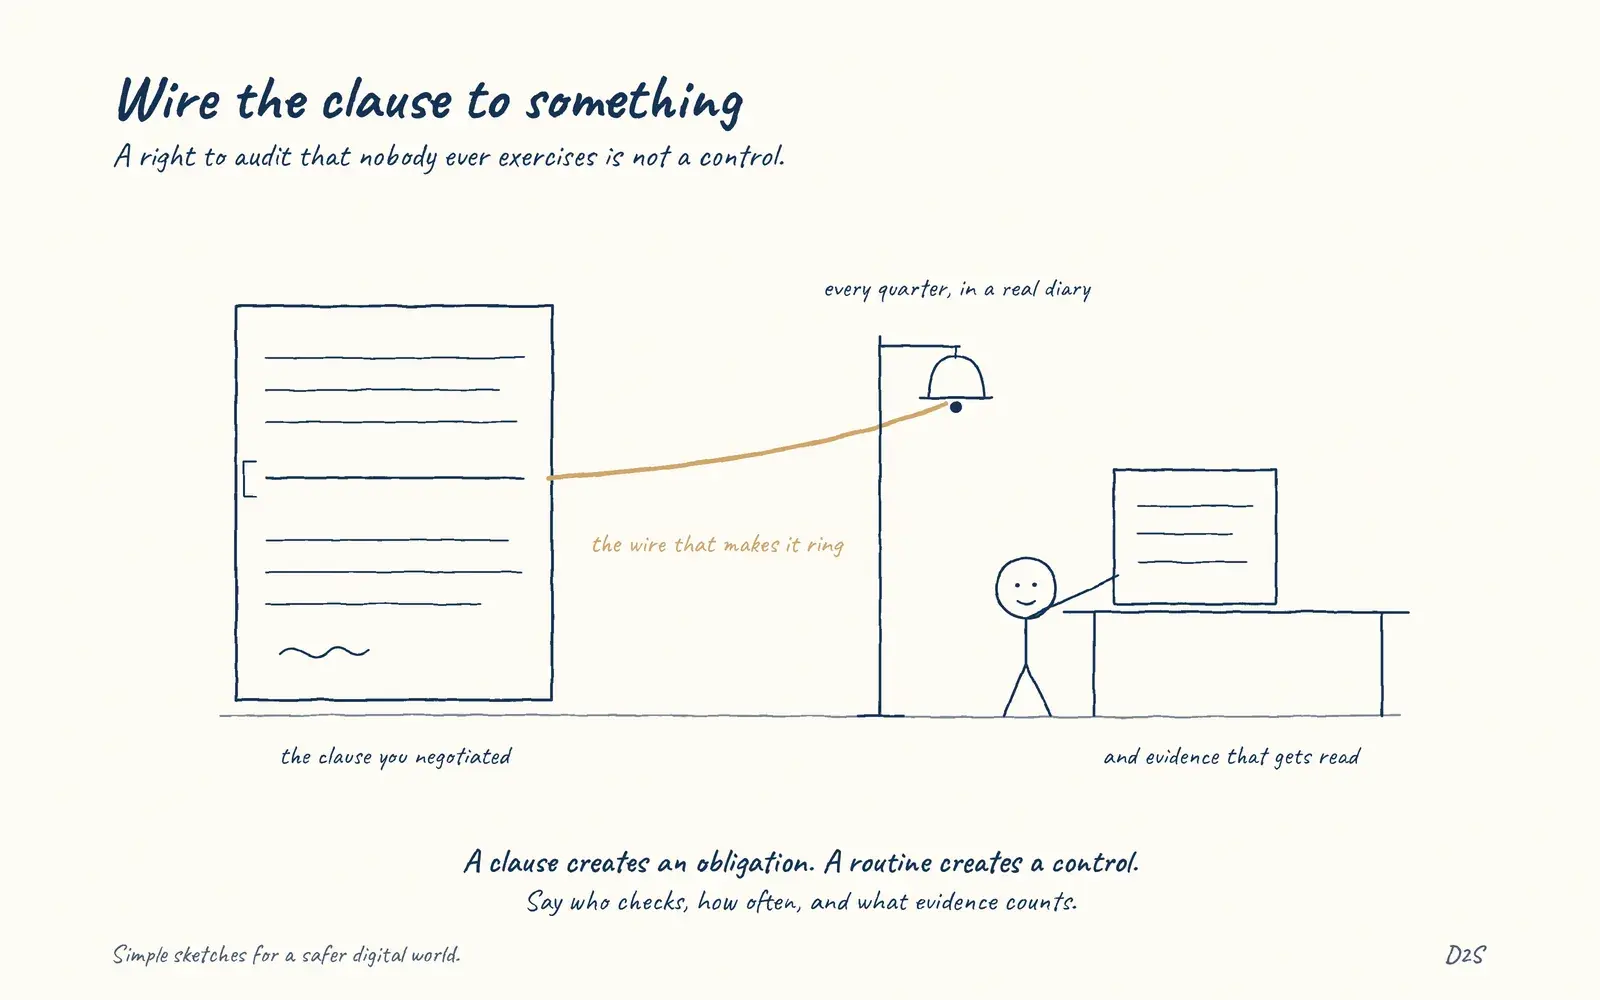 Security clauses need operational follow-throughWire the clause to something
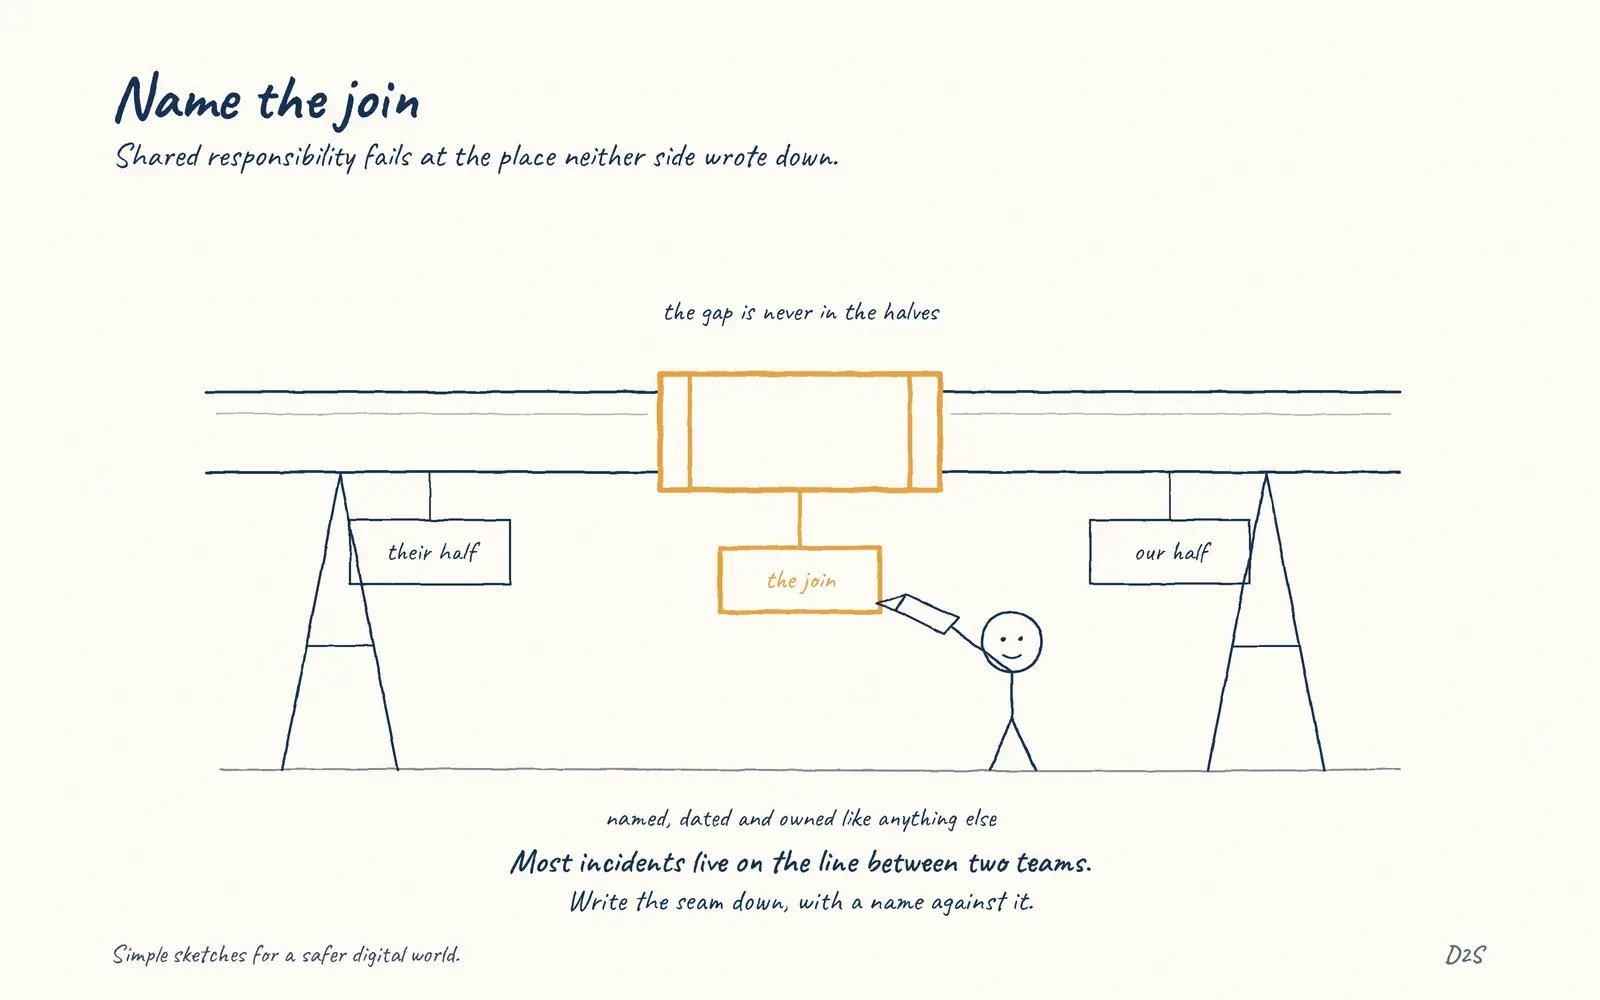 Shared responsibility should name the seamName the join
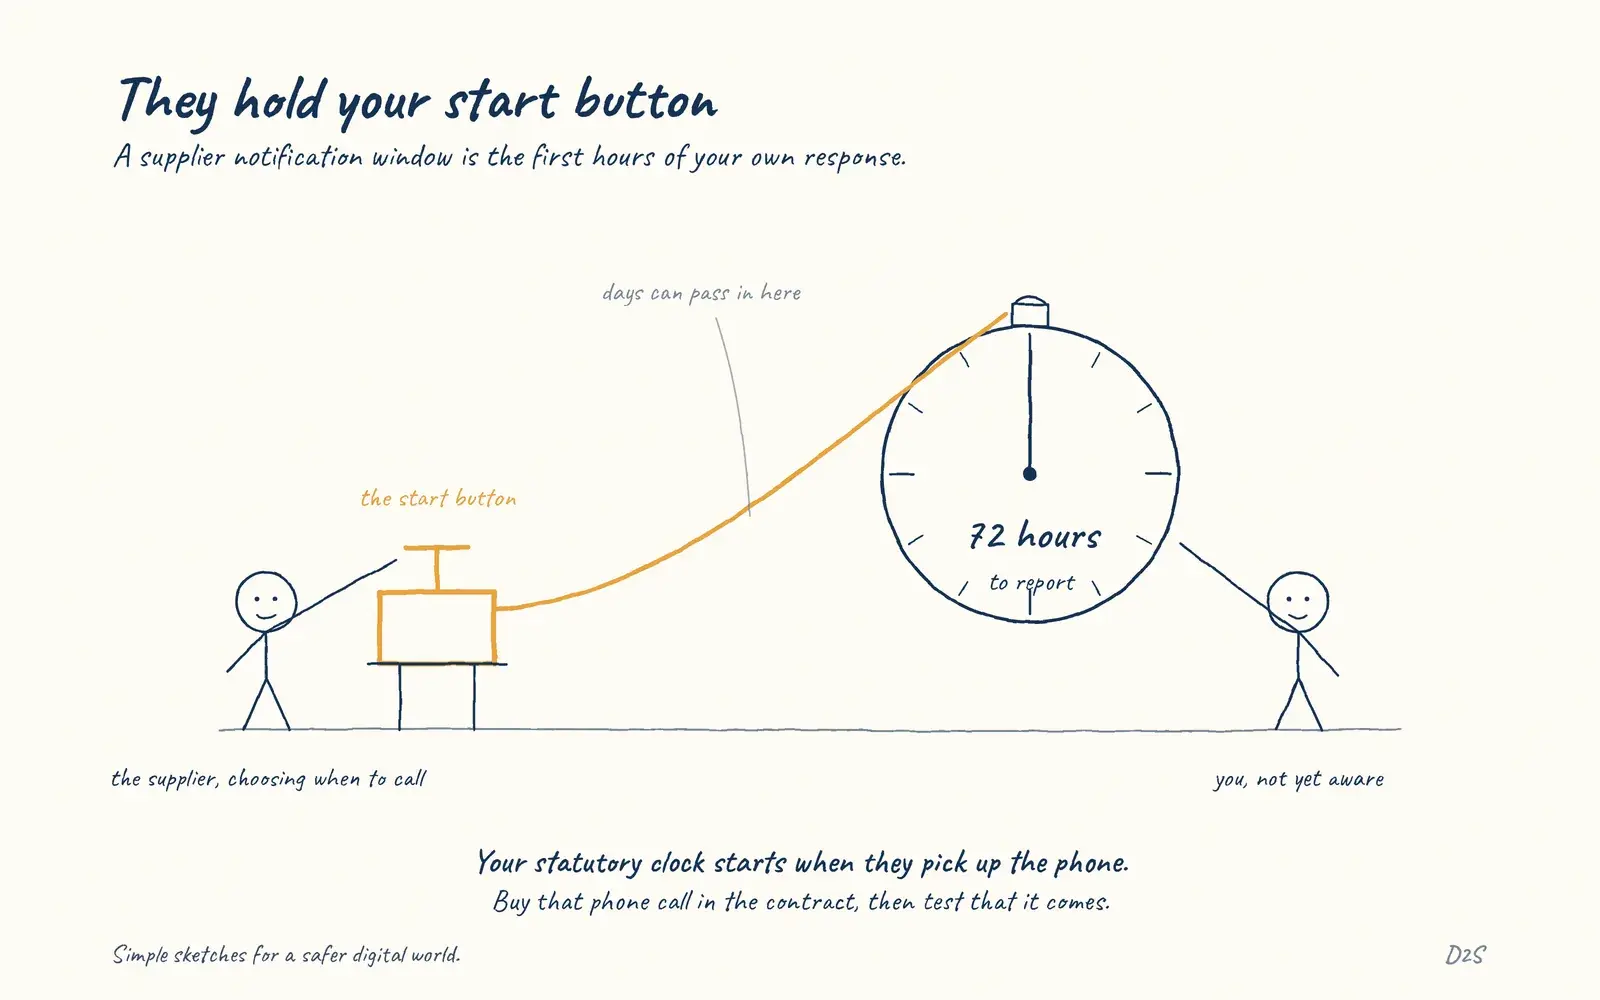 Supplier notification affects your response clockThey hold your start button
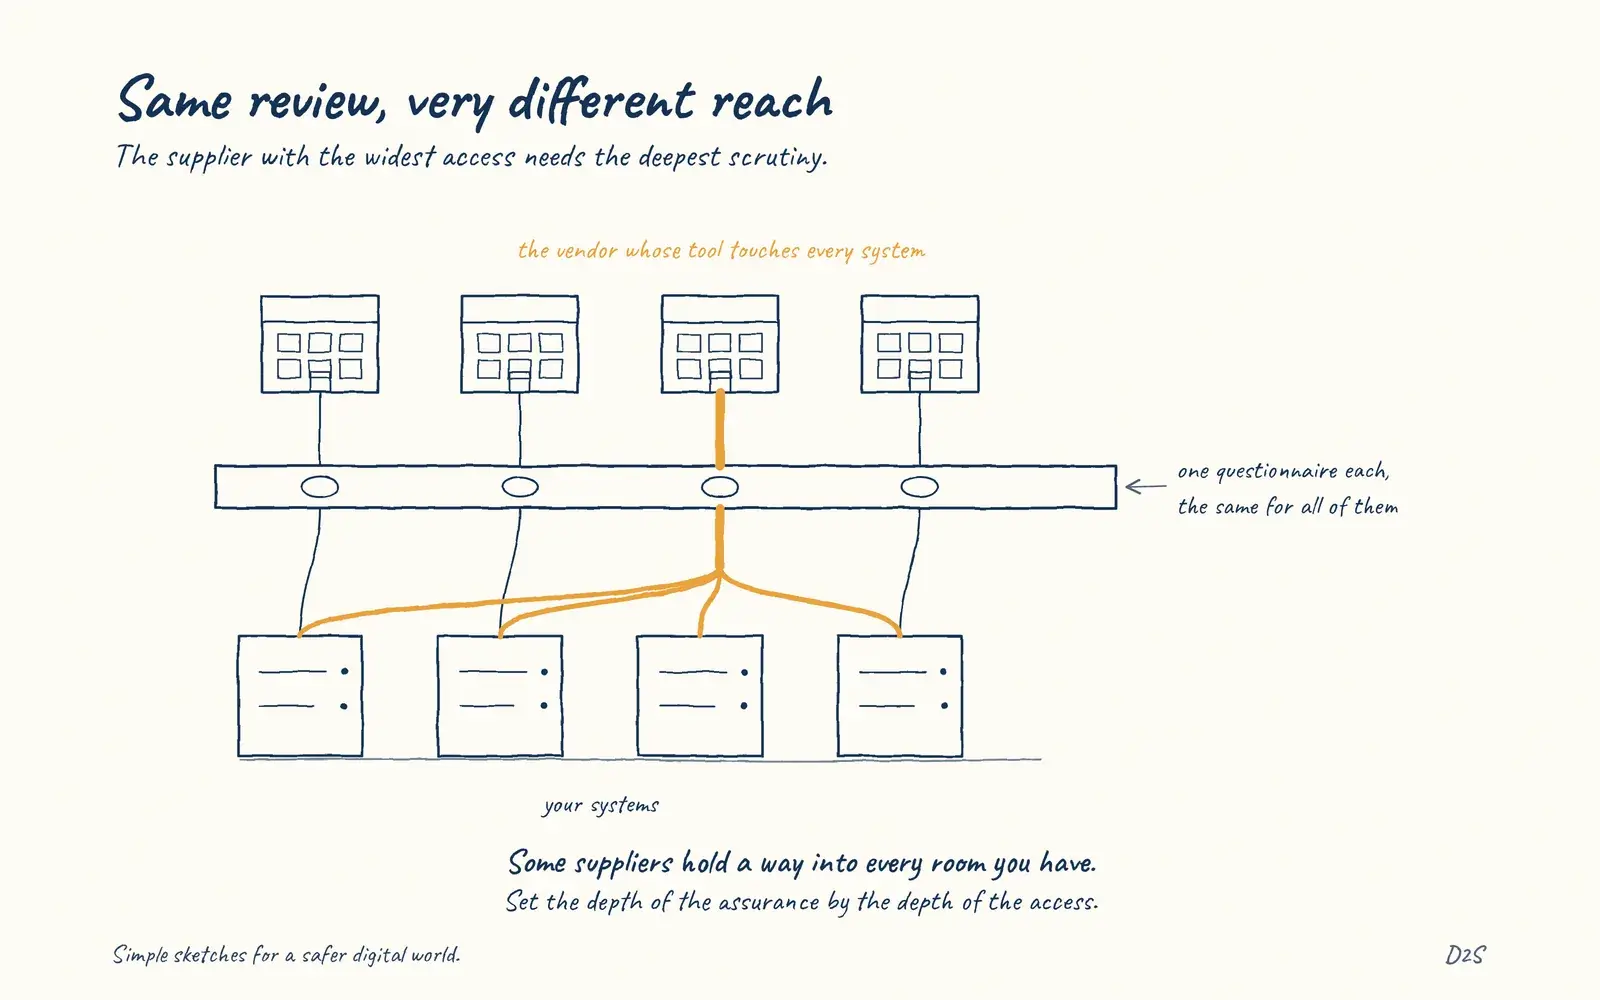 Privileged vendors deserve privileged controlsSame review, very different reach
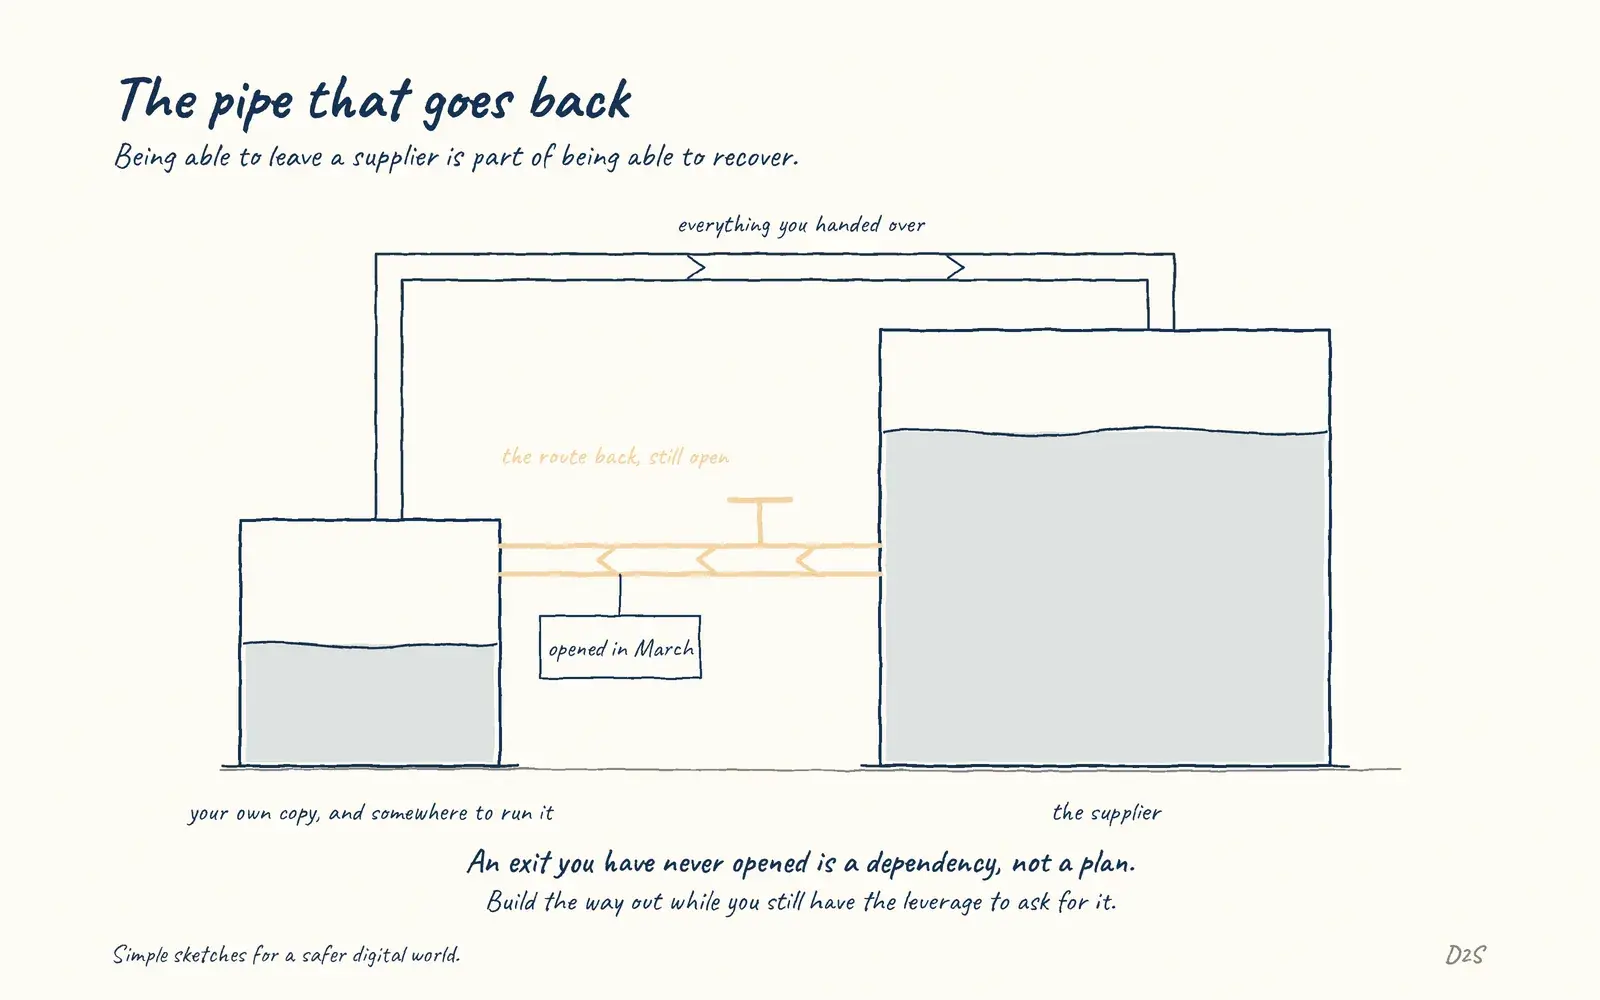 Exit plans are security controlsThe pipe that goes back