
Identity & access
Who someone is, what they may do, and how both get proved. Most breaches start here.
66 sketches
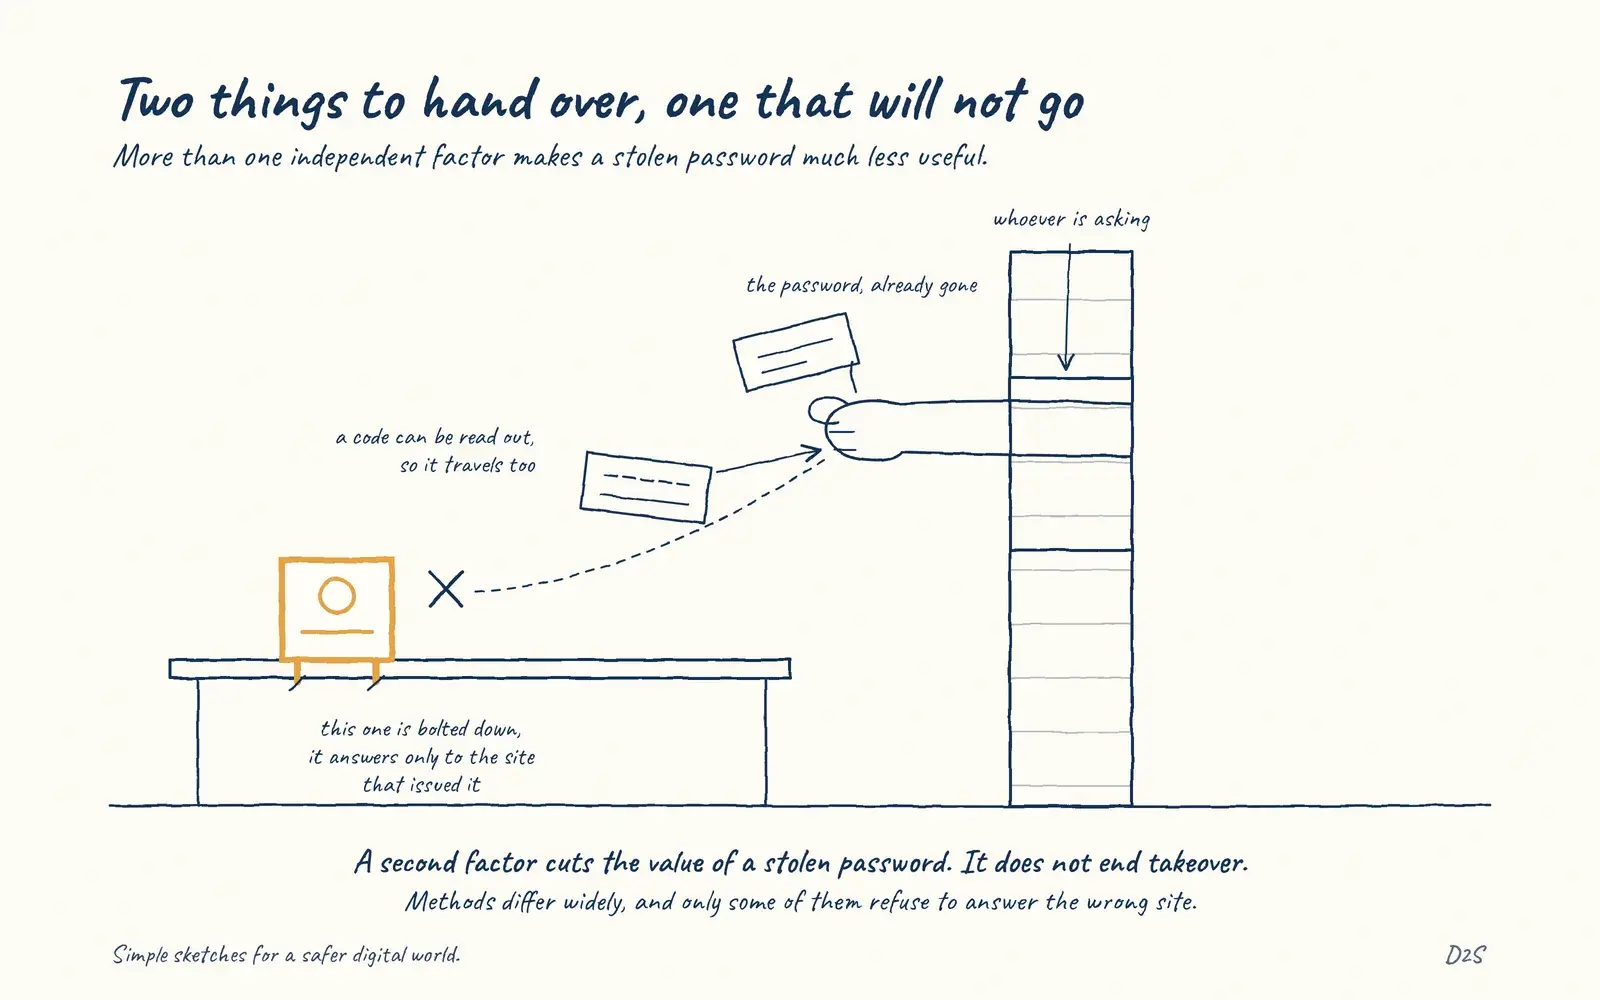 MFATwo things to hand over, one that will not go
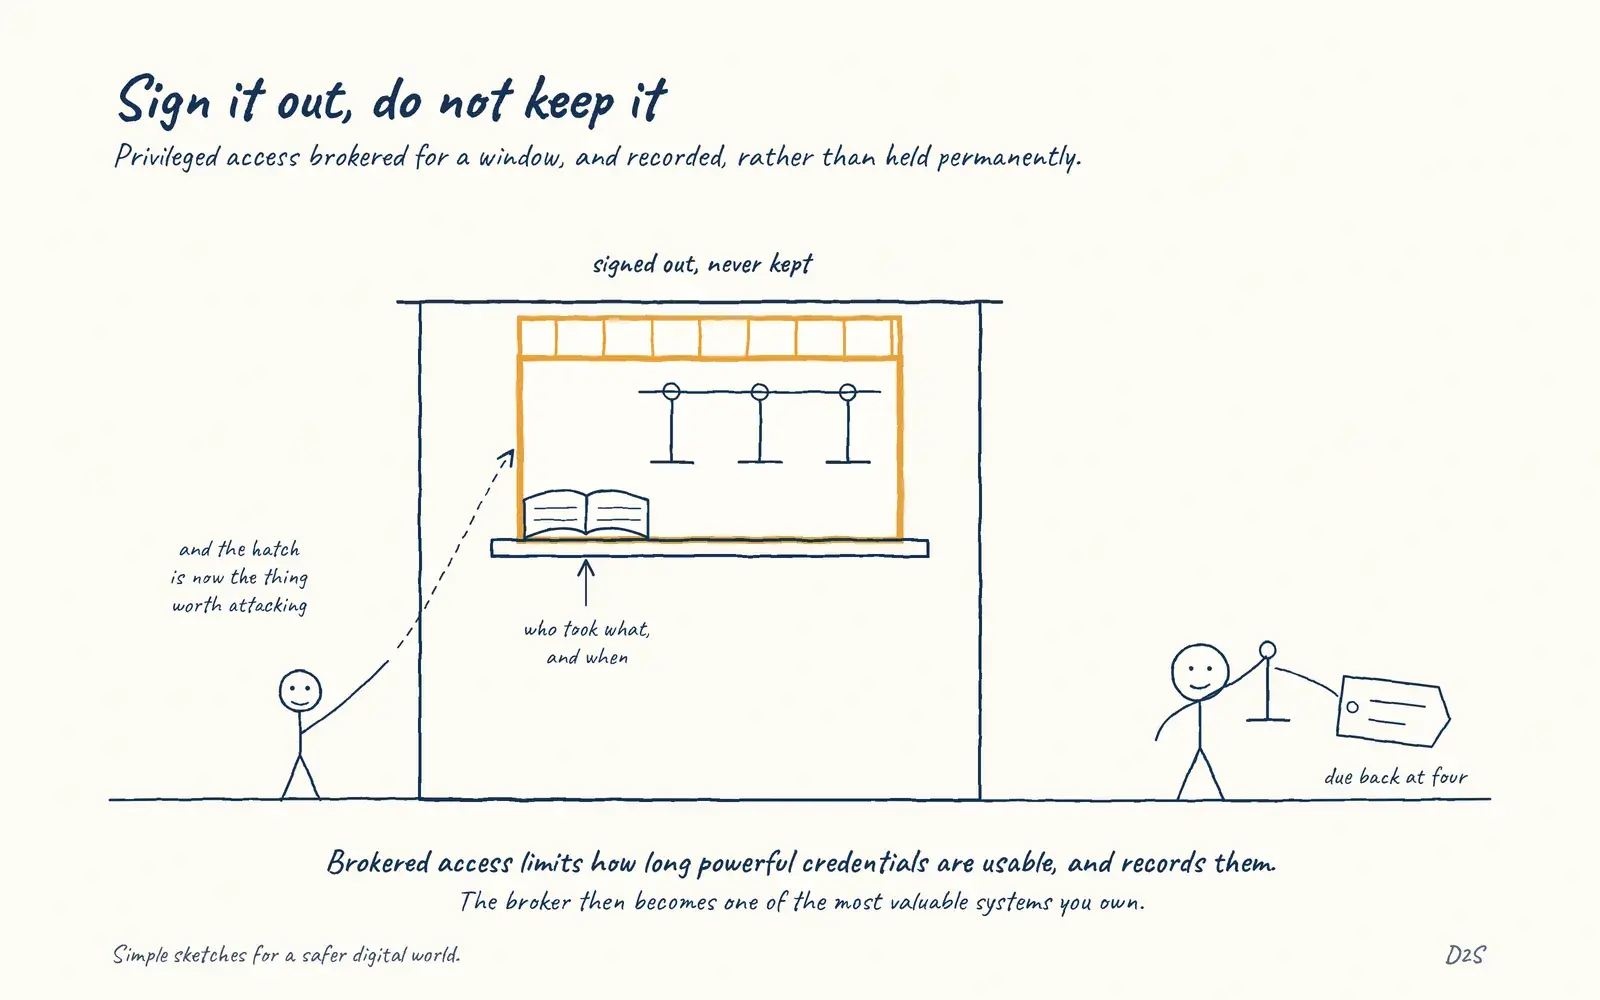 PAMSign it out, do not keep it
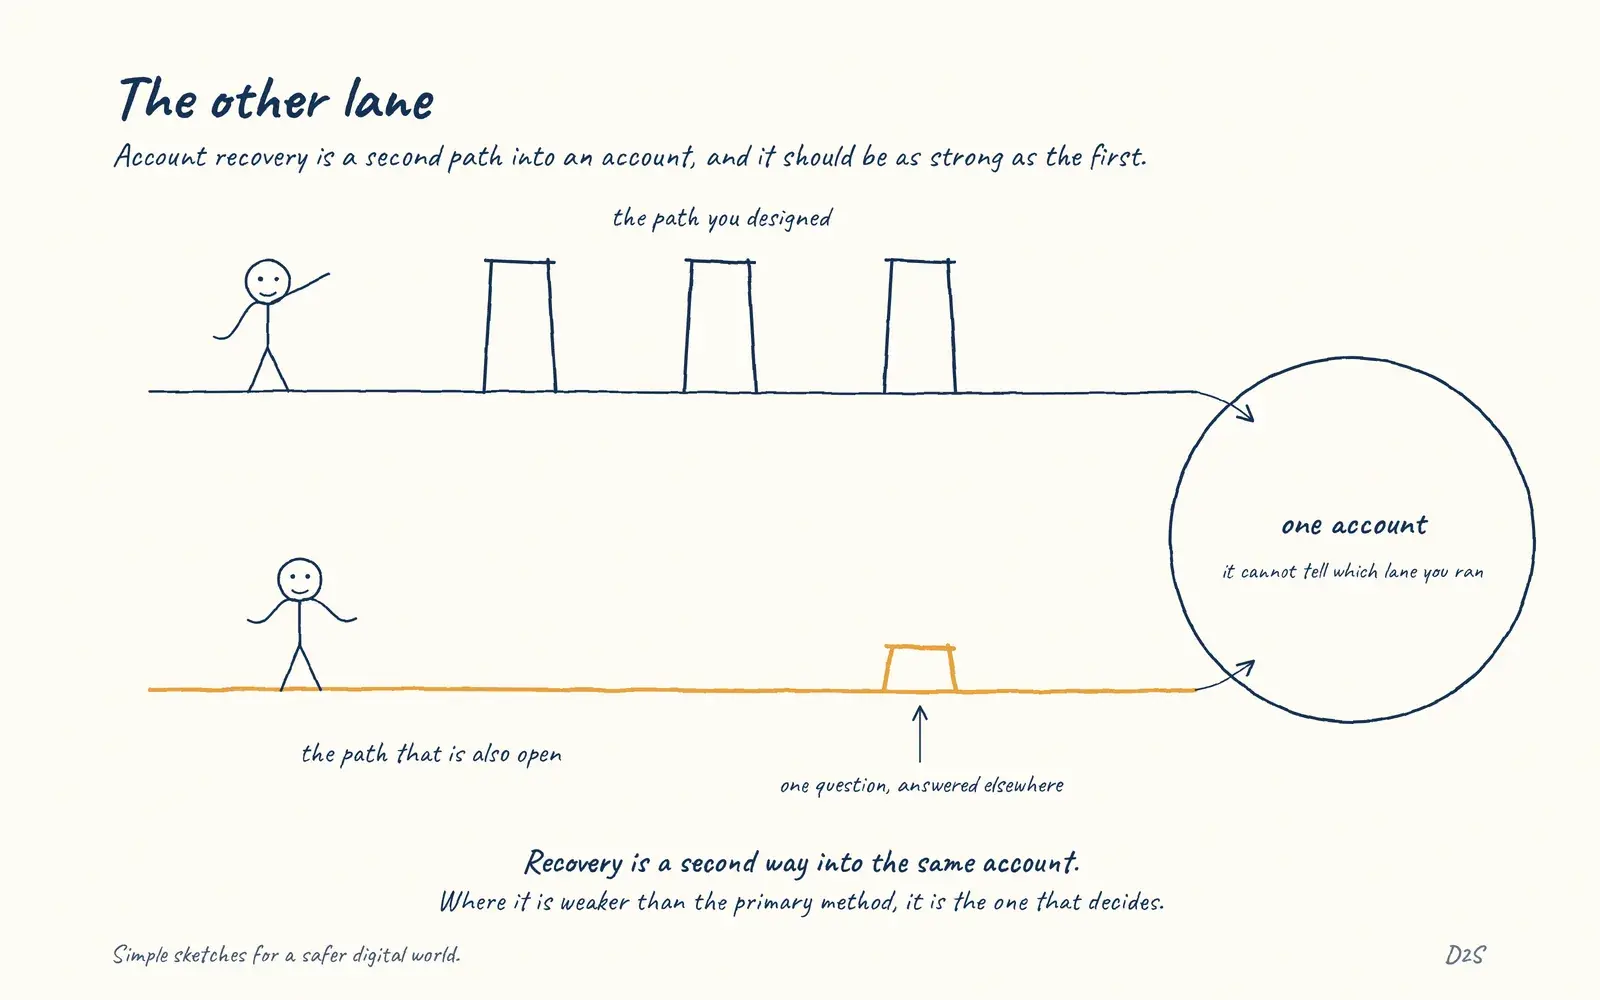 Account recoveryThe other lane
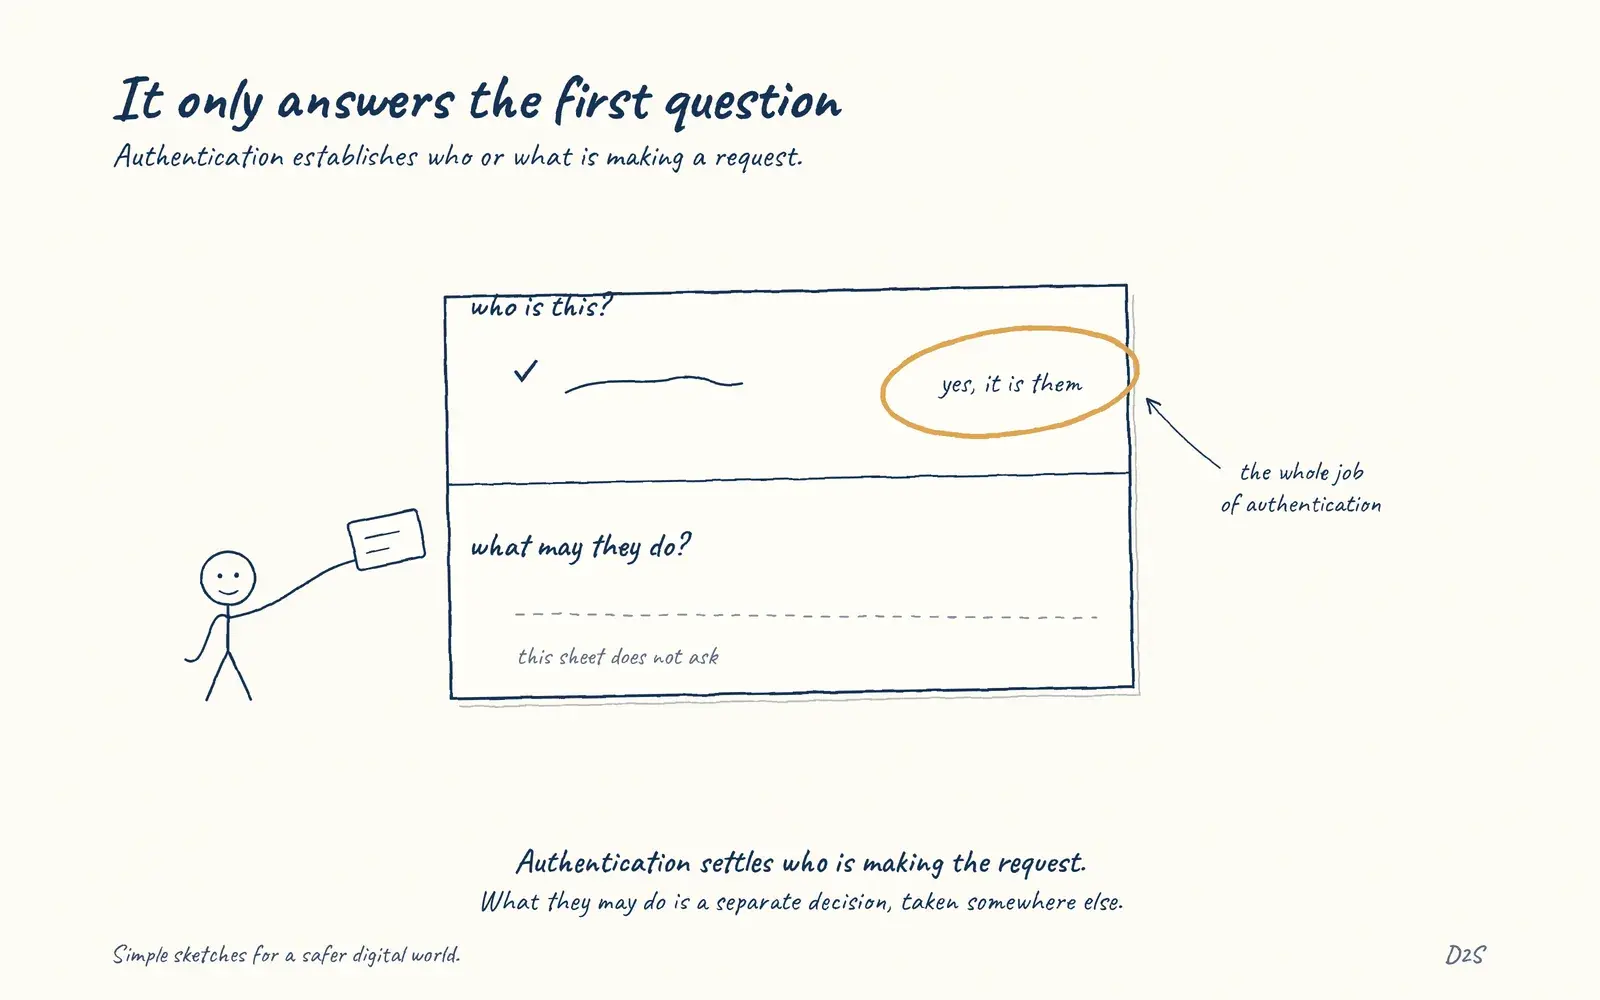 AuthenticationIt only answers the first question
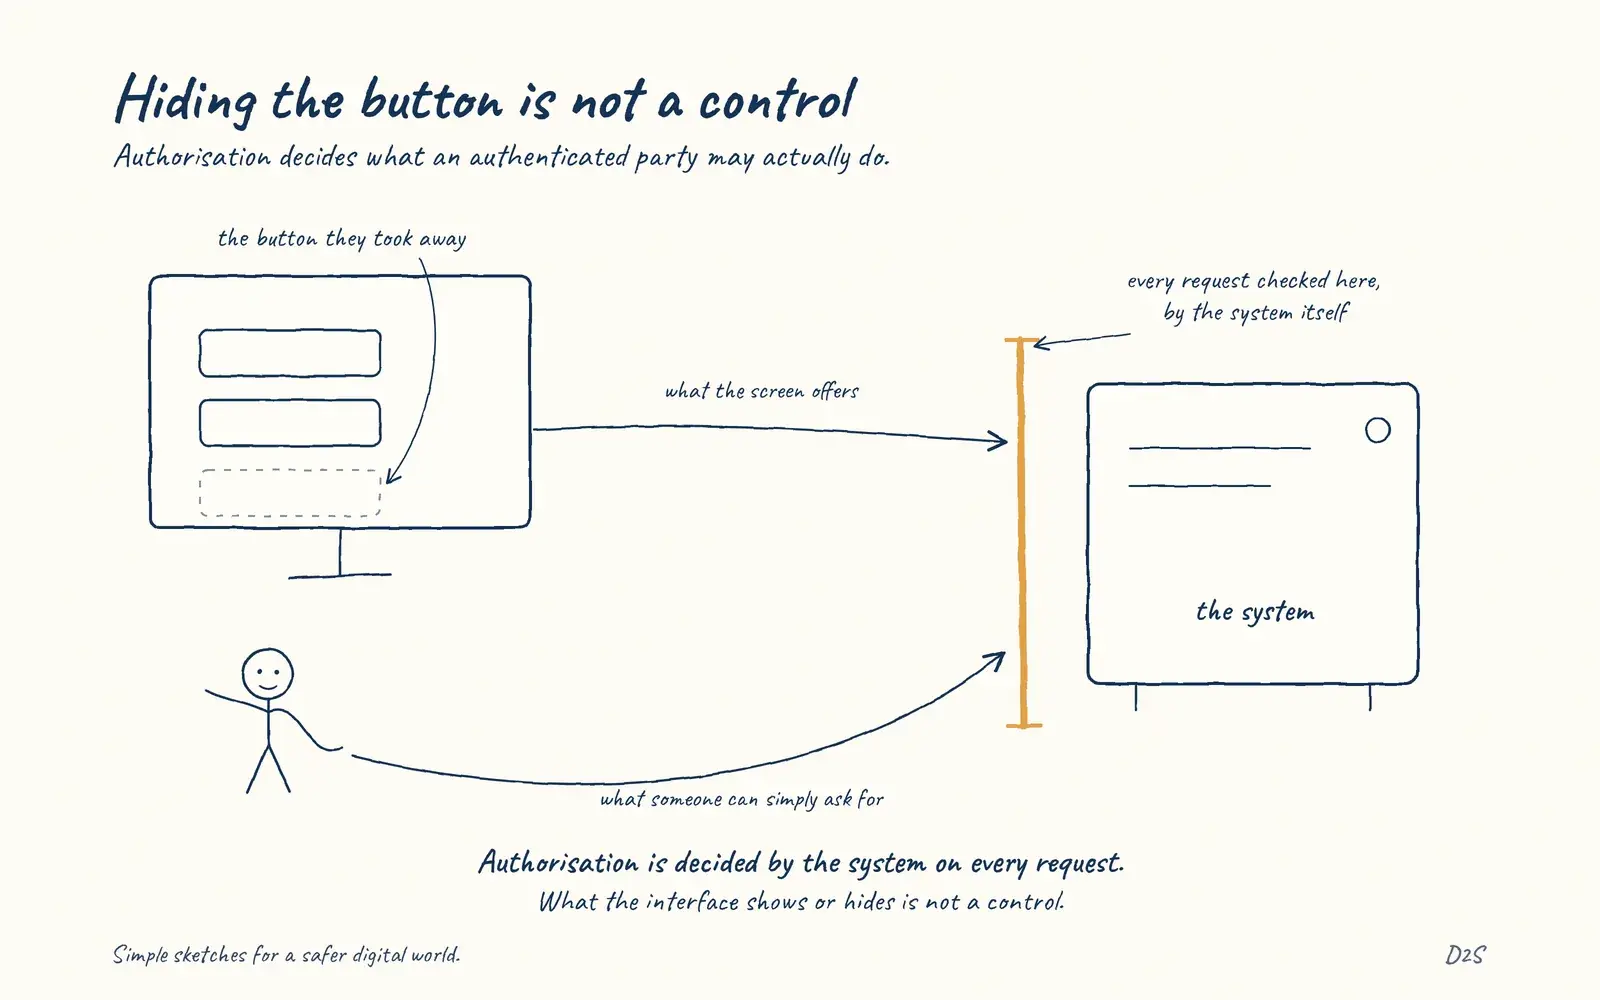 AuthorisationHiding the button is not a control
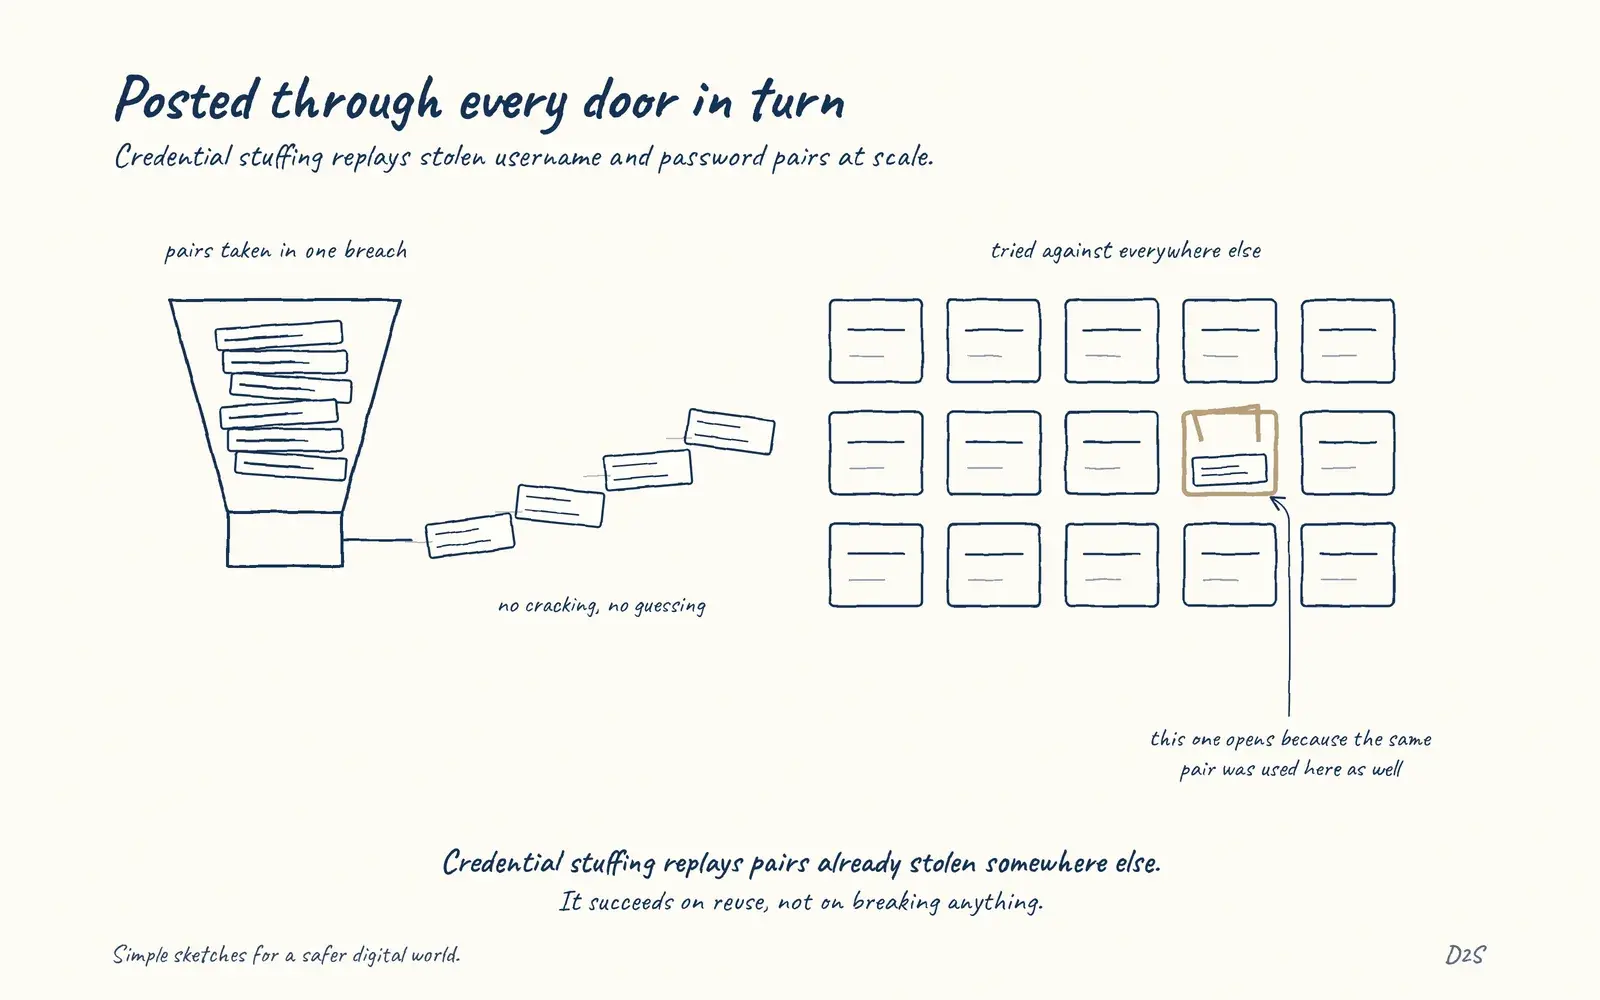 Credential stuffingPosted through every door in turn
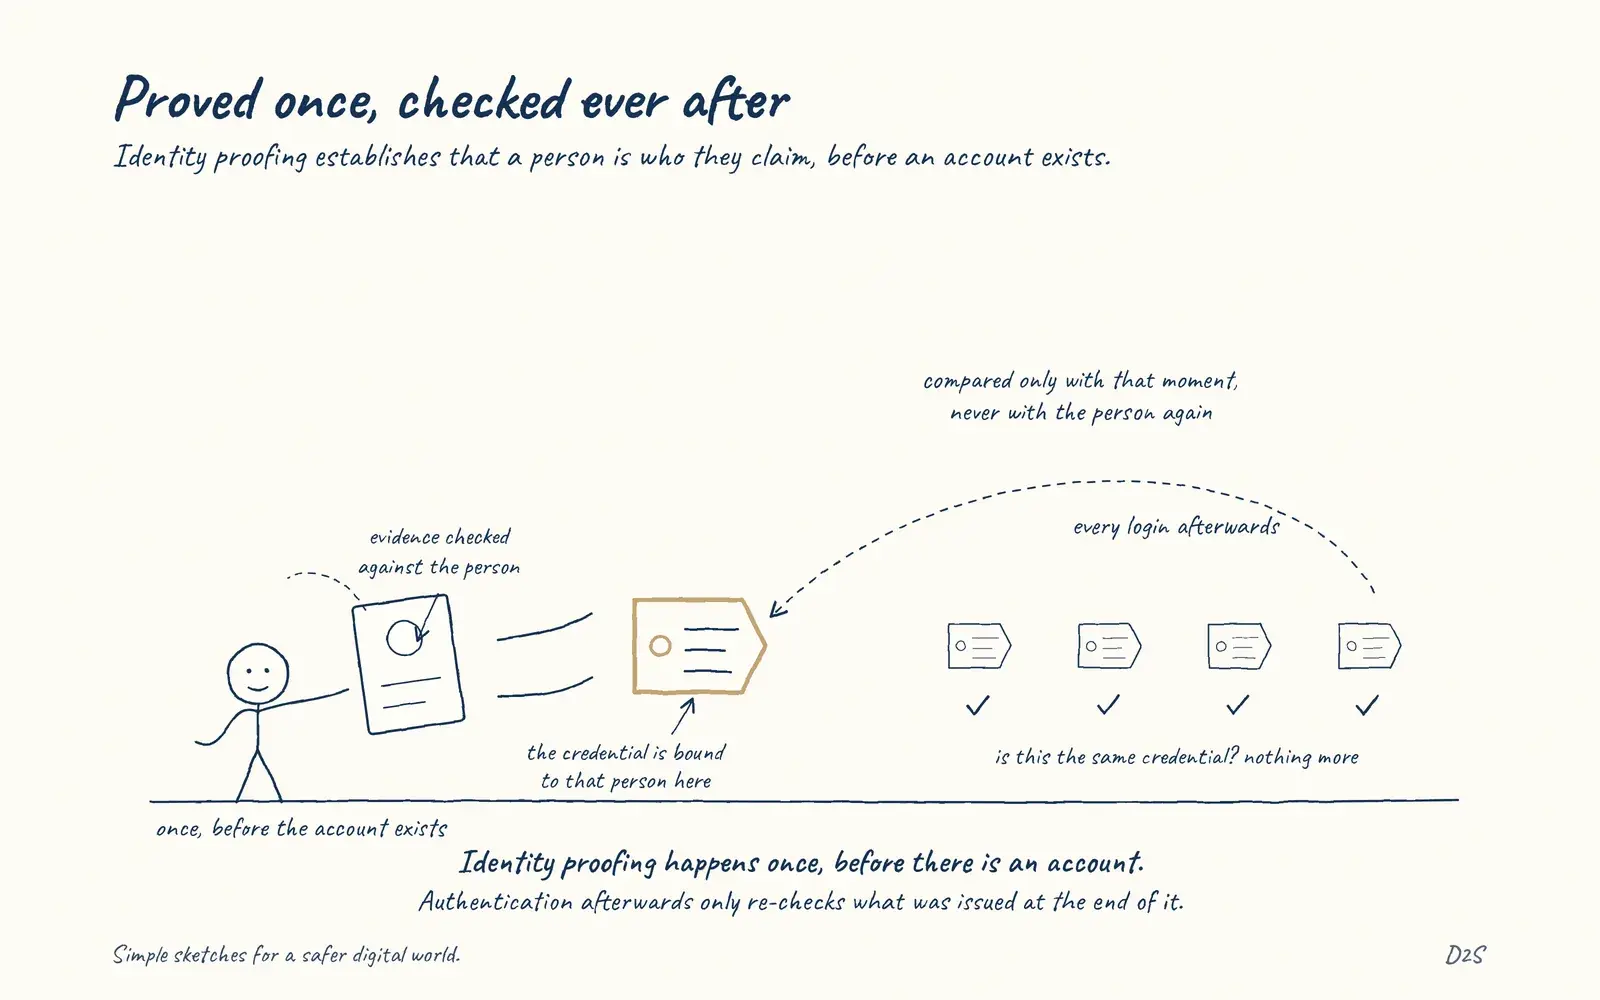 Identity proofingProved once, checked ever after
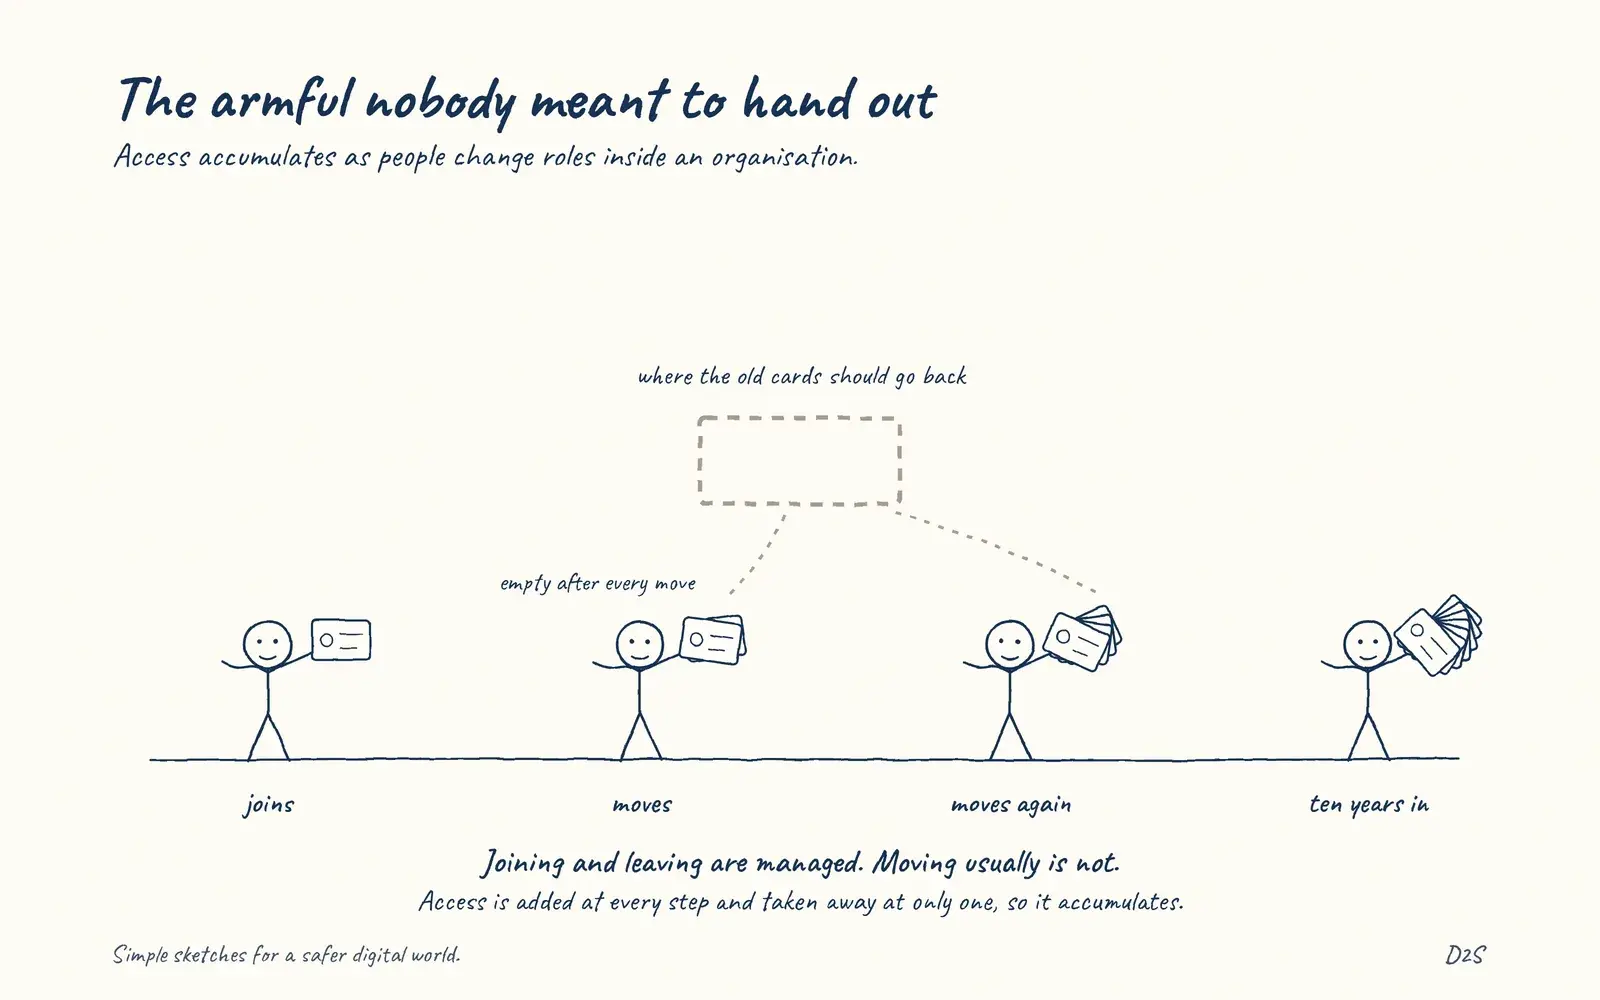 Joiner-mover-leaverThe armful nobody meant to hand out
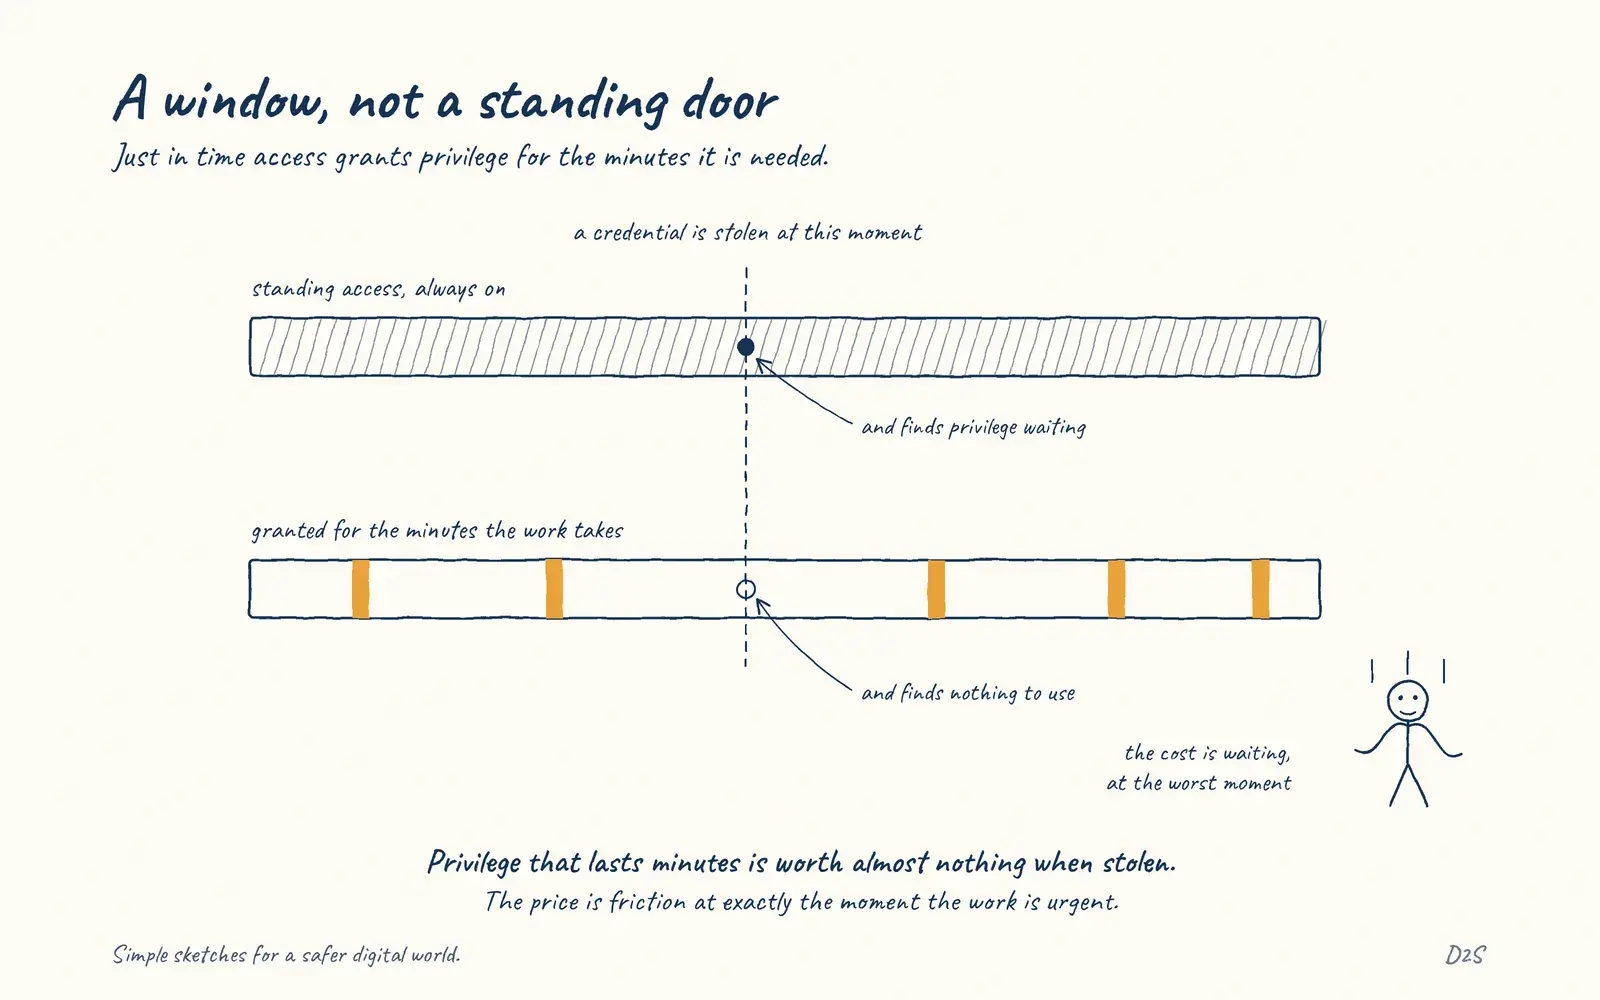 Just-in-time accessA window, not a standing door
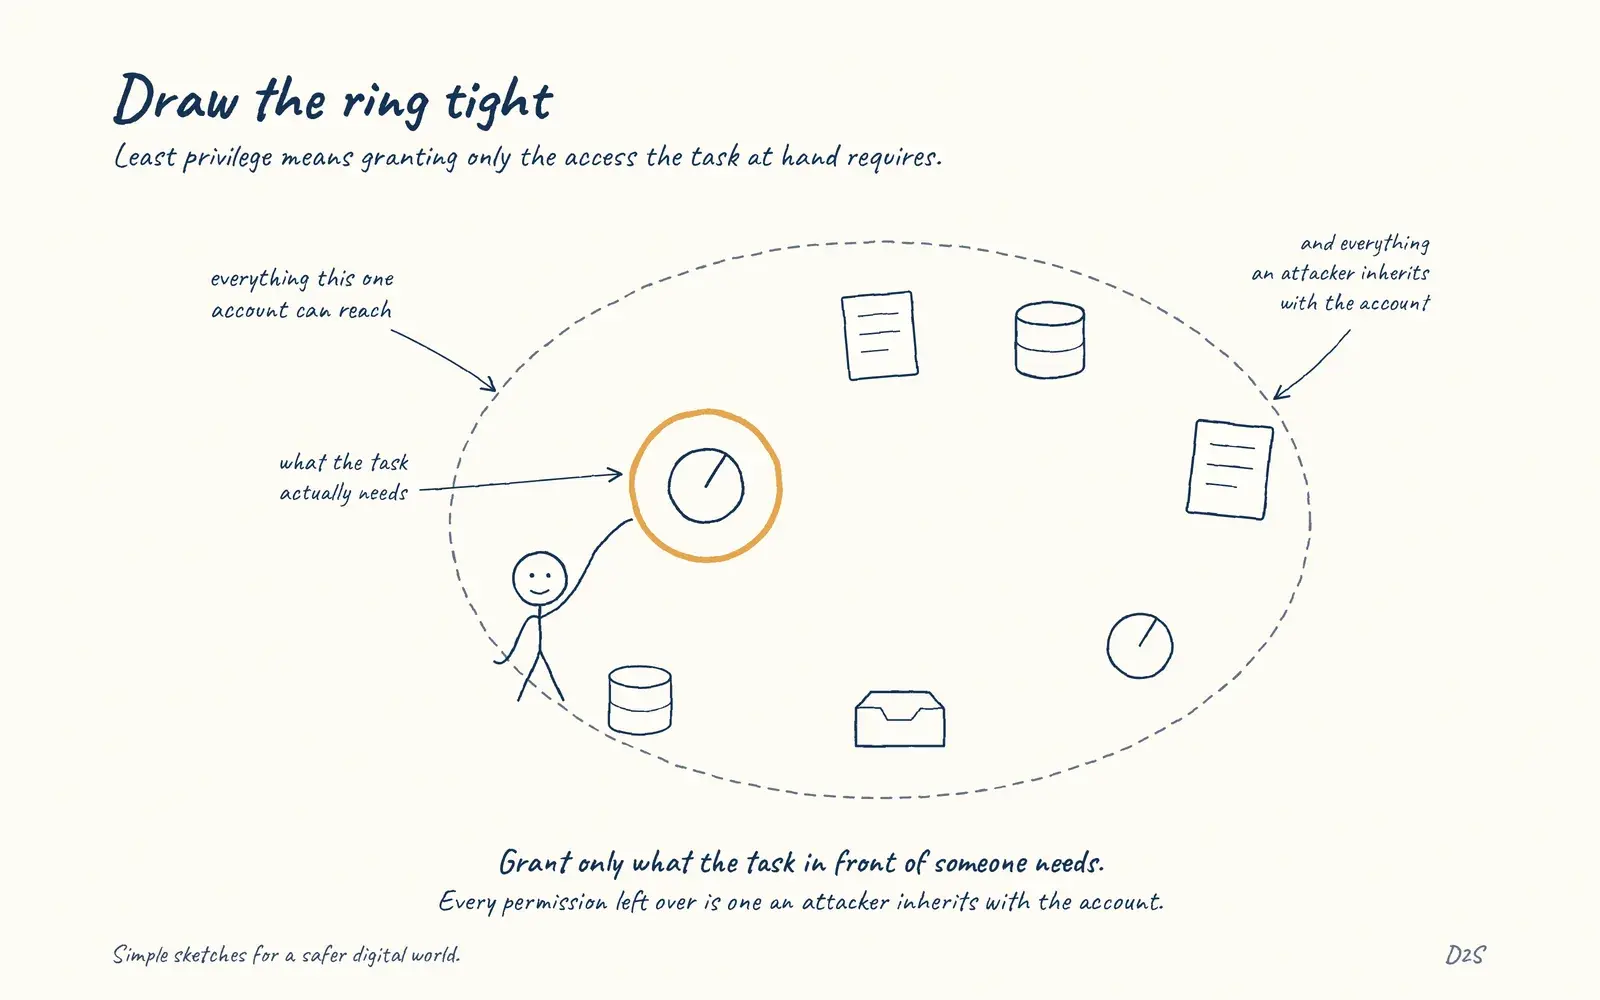 Least privilegeDraw the ring tight
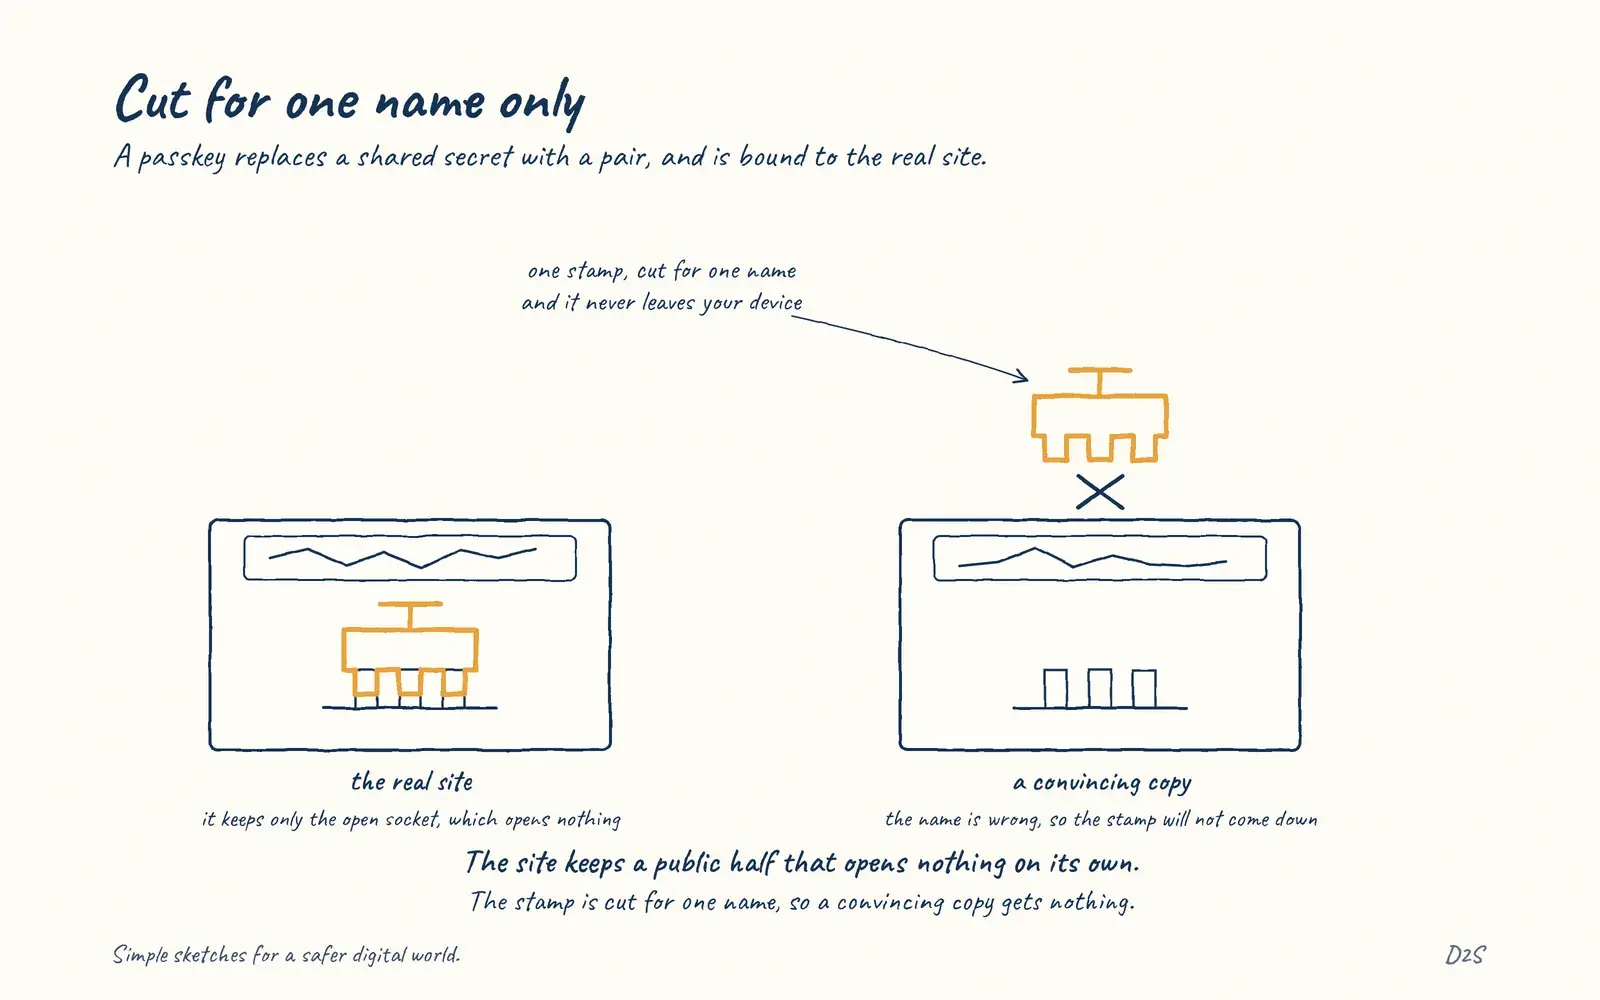 PasskeysCut for one name only
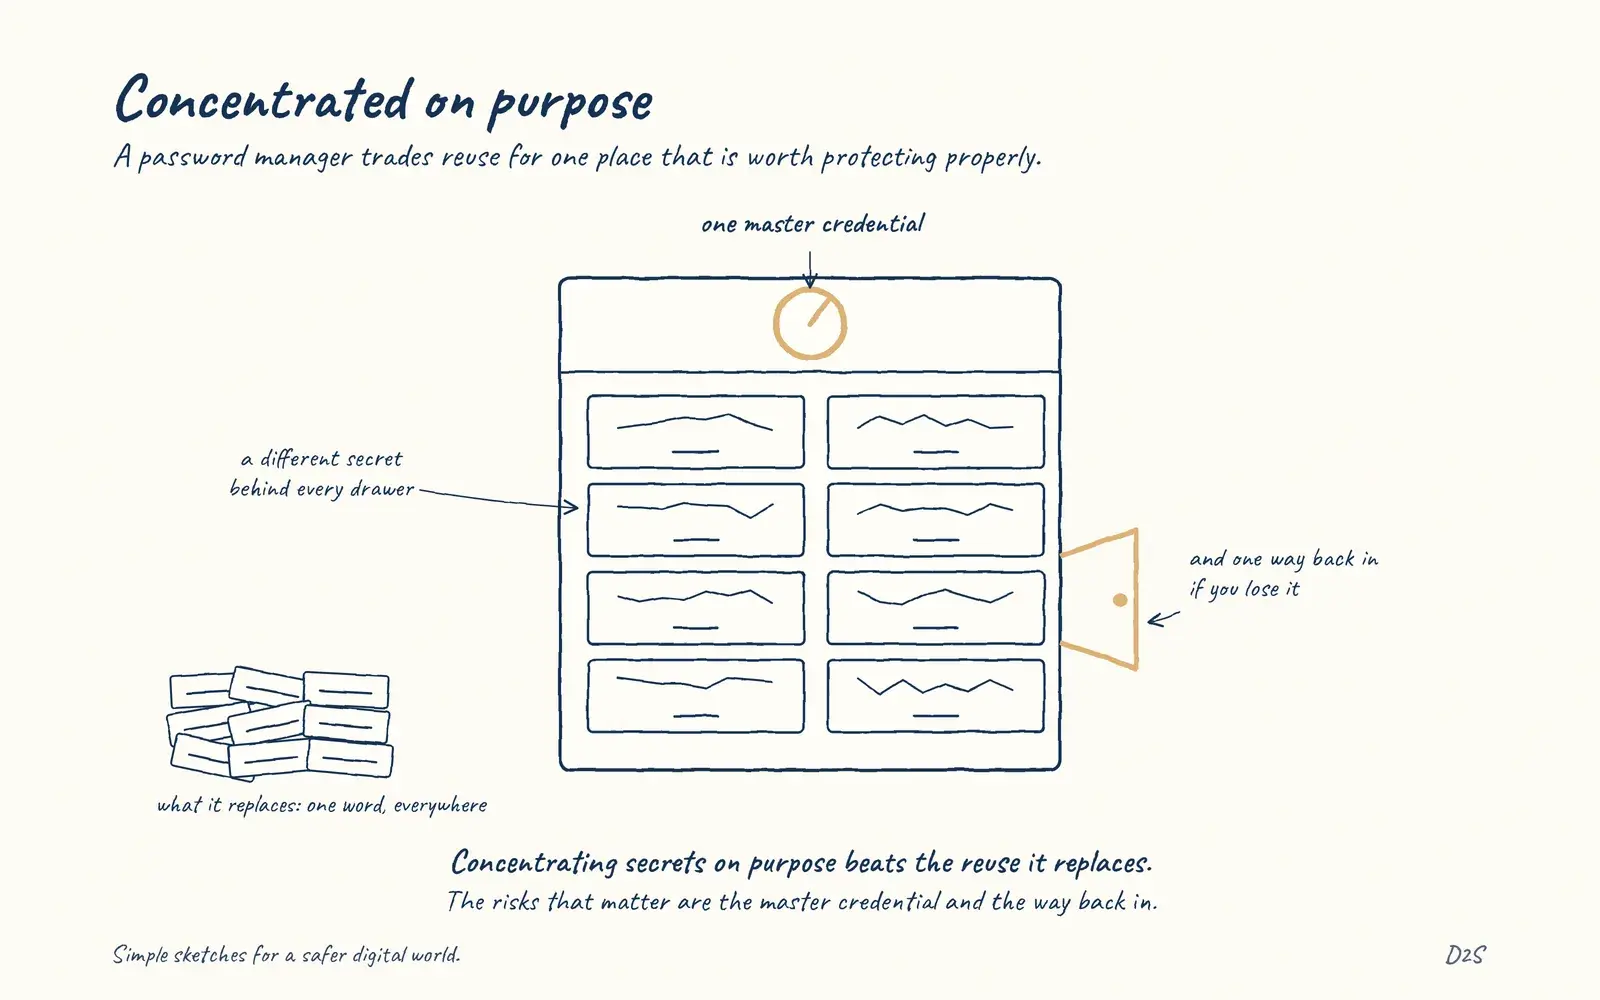 Password managersConcentrated on purpose
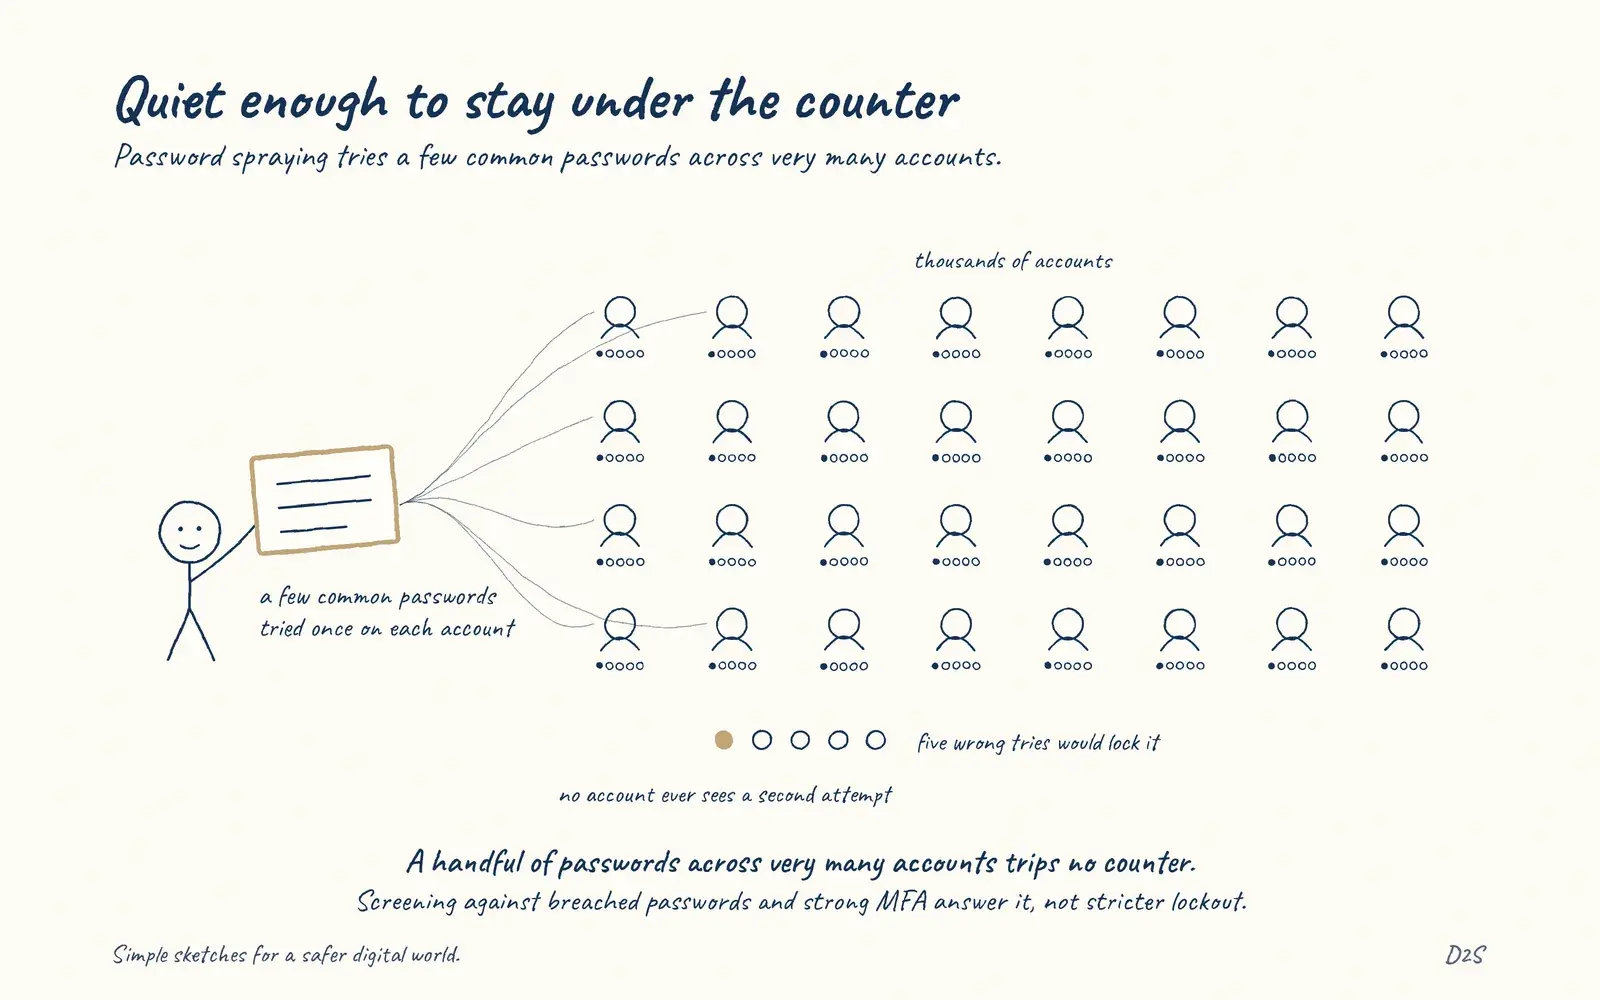 Password sprayingQuiet enough to stay under the counter
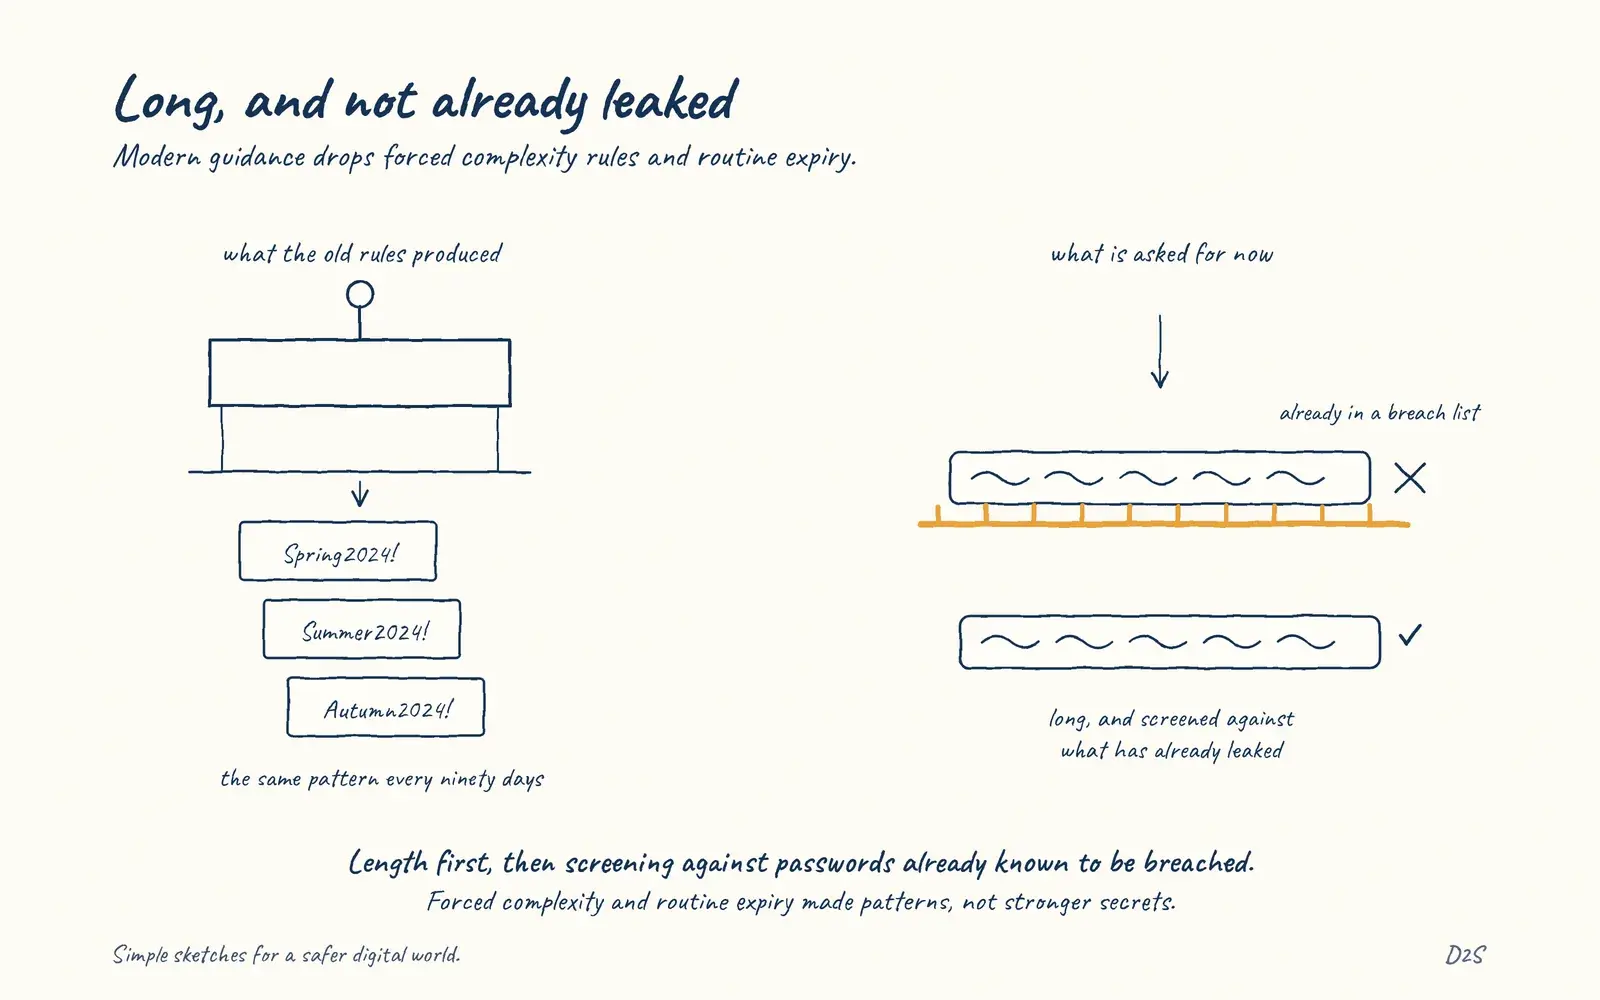 PasswordsLong, and not already leaked
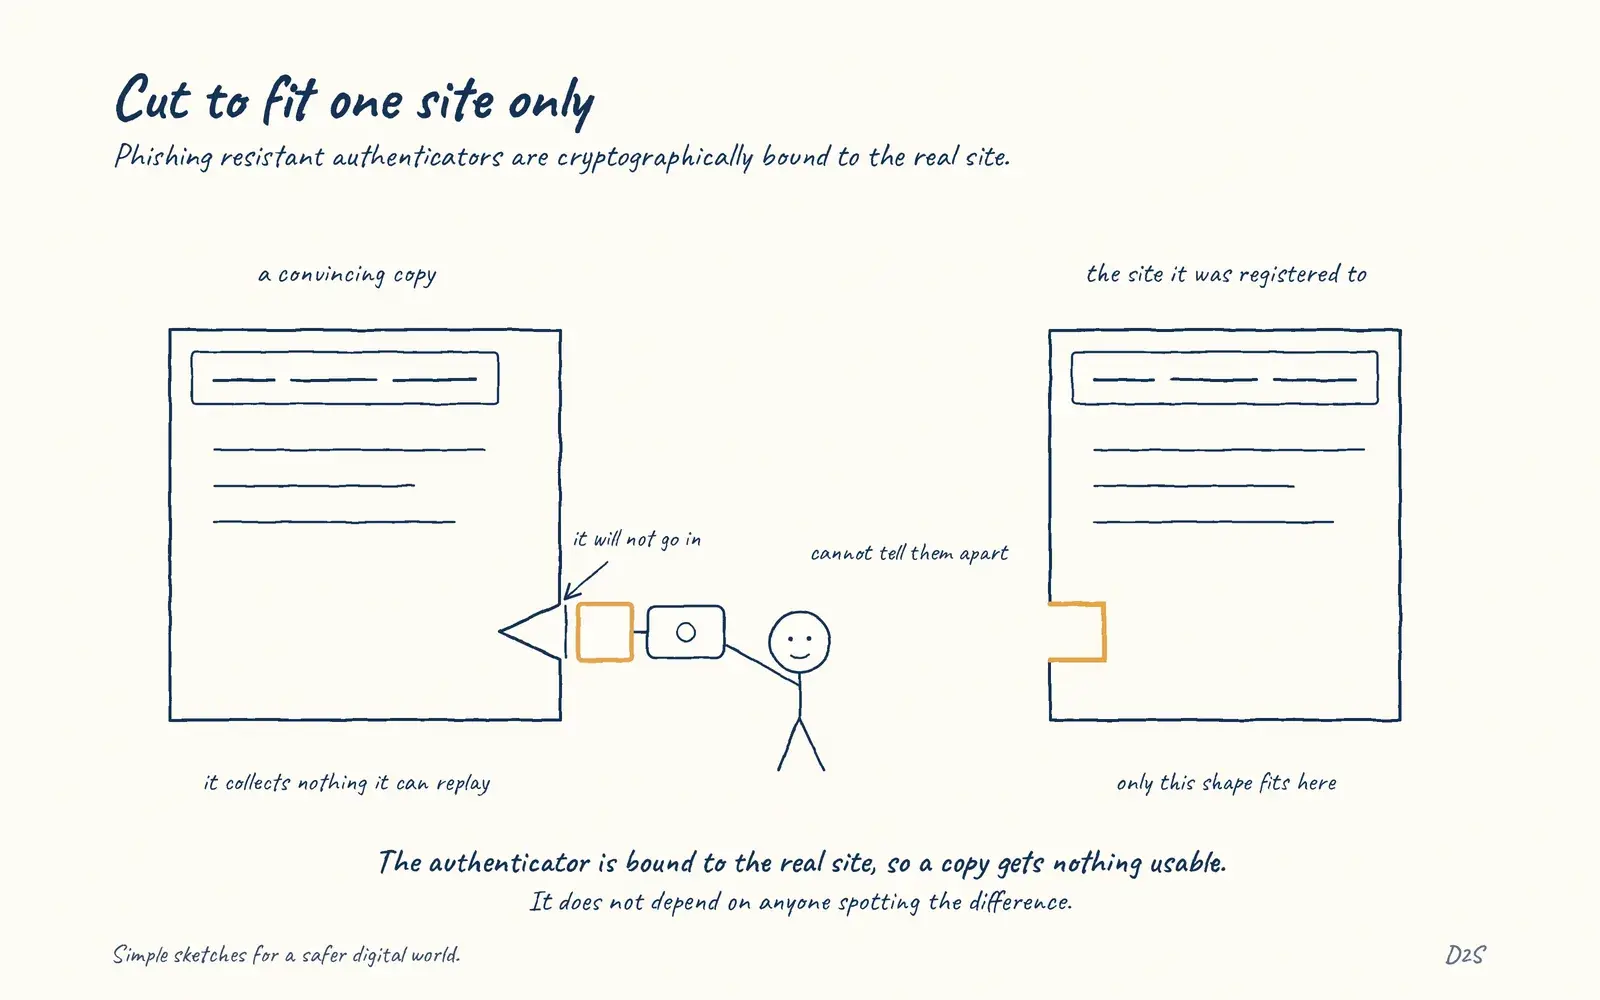 Phishing-resistant MFACut to fit one site only
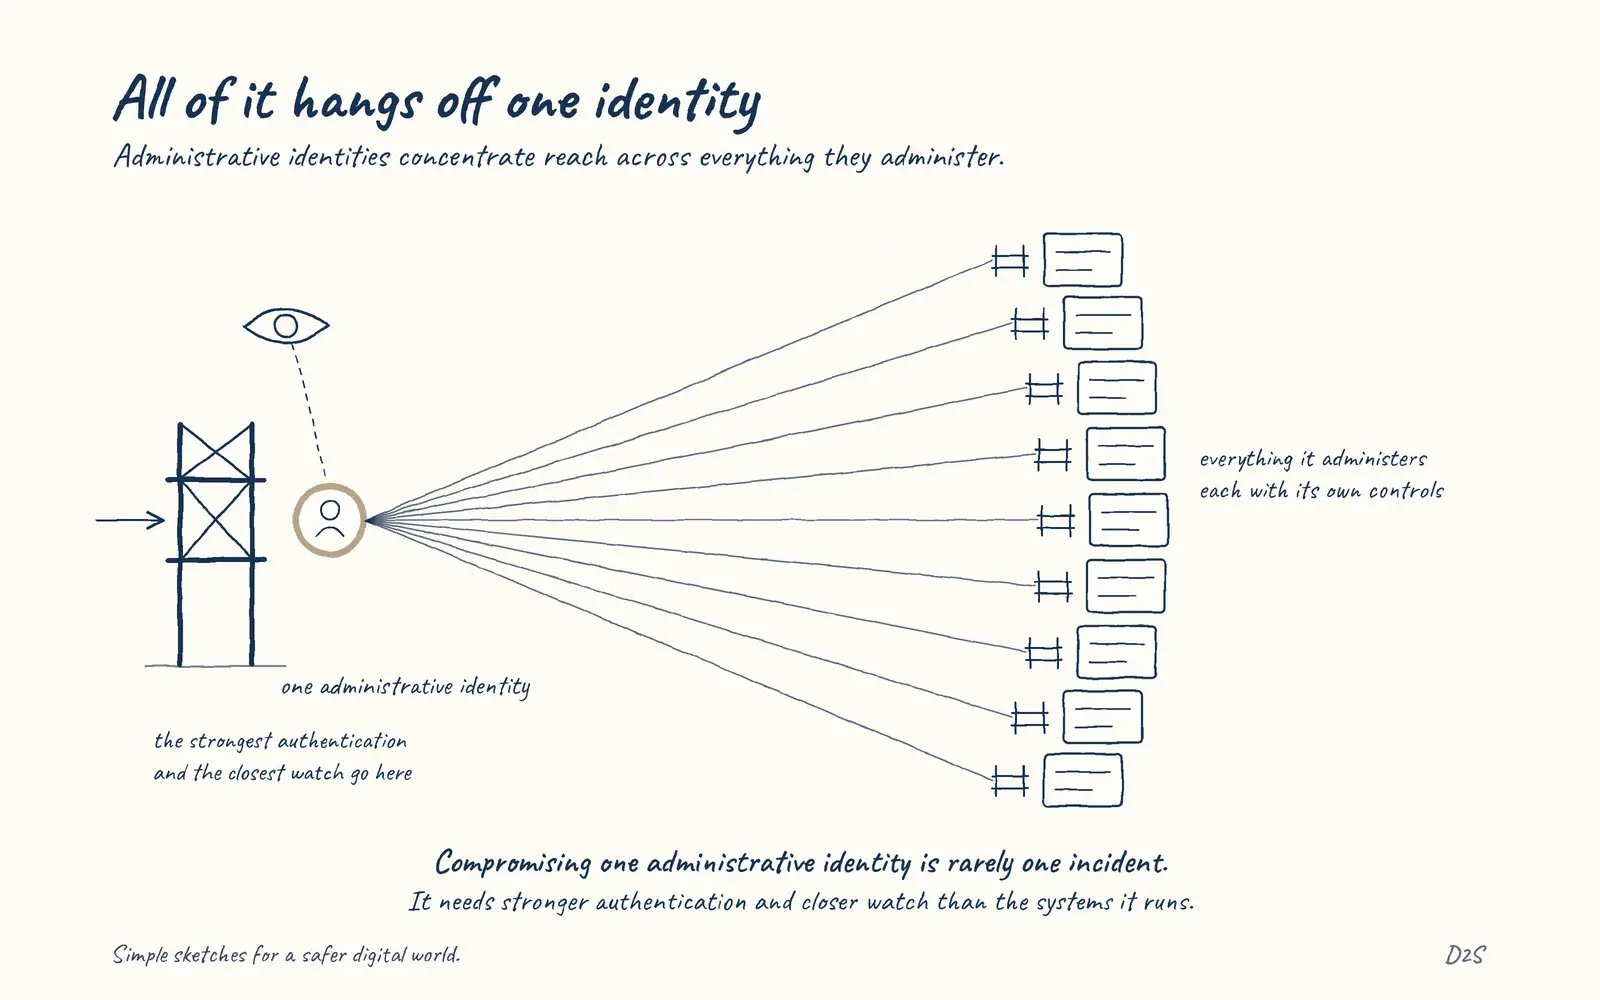 Privileged accountsAll of it hangs off one identity
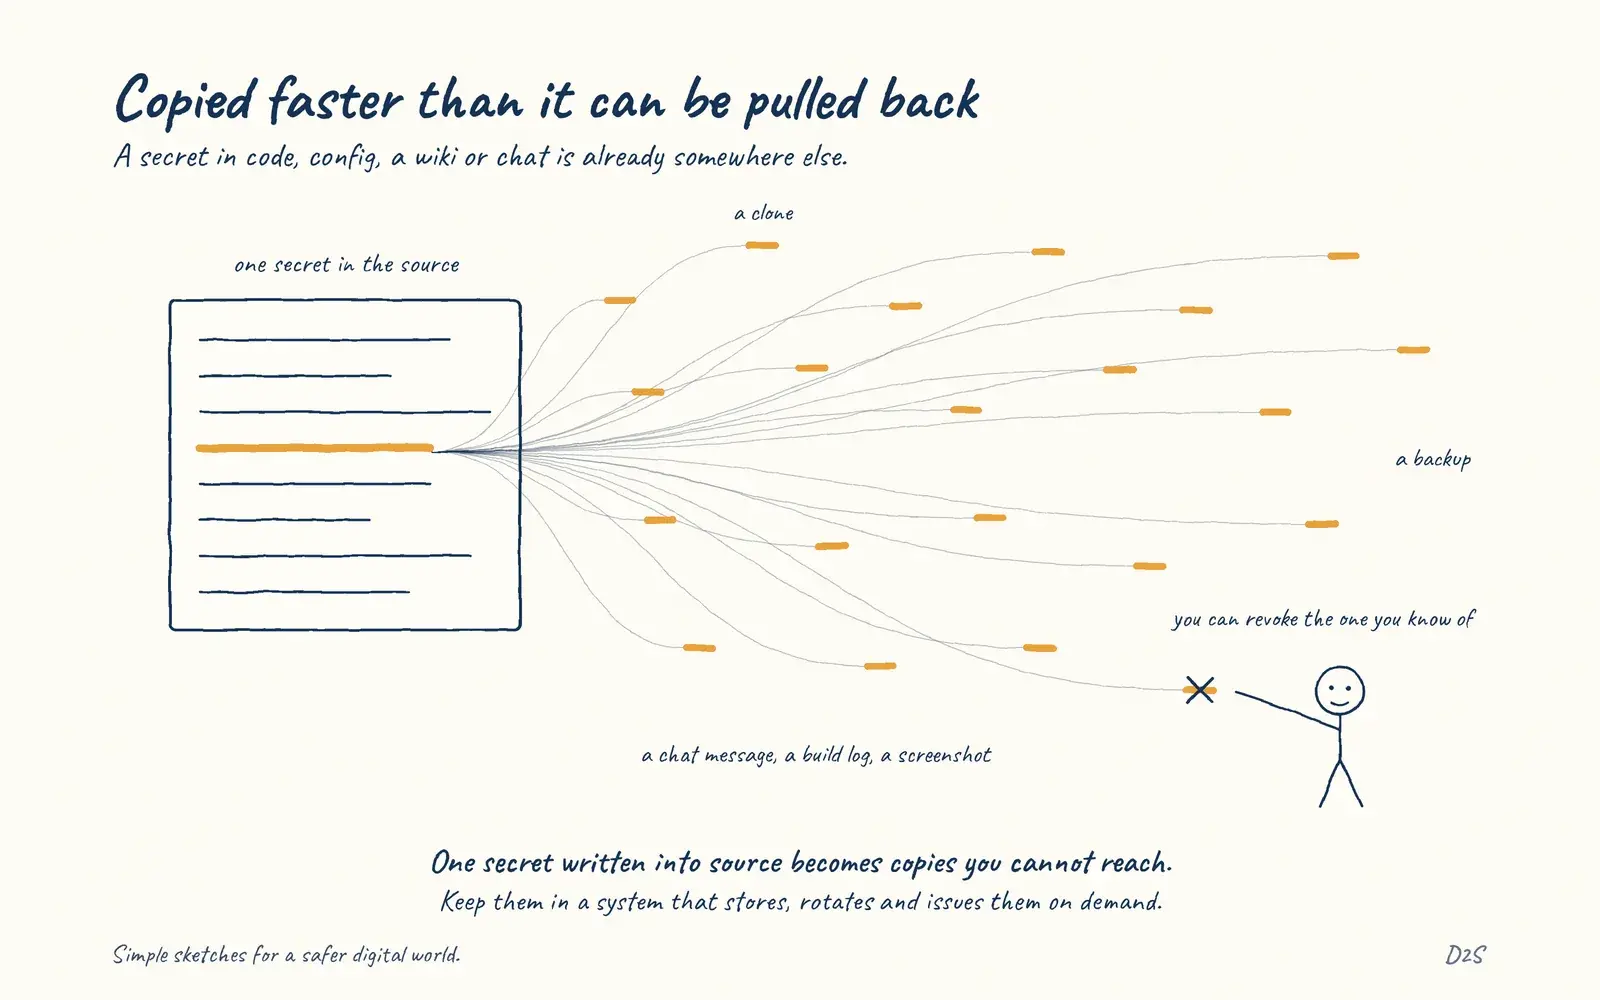 Secrets managementCopied faster than it can be pulled back
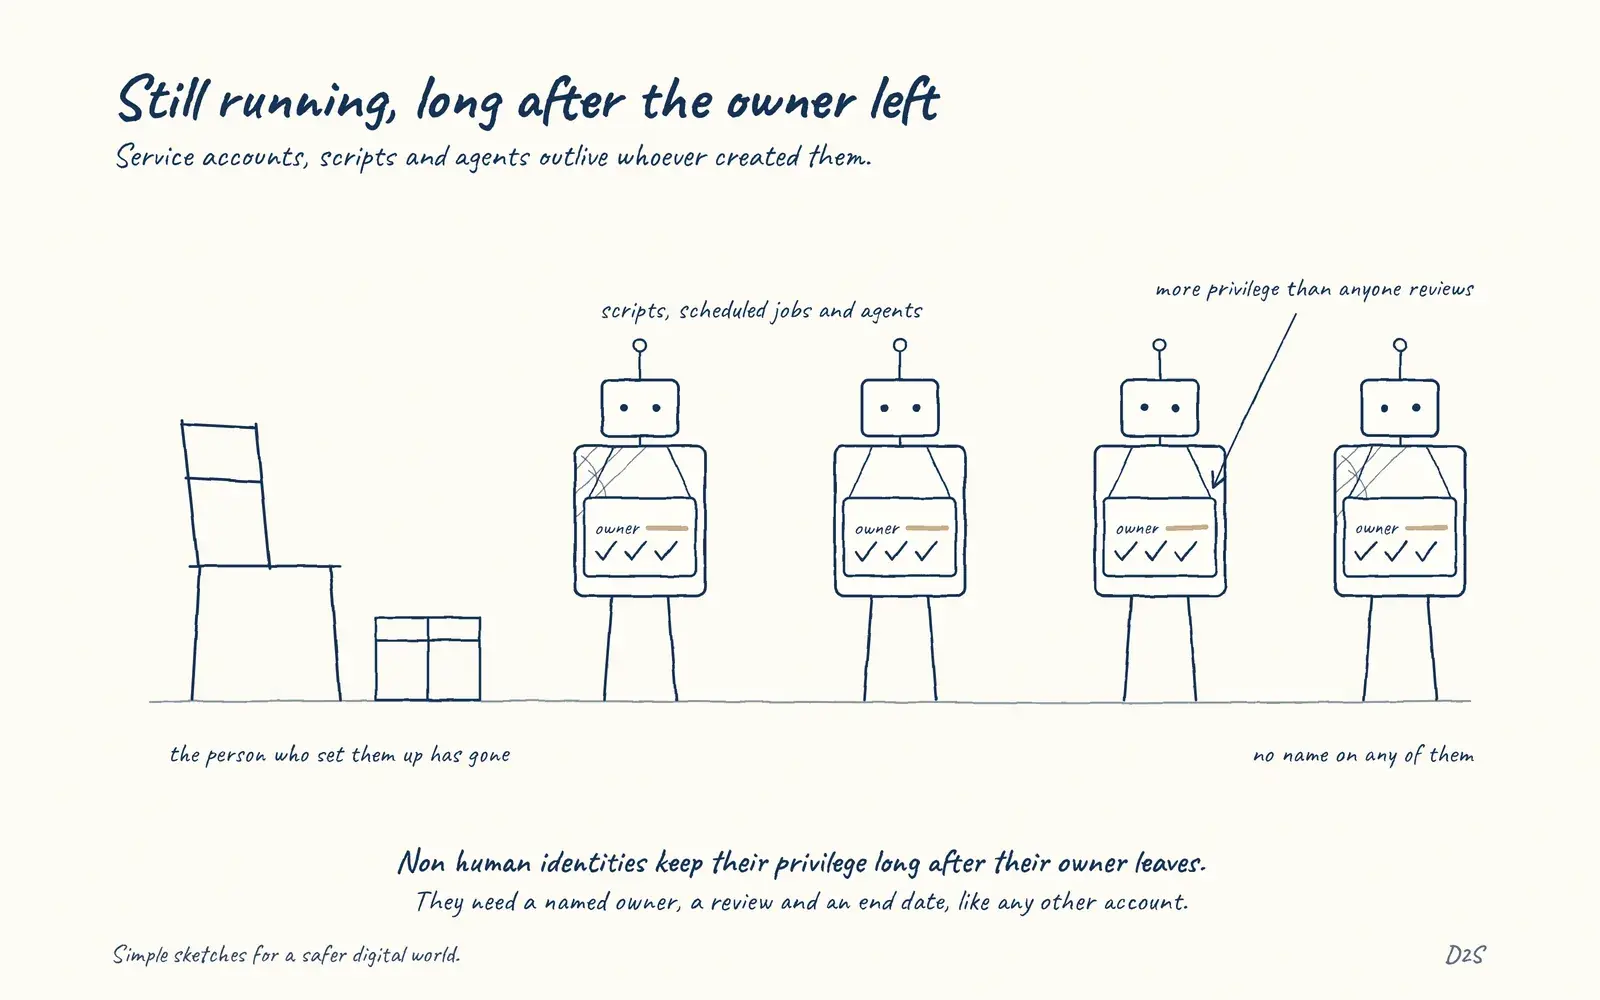 Service accountsStill running, long after the owner left
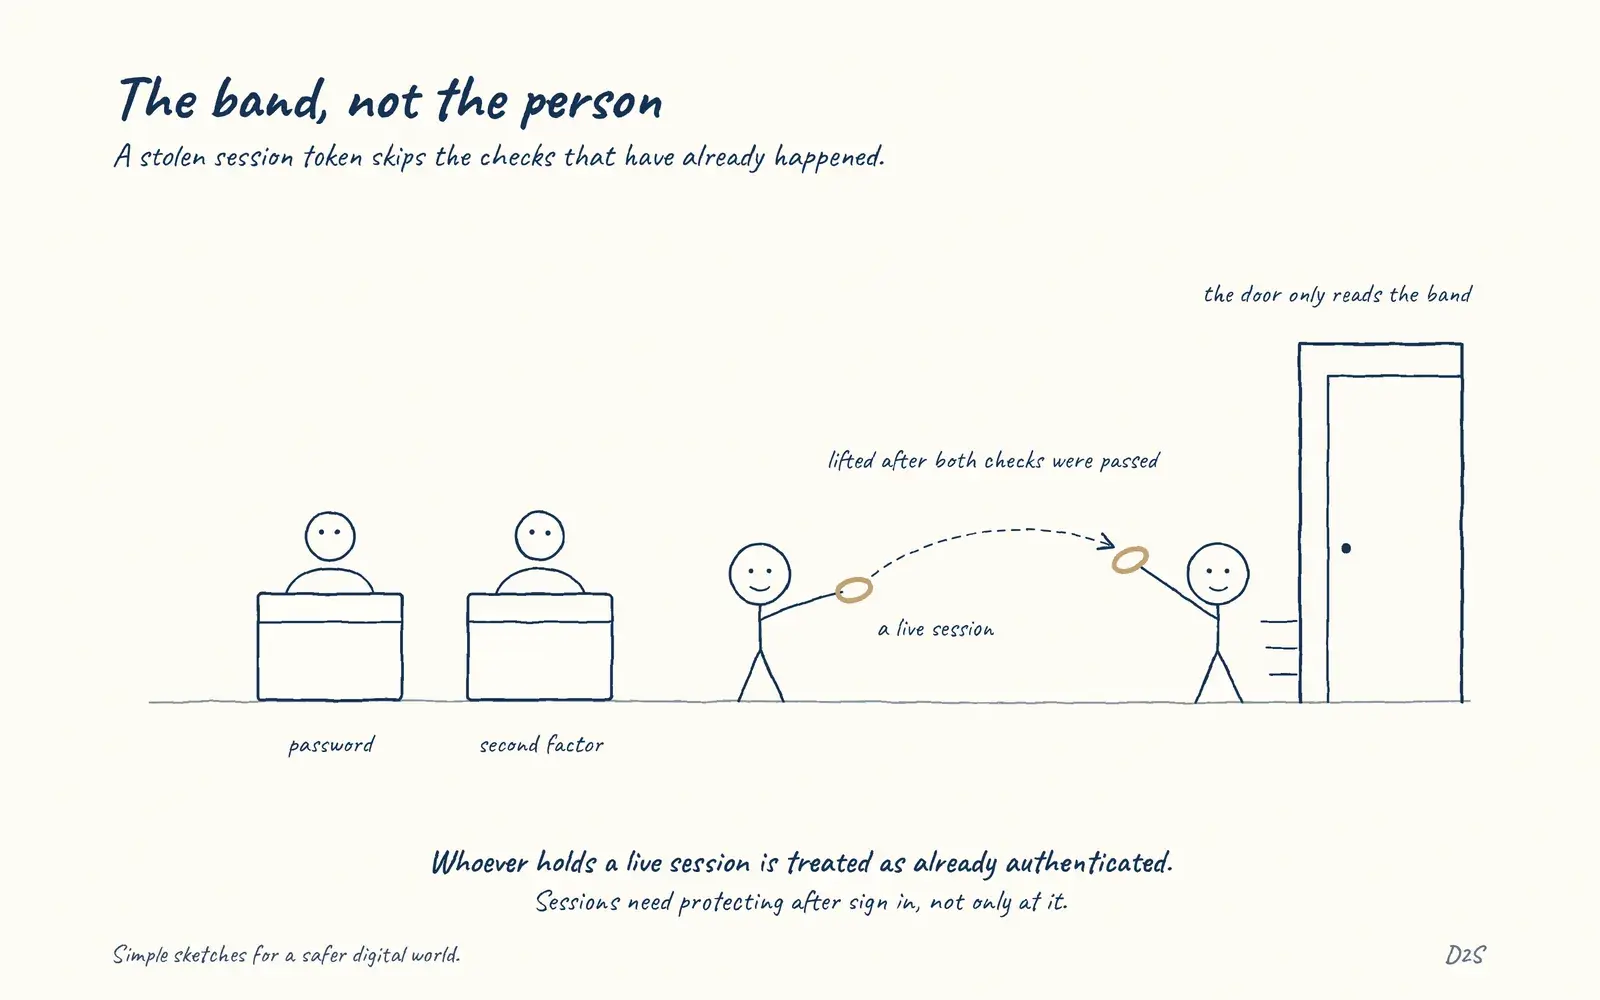 Session securityThe band, not the person
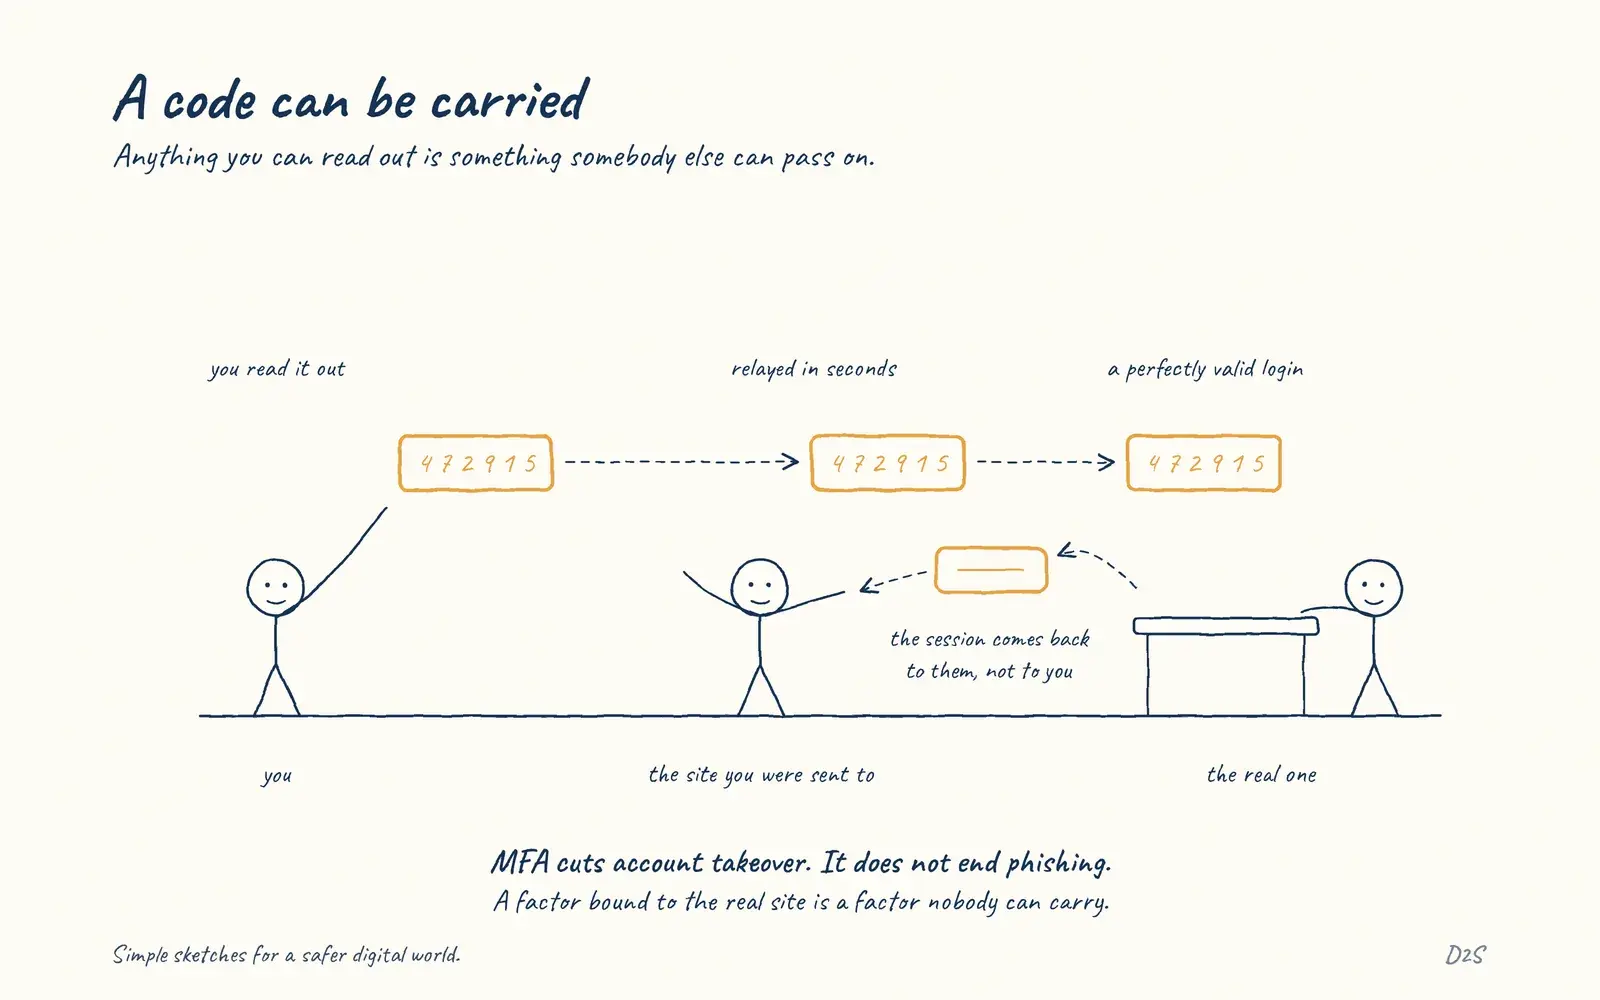 'MFA stops phishing'A code can be carried
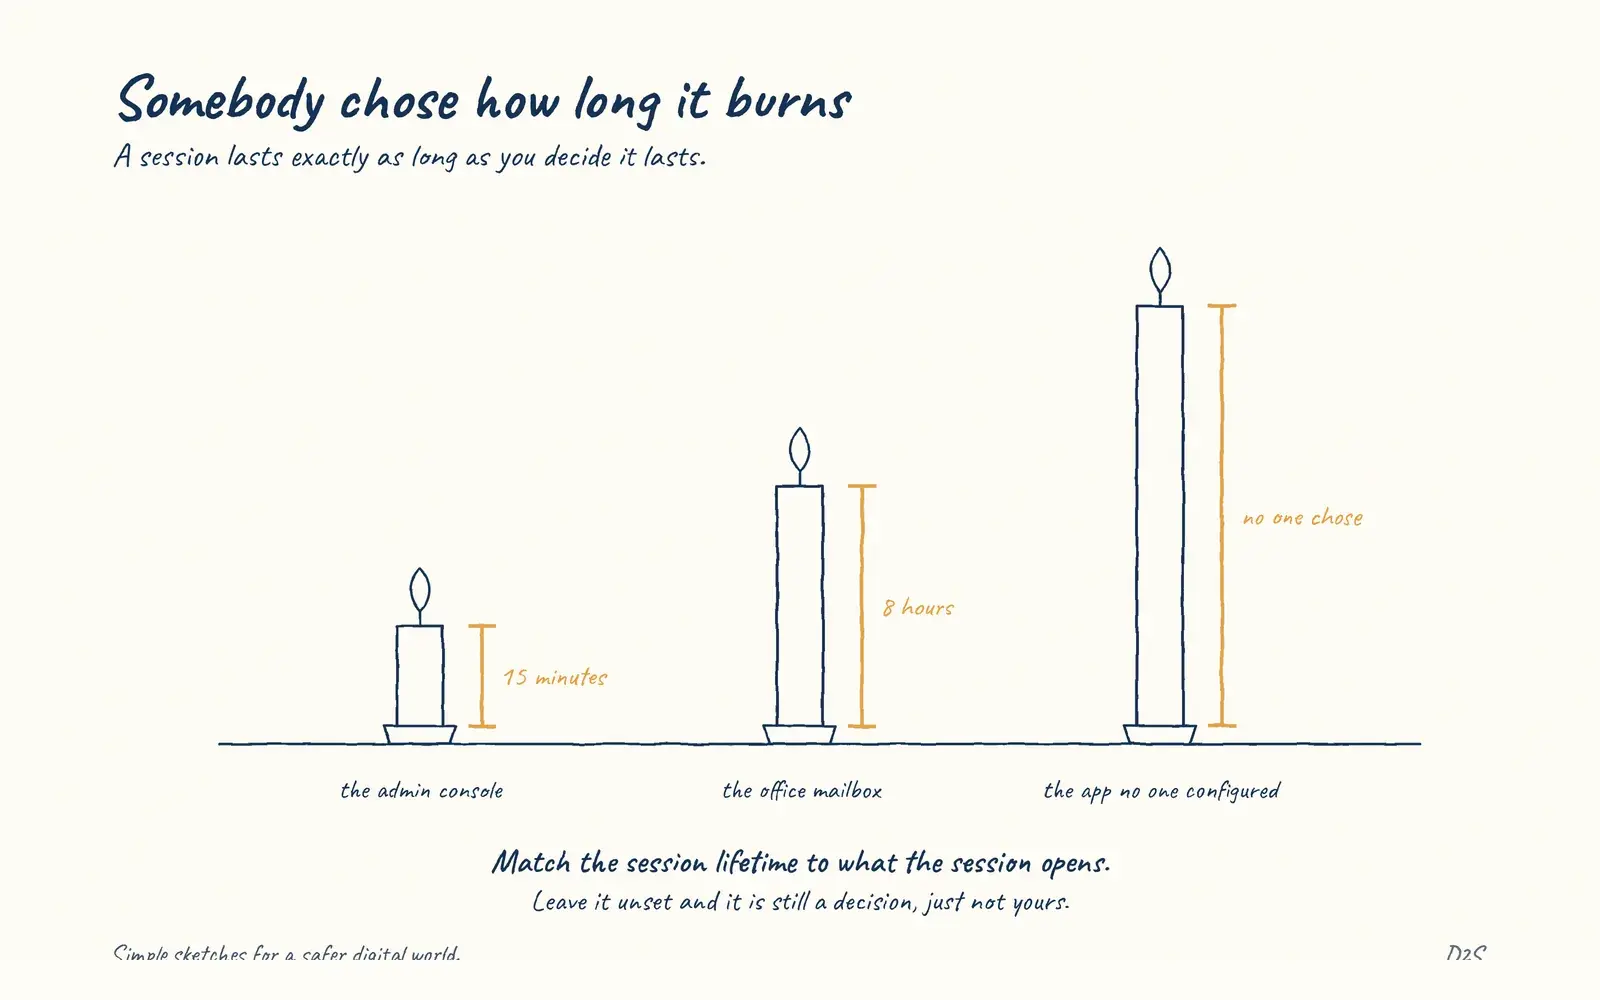 Session lifetime is a security decisionSomebody chose how long it burns
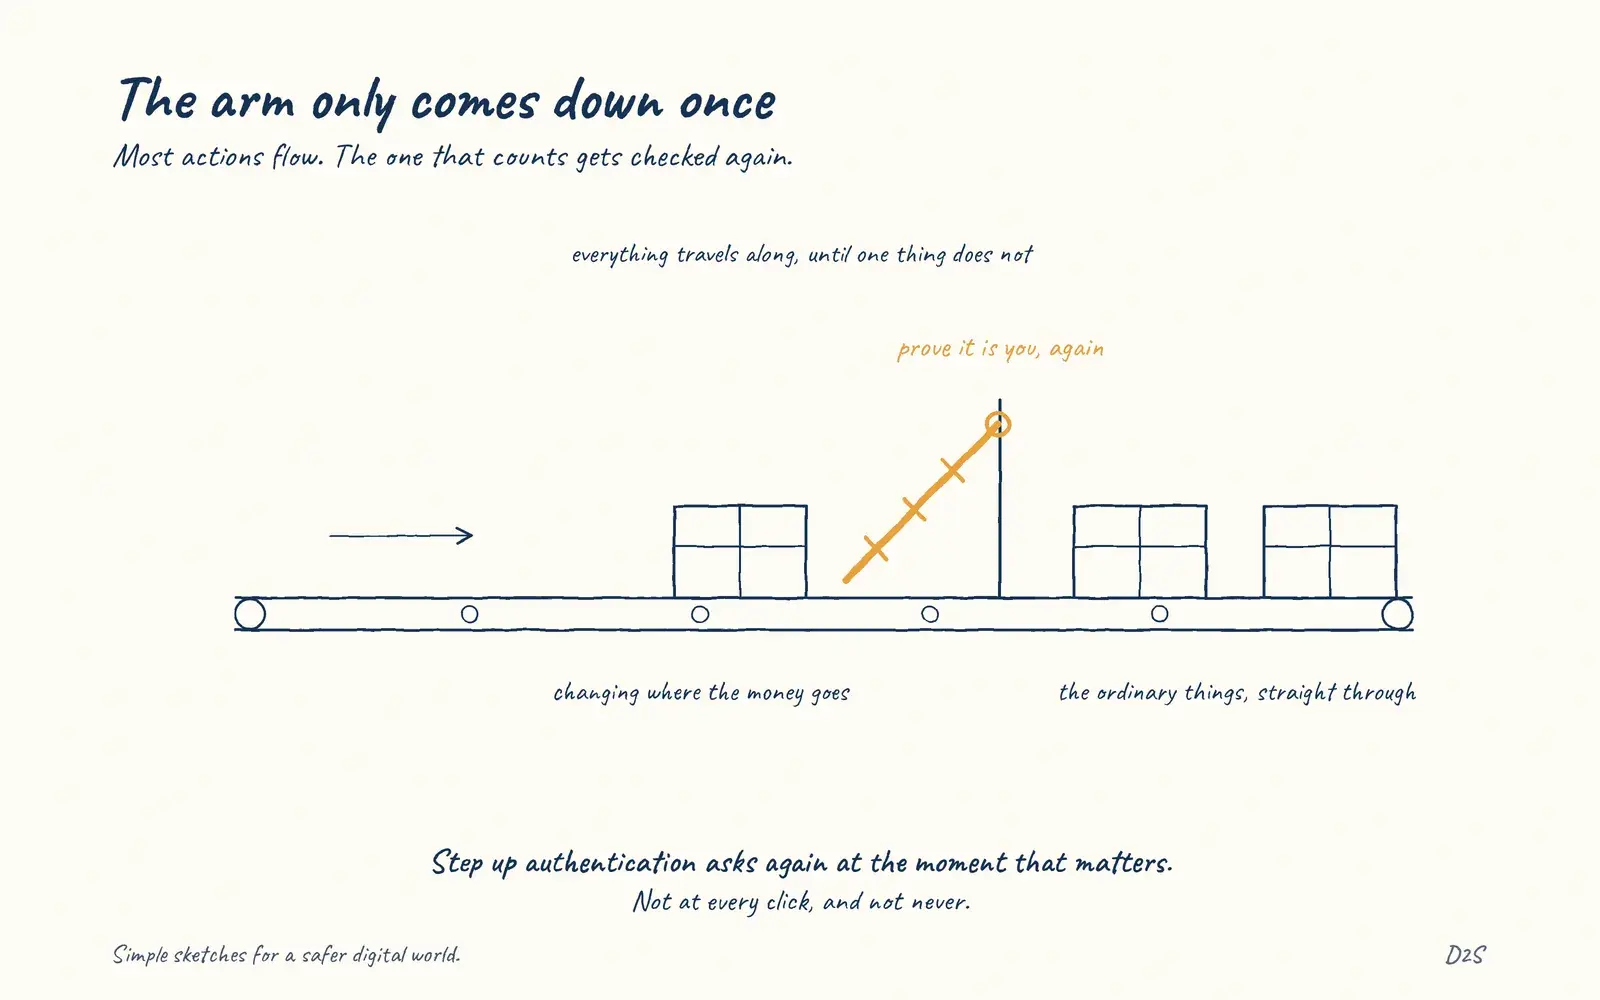 Step-up authentication protects sensitive momentsThe arm only comes down once
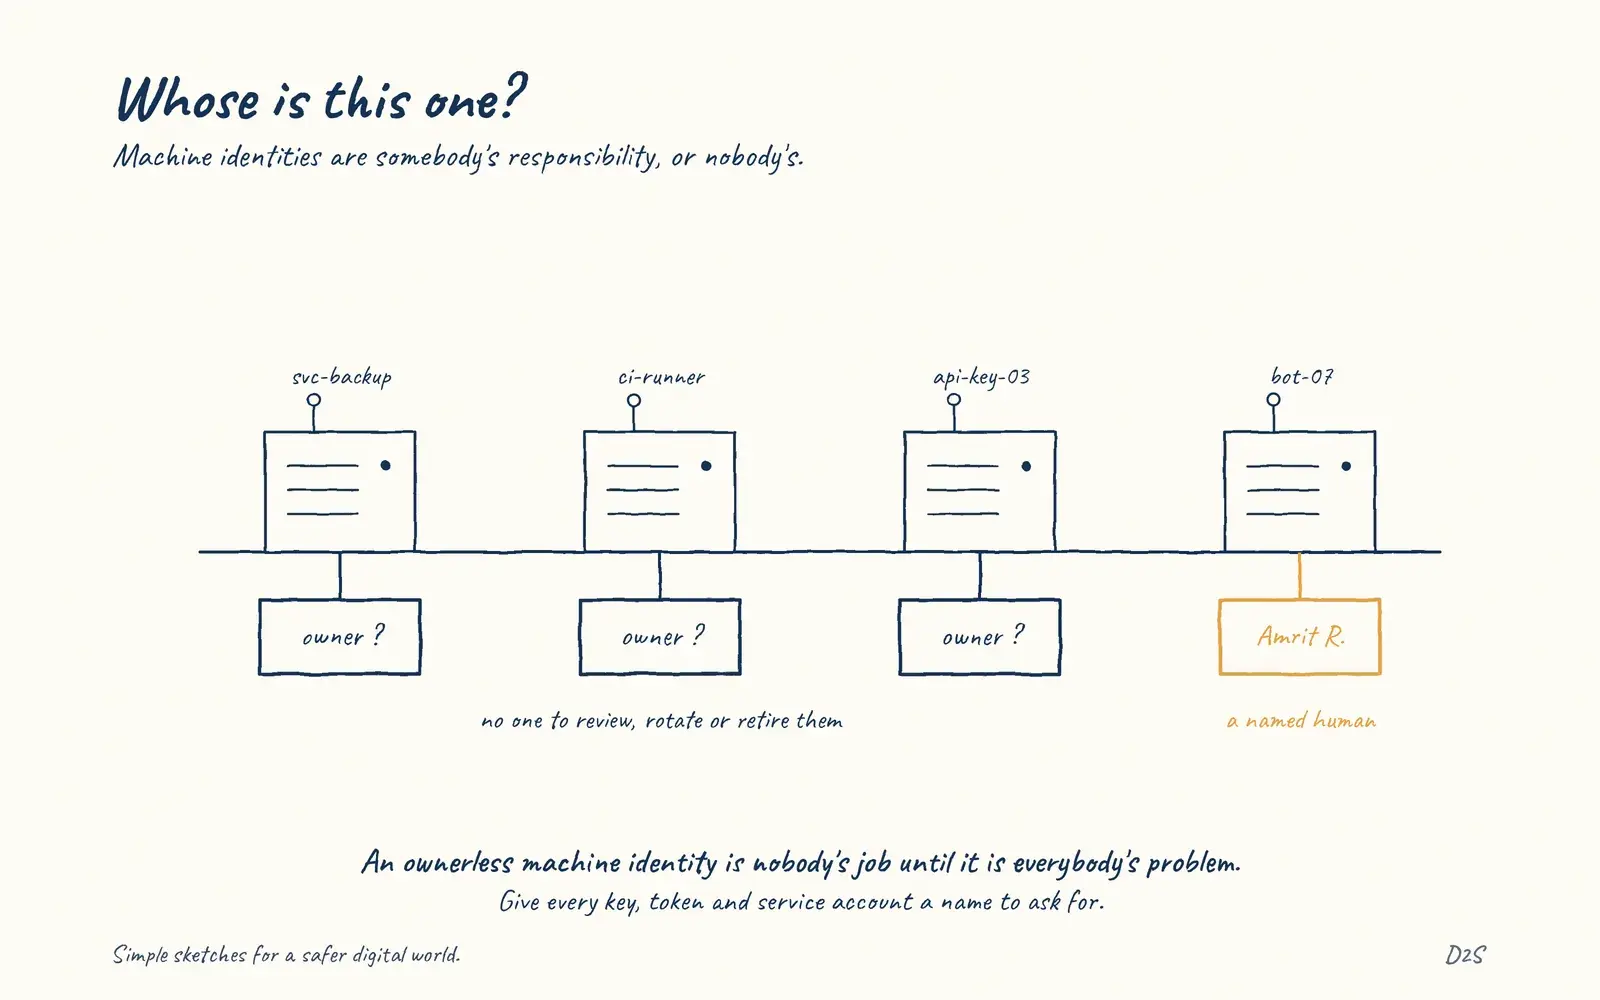 Machine identities need owners tooWhose is this one? Machine identities are somebody's responsibility, or nobody's
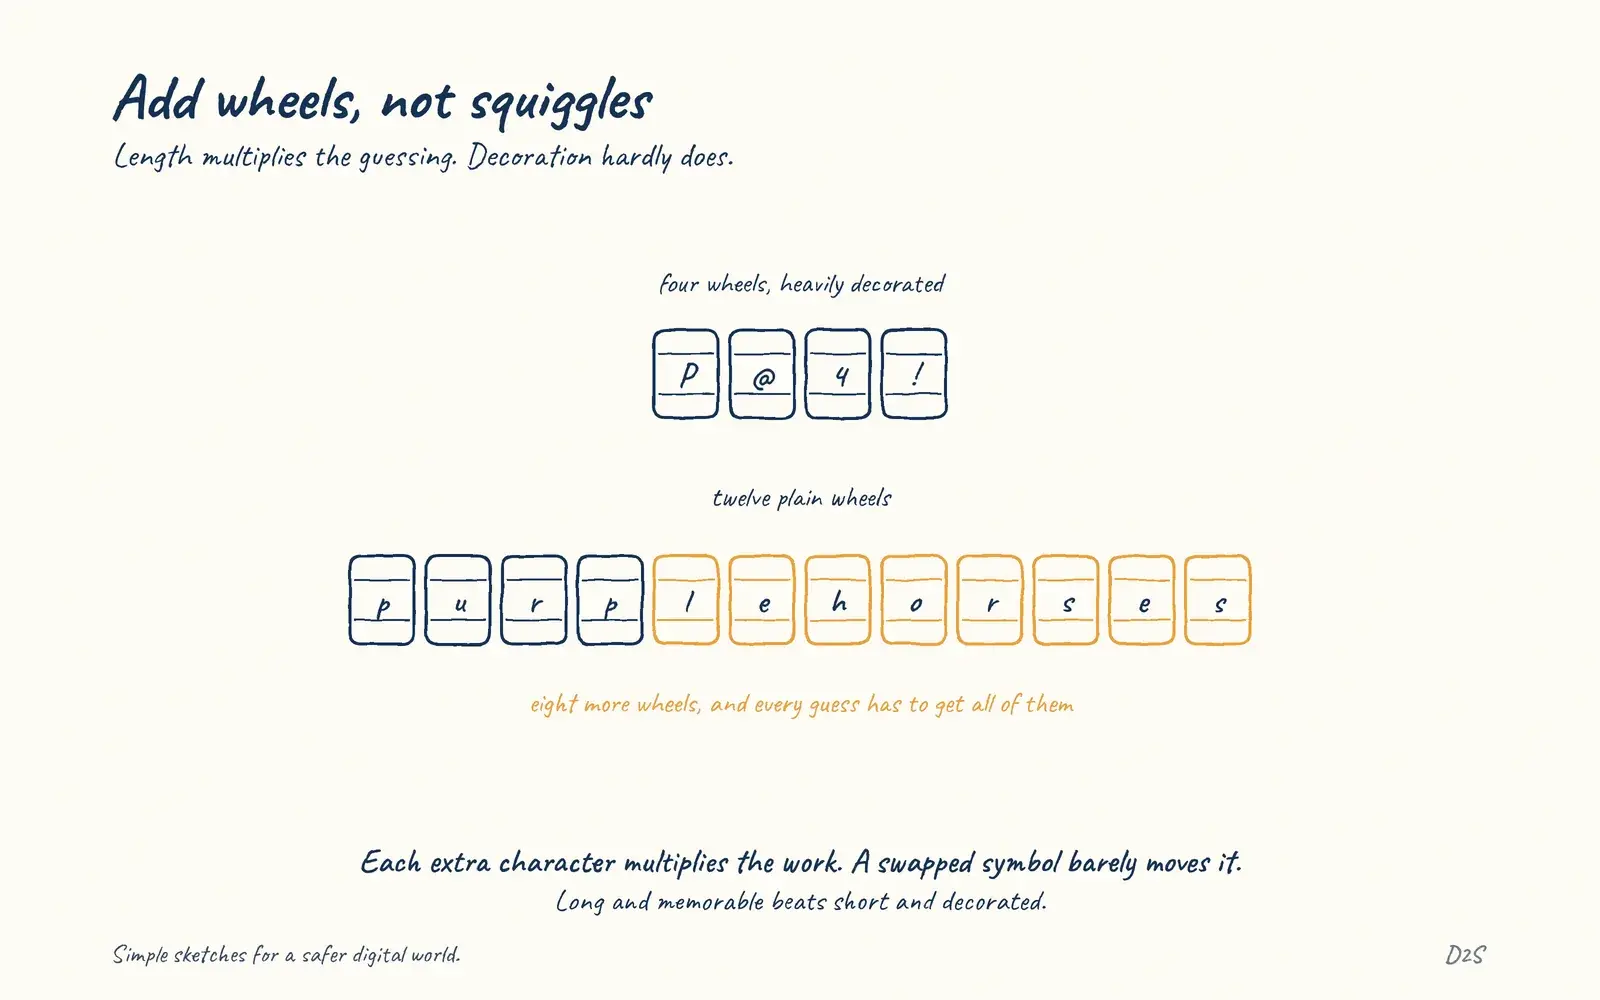 Password length beats decorative complexityAdd wheels, not squiggles
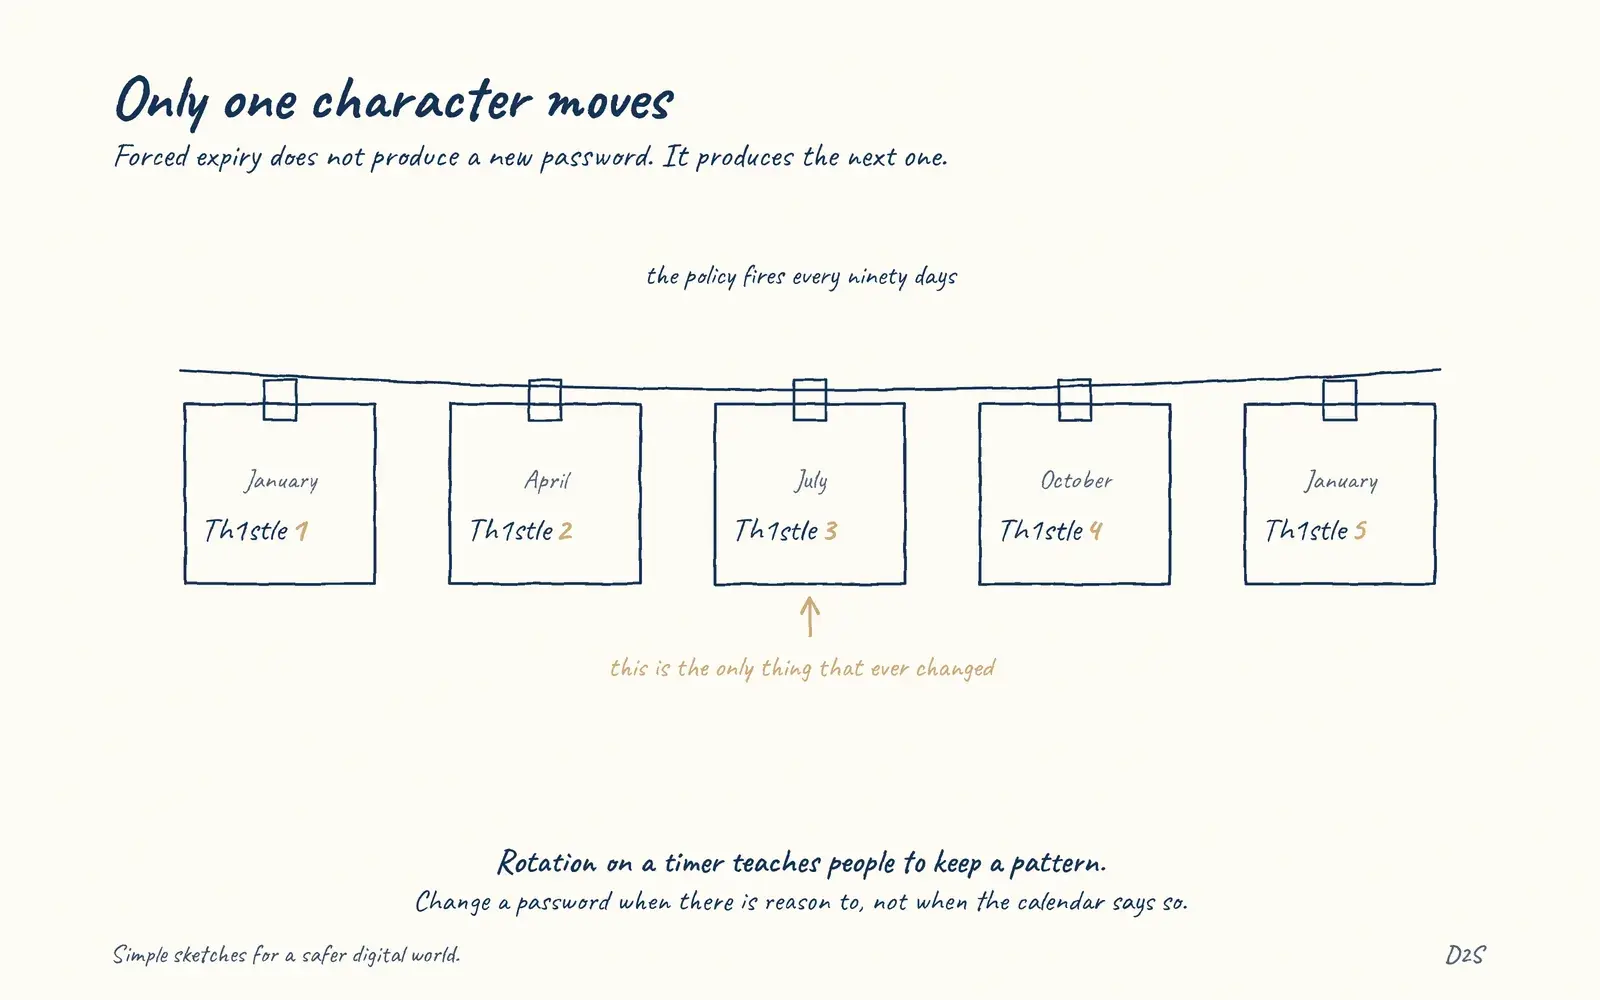 Forced rotation can create predictable passwordsOnly one character moves
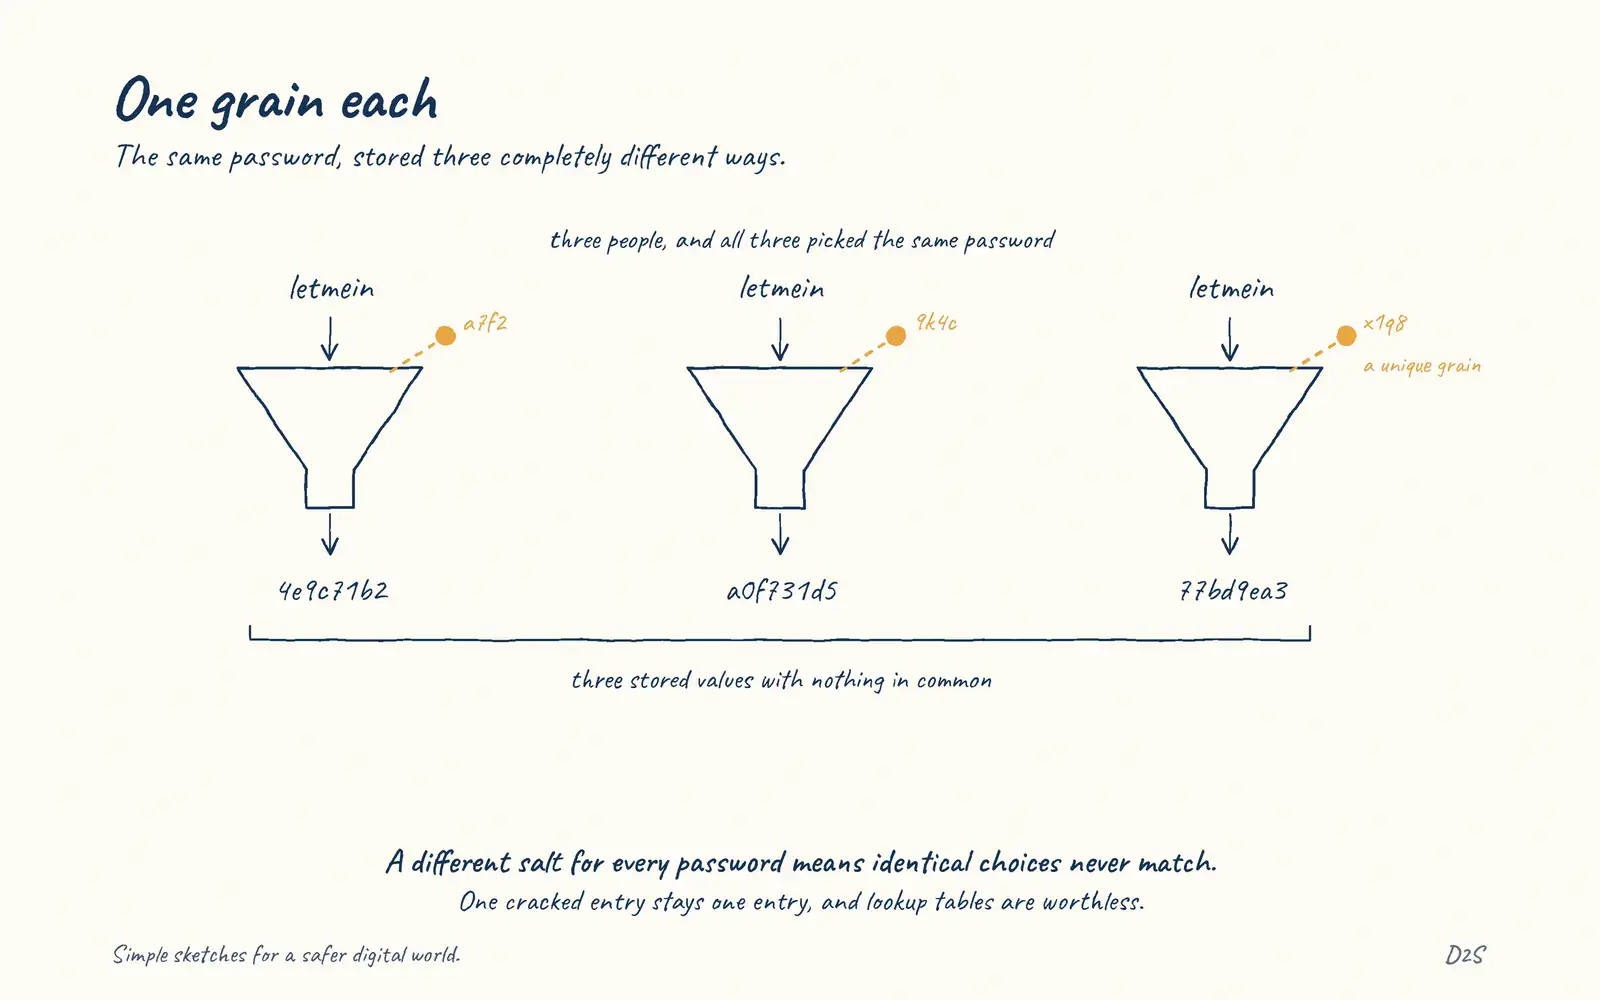 Salts make identical passwords look differentOne grain each
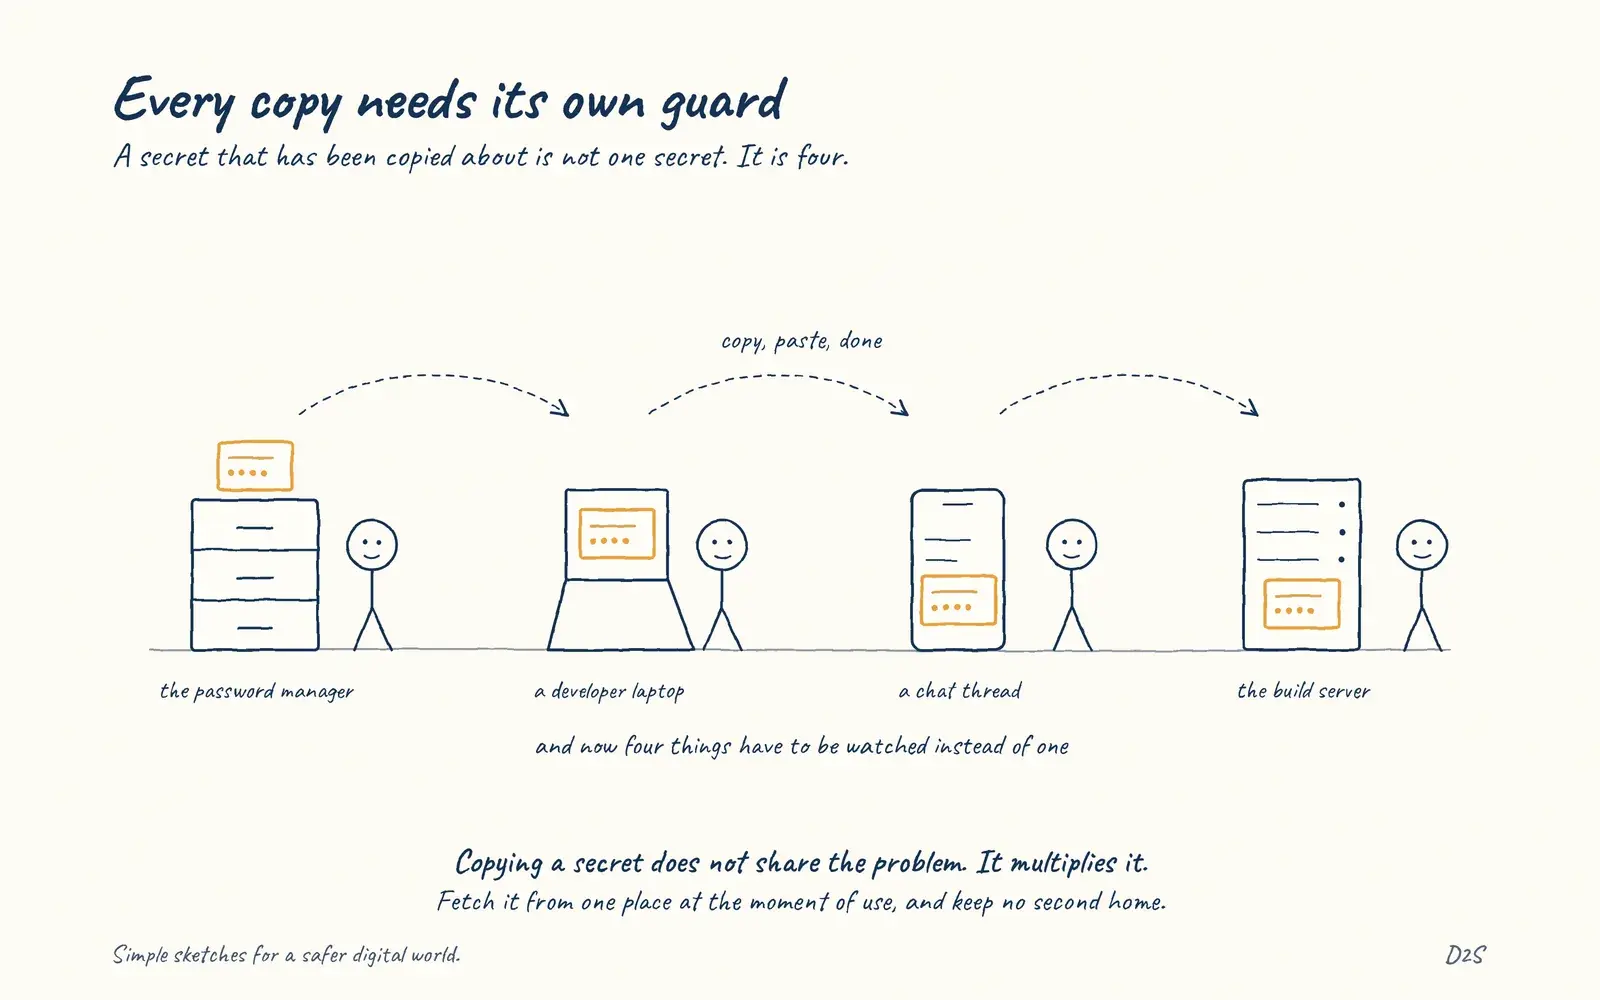 Every secret copy creates another secret to protectEvery copy needs its own guard
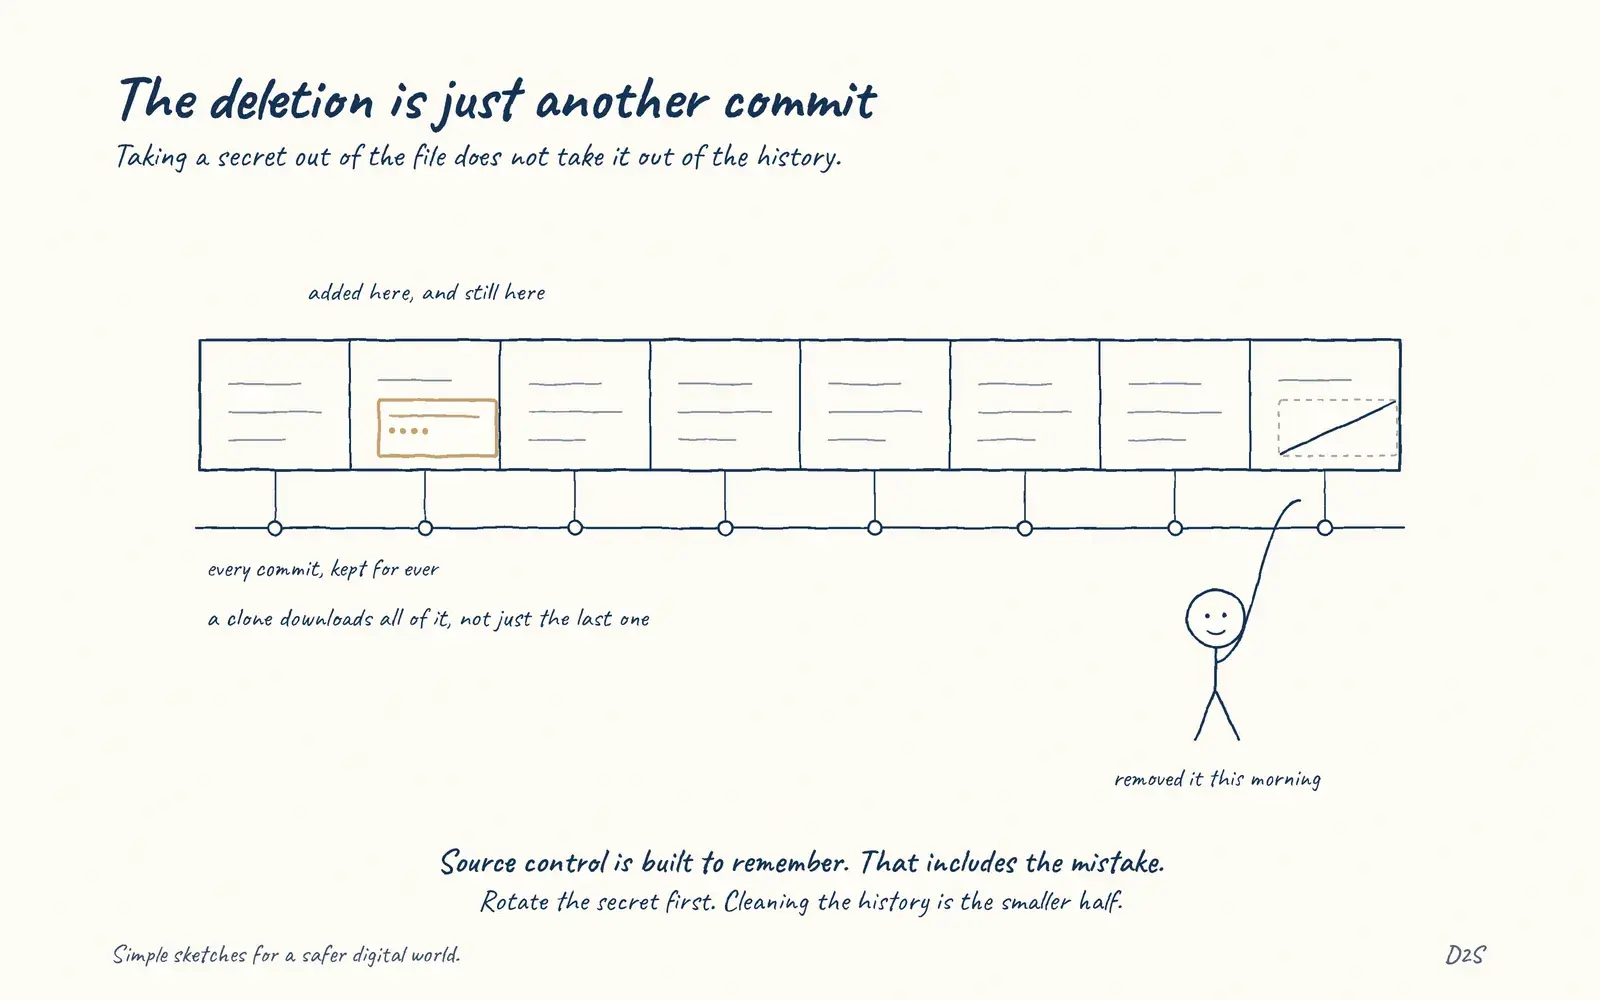 Secrets in source control have a long memoryThe deletion is just another commit
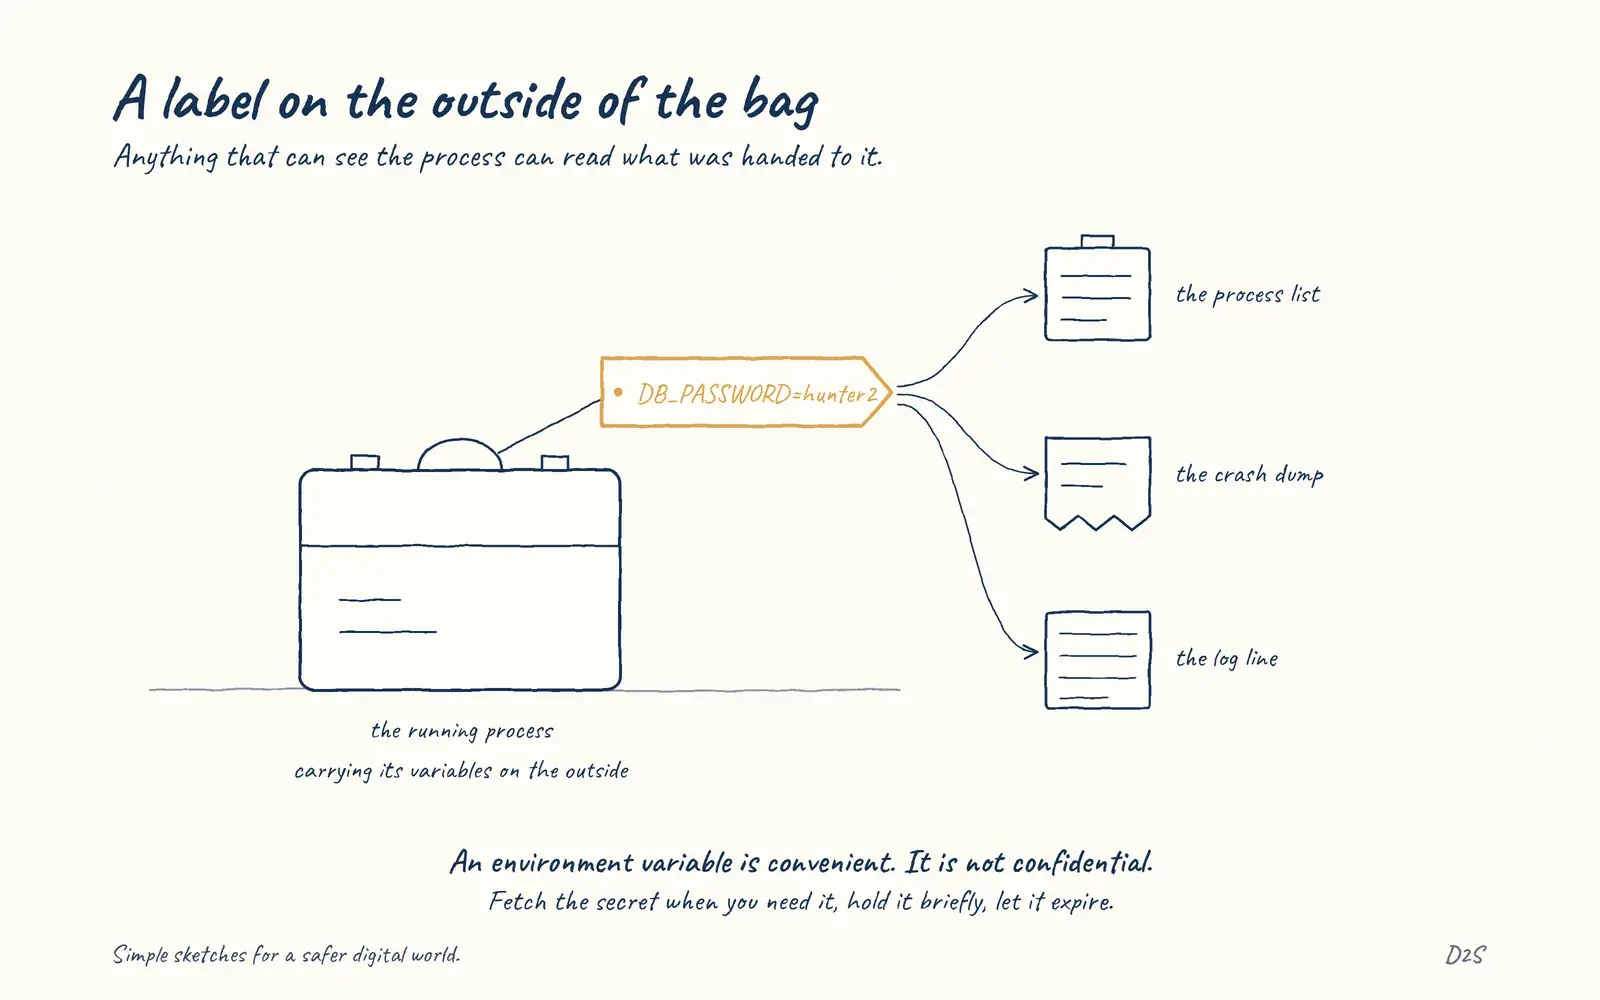 Environment variables are not secret vaultsA label on the outside of the bag
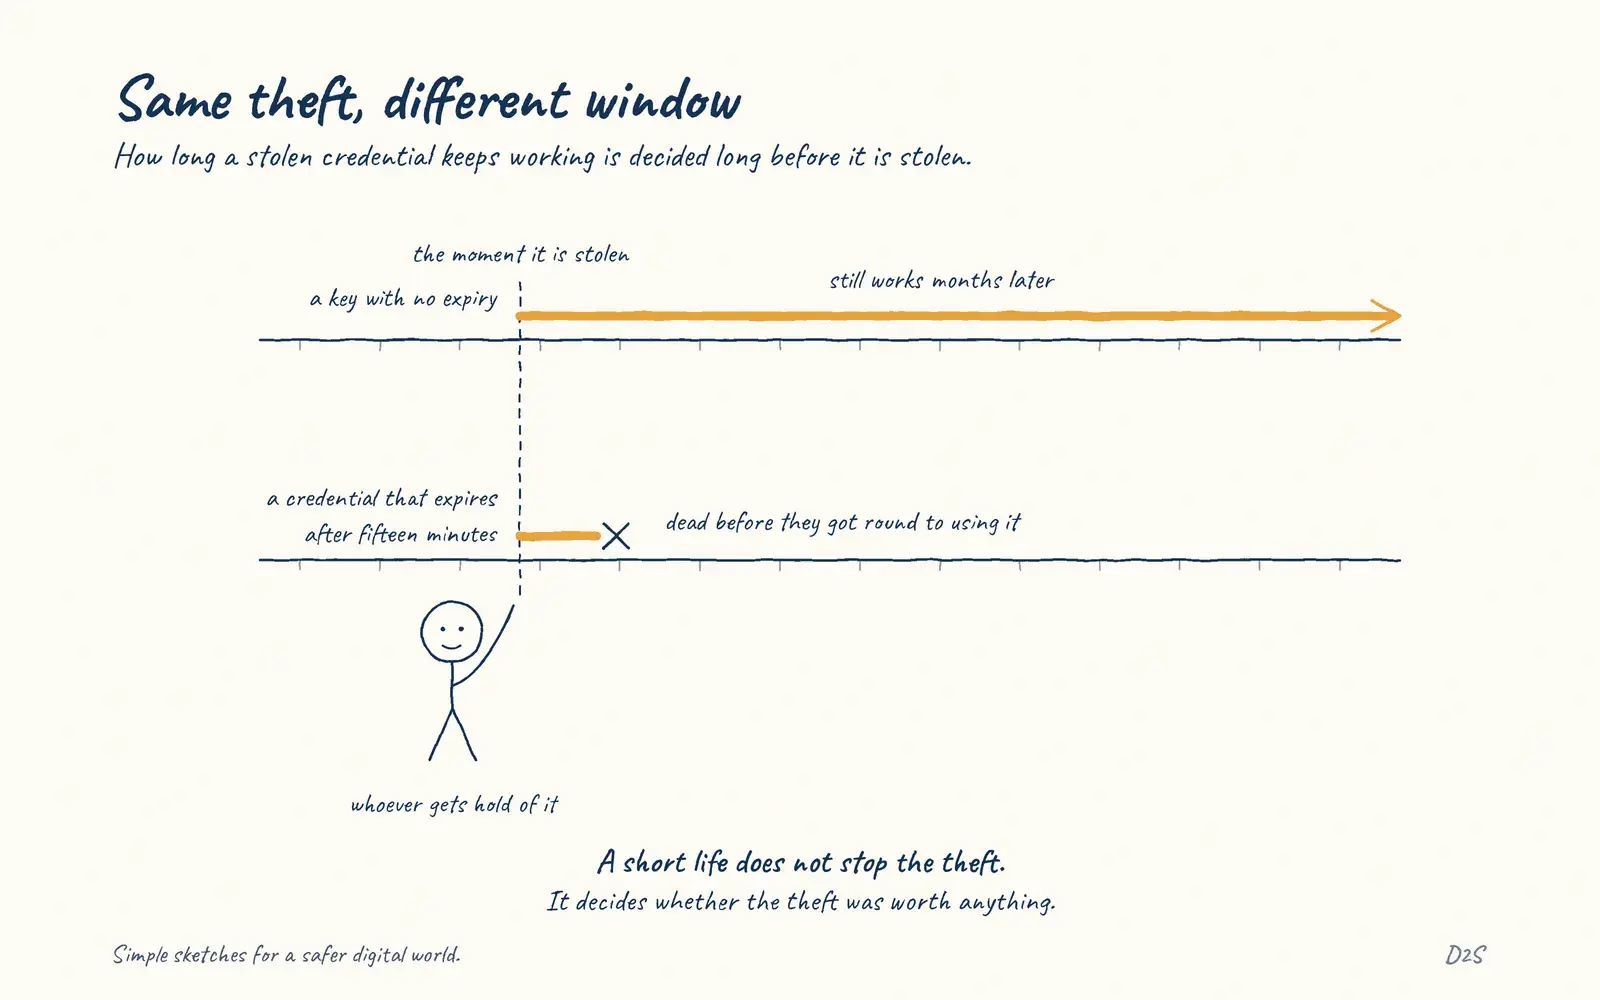 Temporary credentials shrink the theft windowSame theft, different window
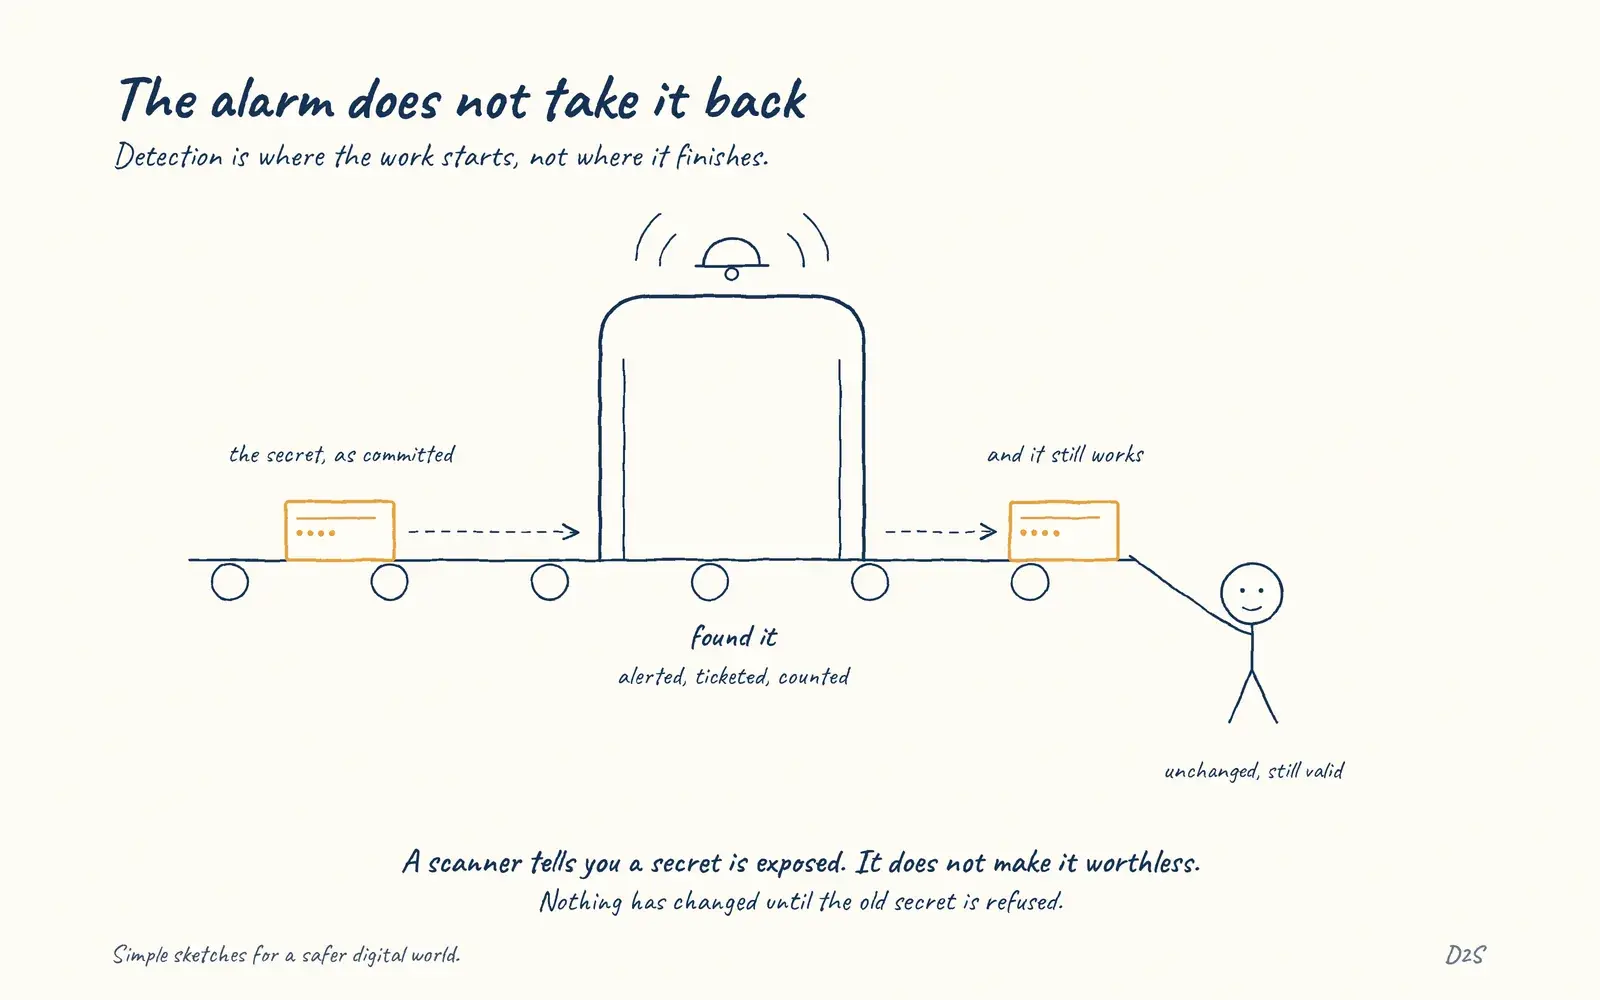 Secret scanning finds exposure, not erasureThe alarm does not take it back
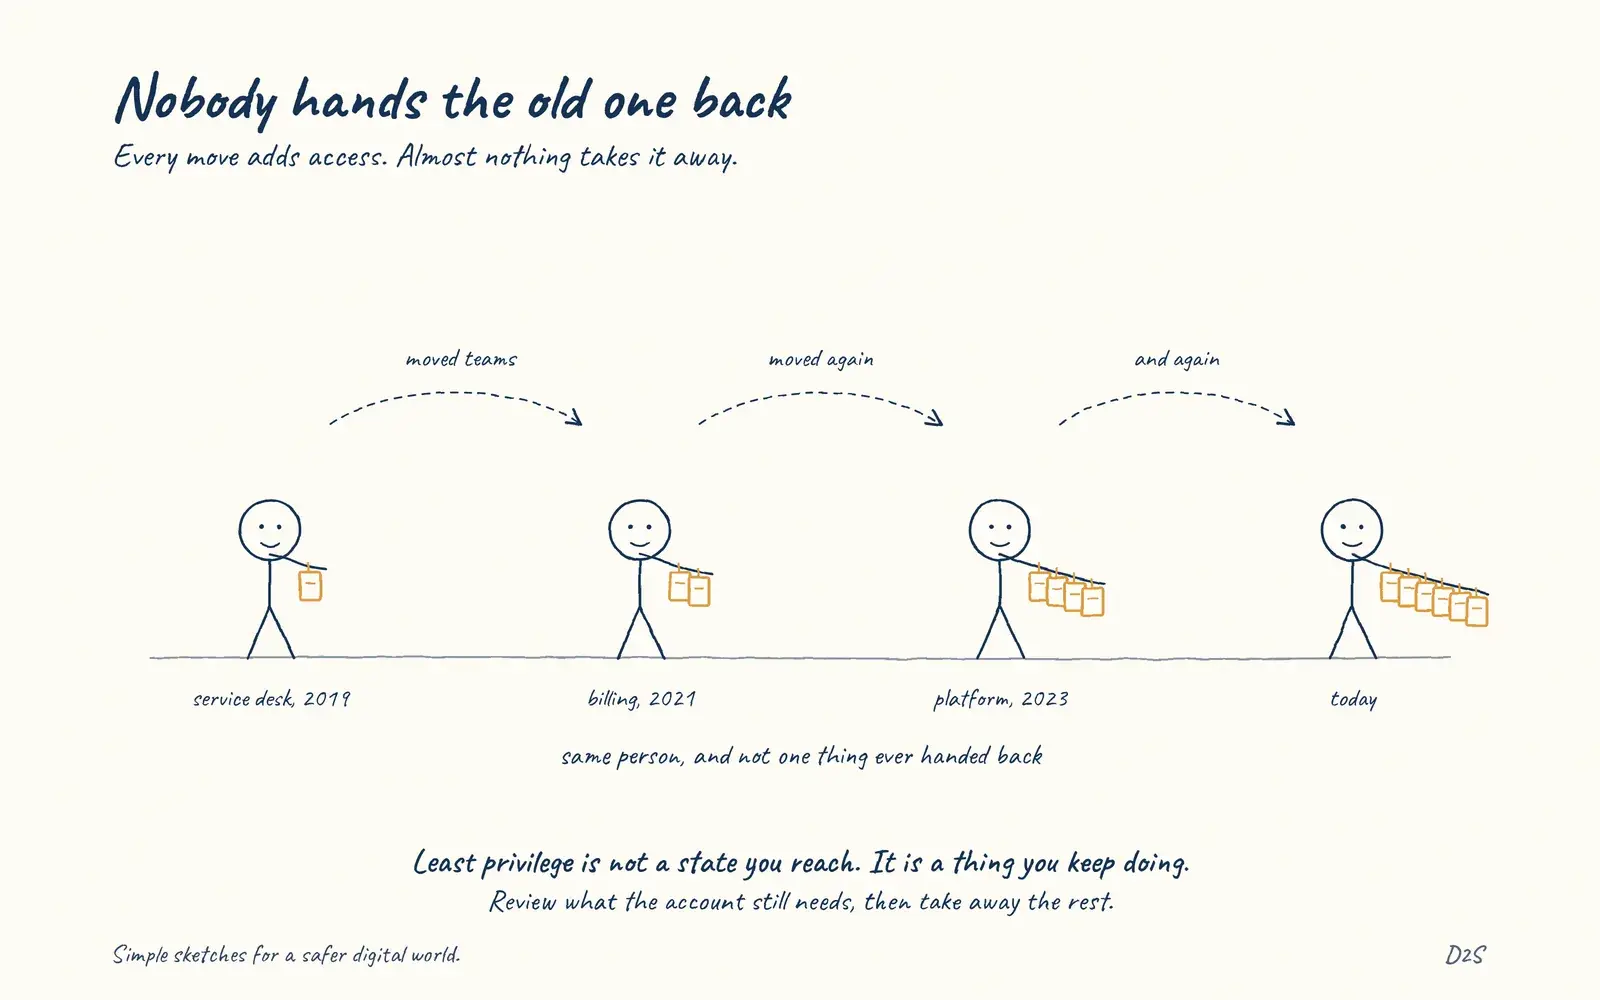 Least privilege decays over timeNobody hands the old one back
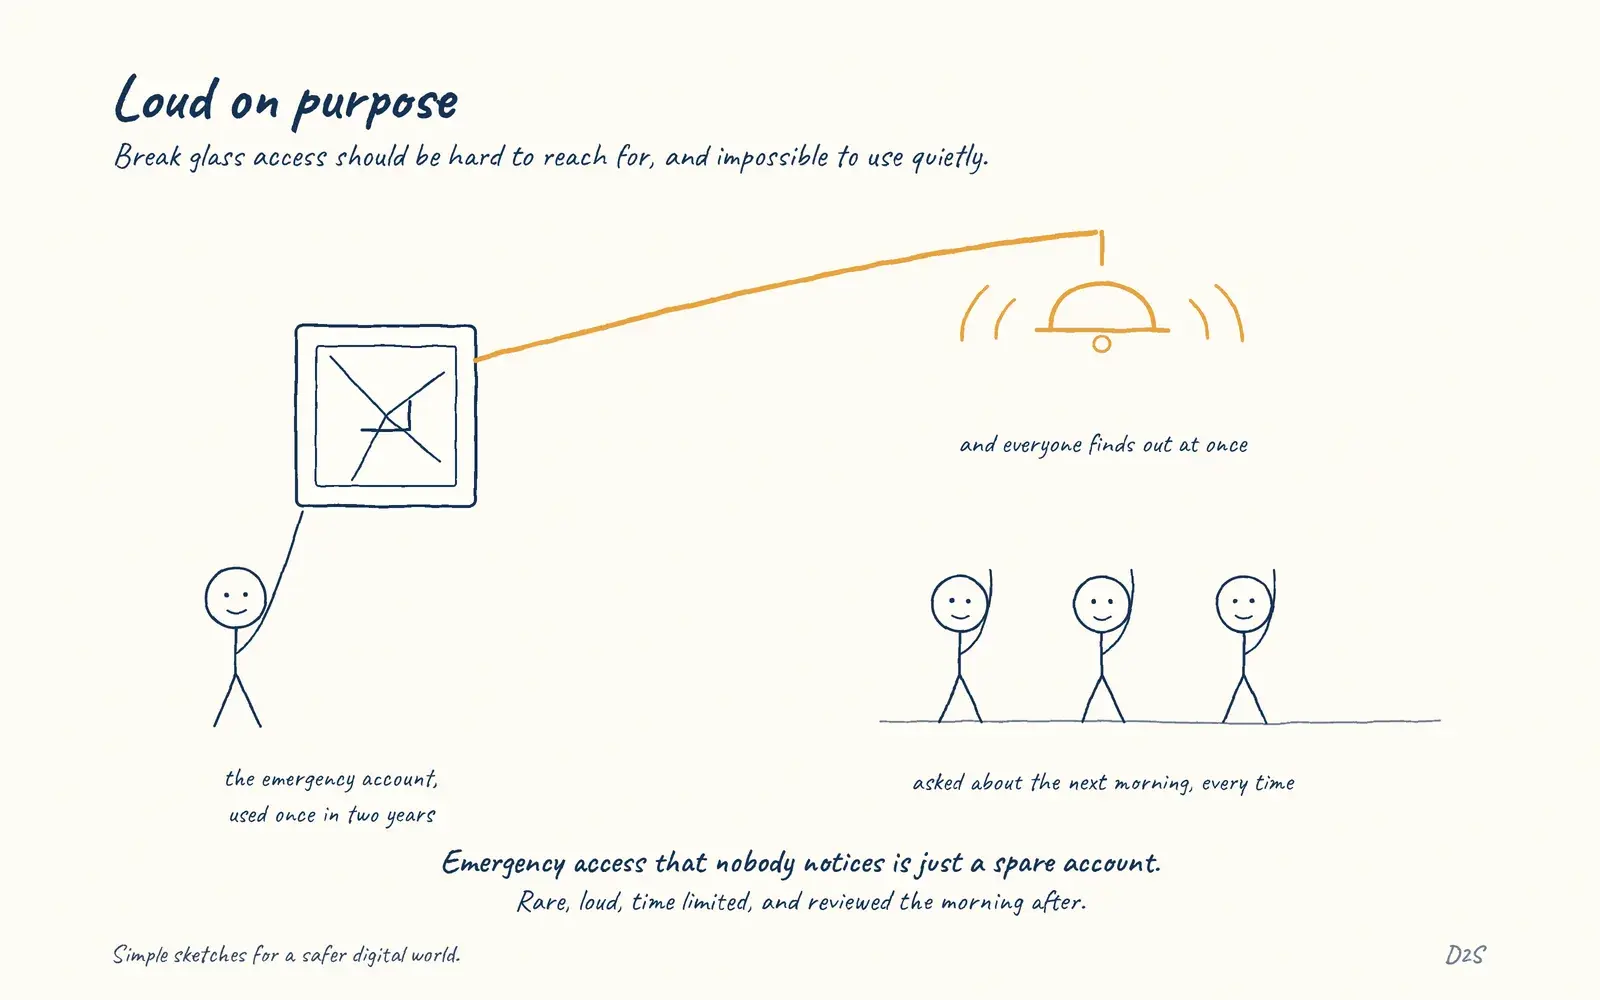 Break-glass access should be exceptional and noisyLoud on purpose
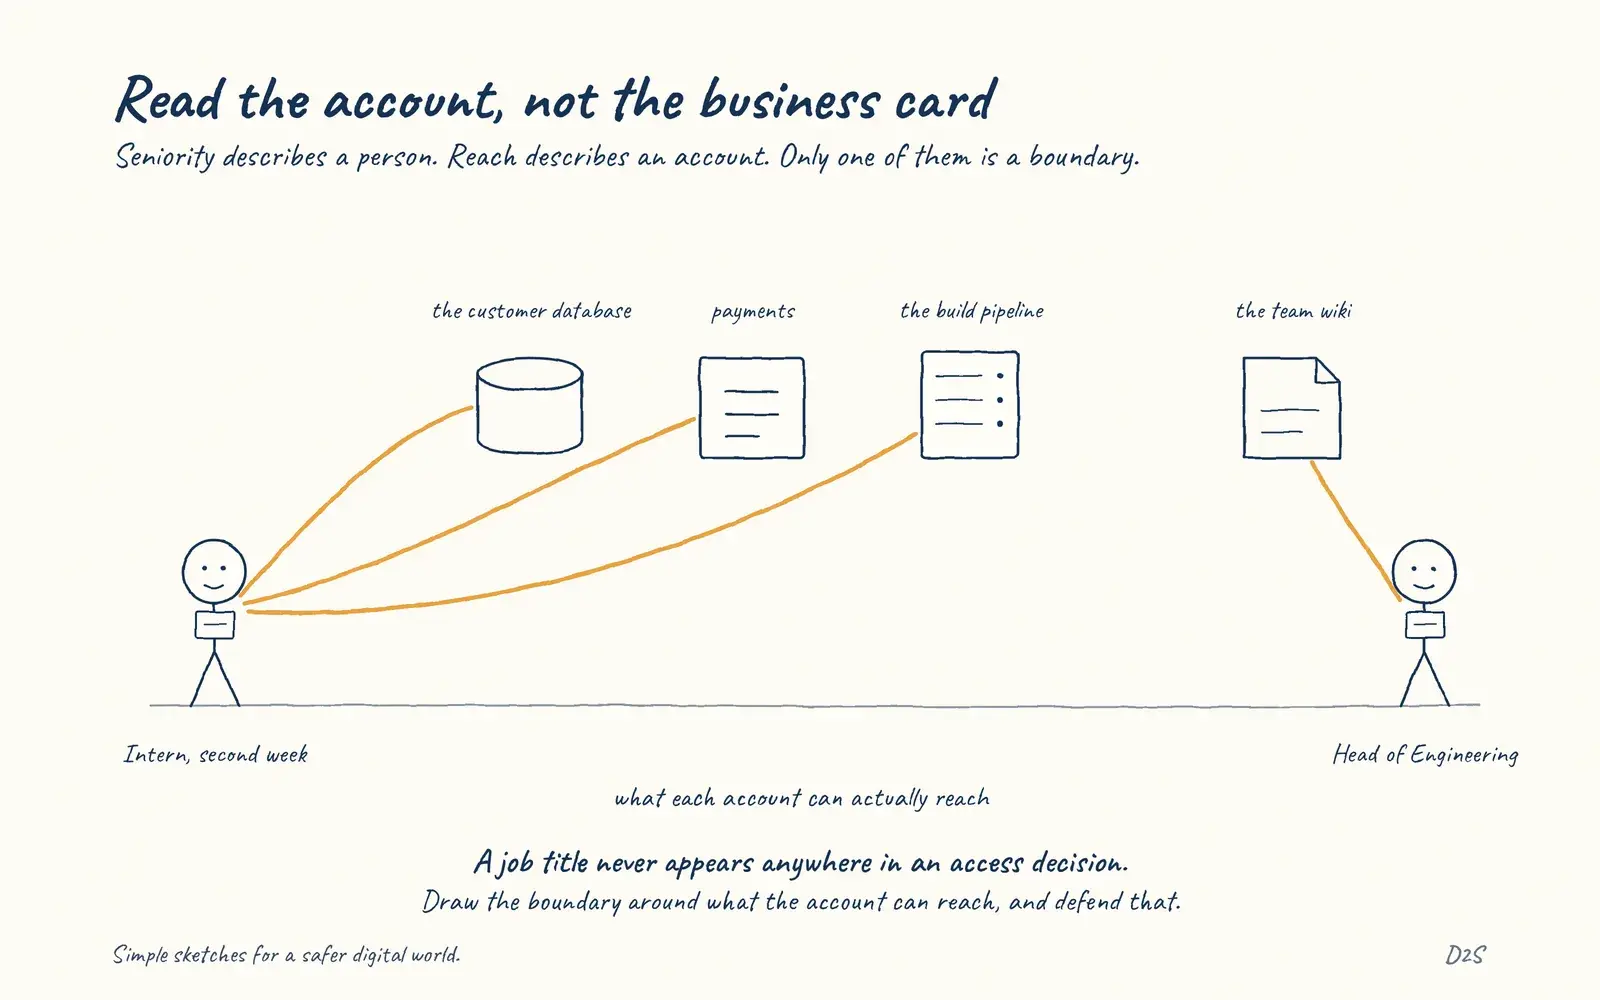 Privilege boundaries matter more than job titlesRead the account, not the business card
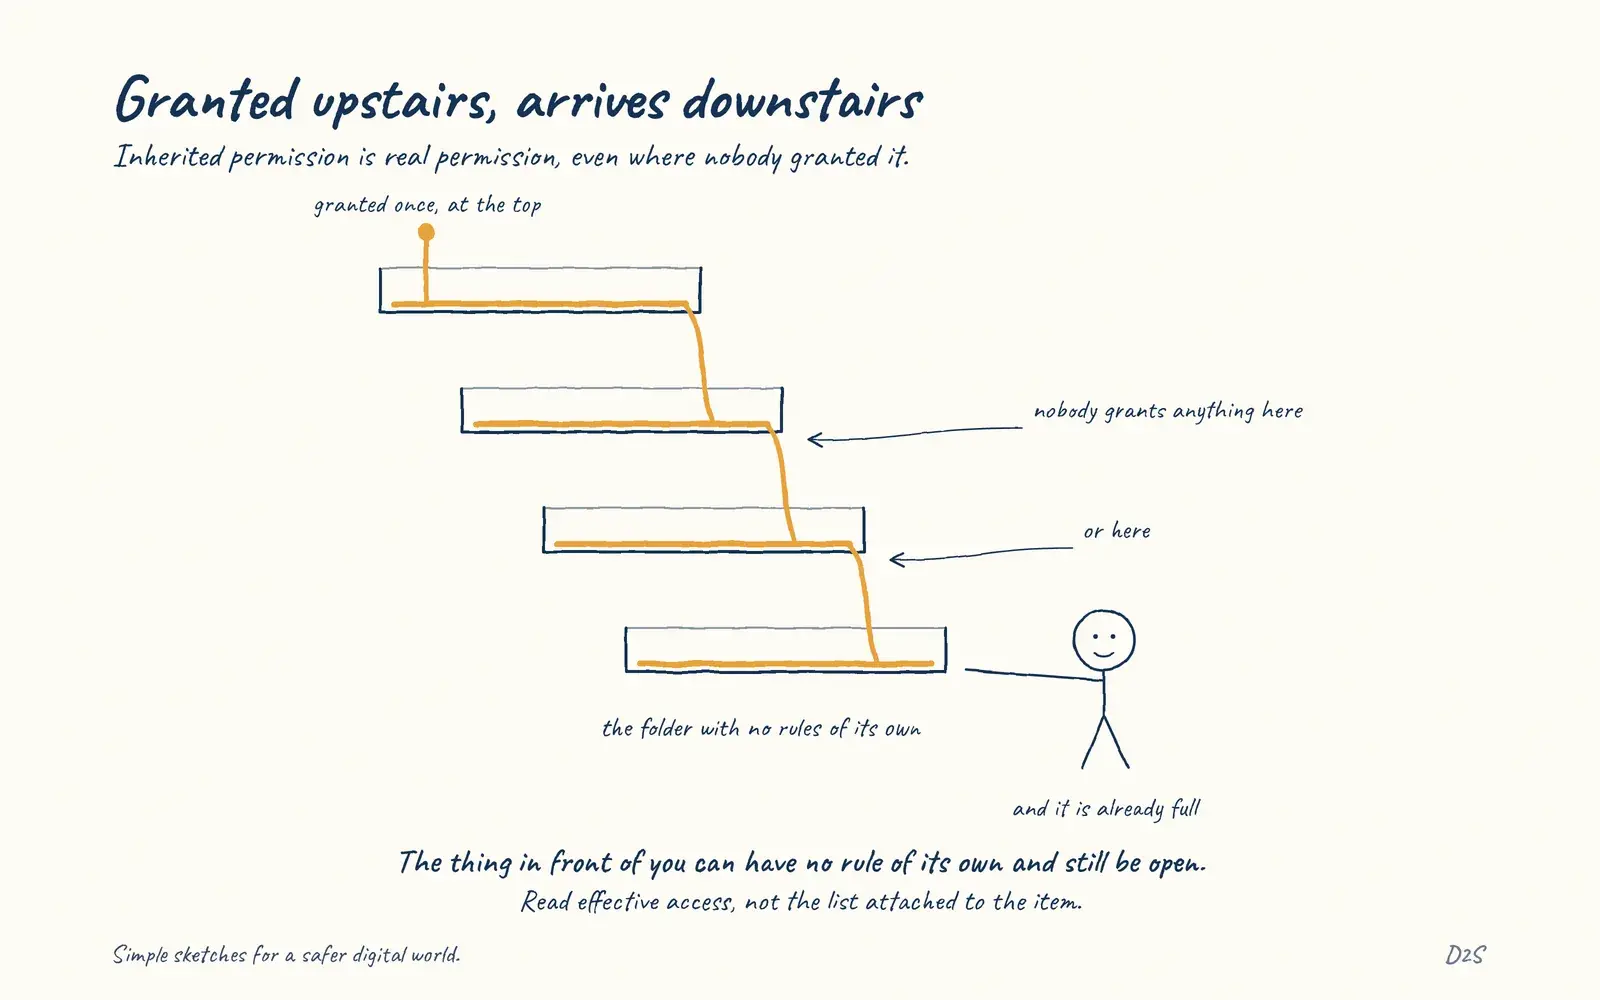 Permission inheritance can hide excessive accessGranted upstairs, arrives downstairs
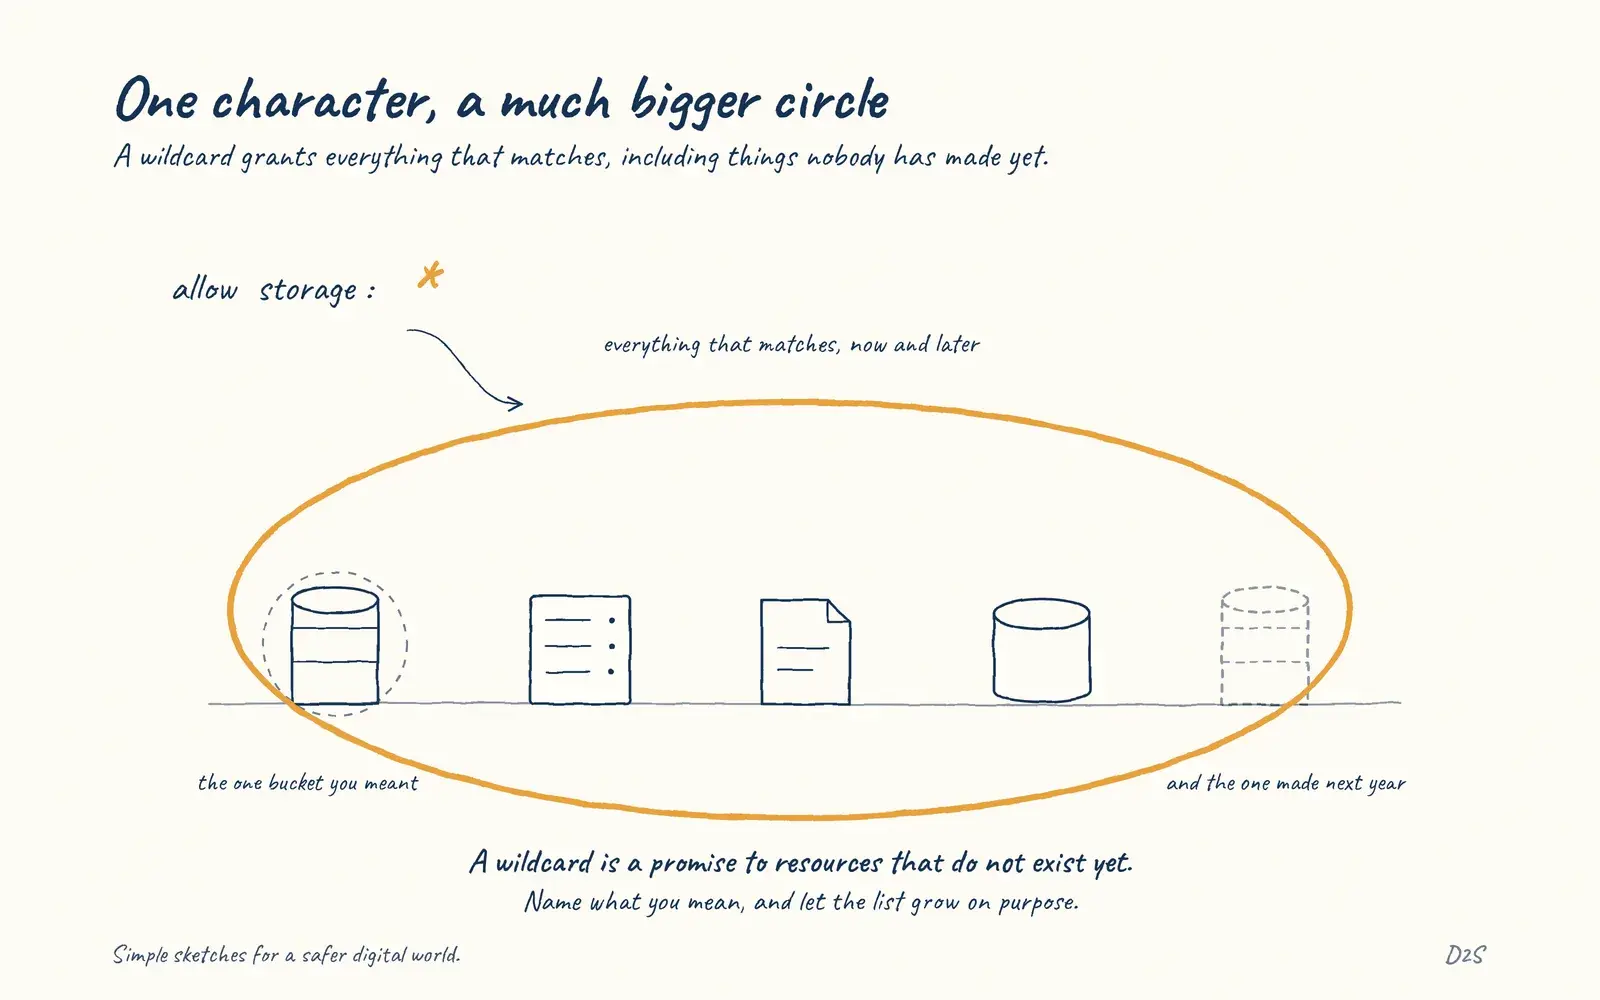 Wildcard permissions widen blast radiusOne character, a much bigger circle
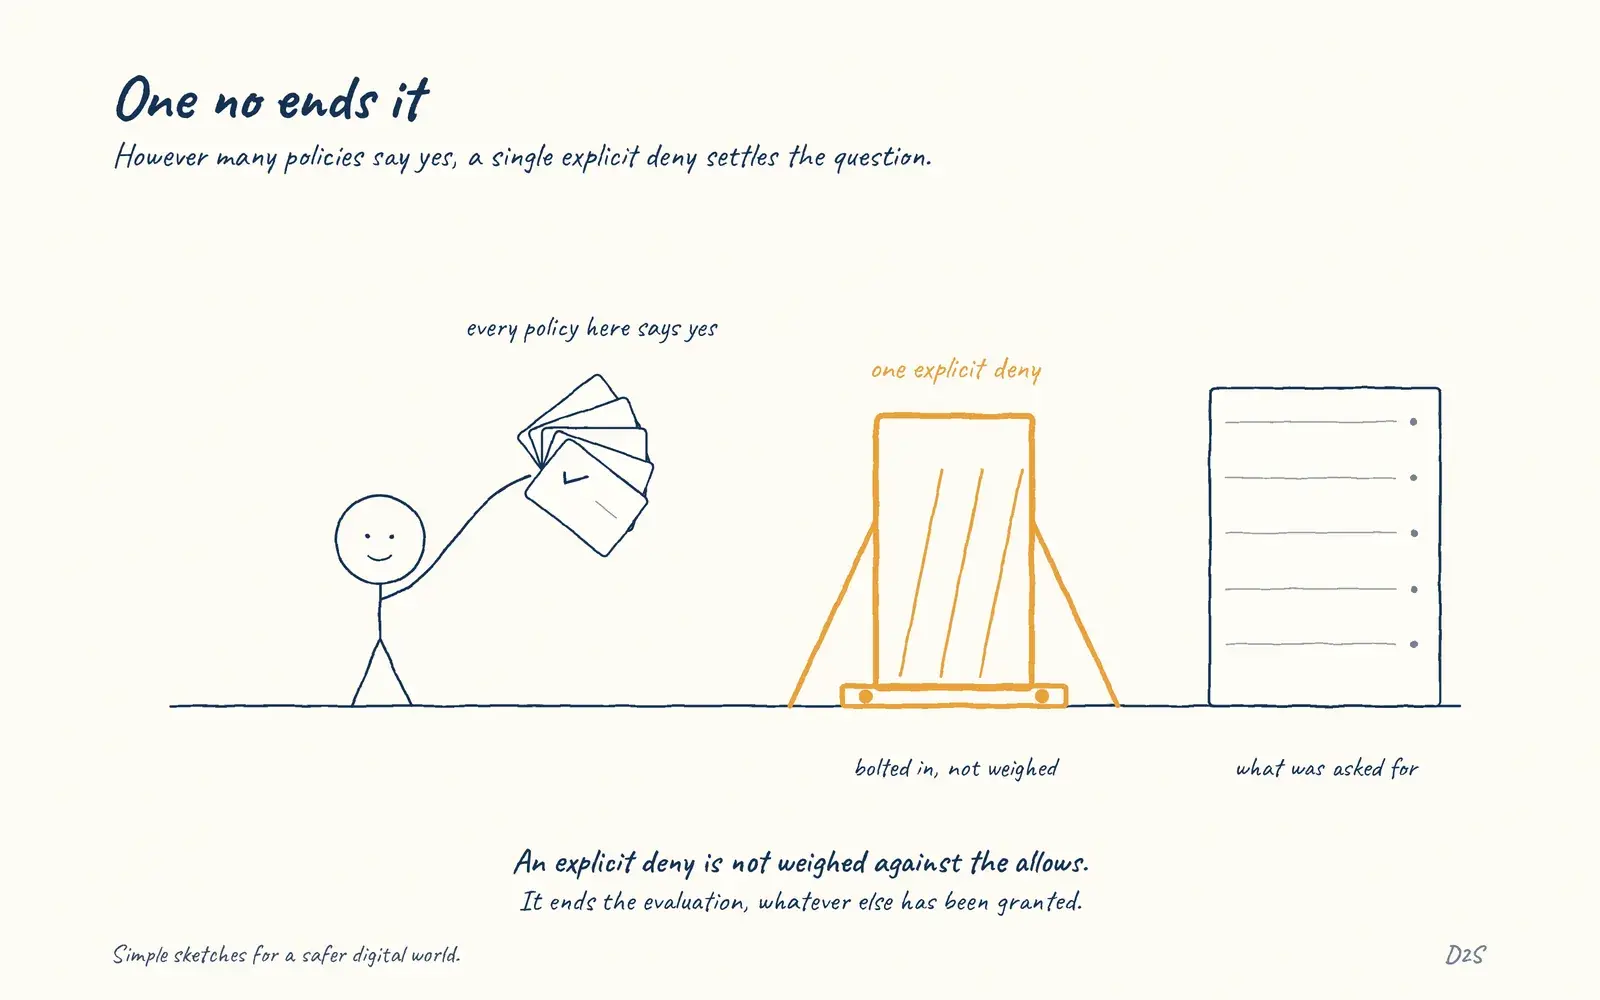 Deny rules can create hard guardrailsOne no ends it
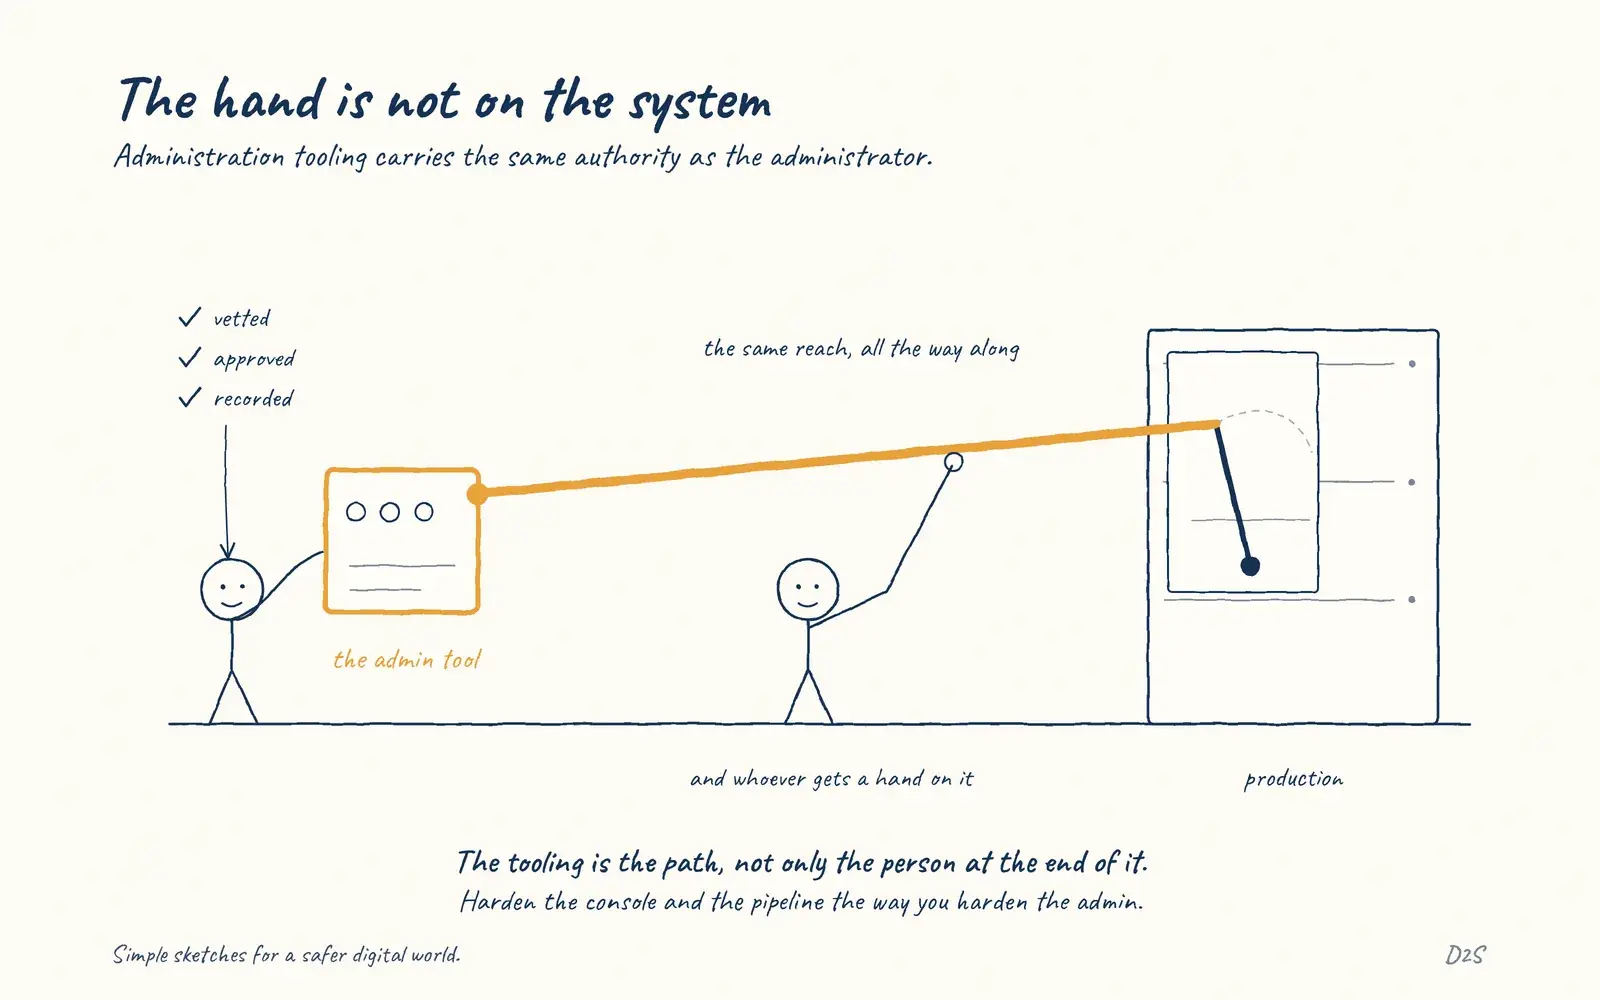 Admin tools are part of the privileged access pathThe hand is not on the system
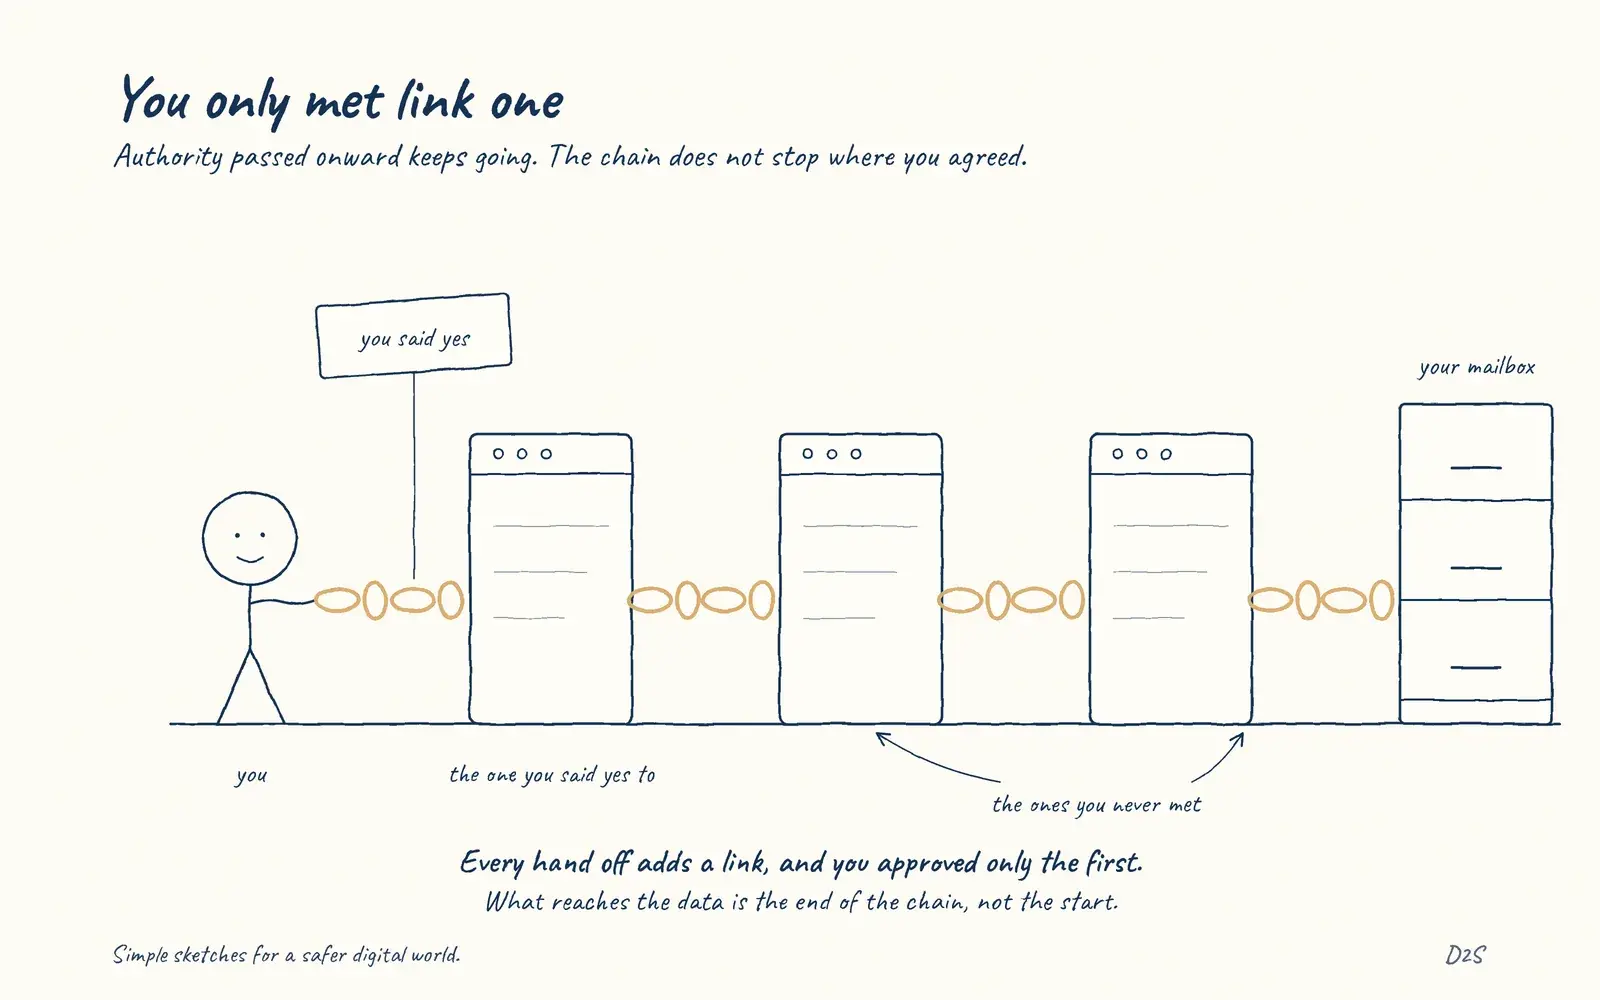 Delegation creates chains of trustYou only met link one
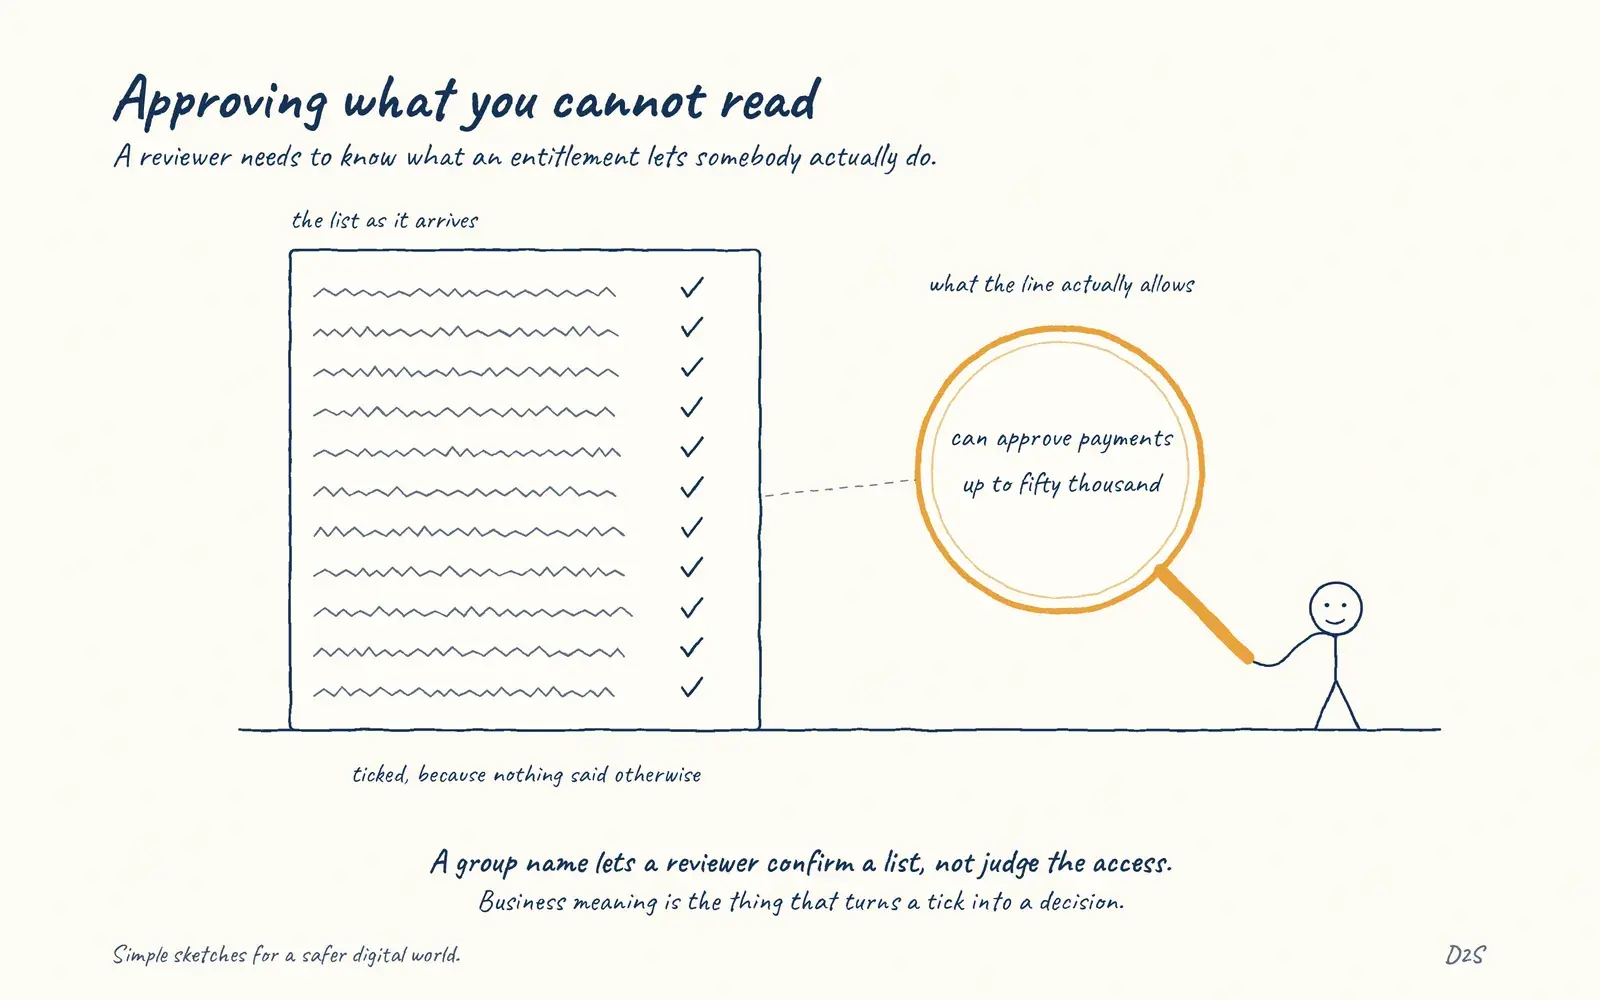 Entitlement reviews need business contextApproving what you cannot read
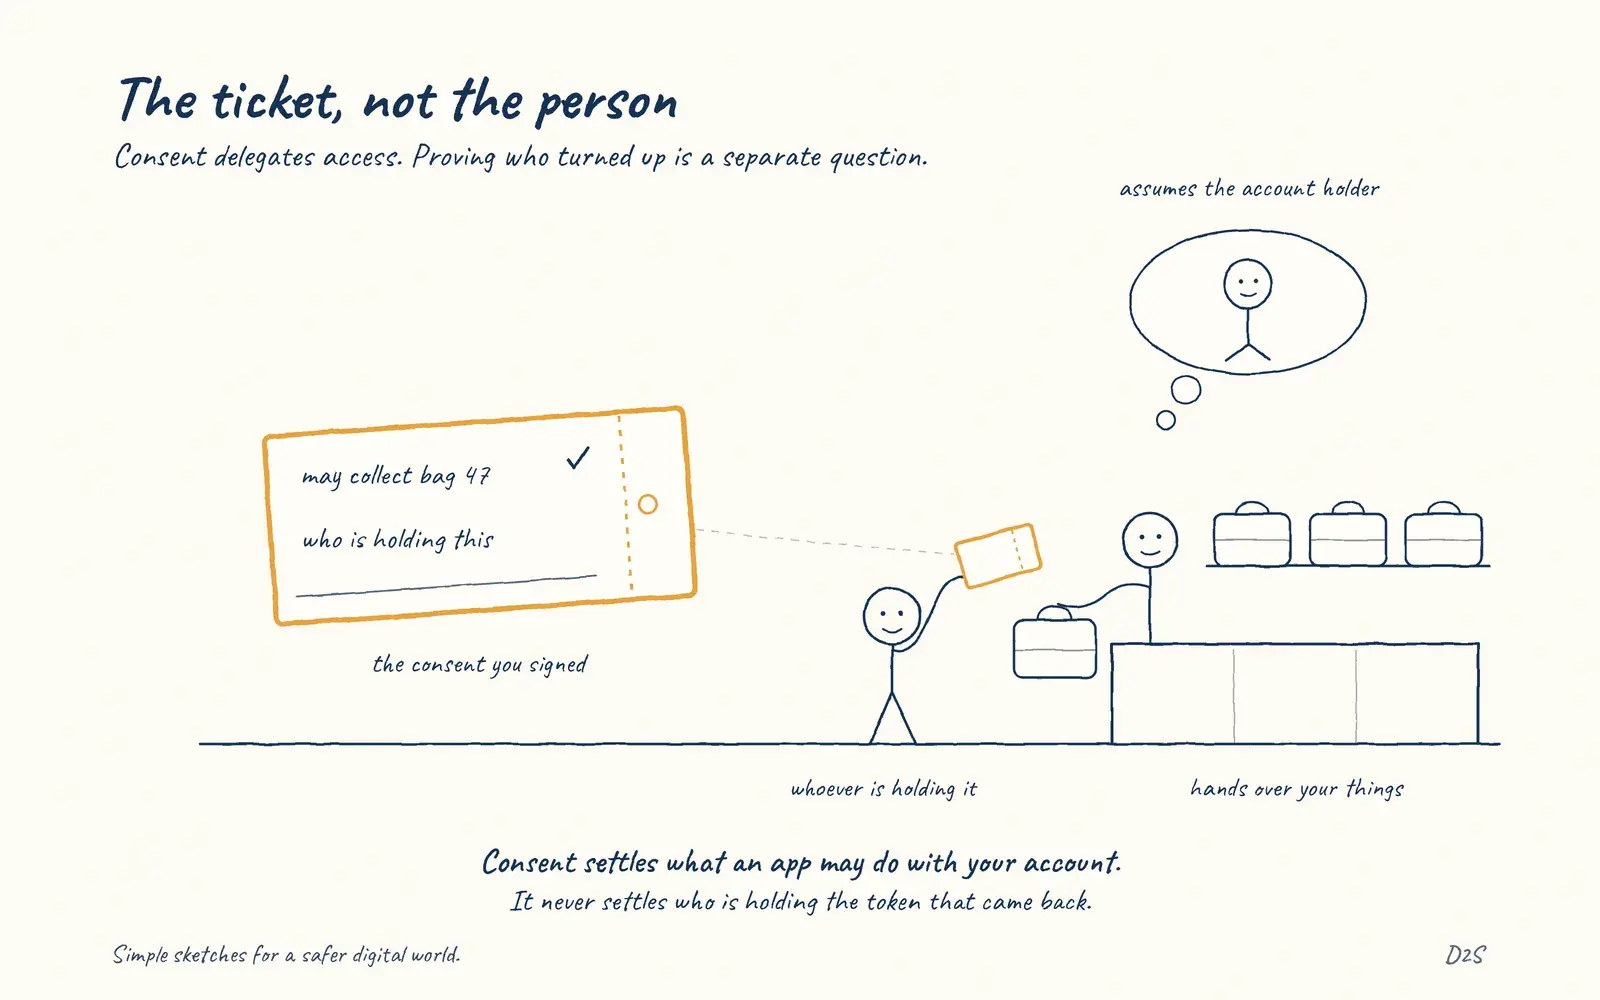 OAuth consent is not proof of identityThe ticket, not the person
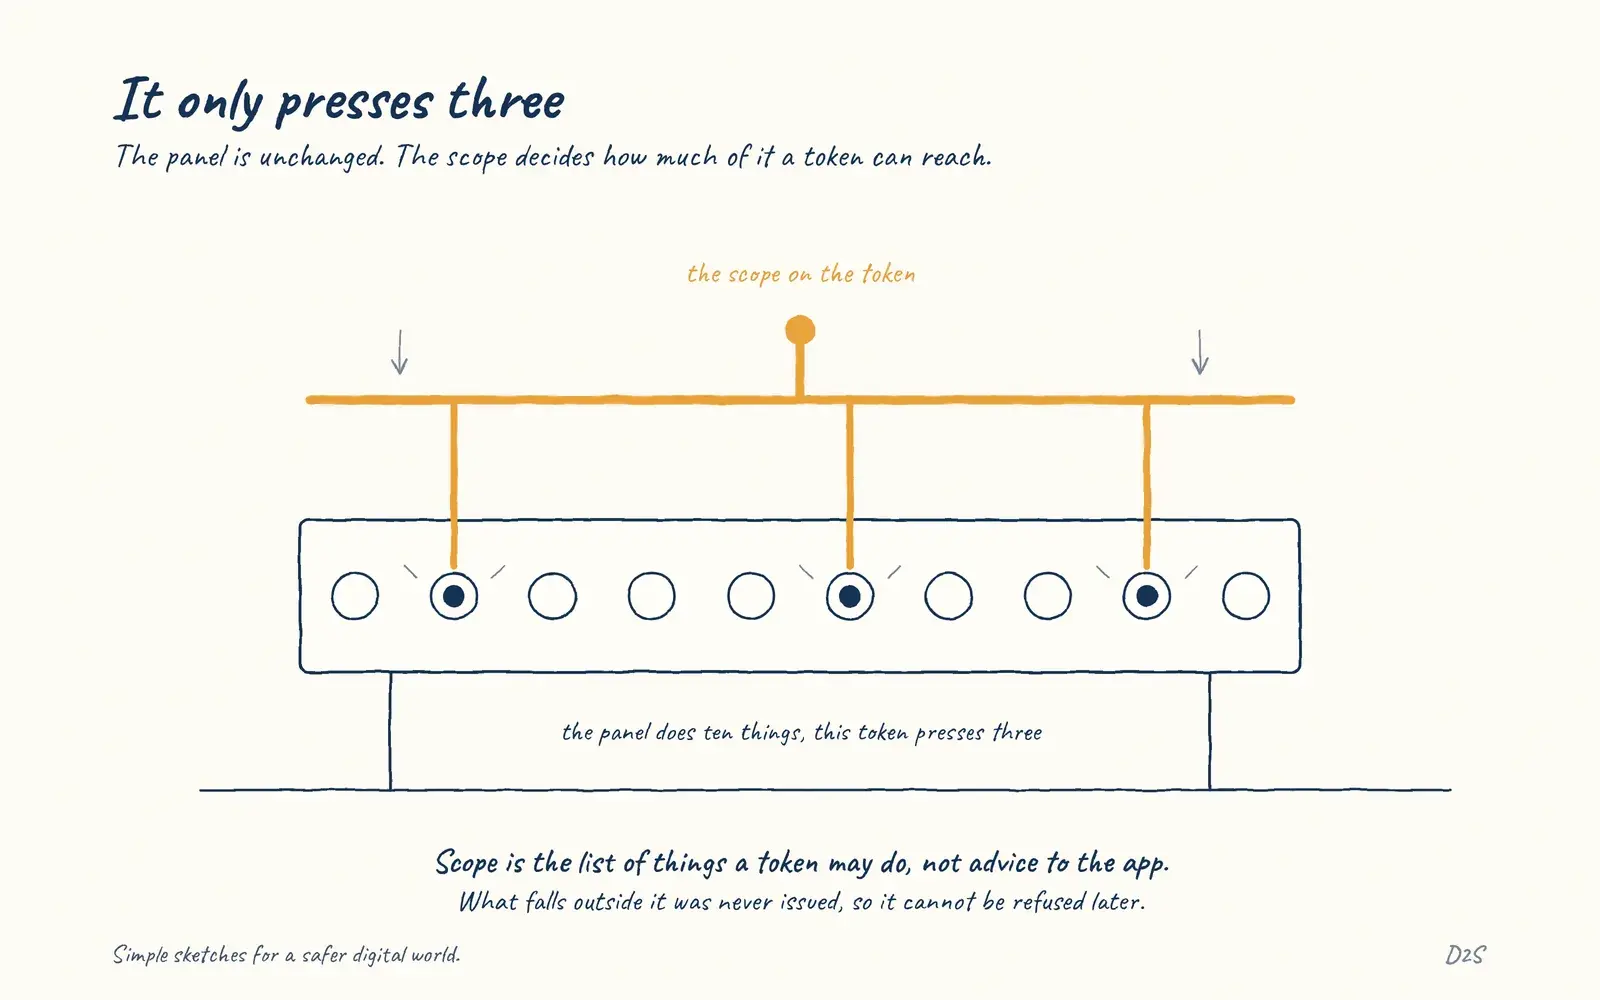 Token scope defines capabilityIt only presses three
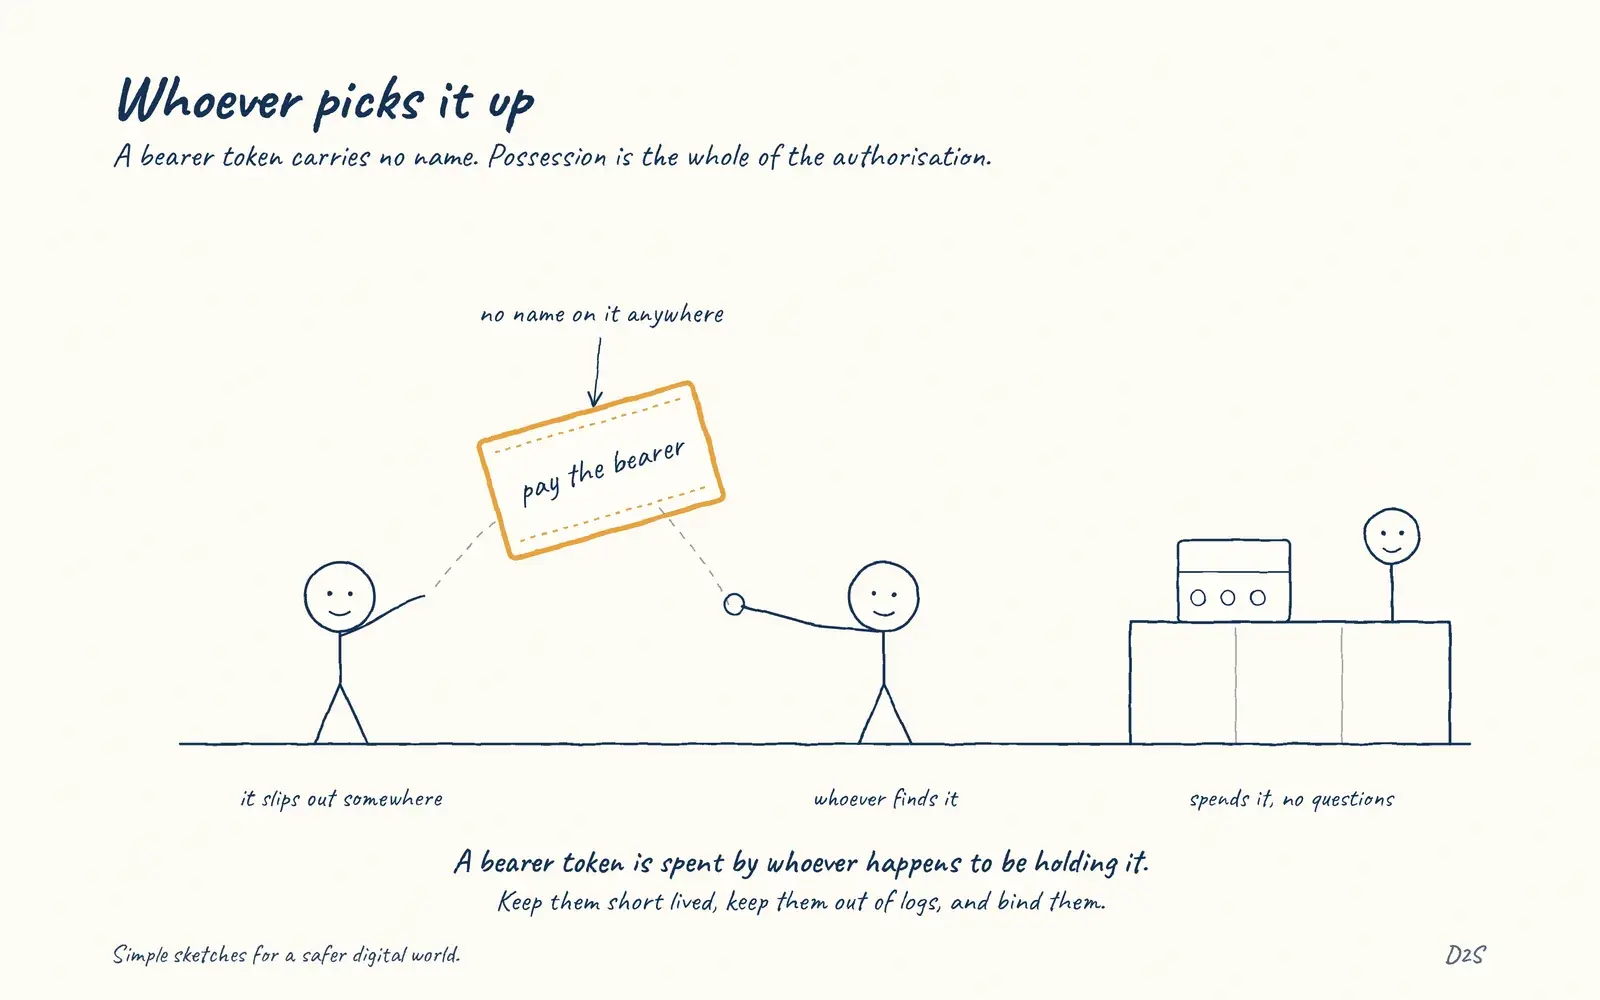 Bearer tokens behave like cashWhoever picks it up
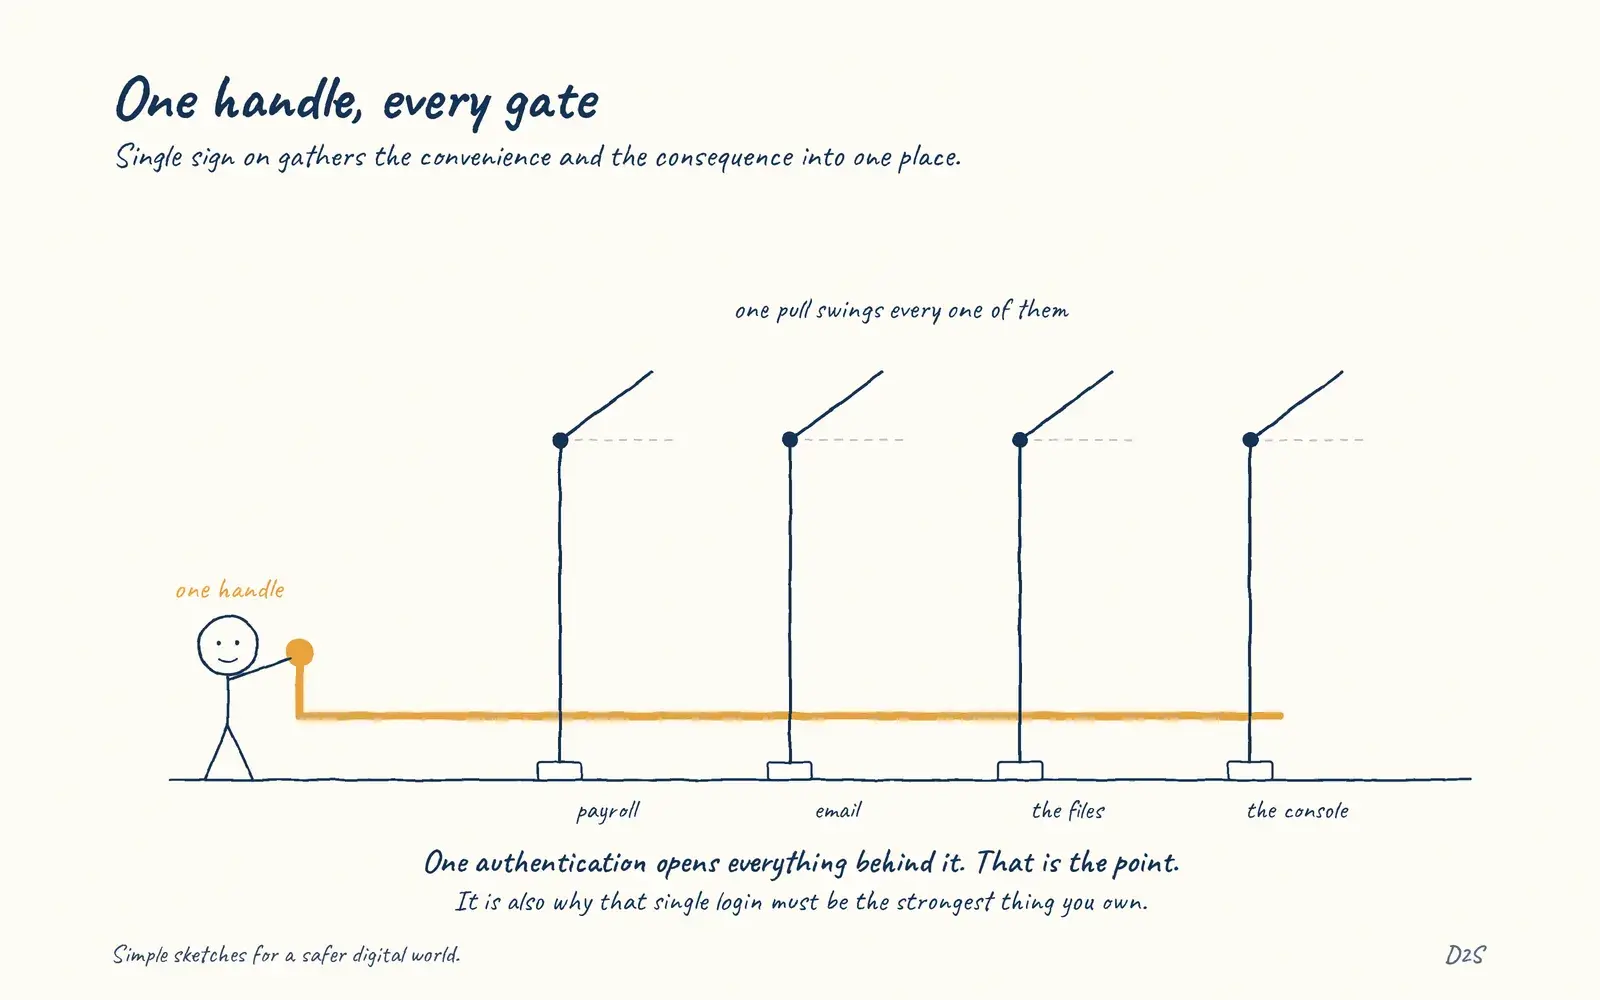 SSO concentrates convenience and consequenceOne handle, every gate
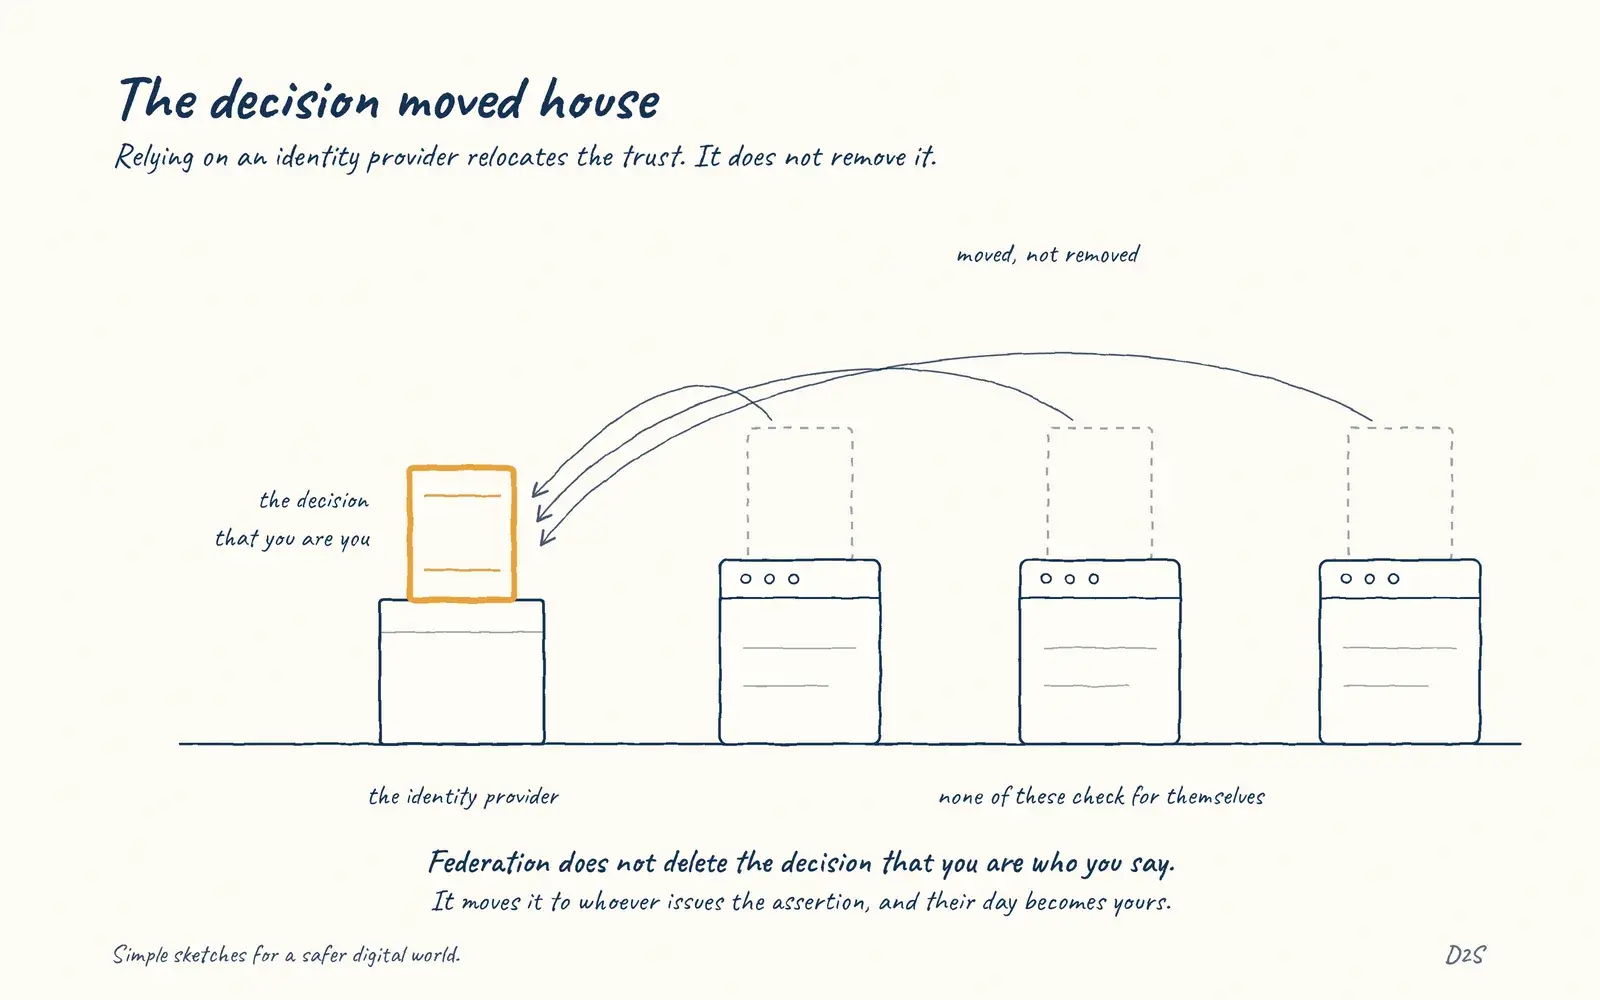 Federation shifts where trust livesThe decision moved house
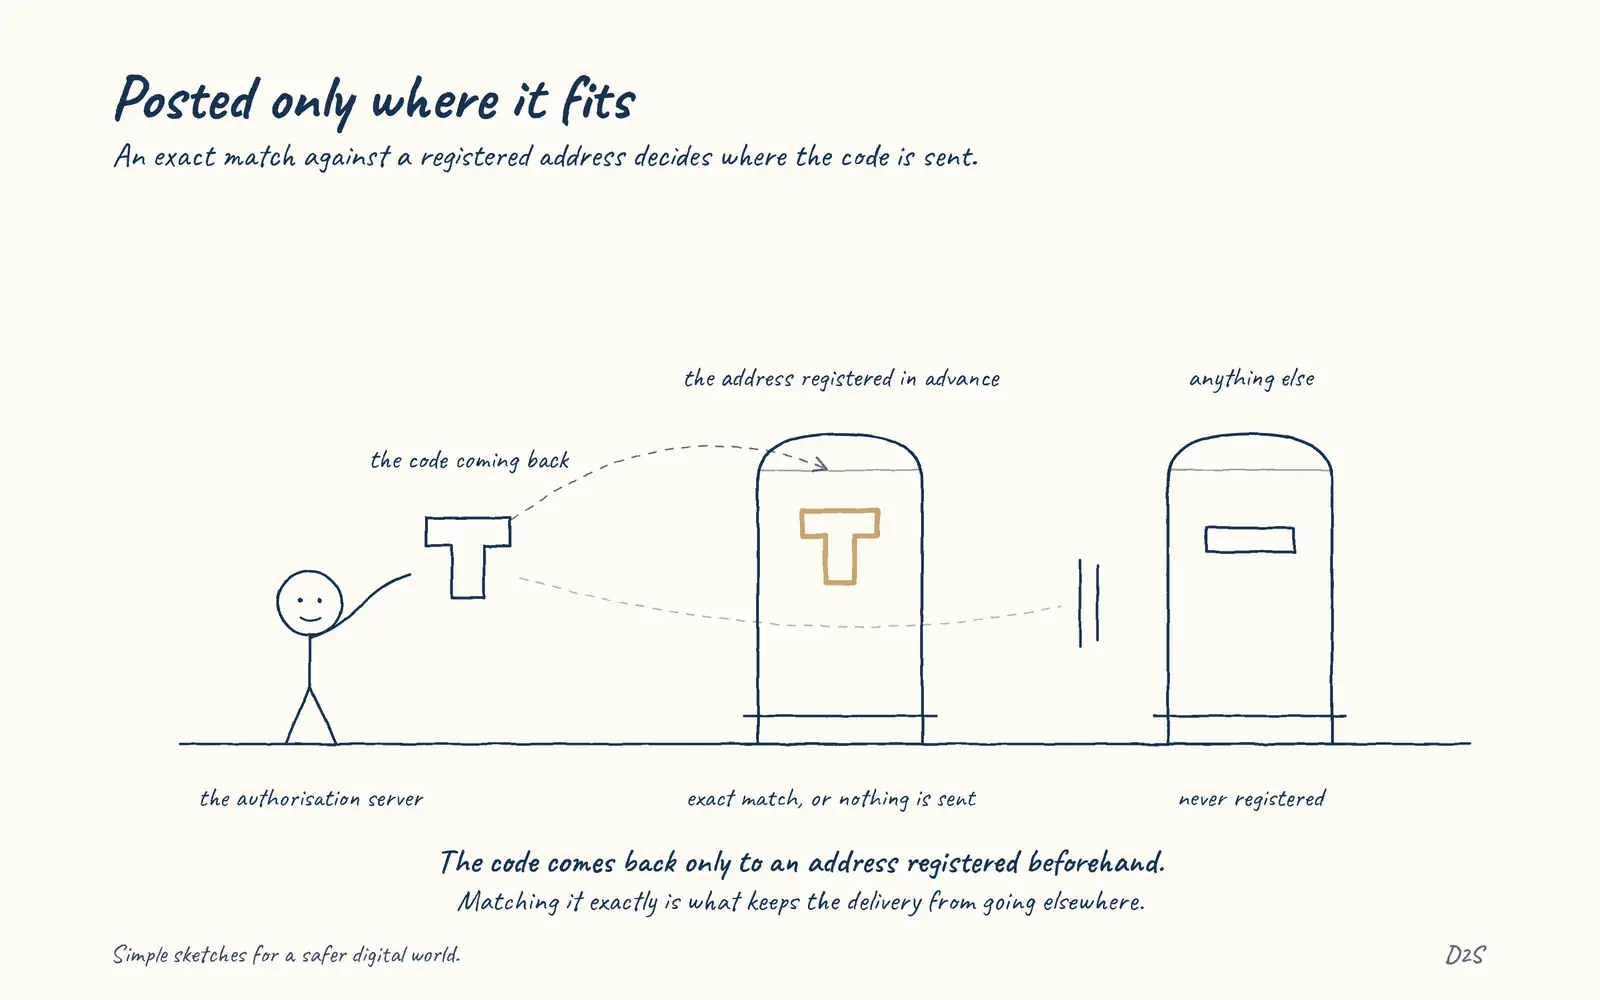 Redirect URI validation protects token deliveryPosted only where it fits
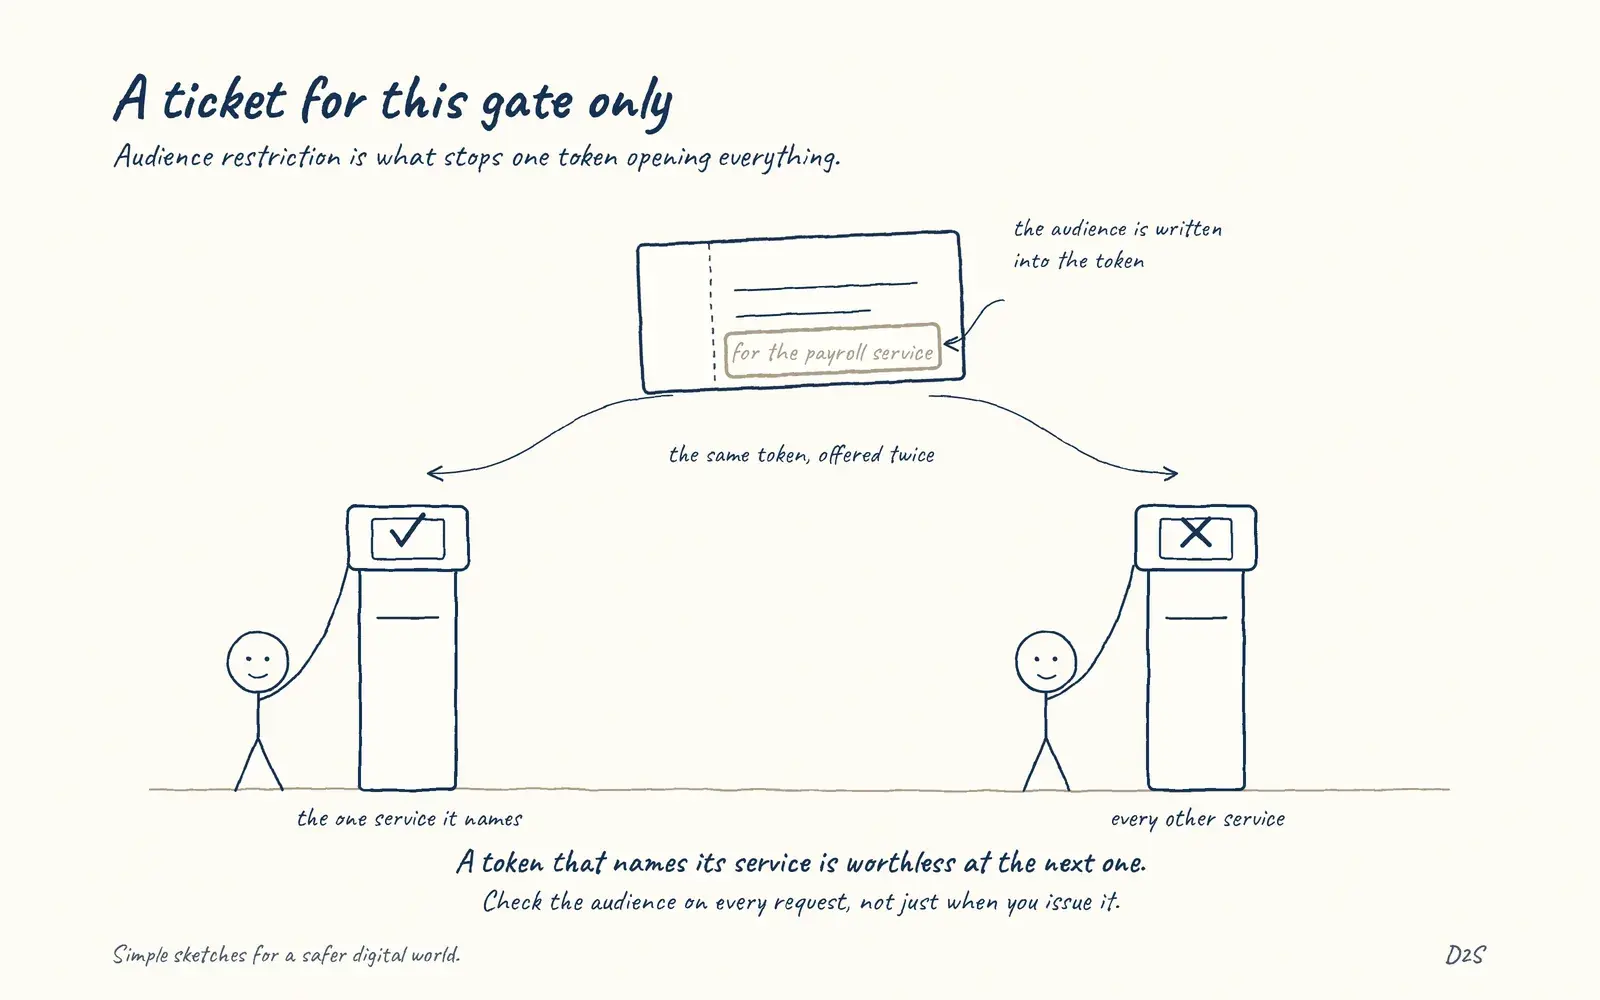 Token audience prevents universal reuseA ticket for this gate only
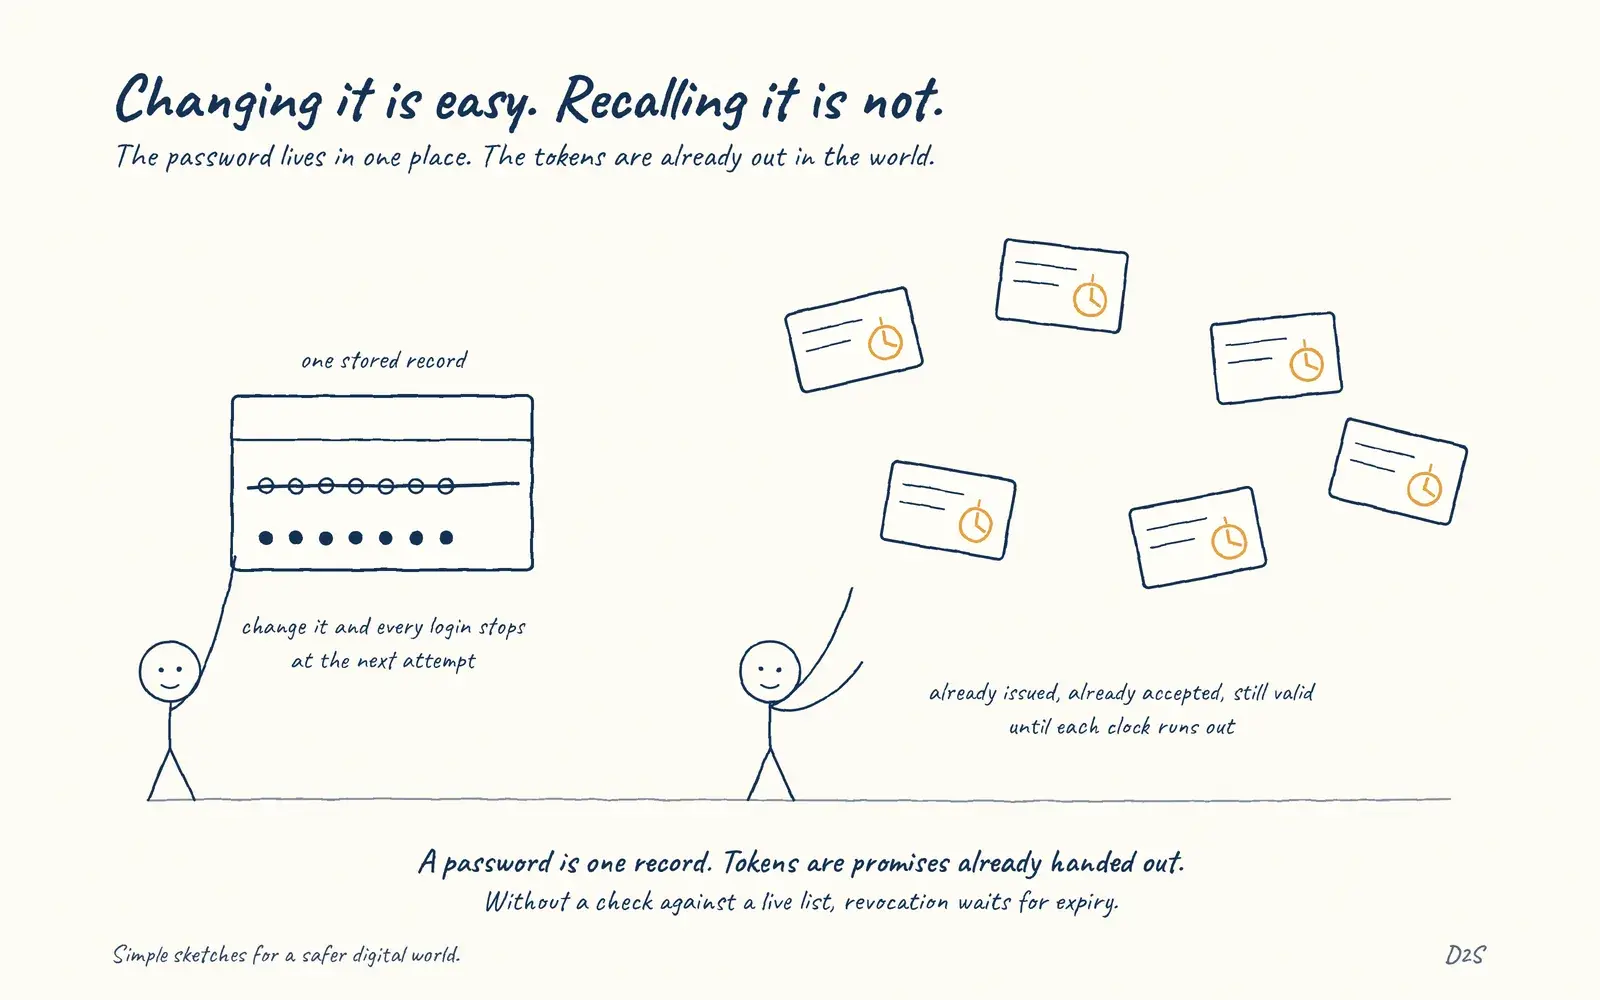 Token revocation is harder than password changeChanging it is easy
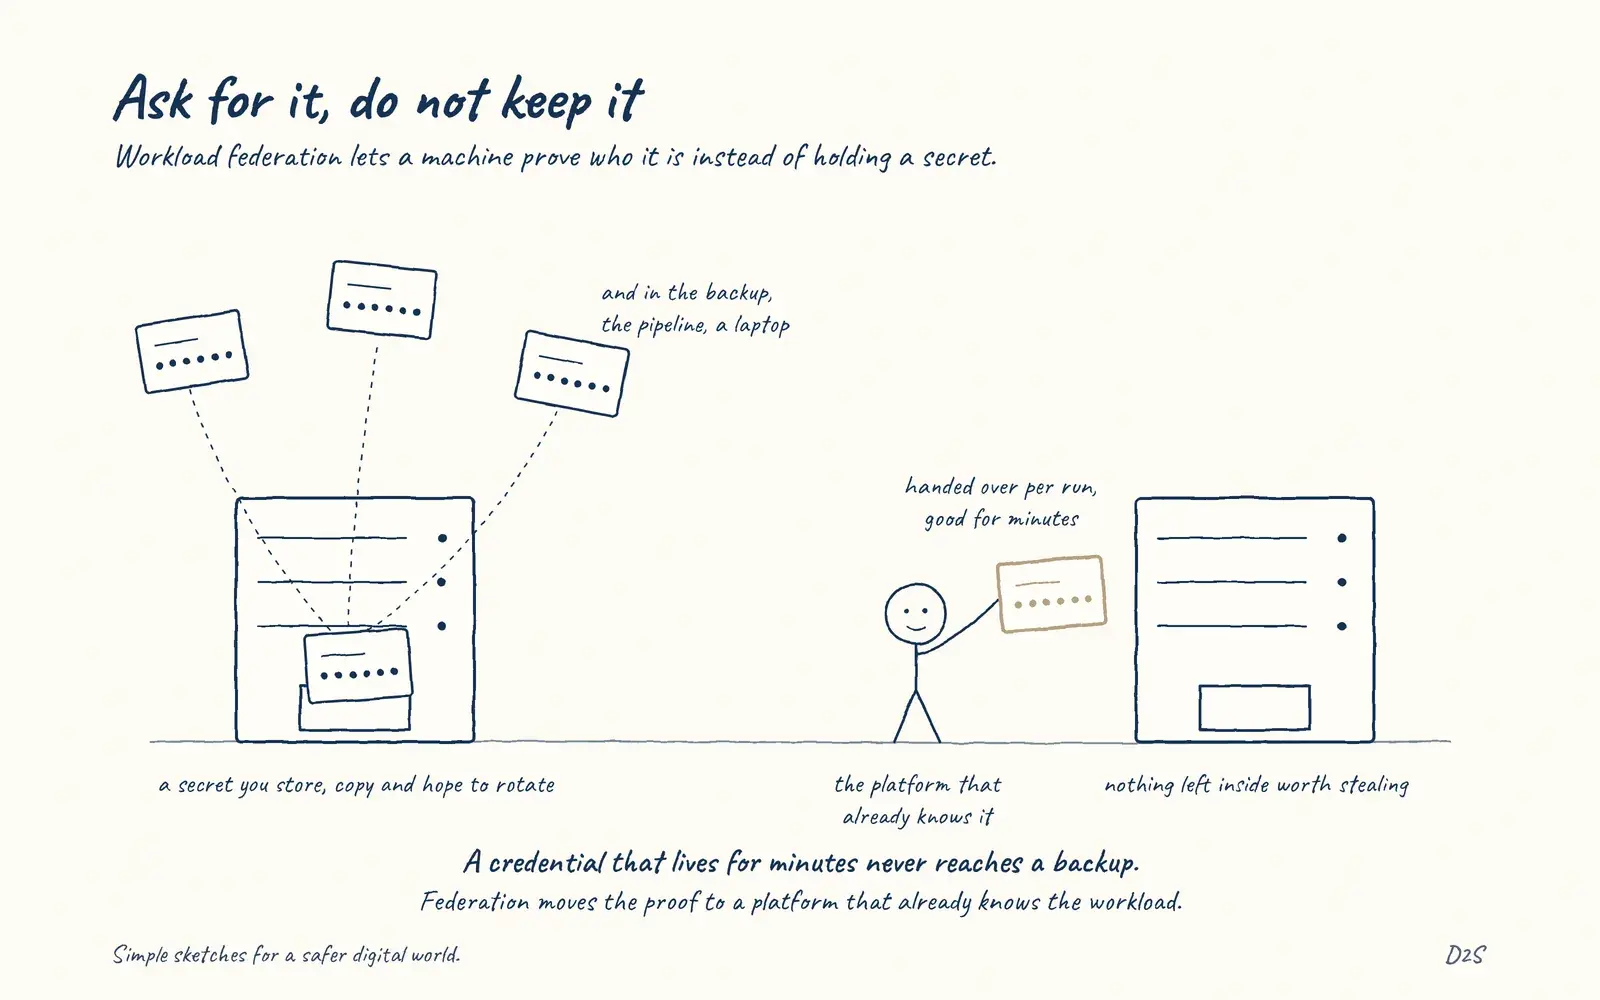 Workload federation can remove stored cloud keysAsk for it, do not keep it
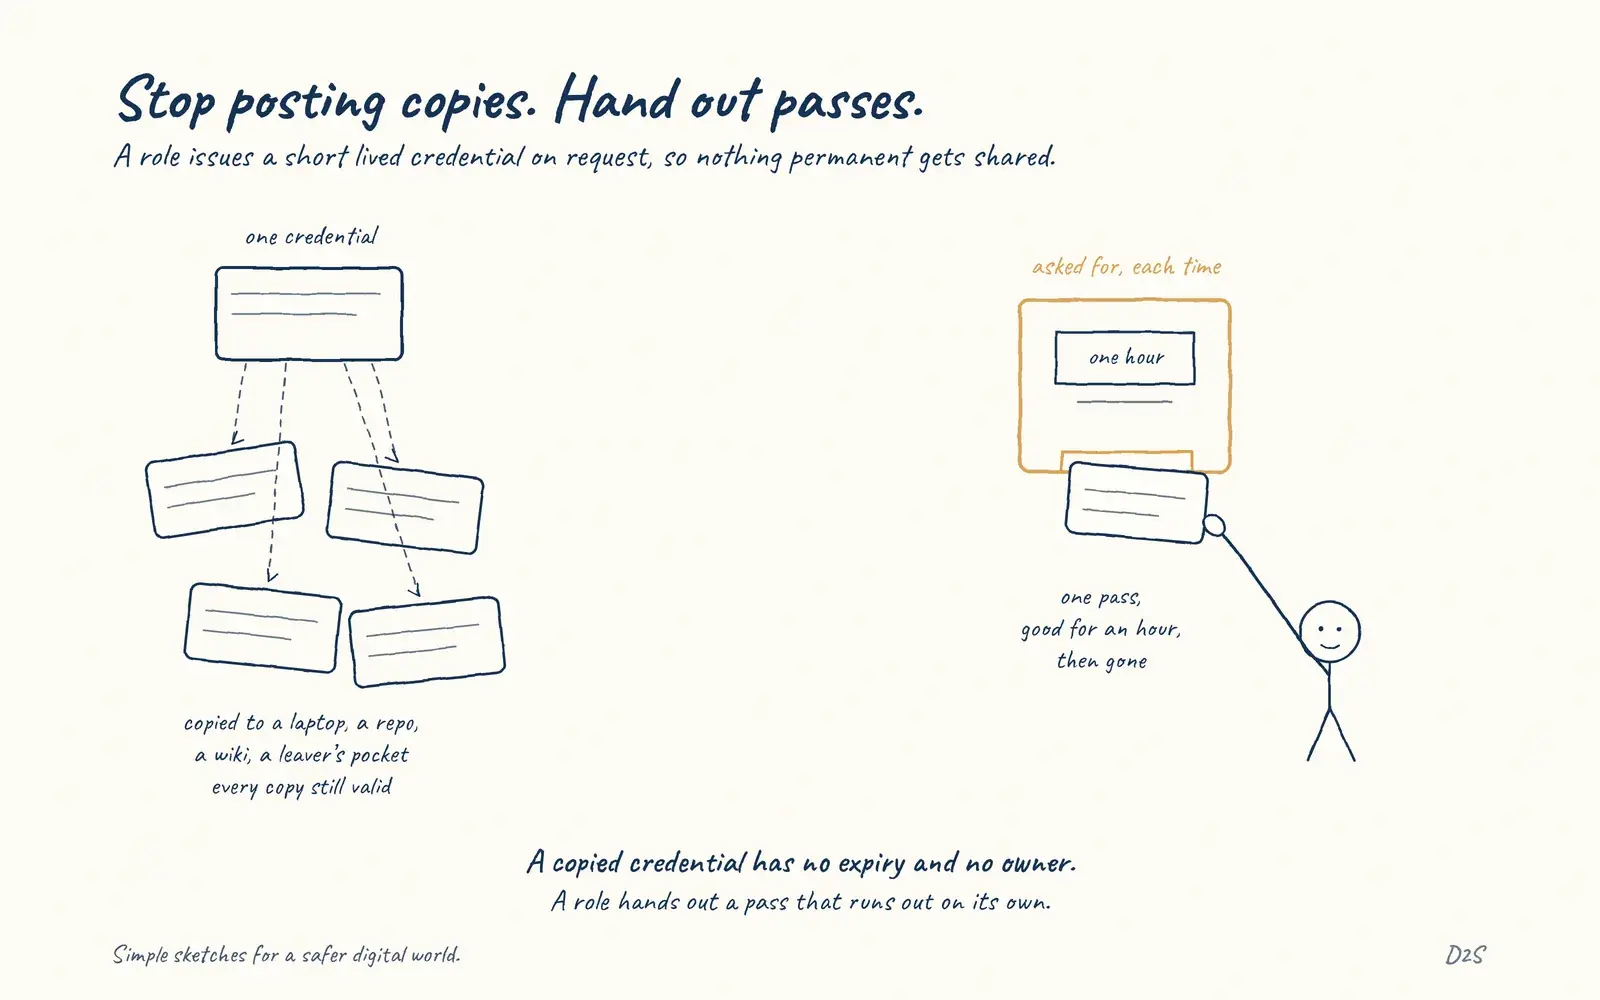 Cloud roles can replace copied long-lived keysStop posting copies. Hand out passes
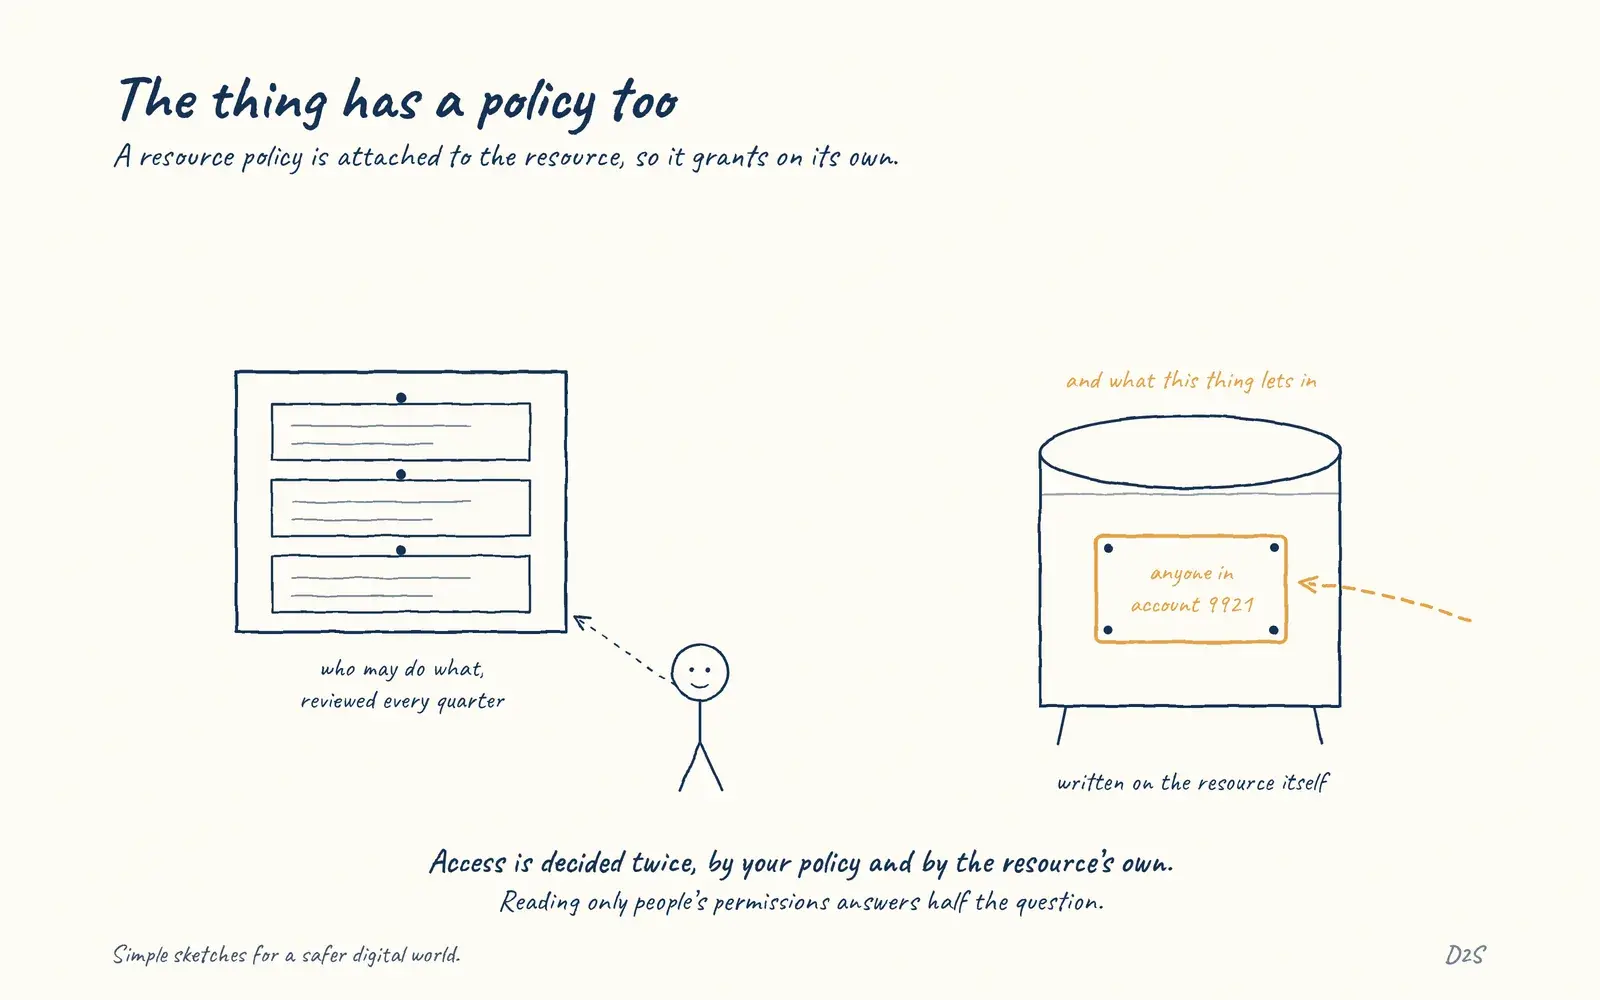 Resource policies create a second authorisation surfaceThe thing has a policy too
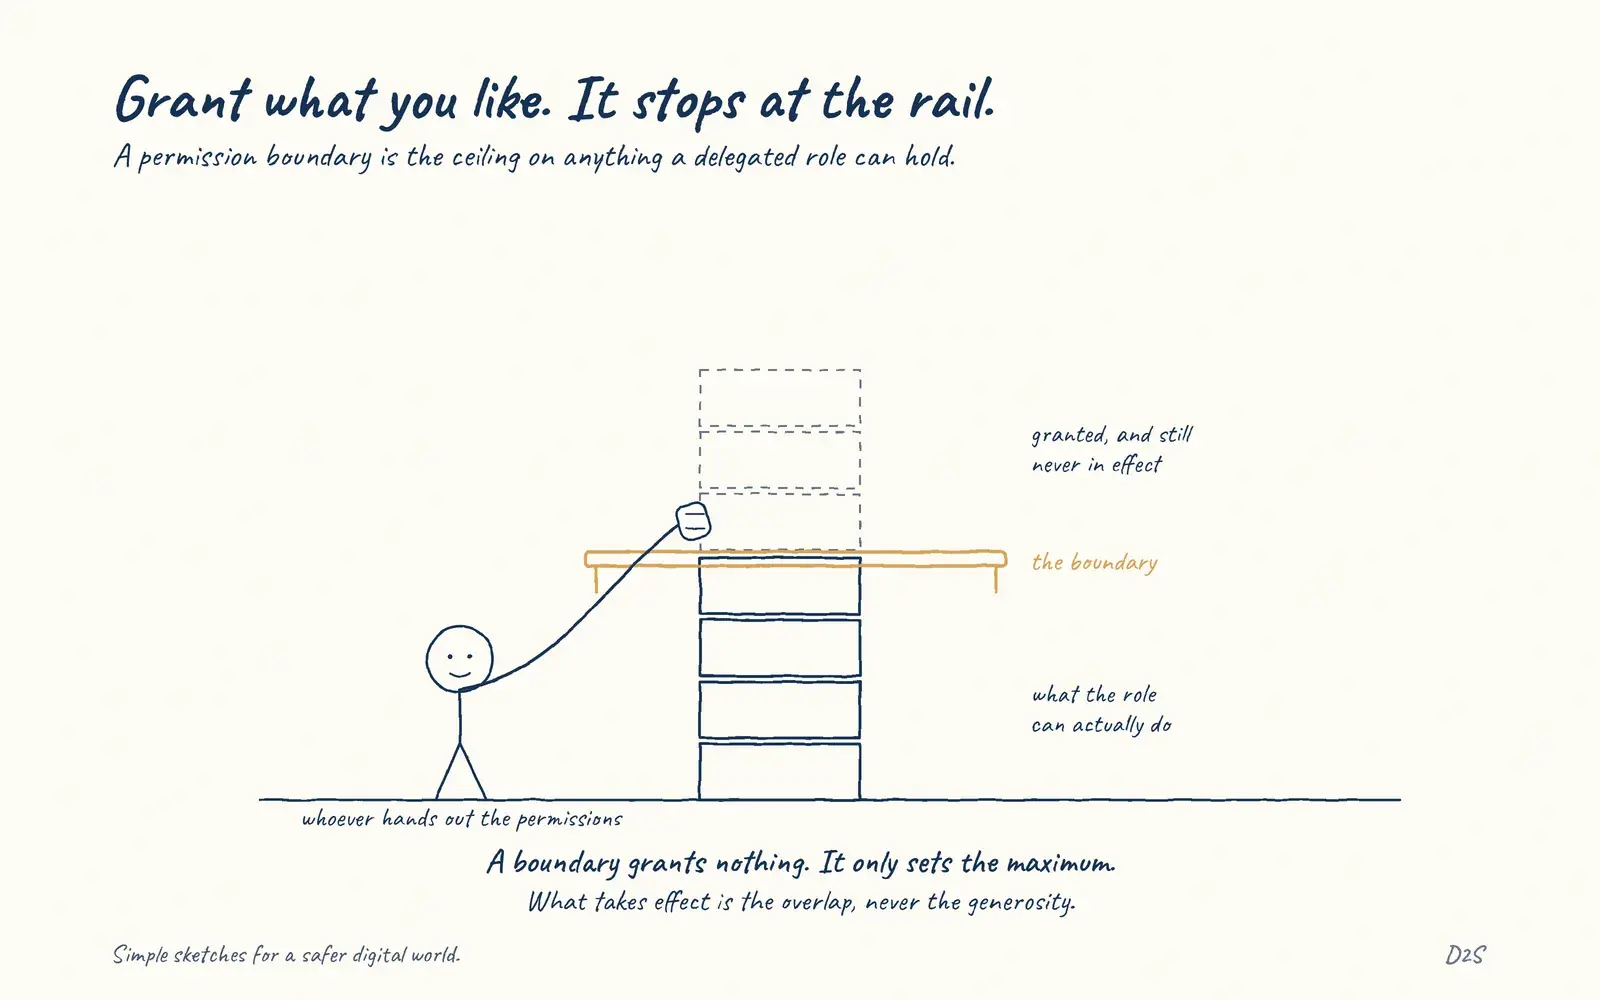 Permission boundaries cap delegated powerGrant what you like. It stops at the rail
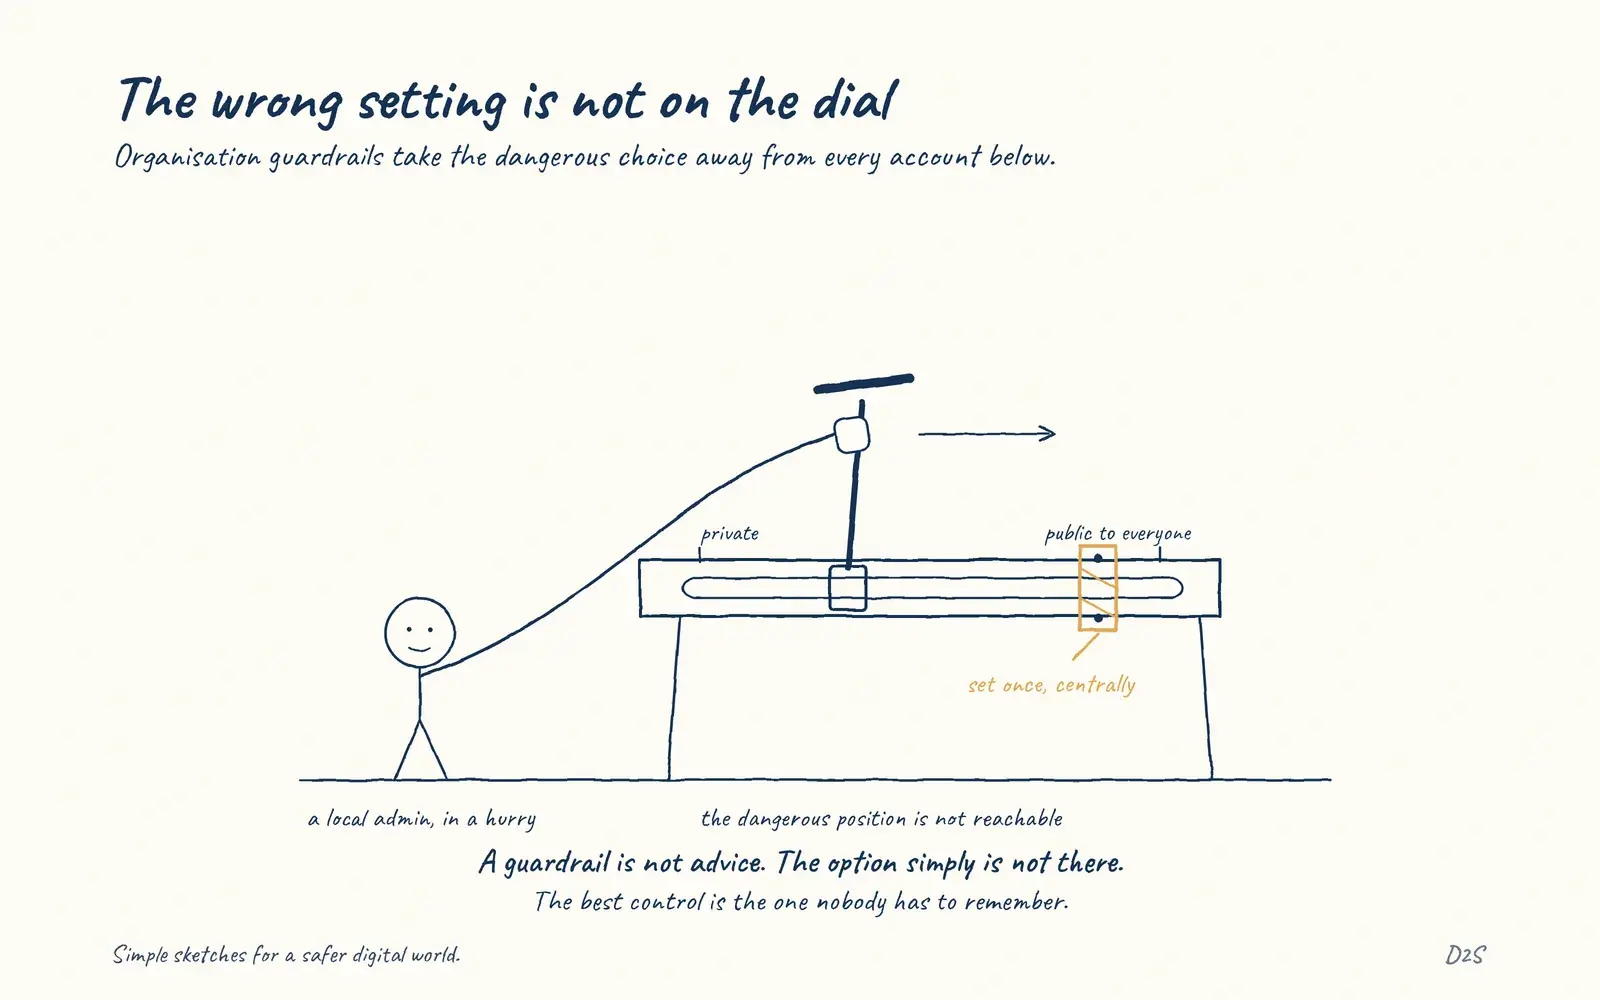 Organisation guardrails prevent dangerous local choicesThe wrong setting is not on the dial
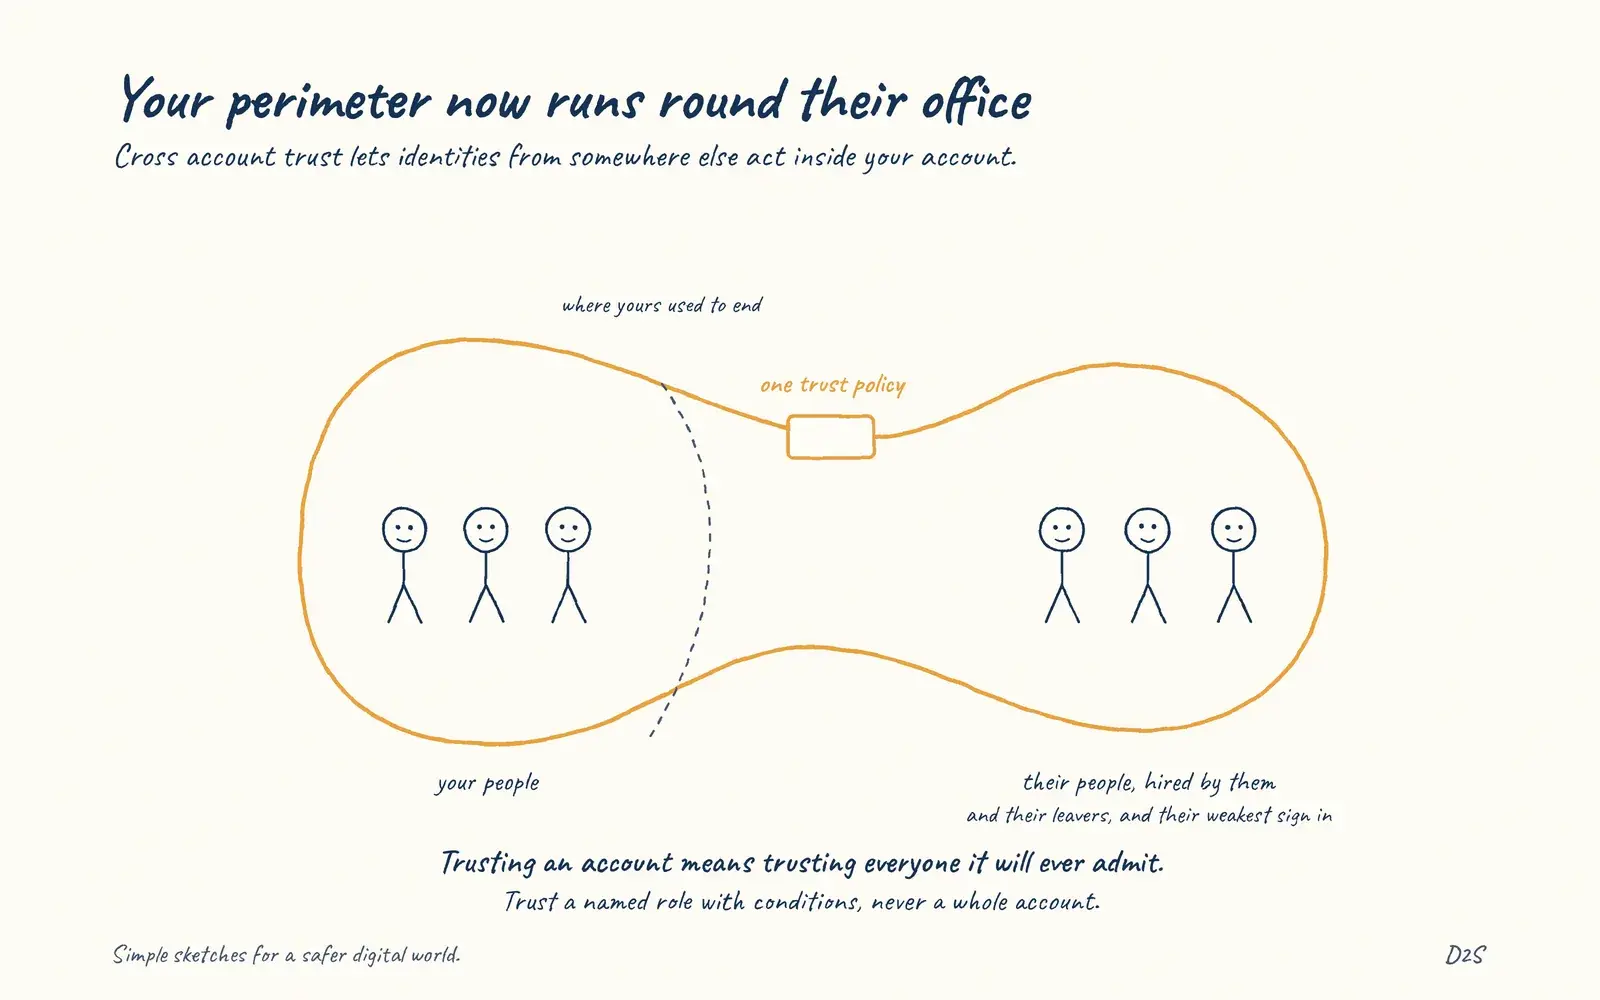 Cross-account trust expands the identity perimeterYour perimeter now runs round their office
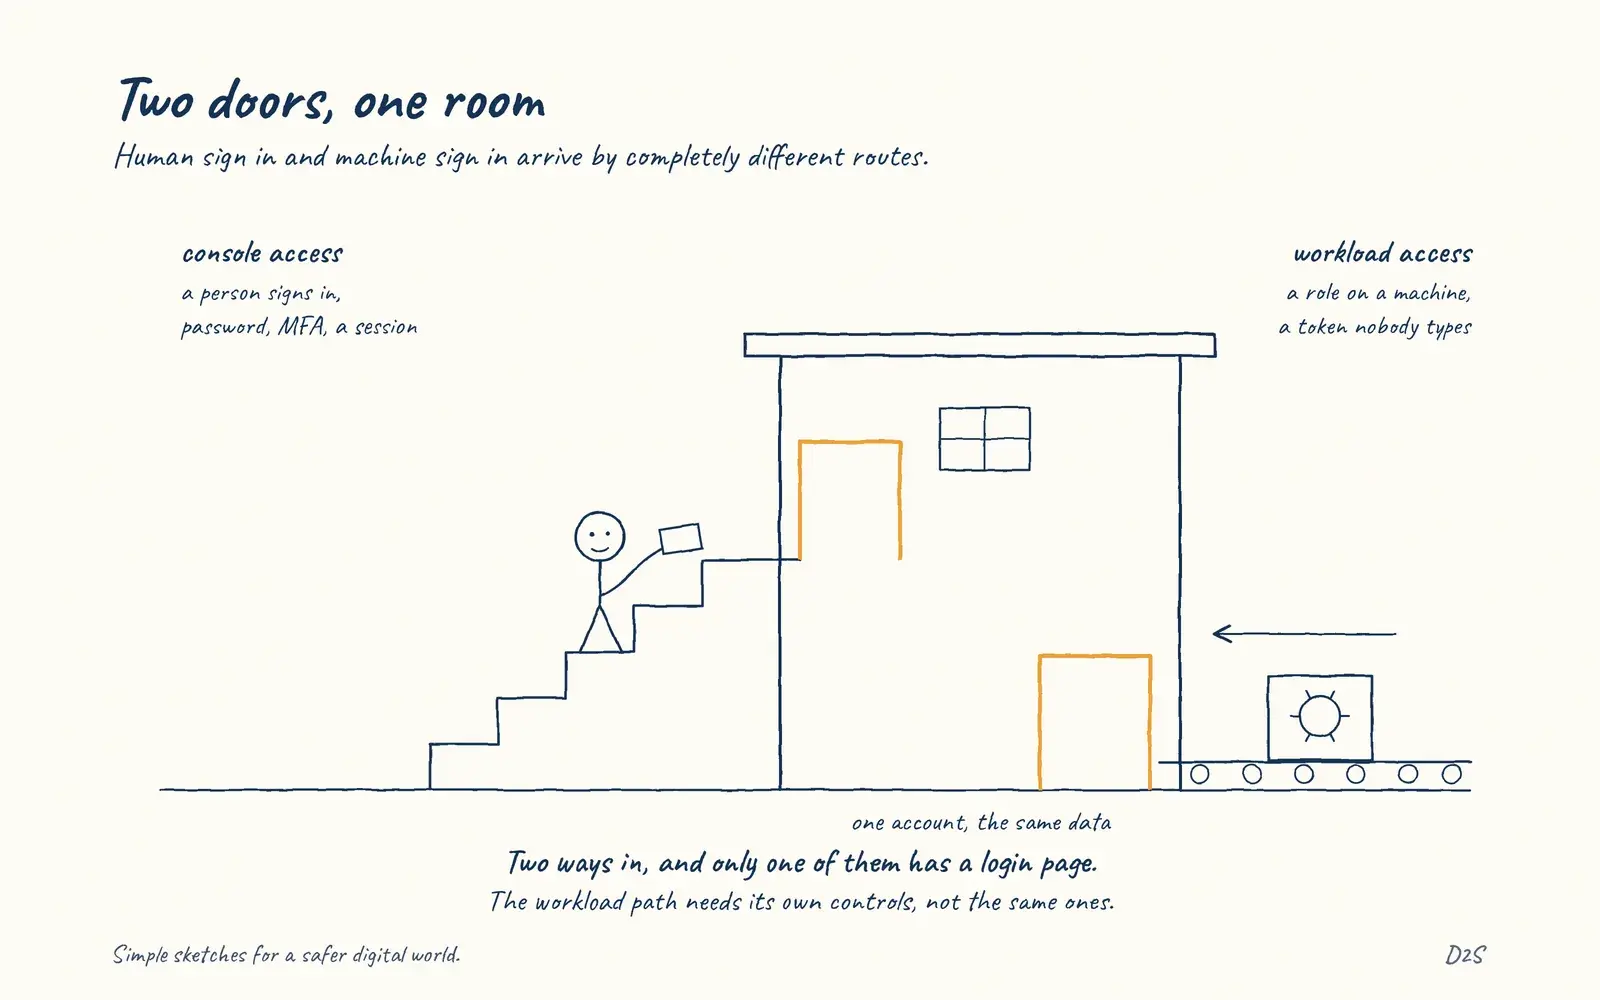 Console access and workload access are different pathsTwo doors, one room
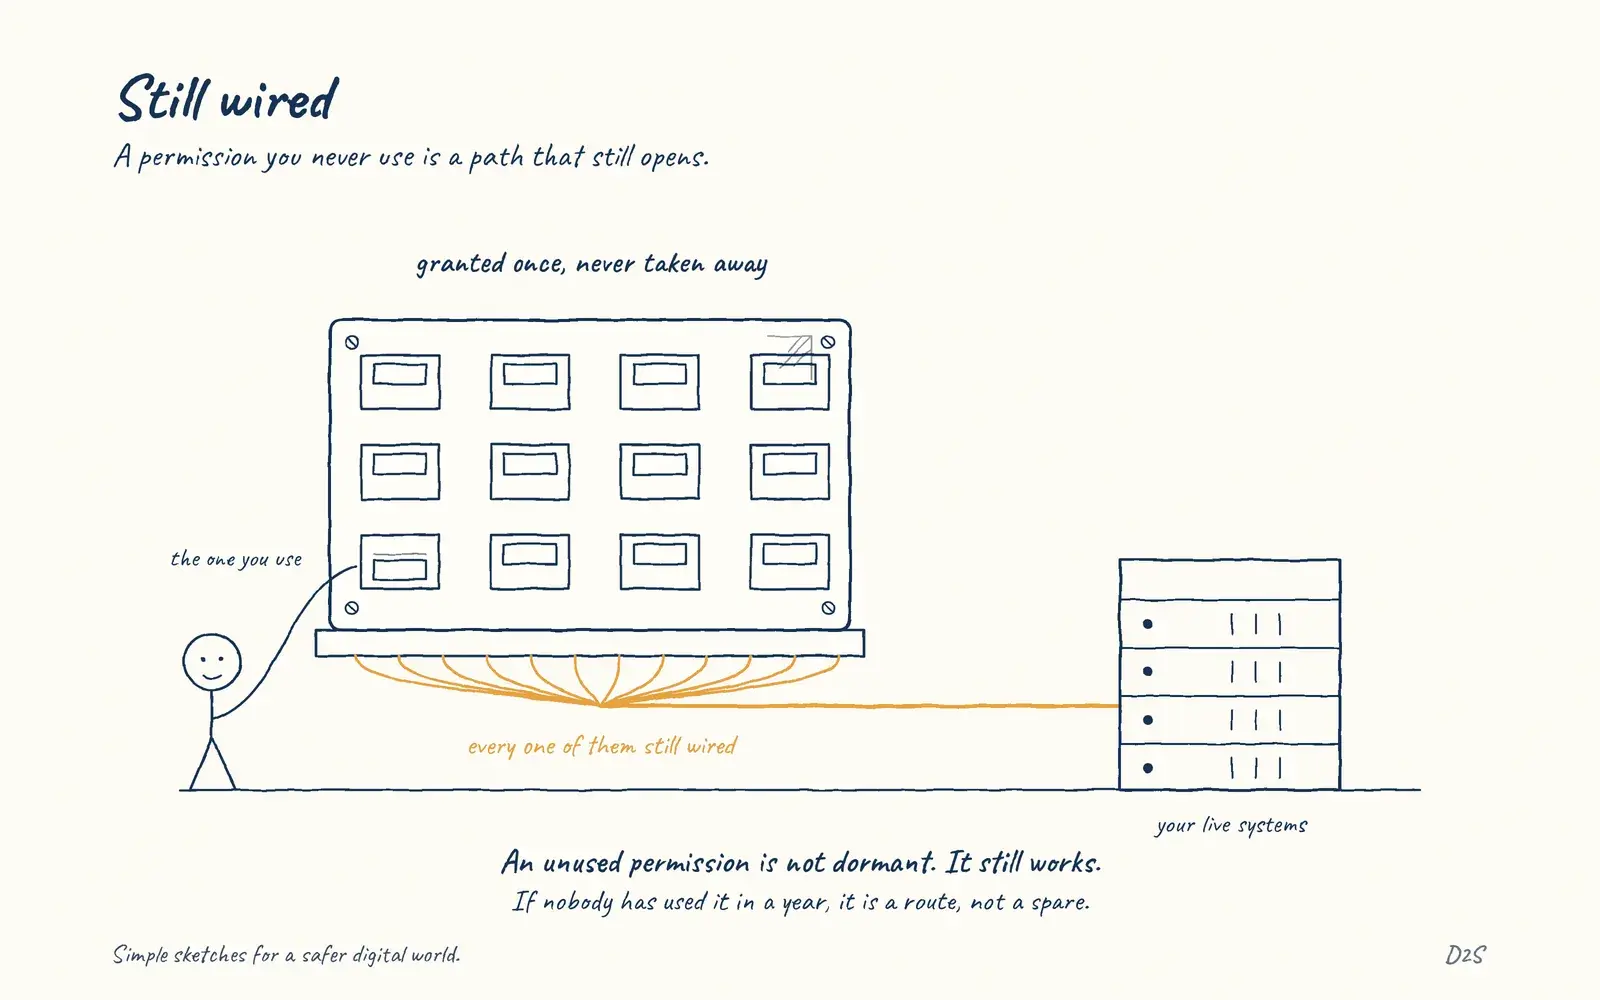 Unused cloud permissions are latent attack pathsStill wired
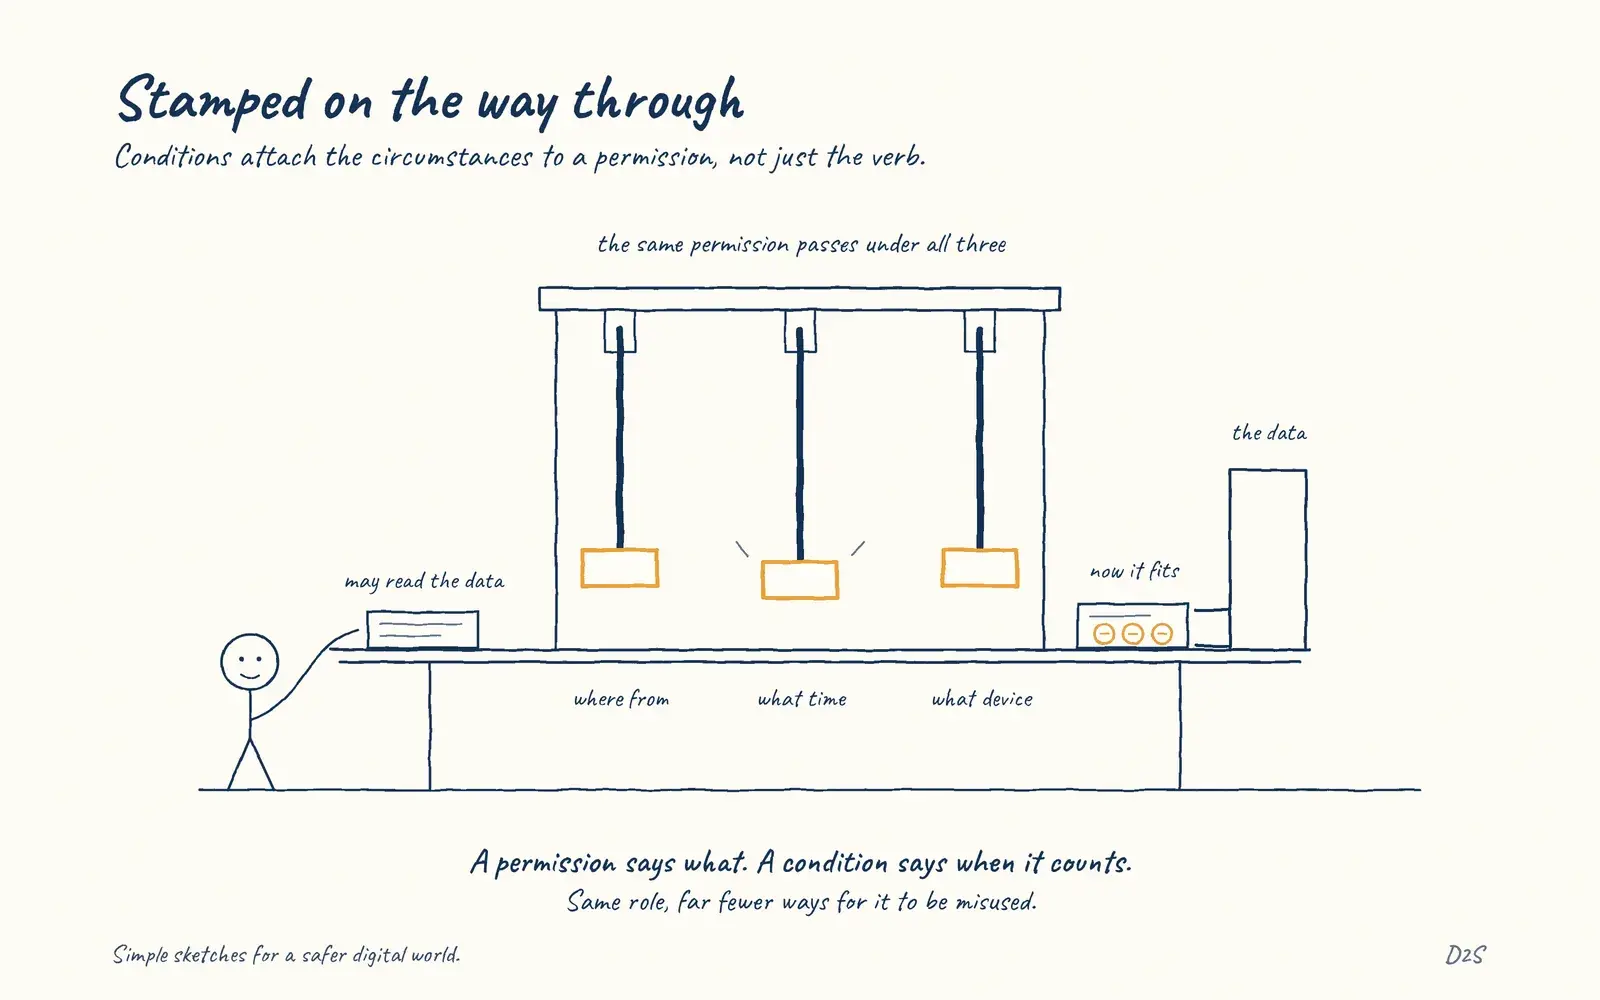 IAM conditions add context to permissionsStamped on the way through
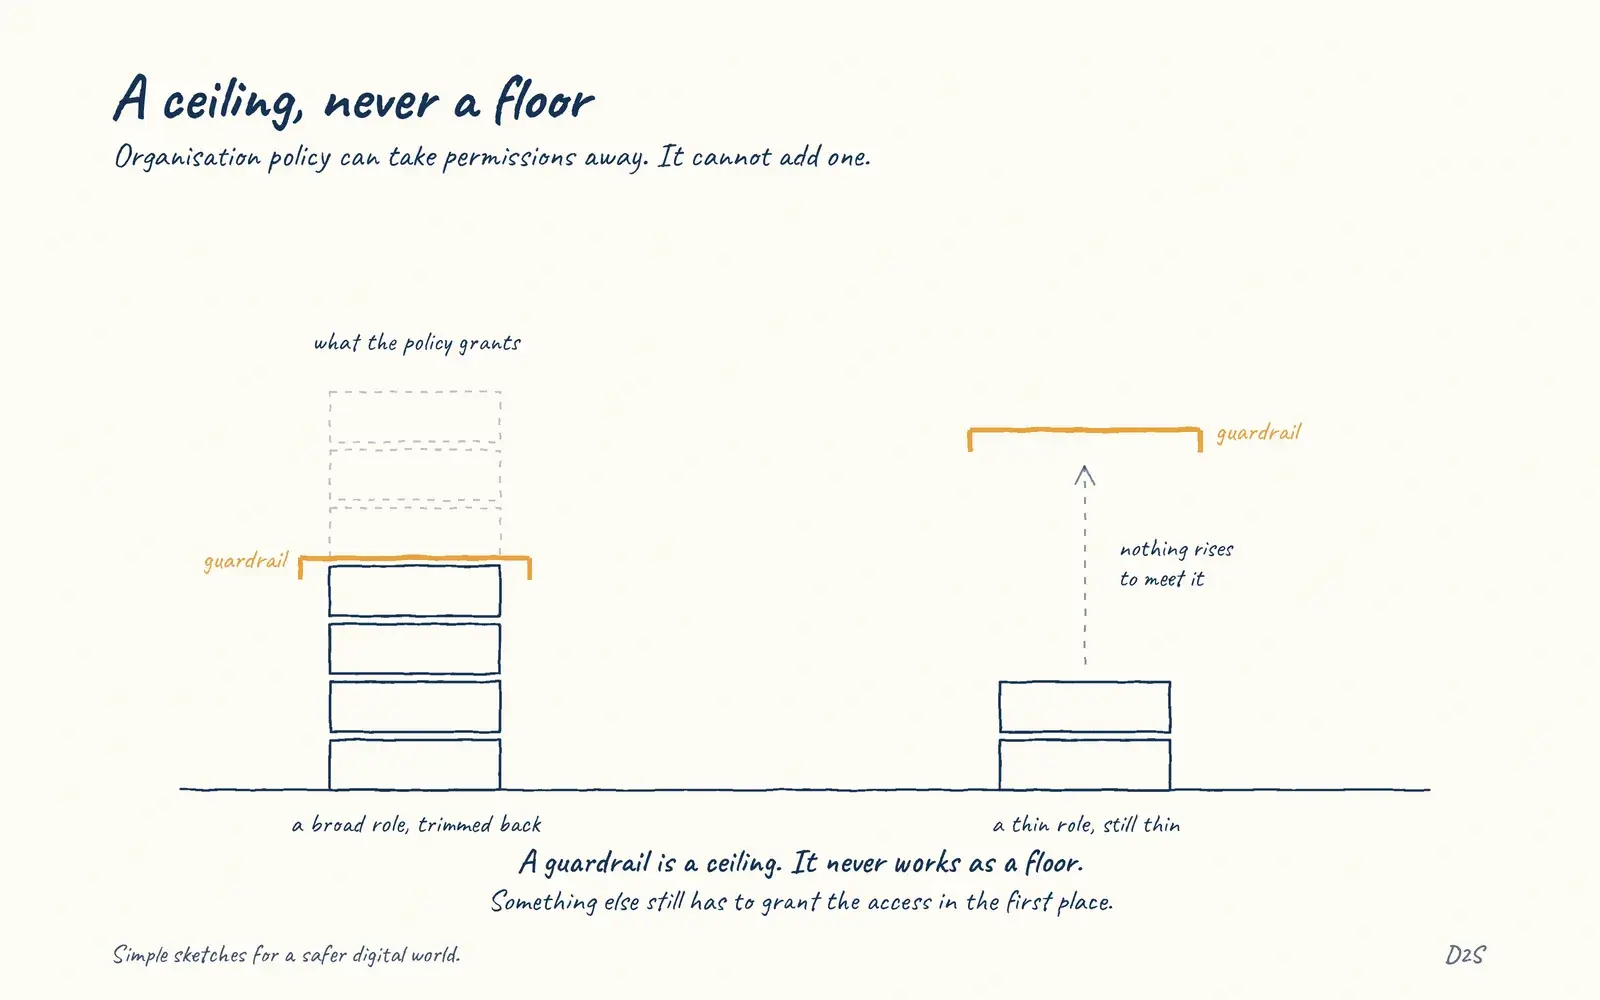 Organisation guardrails limit access but do not grant itA ceiling, never a floor
 Zero trust removes implicit trust in network position, not confidence in colleaguesIt was never about the people
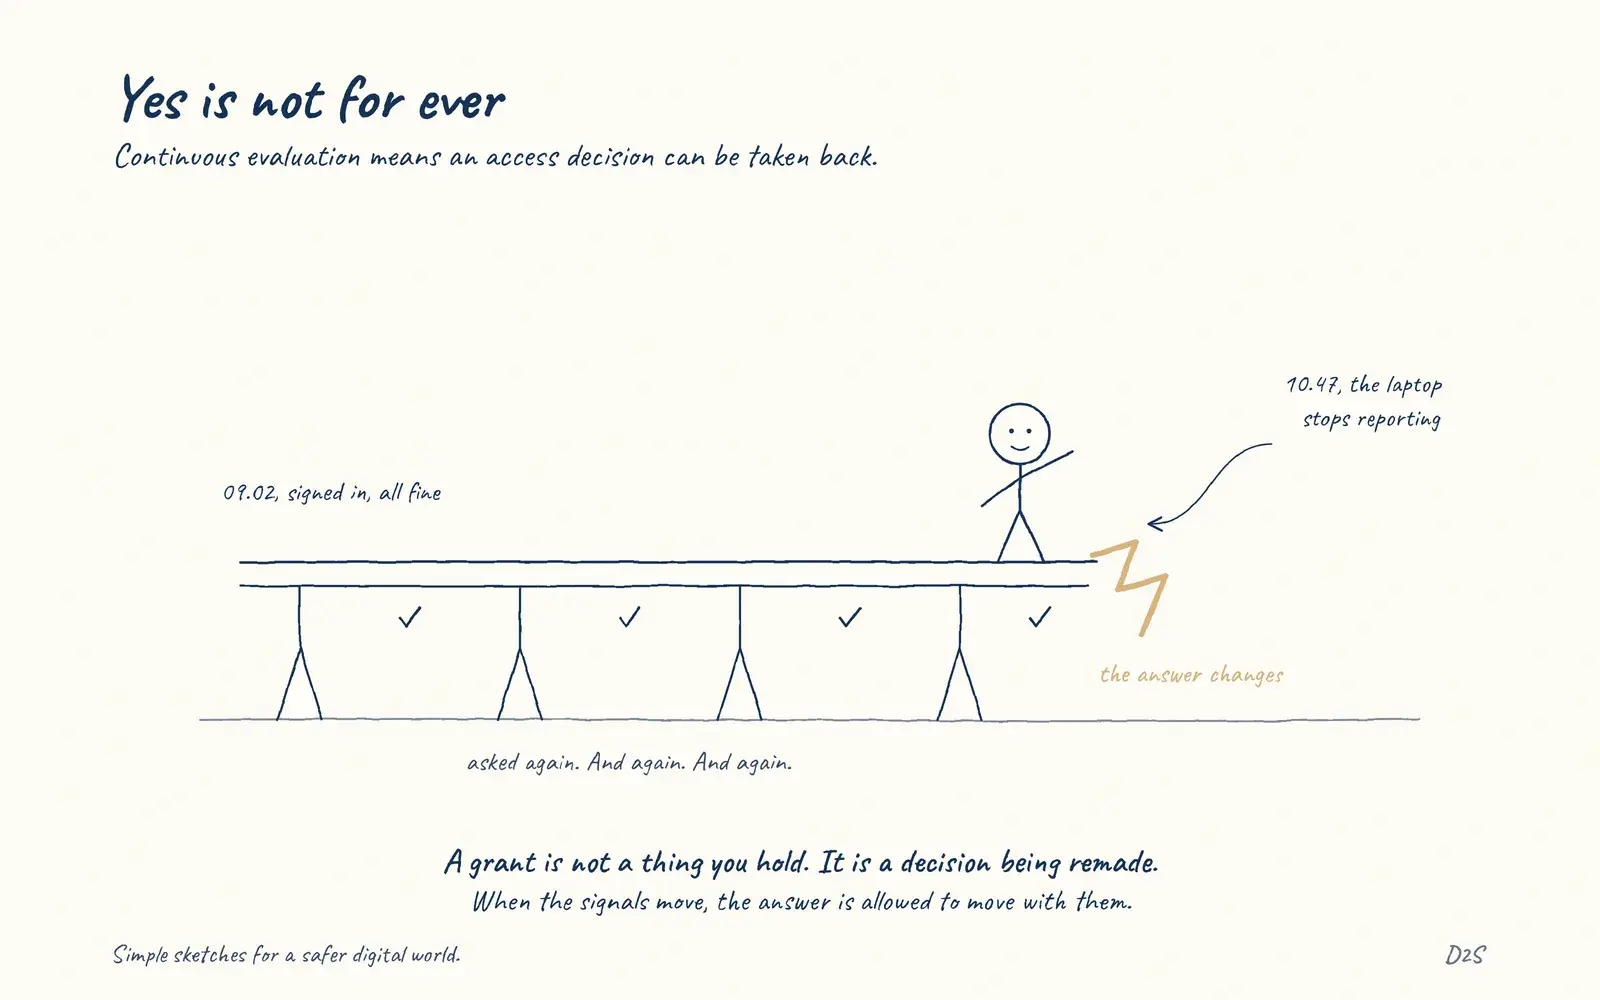 Continuous evaluation means decisions can changeYes is not for ever
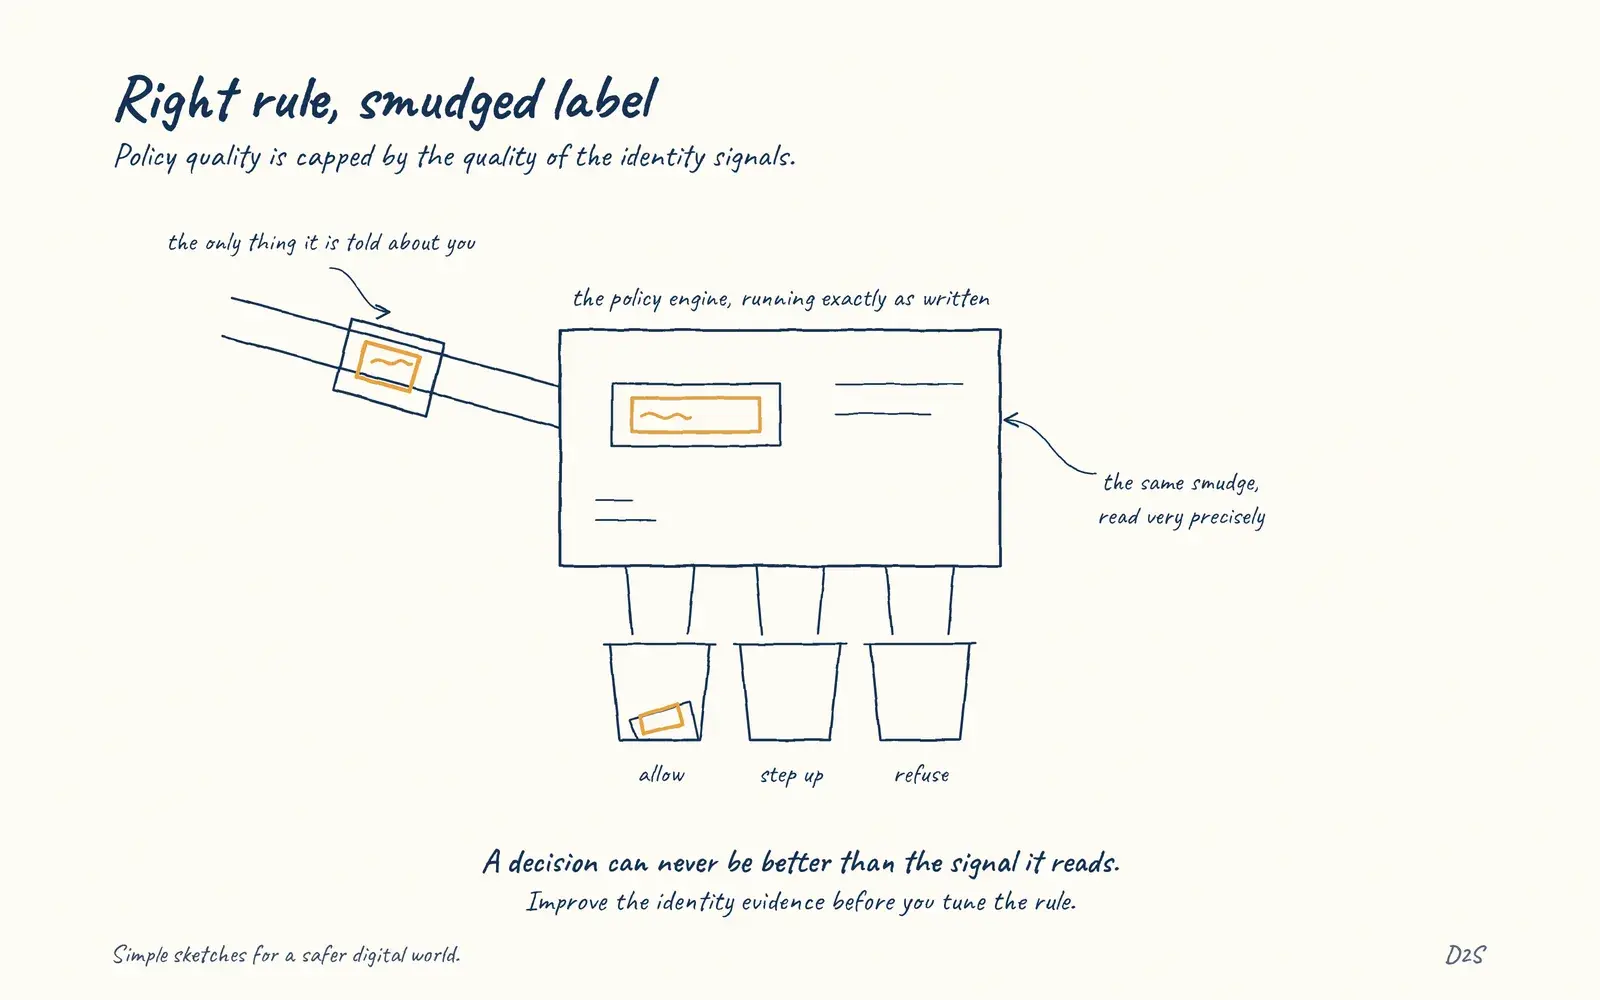 Policy enforcement depends on reliable identity signalsRight rule, smudged label
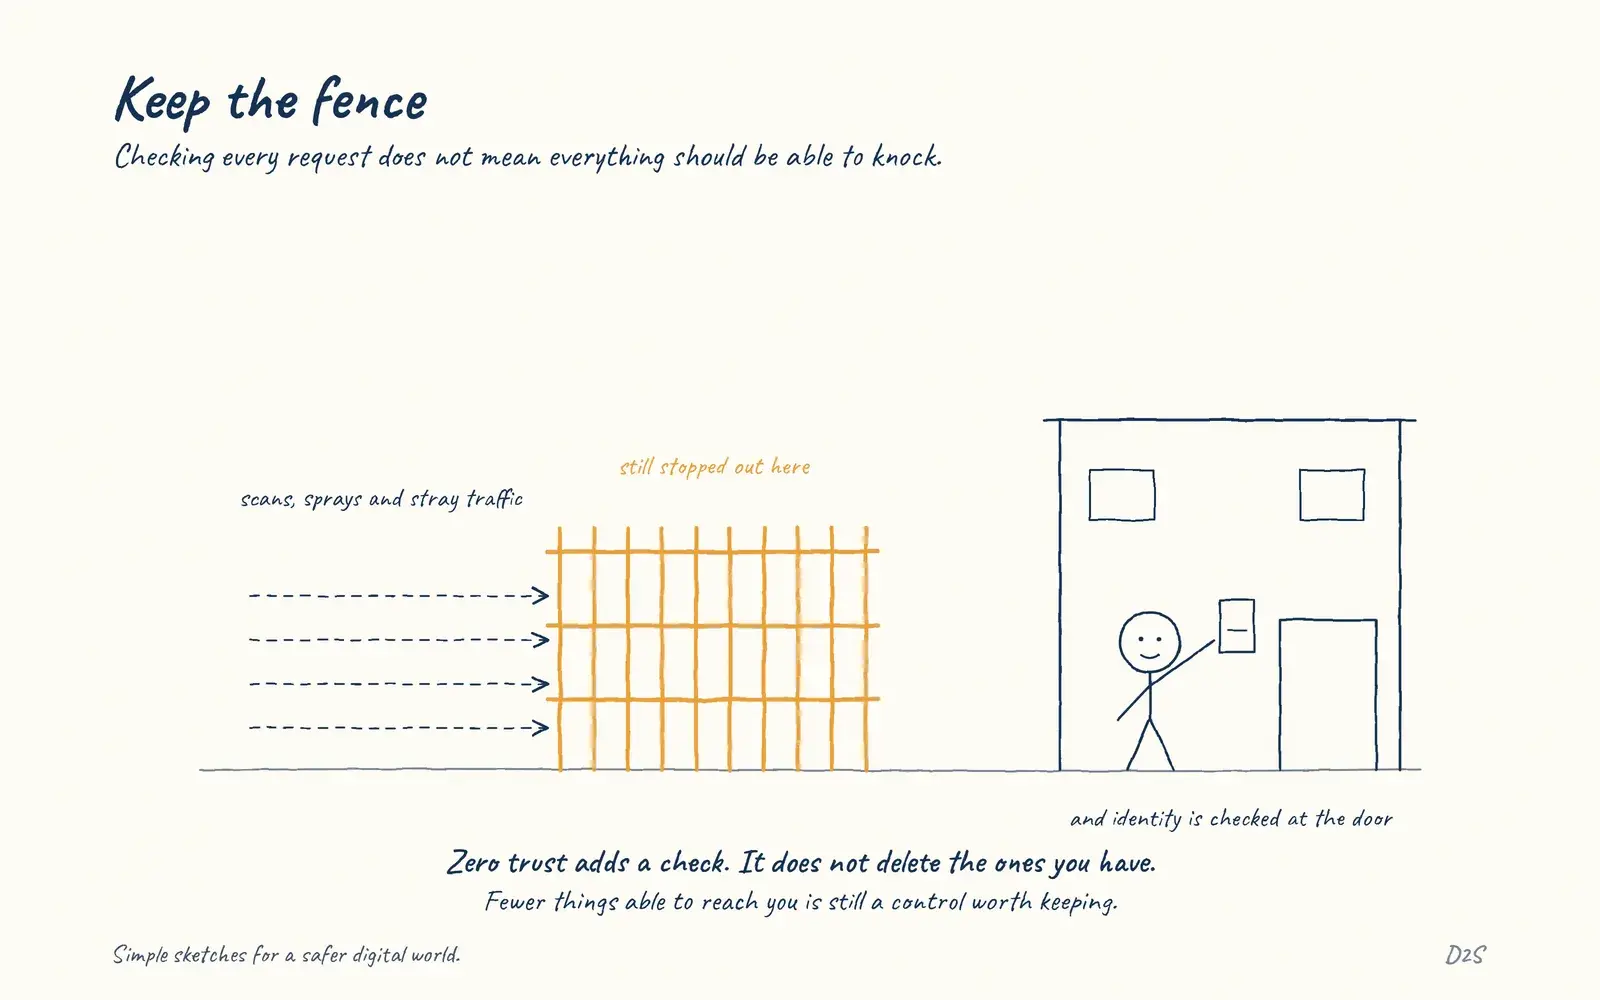 Zero trust does not remove network controlsKeep the fence
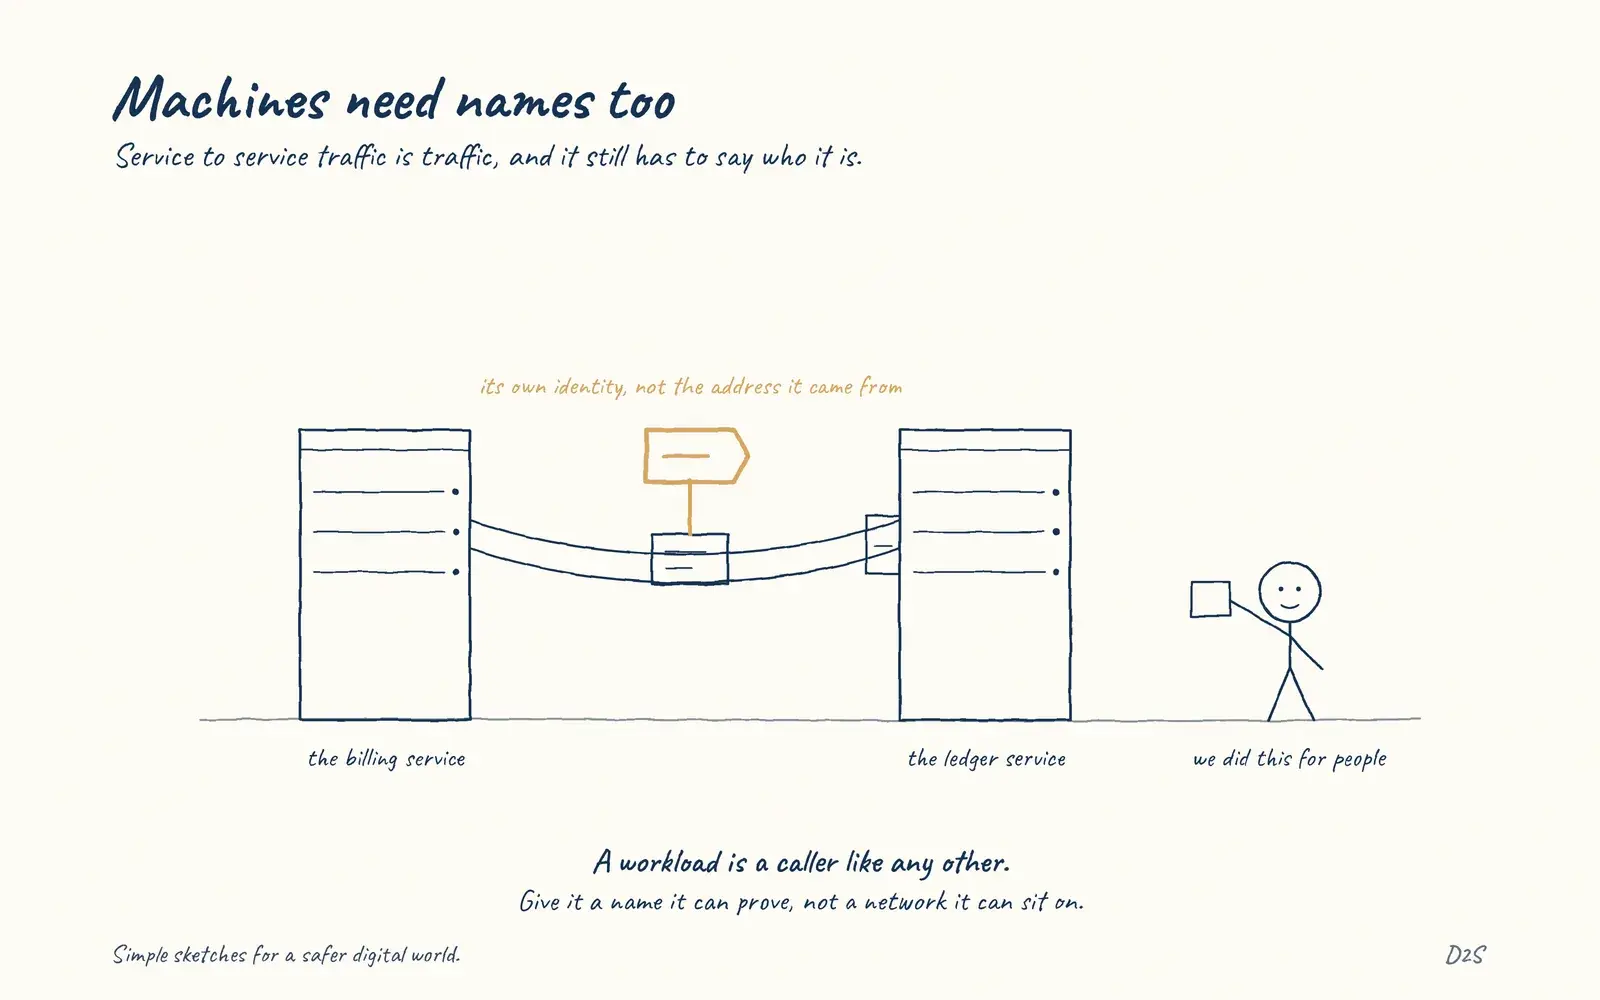 Service-to-service traffic needs identity tooMachines need names too
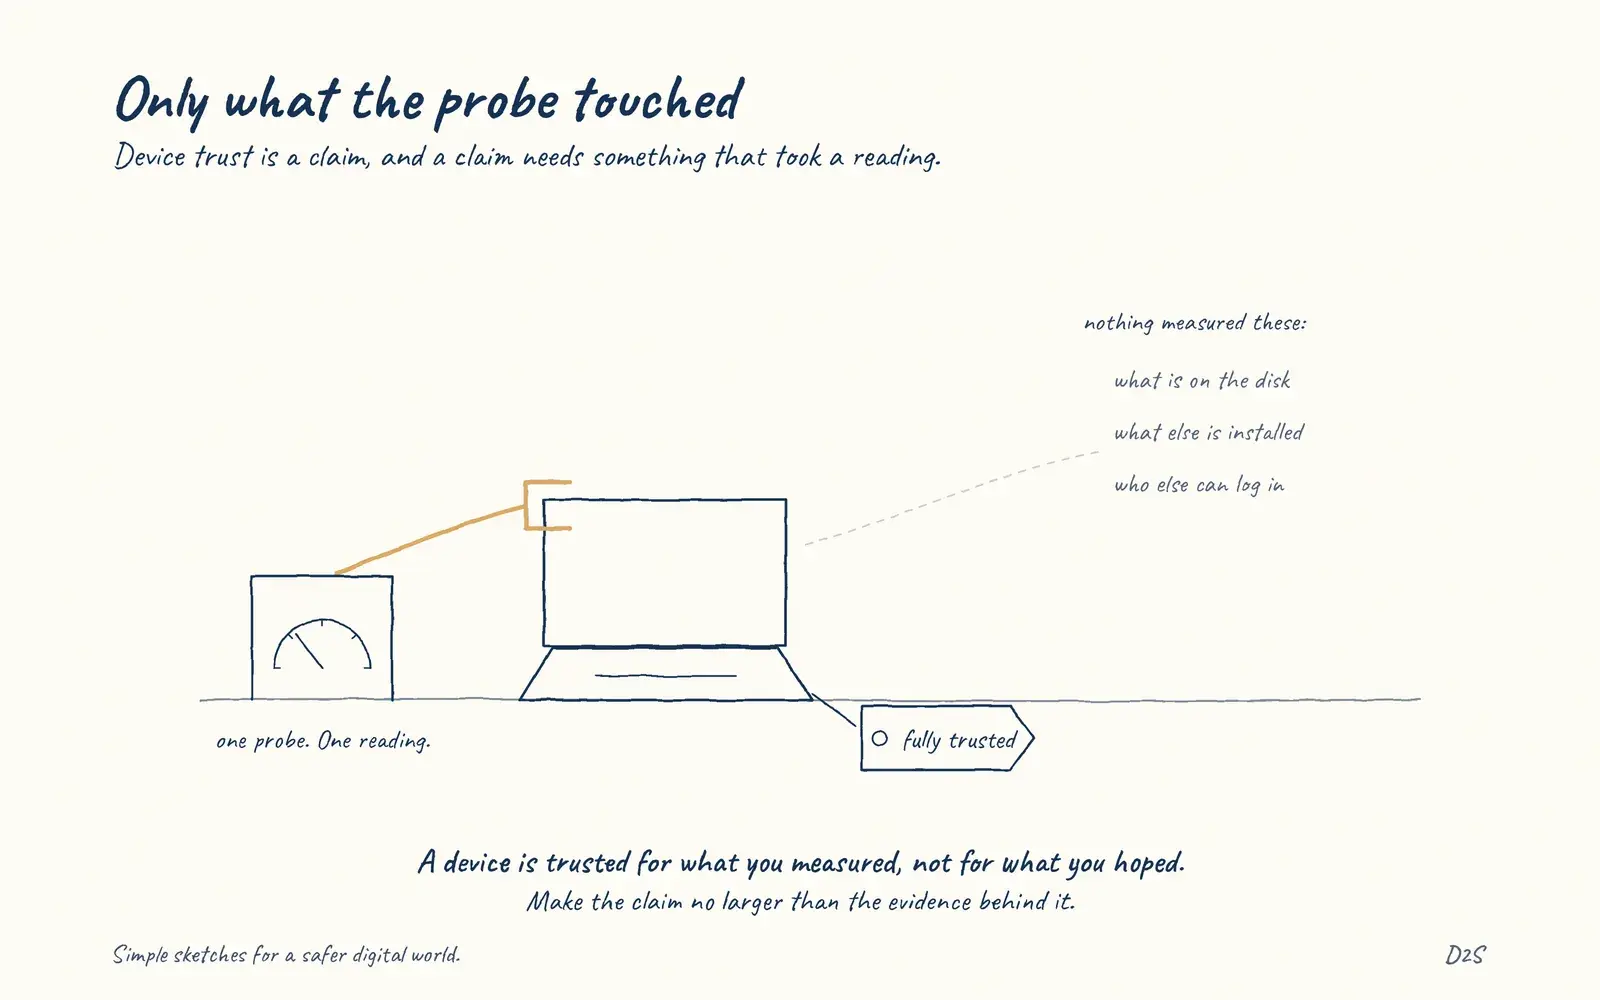 Device trust should match what is actually measuredOnly what the probe touched
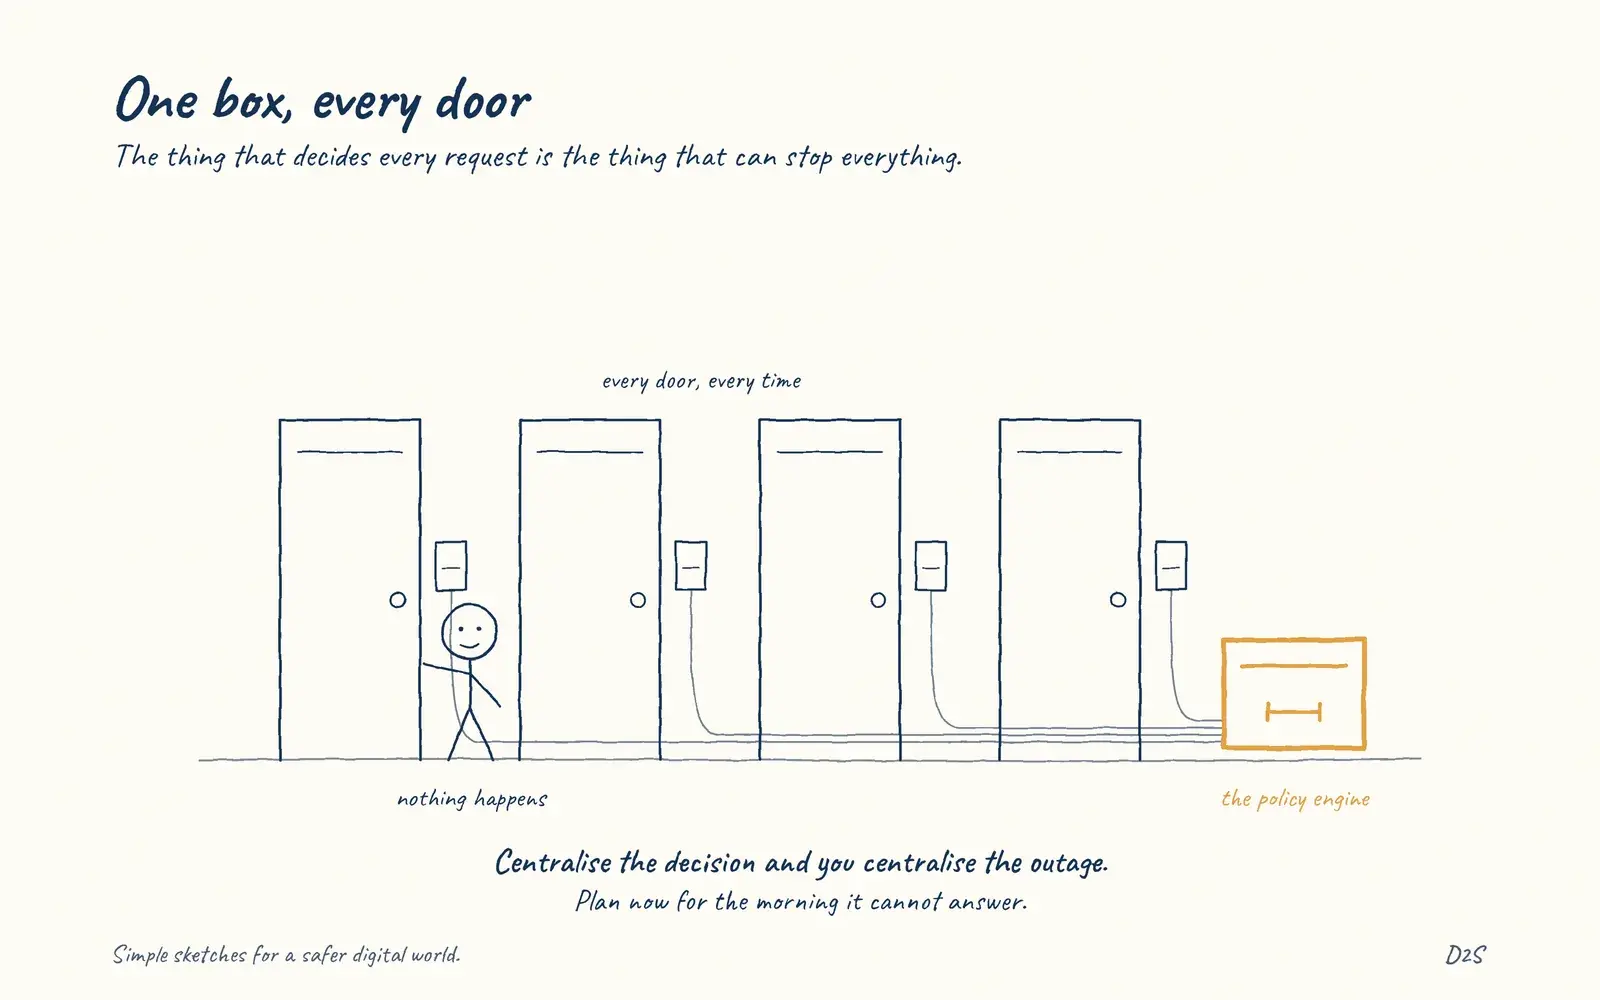 Policy engines create critical dependenciesOne box, every door
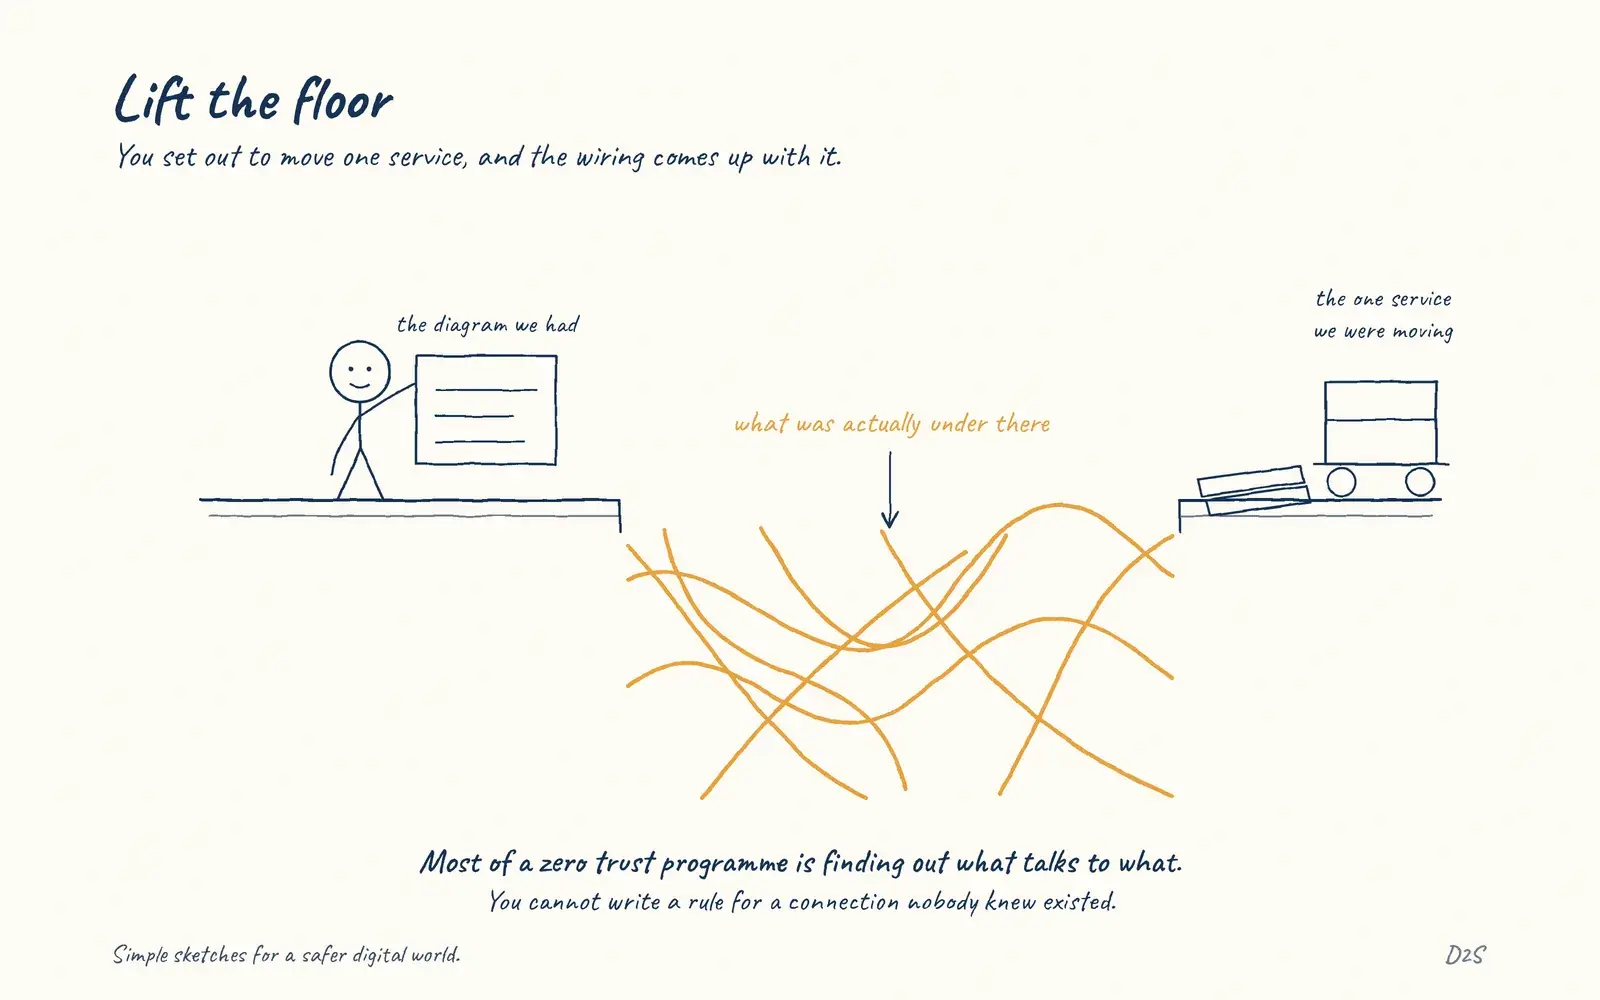 Zero trust migration is dependency discoveryLift the floor